 Do Son
TL;DR
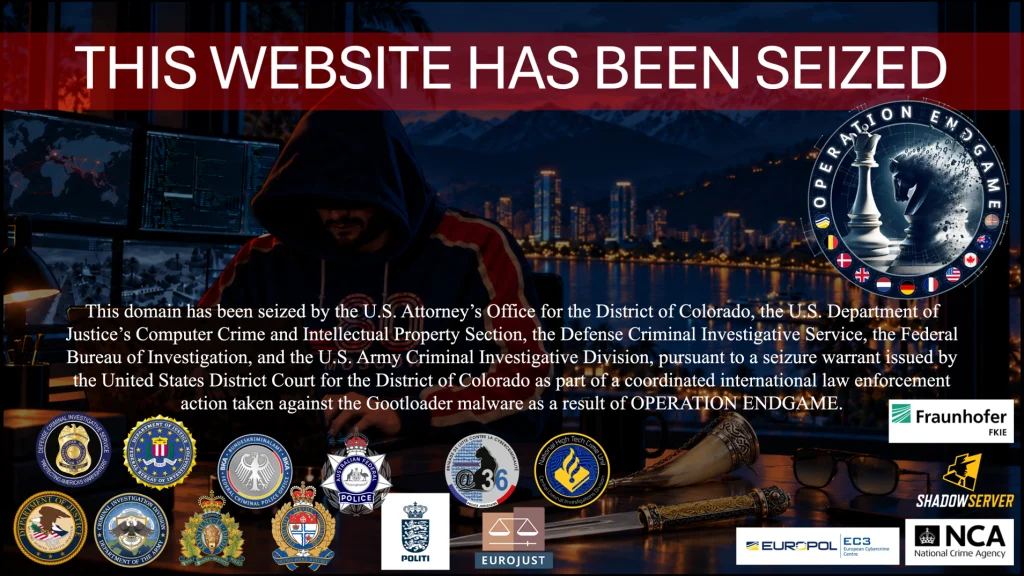
Federal authorities removed Gootloader malware from more than 100 computer servers and seized the U.S. domains controlling the network. Conducted alongside Operation Endgame partners, this Gootloader malware takedown dismantled a botnet that infected at least 25,000 systems worldwide since 2018. Furthermore, prosecutors linked the operation to 44 U.S. ransomware attacks that caused roughly $28.8 million in claimed losses.
What Happened in the Takedown
With court authorization from the District of Colorado, the Department of Justice and international partners wiped malicious code from over 100 servers, including hijacked WordPress websites. According to unsealed court warrants, the operators used compromised websites to trick visitors into downloading malicious files. Once installed, the software enrolled victim machines into a global botnet and sold network access to ransomware gangs.
“With court authorization, the Department of Justice and FBI, along with our international partners, conducted an online operation that liberated over 100 servers from malicious software, denying ransomware criminals a platform,” said Assistant Attorney General A. Tysen Duva. Meanwhile, the Shadowserver Foundation worked with internet service providers and national incident response teams to notify affected owners.
Who Is Behind the Activity
While authorities have not named individual suspects yet, investigators attribute the infrastructure with high confidence to initial access brokers supplying ransomware affiliates. The disruption took place under Operation Endgame, a multinational coalition involving Europol and police agencies from Germany, the Netherlands, Canada, Denmark, France, the United Kingdom, and Australia. Technical groups including Fraunhofer FKIE, OpenAI, Registrar of Last Resort, and Sharktech also assisted the investigation.
Impact and Defense Scale
Since 2018, the Gootloader malware has infected over 25,000 computers globally and enabled 44 U.S. ransomware incidents costing $28.8 million. “The Gootloader malware targeted victims on a global scale, including attacks on the U.S. Department of War and the Defense Industrial Base,” said Special Agent in Charge Kenneth DeChellis of the Defense Criminal Investigative Service.
How Organizations Can Stay Protected
Following this Gootloader malware takedown, website administrators should audit their WordPress installations for unauthorized scripts, update vulnerable plugins, and check notifications from the Shadowserver Foundation to remediate lingering infections.
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
