Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Malware
  • Hide’N Seek Botnet is Targeting Smart Home Devices
  • Malware

Hide’N Seek Botnet is Targeting Smart Home Devices

Do Son July 26, 2018 2 minutes read
Hide’N Seek Botnet
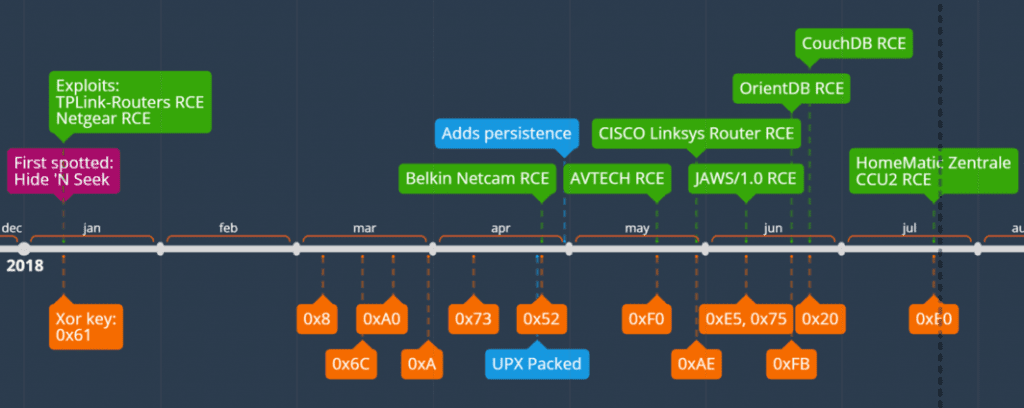
The Hide’N Seek botnet was first discovered in January this year, with initial targets for home routers and IP cameras, and a decentralised peer-to-peer architecture. As of May, this botnet has infected more than 90,000 IoT devices and is starting to target more device types and architectures.
Earlier this month, researchers at Qihoo 360 NetLab revealed that the botnet’s attack targets also covered AVTECH webcam and Cisco Linksys routers as well as OrientDB and CouchDB database servers and added a CPU mining program, but This feature was not enabled at the time.
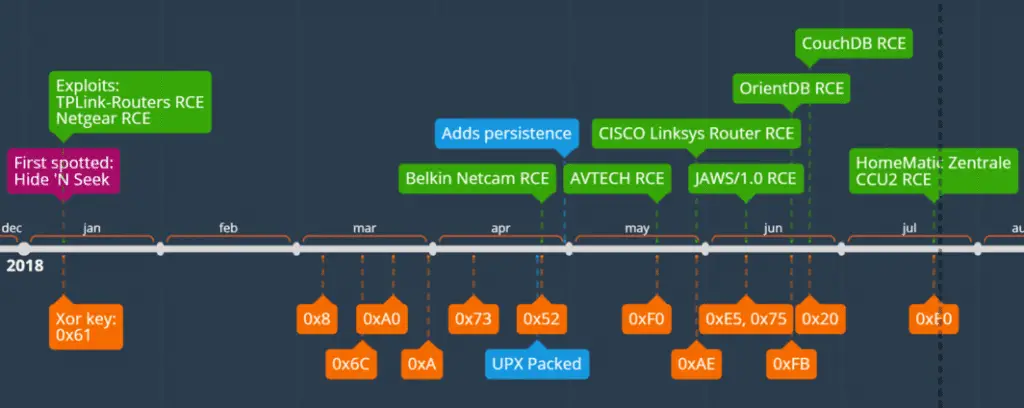
The latest report from Fortinet states that they have recently captured three new samples of HNS bots. The first sample configuration has 60 entries, including two exploits; the second sample has 81 entries and six exploits; and the third, and most recent, the sample has 110 entries and nine exploits. The vulnerabilities that have exploited so far are as follows:
Exploit Poc Published date
TP-Link Routers RCE 2013-03-12
Netgear DGN1000 RCE 2017-10-25
Belkin NetCam RCE 2017-07-17
AVTECH IP Camera/NVR/DVR RCE 2016-10-11
CISCO Linksys Router RCE 2014-02-16
JAWS/1.0 RCE 2016-02-10
OrientDB RCE 2017-10-09
Apache CouchDB RCE 2018-06-20
HomeMatic Zentrale CCU2 RCE 2018-07-18
More importantly, Fortinet security researchers also revealed that HNS has now added remote code execution vulnerabilities to HomeMatic Zentrale CCU2, Apache CouchDB remote code execution vulnerabilities, and remote code execution vulnerabilities in Belkin NetCam devices. Use.
The HomeMatic German manufacturer eQ-3 is a smart home equipment supplier, while the HomeMatic Zentrale CCU2 is the heart of the HomeMatic system, offering a wide range of control, monitoring and configuration options for all HomeMatic devices. This means that if a bot compromises the HomeMatic Zentrale CCU2, the victim may lose control of the entire smart home device.

Source, Image: Fortinet

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Microsoft warned that a PDF editor was carrying a mining program after being hacked
  • NPM Typosquatting Malware Targets WSL Developers
  • Android/Xamalicious Malware Hijacks 327K+ Android Devices
  • Lookout: Mobile phishing increase 85% over year for the past five years
  • School District was Infected by Emotet Bank Trojans, over 20 servers paralyzed
  • The High Cost of ‘Free’: How PiviGames Became a Lovecraftian Malware Hub for HijackLoader and ACRStealer
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Hide’N Seek (HNS) Botnet

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-77876CVSS 9.3
    Control Web Panel (CWP) before webpanel_version 1.16 contains an OS command injection vulnerability in the protected_directory user panel...
    📅 Updated: Nov 2, 2026
  • CVE-2026-79873CVSS 9.3
    Authentication bypass vulnerabilities in the PAPI protocol of AOS-10 could allow an unauthenticated adjacent attacker to circumvent existing...
    📅 Updated: Nov 2, 2026
  • CVE-2026-79874CVSS 9.3
    An authentication bypass in the API of AOS-10 allows an unauthenticated adjacent attacker to circumvent existing authentication controls....
    📅 Updated: Nov 2, 2026
  • CVE-2026-79872CVSS 9.4
    A buffer overflow vulnerability exists in the underlying operating system of AOS that could lead to unauthenticated remote...
    📅 Updated: Nov 2, 2026
  • CVE-2026-55981CVSS 9.6
    A firmware verification vulnerability in Creative Sound Blaster Katana could allow an attacker to modify a legitimate firmware...
    📅 Updated: Nov 2, 2026
  • CVE-2026-118235CVSS 9.8
    The SimpleForm – Form Maker to Chat Apps with Quiz, Poll and Multi Lead Notifications plugin for WordPress...
    📅 Updated: Nov 2, 2026
  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.