Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Data Leak
  • Intel Alder Lake source code leaked
  • Data Leak

Intel Alder Lake source code leaked

Do Son October 9, 2022 2 minutes read
Intel Alder Lake source code

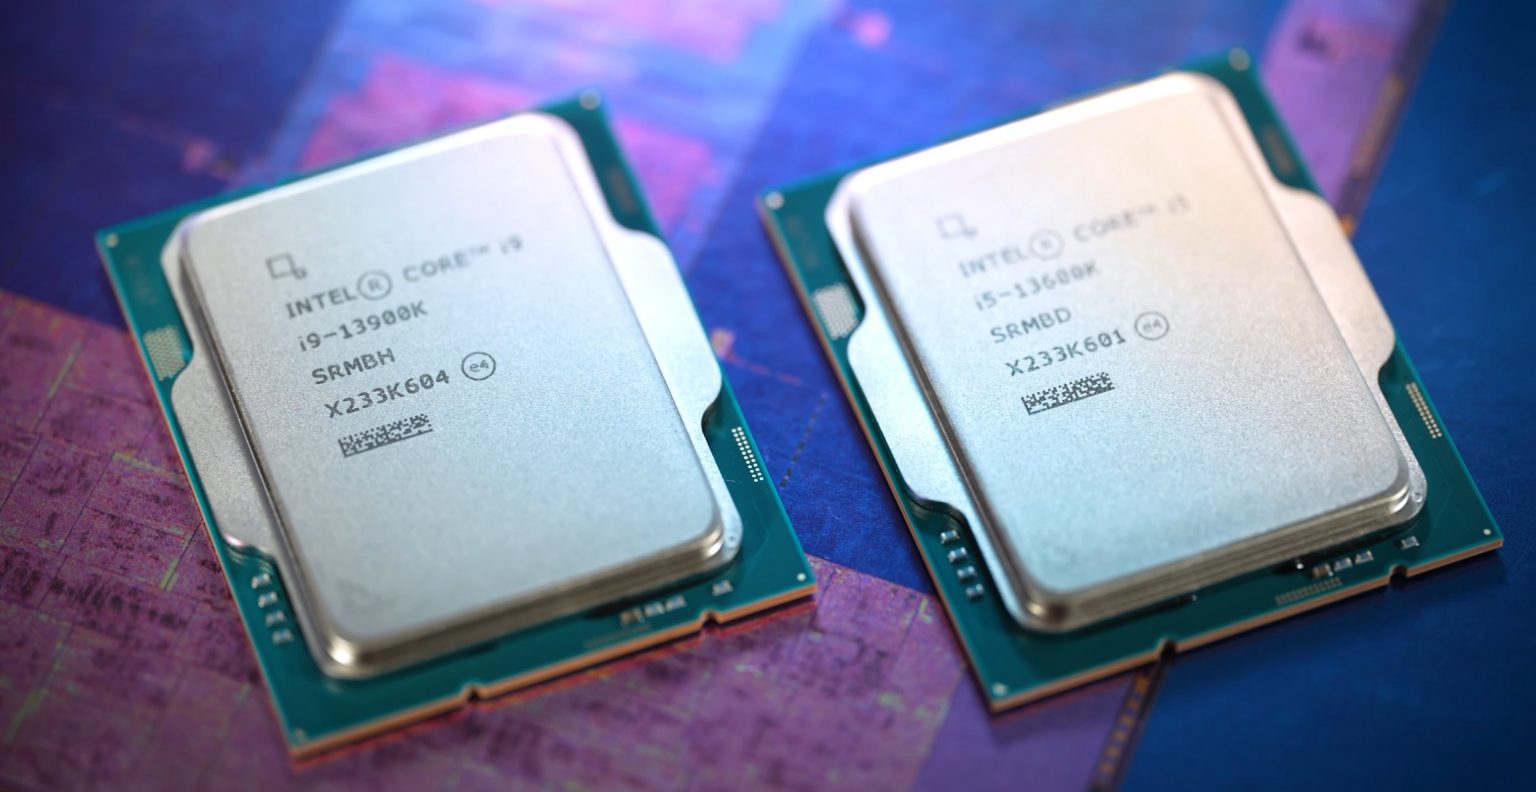
Image: Intel

In the past two years, hacker attacks have continued. For example, Nvidia suffered a ransomware attack by a hacker group earlier this year. After the internal system was compromised, more than 1TB of data was leaked, including drivers, design drawings, and firmware. In the middle of this year, another hacker obtained a large amount of data from AMD and tried to extort it, but AMD refused to pay the ransom, and the leaked information about the Zen 4 architecture processor was later confirmed to be true.

Recently, Twitter users @vxunderground and @glowingfreak revealed that after a major hack, the source code of Intel Alder Lake (including information such as BIOS and related chipsets) was leaked, and the size of the compressed file reached 2.8GB (5.86GB after decompression), and the code base is very large.
Intel Alder Lake source code
Image: Intel
It is unclear whether the data and documents came from Intel or its partners such as OEMs, as one of the documents mentioned “Lenovo Feature Tag Test Information.” The source code for Intel Alder Lake BIOS has been shared online on Github but it was taken down earlier. If these data and files contain sensitive material, it is uncertain whether they can be used to develop some exploit programs, thus posing a security risk.

Some media have contacted Intel to understand the situation, but Intel has not responded to the matter for the time being.

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • KDDI Data Breach: Millions of Emails and Passwords Stolen
  • Unmasked: 16GB “Rocket” Database Leak Exposes The Gentlemen Ransomware Cartel
  • AnyDesk Breach 2024: Dark Web Sale of 18,317 Credentials
  • Nissan Canada company was hacked andleaked 1.13 million sensitive information
  • Equifax Slapped with £11M FCA Fine Over Data Security Lapse
  • Microsoft workers uploaded sensitive login credentials to Microsoft’s own systems to GitHub
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Intel Alder Lake source code

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-121952CVSS 9.3
    FreeRDP before 3.32.2 has an out-of-bounds write in the proxy because rdp_read_bitmap_cache_v2_capability_set rejects only numCellCaches values above 5,...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121953CVSS 9.3
    FreeRDP before 3.32.2 has a use-after-free in the client's rdpgfx dynamic virtual channel: a duplicate-name channel with a...
    📅 Updated: Nov 4, 2026
  • CVE-2026-86574CVSS 9.8
    Heap-based Buffer Overflow Vulnerability in JP1/Base. This issue affects JP1/Base: from 11-00 before 12-50-54.
    📅 Updated: Nov 4, 2026
  • CVE-2026-86575CVSS 9.4
    Stack-based Buffer Overflow Vulnerability in JP1 Products. This issue affects JP1/Integrated Management 3 - Manager: from 13-00 before...
    📅 Updated: Nov 4, 2026
  • CVE-2026-86576CVSS 9.4
    Heap-based Buffer Overflow Vulnerability in JP1 Products. This issue affects JP1/Integrated Management 3 - Manager: from 13-00 before...
    📅 Updated: Nov 4, 2026
  • CVE-2026-86577CVSS 9.4
    Out-of-bounds Write Vulnerability in JP1 Products. This issue affects JP1/Integrated Management 3 - Manager: from 13-00 before 13-50-31;...
    📅 Updated: Nov 4, 2026
  • CVE-2026-84539CVSS 9.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in macOS Golden Gate...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.