Skip to content
October 20, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • Microsoft has published the Windows Desktop Program
  • Technology

Microsoft has published the Windows Desktop Program

Do Son January 24, 2018 1 minute read
Windows Desktop Program
Add Daily CyberSecurity as a preferred source on Google

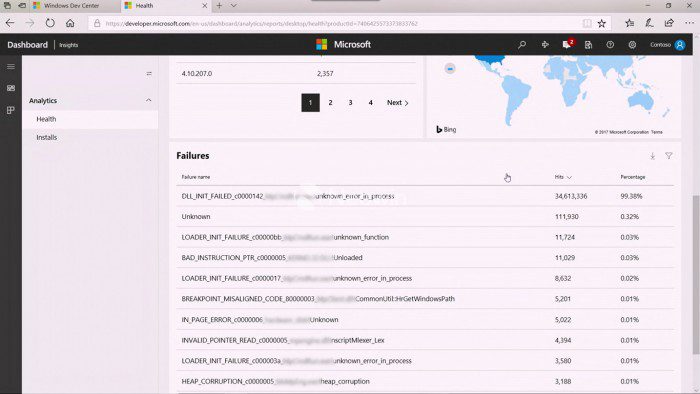
In a blog post updated Tuesday, Microsoft announced the launch of the new Windows Desktop project, an online developer tool designed to streamline data analysis and processing for application performance and application debugging.

As the picture above shows, developers on the Dashboard have access to the combined performance of added EXE files, plus options to track more files. Tasks for working on new files involve downloading unsigned files, signing them up as someone’s desktop application using the same certificate, and uploading to the signed file to the platform. This allows Microsoft to map code-signing certificates to telemetry to collect all applications signed with the same certificate, making it easy to track multiple EXE files at once.


This tool allows developers to access data through the API, rather than relying on the channel. This project will replace Microsoft Sysdev Partner Portal after it goes online, and interested developers can access it for free.

Source: neowin

Related coverage

  • Intel Raptor Lake CPUs Facing Widespread Stability Issues, Causing Firefox Crashes
  • IBM Partners with Anthropic to Embed Claude AI in New Development Tools, Reporting 45% Productivity Boost
  • Github launches Python security alerts
  • Let’s Encrypt to Deprecate OCSP in Favor of CRLs, Enhancing User Privacy
  • Apple Leverages Supreme Court Ruling to Fight App Store External Payment Links Mandate
  • Google’s Antitrust Showdown: DOJ Demands Chrome Separation, Android Reforms
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Windows Desktop Program

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 20, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 20, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 20, 2026
  • CVE-2026-66373CVSS 7.5
    Redis before 8.8.0, in the unusual case where an authenticated attacker can execute RESTORE, allows remote code execution...
    Admin intel📅 Updated: Oct 20, 2026
  • CVE-2026-110936CVSS 8.4
    A vulnerability has been identified in Siemens Software Center (All versions < V4.0.9.8). The affected application loads dynamic-link...
    Admin intel📅 Updated: Oct 20, 2026
  • CVE-2026-111862CVSS 9.8
    Rank Math SEO PRO for WordPress is affected by a supply-chain compromise in a subset of version 3.0.123...
    Admin intel📅 Updated: Oct 17, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    Watchtower Verified📅 Updated: Oct 17, 2026
  • CVE-2025-61624CVSS 6.0
    An Improper Limitation of a Pathname to a Restricted Directory (\'Path Traversal\') [CWE-22] vulnerability in Fortinet FortiOS 7.6.0...
    CISA KEV📅 Added to KEV: Oct 16, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-110957CVSS 10.0
    A vulnerability has been found in Wavlink WL-WN530BE2-A up to M30BE2_V250604. The affected element is the function sub_12580...
    📅 Updated: Oct 20, 2026
  • CVE-2026-77524CVSS 9.9
    KEDA is a Kubernetes-based Event Driven Autoscaling component. In version 2.20.2 and earlier, a namespace administrator who can...
    📅 Updated: Oct 20, 2026
  • CVE-2026-110646CVSS 9.2
    Beganovich snappdf from 1.1.0 before 6.1.0 contains an OS command injection vulnerability on Windows that allows attackers to...
    📅 Updated: Oct 20, 2026
  • CVE-2026-110636CVSS 9.3
    pypdftk through 0.5 contains an OS command injection vulnerability in fill_form(), dump_data_fields(), and pdftk_cmd_util() that builds shell commands...
    📅 Updated: Oct 20, 2026
  • CVE-2026-110631CVSS 9.3
    Komodo through 2.3.3 contains an authentication bypass vulnerability in the Periphery agent that allows unauthenticated attackers to connect...
    📅 Updated: Oct 20, 2026
  • CVE-2026-110616CVSS 9.2
    NullHub through 2026.5.29 contains a missing authentication vulnerability that allows unauthenticated attackers to access the /api/* management API...
    📅 Updated: Oct 20, 2026
  • CVE-2026-77936CVSS 9.3
    Letta through 0.16.8 ships a compose.yaml that does not enable LETTA_SERVER_SECURE, so the password middleware is never added...
    📅 Updated: Oct 20, 2026
  • CVE-2026-77933CVSS 9.3
    DB-GPT through 0.8.2 contains a hardcoded credentials vulnerability in its default docker-compose.yml that sets a static MYSQL_ROOT_PASSWORD and...
    📅 Updated: Oct 20, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.