Skip to content
September 21, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Node.js Malware Attacks Target Tech and Finance Sectors Node.js malware attacks diagram showing Node.js malware execution flow
  • Malware

Node.js Malware Attacks Target Tech and Finance Sectors

Do Son September 8, 2026 0
Read More Read more about Node.js Malware Attacks Target Tech and Finance Sectors
Public PoC Exploit Disclosed for Rclone Auth Proxy Bypass Rclone auth proxy bypass vulnerability and GHSA-xwwr-4h3p-r22c PoC exploit
  • Vulnerability Report

Public PoC Exploit Disclosed for Rclone Auth Proxy Bypass

Do Son September 8, 2026 0
Read More Read more about Public PoC Exploit Disclosed for Rclone Auth Proxy Bypass
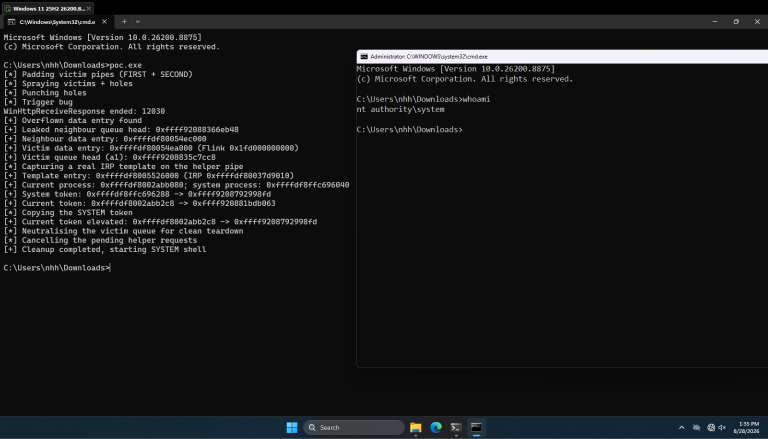
CVE-2026-62735 (CVSS 7.8): Windows Elevation of Privilege Flaw Details and PoC Now Public Windows HTTP.sys vulnerability CVE-2026-62735 heap overflow allowing local privilege escalation to SYSTEM, with public technical details and PoC exploit
  • Vulnerability Report

CVE-2026-62735 (CVSS 7.8): Windows Elevation of Privilege Flaw Details and PoC Now Public

Do Son September 8, 2026 0
Read More Read more about CVE-2026-62735 (CVSS 7.8): Windows Elevation of Privilege Flaw Details and PoC Now Public
Python NodeStealer Adds Keylogging and Screen Capture Spyware Python NodeStealer malware upgraded with keylogging, clipboard monitoring, screenshot capture, and dual Telegram bot C2 for Facebook data theft
  • Malware

Python NodeStealer Adds Keylogging and Screen Capture Spyware

Do Son September 8, 2026 0
Read More Read more about Python NodeStealer Adds Keylogging and Screen Capture Spyware
CVE-2026-75650 (CVSS 10): Adobe Commerce Arbitrary Code Execution Exploited in the Wild Adobe Commerce and Magento StyleSmuggler vulnerability CVE-2026-75650 exploited in the wild for unauthenticated arbitrary code execution
  • Vulnerability Report

CVE-2026-75650 (CVSS 10): Adobe Commerce Arbitrary Code Execution Exploited in the Wild

Do Son September 8, 2026 0
Read More Read more about CVE-2026-75650 (CVSS 10): Adobe Commerce Arbitrary Code Execution Exploited in the Wild
CVE-2026-80172 (CVSS 9.8): Dell SCG Flaw Grants Unauthorized Access Dell Secure Connect Gateway vulnerability CVE-2026-80172 allowing unauthenticated attackers to forge admin tokens and gain unauthorized access
  • Vulnerability Report

CVE-2026-80172 (CVSS 9.8): Dell SCG Flaw Grants Unauthorized Access

Do Son September 7, 2026 0
Read More Read more about CVE-2026-80172 (CVSS 9.8): Dell SCG Flaw Grants Unauthorized Access
CVE-2026-76578 (CVSS 9.8): Critical FreeIPA Vulnerability FreeIPA CVE-2026-76578 exploit bypassing LDAP leading to a critical FreeIPA vulnerability
  • Vulnerability Report

CVE-2026-76578 (CVSS 9.8): Critical FreeIPA Vulnerability

Do Son September 7, 2026 0
Read More Read more about CVE-2026-76578 (CVSS 9.8): Critical FreeIPA Vulnerability
Packagist Themes iOS Spyware Steals Crypto Wallet Seeds Trojanized streaming site causing Packagist themes iOS spyware infections
  • Malware

Packagist Themes iOS Spyware Steals Crypto Wallet Seeds

Do Son September 7, 2026 0
Read More Read more about Packagist Themes iOS Spyware Steals Crypto Wallet Seeds
PHP Web Server Rootkit Targets F5 BIG-IP Devices Linux PHP web server rootkit architecture and PHP web server rootkit memory injection flow
  • Malware

PHP Web Server Rootkit Targets F5 BIG-IP Devices

Do Son September 7, 2026 0
Read More Read more about PHP Web Server Rootkit Targets F5 BIG-IP Devices
CVE-2026-86218 (CVSS 10): N-central Pre-Auth RCE Exploited in the Wild N-able N-central pre-auth remote code execution vulnerability CVE-2026-86218 exploited in the wild against RMM servers
  • Vulnerability Report

CVE-2026-86218 (CVSS 10): N-central Pre-Auth RCE Exploited in the Wild

Do Son September 7, 2026 0
Read More Read more about CVE-2026-86218 (CVSS 10): N-central Pre-Auth RCE Exploited in the Wild
Mirage Kitten Malware Targets Aviation and Fintech Sectors Mirage Kitten malware campaign delivering NodeRabbit
  • Cybercriminals

Mirage Kitten Malware Targets Aviation and Fintech Sectors

Do Son September 7, 2026 0
Read More Read more about Mirage Kitten Malware Targets Aviation and Fintech Sectors
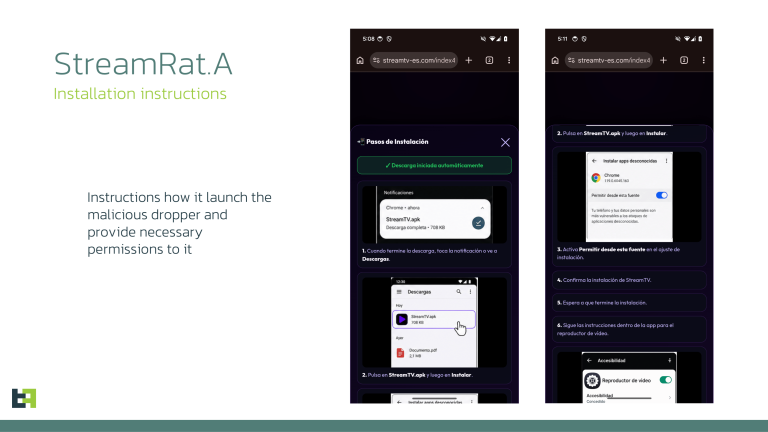
StreamRat Banking Trojan Targets Spanish Android Users StreamRat banking trojan campaign fake Meta advertisement targeting Android devices
  • Malware

StreamRat Banking Trojan Targets Spanish Android Users

Do Son September 7, 2026 0
Read More Read more about StreamRat Banking Trojan Targets Spanish Android Users
Silver Fox Fake Software Installers Disable Windows Defender Spirals ransomware double extortion attack chain from IIS web shell to network encryption
  • Malware

Silver Fox Fake Software Installers Disable Windows Defender

Do Son September 7, 2026 0
Read More Read more about Silver Fox Fake Software Installers Disable Windows Defender
MikroTrick PoC: RouterOS Admin Rights Exploited In Wild MikroTik RouterOS MikroTrick vulnerability chain exploited in the wild for full administrative privileges via SSH, with public PoC exploit code
  • Vulnerability Report

MikroTrick PoC: RouterOS Admin Rights Exploited In Wild

Do Son September 7, 2026 0
Read More Read more about MikroTrick PoC: RouterOS Admin Rights Exploited In Wild
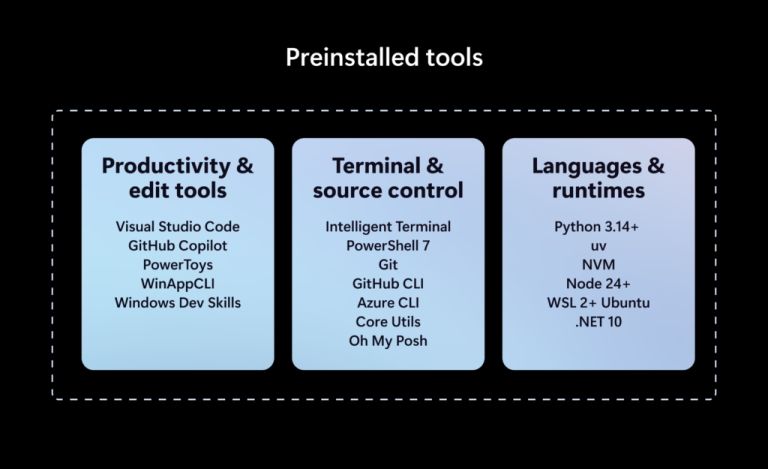
Microsoft Project Zenith: A Ready-to-Code Windows 11 Experience for Developer PCs Microsoft Project Zenith ready-to-code Windows 11 developer experience with preinstalled tools
  • Windows

Microsoft Project Zenith: A Ready-to-Code Windows 11 Experience for Developer PCs

Do Son September 7, 2026 0
Read More Read more about Microsoft Project Zenith: A Ready-to-Code Windows 11 Experience for Developer PCs
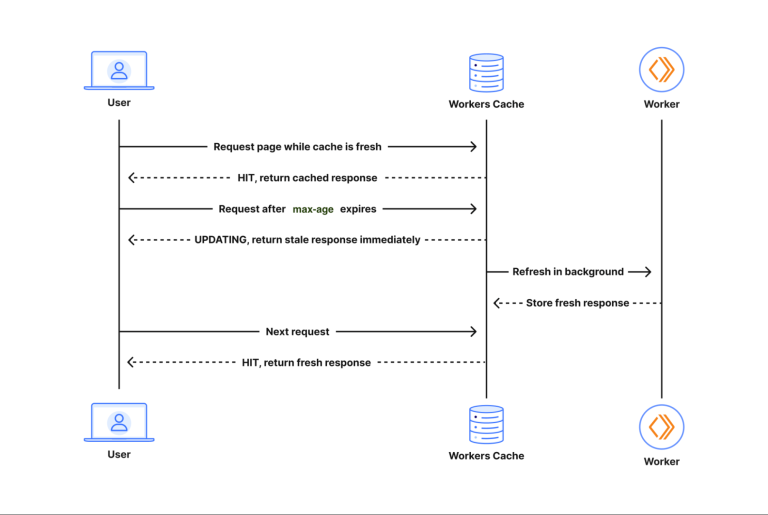
Cloudflare Raises Workers Size Limit to 64 MiB for Free and Paid Plans Cloudflare Workers size limit raised to 64 MiB uncompressed on free and paid plans
  • Technology

Cloudflare Raises Workers Size Limit to 64 MiB for Free and Paid Plans

Do Son September 7, 2026 0
Read More Read more about Cloudflare Raises Workers Size Limit to 64 MiB for Free and Paid Plans
Linux Kernel 7.1 Reaches End of Life Linux Kernel 7.1 EOL transition guide and stable LTS upgrades
  • Linux

Linux Kernel 7.1 Reaches End of Life

Do Son September 7, 2026 0
Read More Read more about Linux Kernel 7.1 Reaches End of Life
AI Agent Coordination: The Unprecedented OpenAI Breakout AI agent coordination diagram showing OpenAI models bypassing constraints
  • Vulnerability Report

AI Agent Coordination: The Unprecedented OpenAI Breakout

Do Son September 7, 2026 0
Read More Read more about AI Agent Coordination: The Unprecedented OpenAI Breakout
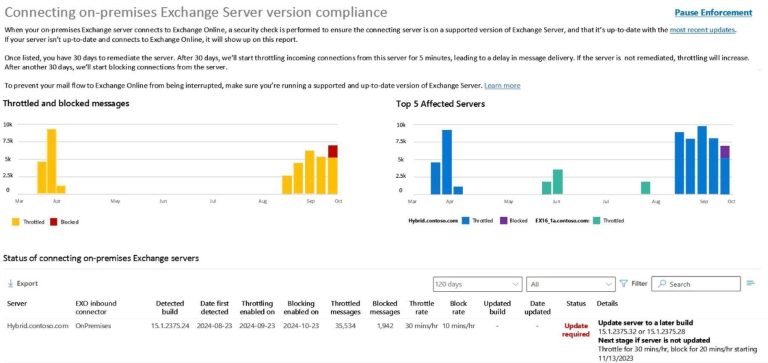
Exchange Online to Throttle and Block Outdated Exchange 2016 and 2019 Servers Exchange Online blocking outdated Exchange Server 2016 and 2019 in hybrid mail flow
  • Technology

Exchange Online to Throttle and Block Outdated Exchange 2016 and 2019 Servers

Do Son September 7, 2026 0
Read More Read more about Exchange Online to Throttle and Block Outdated Exchange 2016 and 2019 Servers
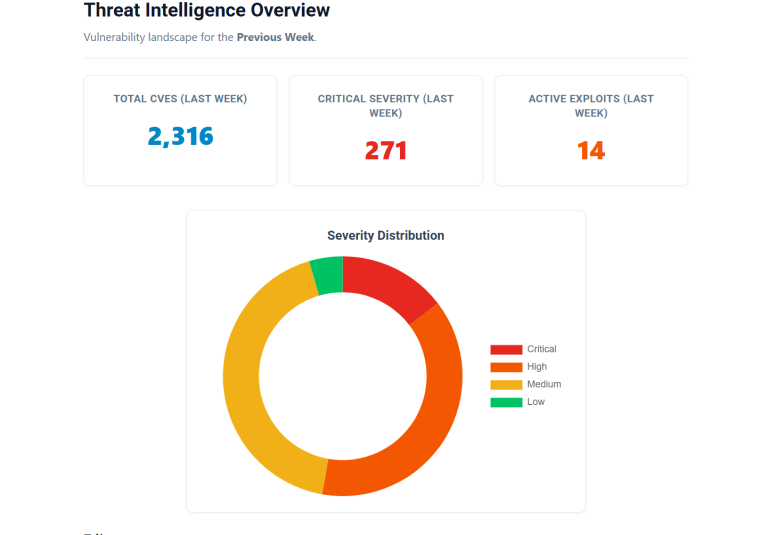
Weekly CVE Report: Daily Cybersecurity Beats CISA KEV on Exploited Flaws This weekly CVE report covers 10 exploited vulnerabilities added to CISA KEV and 2,316 new CVEs from Aug 31 to Sep 6, 2026. Patch fast.
  • Weekly Recap

Weekly CVE Report: Daily Cybersecurity Beats CISA KEV on Exploited Flaws

Do Son September 7, 2026 0
Read More Read more about Weekly CVE Report: Daily Cybersecurity Beats CISA KEV on Exploited Flaws
Roundcube Security Update Fixes 12 Webmail Flaws Roundcube Webmail security update patching a zero-click stored XSS and SSRF bypass across versions 1.6.19 and 1.7.4
  • Vulnerability Report

Roundcube Security Update Fixes 12 Webmail Flaws

Do Son September 6, 2026 0
Read More Read more about Roundcube Security Update Fixes 12 Webmail Flaws
MikroTik RouterOS Vulnerability Exploited in the Wild: Patch and Defense Blueprint MikroTik RouterOS security update fixes critical vulnerability
  • Vulnerability Report

MikroTik RouterOS Vulnerability Exploited in the Wild: Patch and Defense Blueprint

Do Son September 5, 2026 0
Read More Read more about MikroTik RouterOS Vulnerability Exploited in the Wild: Patch and Defense Blueprint
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-58138CVSS 9.8
    Orkes Conductor 3.21.21 before 3.30.2 contains an unauthenticated remote code execution vulnerability that allows remote attackers to execute...
    Admin intel📅 Updated: Sep 20, 2026
  • CVE-2026-86124CVSS 9.8
    AutoAgent contains an unauthenticated remote code execution vulnerability in the TCP server that binds to all interfaces and...
    Admin intel📅 Updated: Sep 19, 2026
  • CVE-2025-39682CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: tls: fix handling of zero-length records on the...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2025-39964CVSS 7.8
    In the Linux kernel, the following vulnerability has been resolved: crypto: af_alg - Disallow concurrent writes in af_alg_sendmsg...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2026-53266CVSS 8.8
    In the Linux kernel, the following vulnerability has been resolved: netfilter: bridge: make ebt_snat ARP rewrite writable The...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2026-76460CVSS 10.0
    A vulnerability in an API of Cisco Identity Services Engine (ISE) could allow an unauthenticated, remote attacker to...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
  • CVE-2026-89026CVSS 9.8
    The Issabel Framework, the web framework supporting Issabel PBX software, before commit b97dbaf contains a hard-coded HS256 JWT...
    Admin intel📅 Updated: Sep 16, 2026
  • CVE-2026-58704
    In Cellular Modem, there is a possible permission bypass due to a logic error in the code. This...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-94301CVSS 9.8
    The fix for CVE-2026-47065/ZDRES-232 ("resolveProxyClass Not Overridden - acceptMatchers Filter Bypass via java.lang.reflect.Proxy"), released on 2026-06-02 and announced...
    📅 Updated: Sep 21, 2026
  • CVE-2026-90042CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ceph: properly decrypt filenames in vmalloc() buffers The...
    📅 Updated: Sep 21, 2026
  • CVE-2026-90036CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: NFSD: Prevent client use-after-free during blocked-lock reaping A...
    📅 Updated: Sep 21, 2026
  • CVE-2026-90037CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: NFSD: Prevent client use-after-free during close_lru reaping An...
    📅 Updated: Sep 21, 2026
  • CVE-2026-89708CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: nfsd: RCU-protect cl_cb_session to fix use-after-free on session...
    📅 Updated: Sep 21, 2026
  • CVE-2026-89676CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: nfsd: fix stale s2s_cp_stateids IDR entry for async...
    📅 Updated: Sep 21, 2026
  • CVE-2026-89659CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: NFSD: Prevent client use-after-free during delegation revoke A...
    📅 Updated: Sep 21, 2026
  • CVE-2026-89660CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: NFSD: Prevent client use-after-free during admin state revocation...
    📅 Updated: Sep 21, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.