Skip to content
September 21, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
September 2026 Patch Tuesday Fixes 2 Exploited Windows Zero-Days Patch Tuesday zero-day CVE-2026-81963 and CVE-2026-85880 Windows elevation of privilege flaws exploited in the wild
  • Vulnerability Report

September 2026 Patch Tuesday Fixes 2 Exploited Windows Zero-Days

Do Son September 8, 2026 0
Read More Read more about September 2026 Patch Tuesday Fixes 2 Exploited Windows Zero-Days
Critical Fortinet Vulnerabilities Expose Networks to Attack Diagram illustrating the three new Fortinet vulnerabilities including CVE-2026-84390 and CVE-2026-26084
  • Vulnerability Report

Critical Fortinet Vulnerabilities Expose Networks to Attack

Do Son September 8, 2026 0
Read More Read more about Critical Fortinet Vulnerabilities Expose Networks to Attack
Windows 11 Performance Enhancements Target 8GB RAM Devices Windows 11 performance optimization showing improved memory usage and faster boot on 8GB RAM PCs
  • Windows

Windows 11 Performance Enhancements Target 8GB RAM Devices

Do Son September 8, 2026 0
Read More Read more about Windows 11 Performance Enhancements Target 8GB RAM Devices
Ivanti Fixes High Severity Ivanti Vulnerabilities in Sentry and EPMM High severity Ivanti vulnerabilities affecting Sentry and EPMM
  • Vulnerability Report

Ivanti Fixes High Severity Ivanti Vulnerabilities in Sentry and EPMM

Do Son September 8, 2026 0
Read More Read more about Ivanti Fixes High Severity Ivanti Vulnerabilities in Sentry and EPMM
PyPI File Hosting Errors: 502s Traced to Fastly Cache PyPI file hosting errors dashboard showing Fastly CDN 502 and 503 cache node failures
  • Technology

PyPI File Hosting Errors: 502s Traced to Fastly Cache

Do Son September 8, 2026 0
Read More Read more about PyPI File Hosting Errors: 502s Traced to Fastly Cache
Broadcom Removes VDDK Downloads, Complicating VMware Migrations Broadcom VDDK download removal error screen halting a VMware migration process
  • Technology

Broadcom Removes VDDK Downloads, Complicating VMware Migrations

Do Son September 8, 2026 0
Read More Read more about Broadcom Removes VDDK Downloads, Complicating VMware Migrations
ONLYOFFICE ownCloud Plugin SSRF Vulnerability ONLYOFFICE ownCloud plugin SSRF vulnerability CVE-2026-84282
  • Vulnerability Report

ONLYOFFICE ownCloud Plugin SSRF Vulnerability

Do Son September 8, 2026 0
Read More Read more about ONLYOFFICE ownCloud Plugin SSRF Vulnerability
Ivanti Neurons for ITSM Remote Code Execution Flaws: 8 CVEs, CVSS Up to 9.9 Ivanti Neurons ITSM remote code execution deserialization missing authorization CVE-2026-12744 CVE-2026-12650 critical vulnerability patch
  • Vulnerability Report

Ivanti Neurons for ITSM Remote Code Execution Flaws: 8 CVEs, CVSS Up to 9.9

Do Son September 8, 2026 0
Read More Read more about Ivanti Neurons for ITSM Remote Code Execution Flaws: 8 CVEs, CVSS Up to 9.9
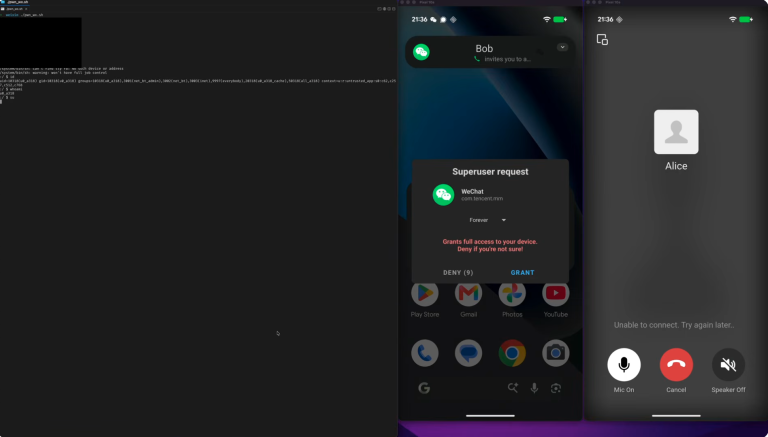
WeWorm: First Zero-Click Worm Spreads Through WeChat Calls on iOS and Android WeWorm first zero-click worm WeChat VoIP RCE iOS Android Calif security research
  • Vulnerability Report

WeWorm: First Zero-Click Worm Spreads Through WeChat Calls on iOS and Android

Do Son September 8, 2026 0
Read More Read more about WeWorm: First Zero-Click Worm Spreads Through WeChat Calls on iOS and Android
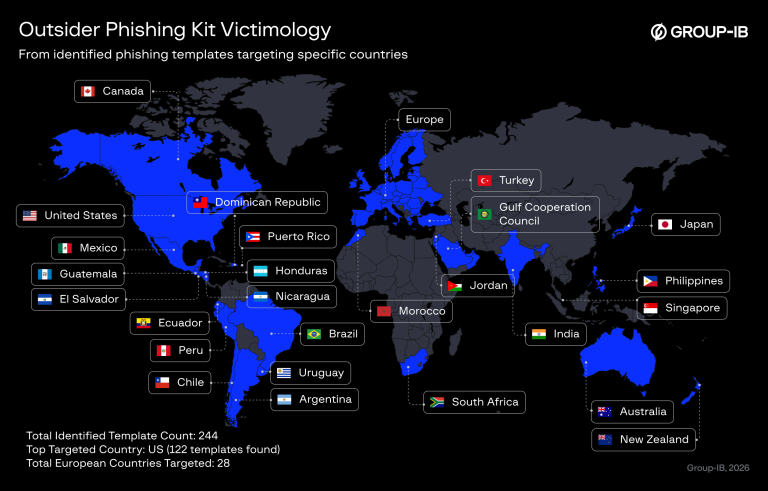
Outsider Phishing Kit Survives Operation Ghost Hook Takedown Outsider Phishing Kit tracking panel and ChenLun Outsider PhaaS kit dashboard
  • Cybercriminals

Outsider Phishing Kit Survives Operation Ghost Hook Takedown

Do Son September 8, 2026 0
Read More Read more about Outsider Phishing Kit Survives Operation Ghost Hook Takedown
Reflectiz Launches Agentic Pentesting for Websites: Up to 10x Coverage vs Conventional Pentests image_5_1788857508pakUwabkhz
  • Press Release

Reflectiz Launches Agentic Pentesting for Websites: Up to 10x Coverage vs Conventional Pentests

cybernewswire September 8, 2026 0
Read More Read more about Reflectiz Launches Agentic Pentesting for Websites: Up to 10x Coverage vs Conventional Pentests
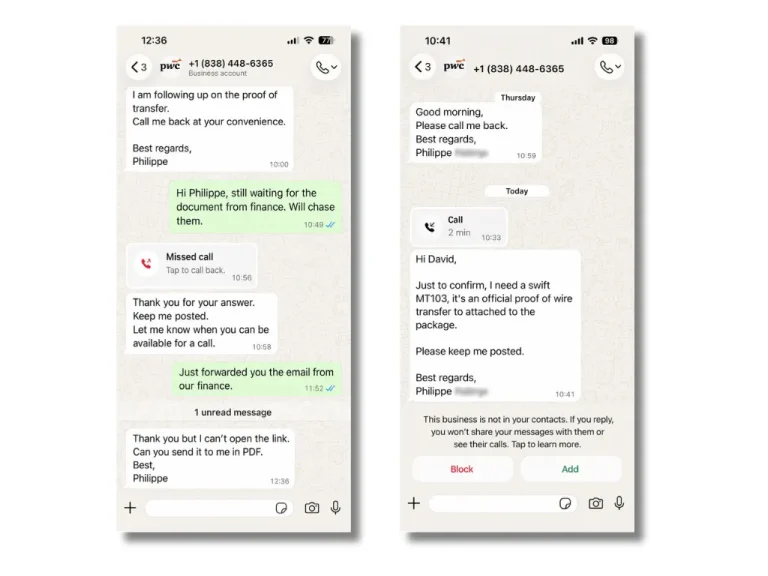
Phantom Deal Scam Targets Executives With Fake NDAs Phantom Deal campaign document tracking diagram illustrating the Phantom Deal scam
  • Cybercriminals

Phantom Deal Scam Targets Executives With Fake NDAs

Do Son September 8, 2026 0
Read More Read more about Phantom Deal Scam Targets Executives With Fake NDAs
September 2026 SAP Security Patch Day Fixes Critical Flaws September 2026 SAP Security Patch Day dashboard showing CVE-2026-44756 alerts
  • Vulnerability Report

September 2026 SAP Security Patch Day Fixes Critical Flaws

Do Son September 8, 2026 0
Read More Read more about September 2026 SAP Security Patch Day Fixes Critical Flaws
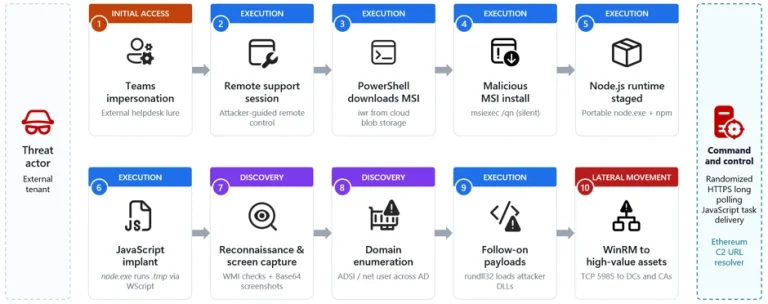
Microsoft Teams IT Support Impersonation Leads to Domain Takeover Microsoft Teams IT support impersonation attack chain from external tenant contact to Node.js implant and WinRM lateral movement toward domain controllers
  • Cybercriminals

Microsoft Teams IT Support Impersonation Leads to Domain Takeover

Do Son September 8, 2026 0
Read More Read more about Microsoft Teams IT Support Impersonation Leads to Domain Takeover
Chinese Actor Gambling Goblin Hijacks Brazilian Gov Sites Gambling Goblin campaign targeting government servers with Gambling Goblin malware
  • Cybercriminals

Chinese Actor Gambling Goblin Hijacks Brazilian Gov Sites

Do Son September 8, 2026 0
Read More Read more about Chinese Actor Gambling Goblin Hijacks Brazilian Gov Sites
ASUS Patches Control Center Express and Armoury Crate Flaws ASUS Control Center Express and Armoury Crate vulnerabilities allowing host takeover and NTLM hash theft, fixed in the latest software update
  • Vulnerability Report

ASUS Patches Control Center Express and Armoury Crate Flaws

Do Son September 8, 2026 0
Read More Read more about ASUS Patches Control Center Express and Armoury Crate Flaws
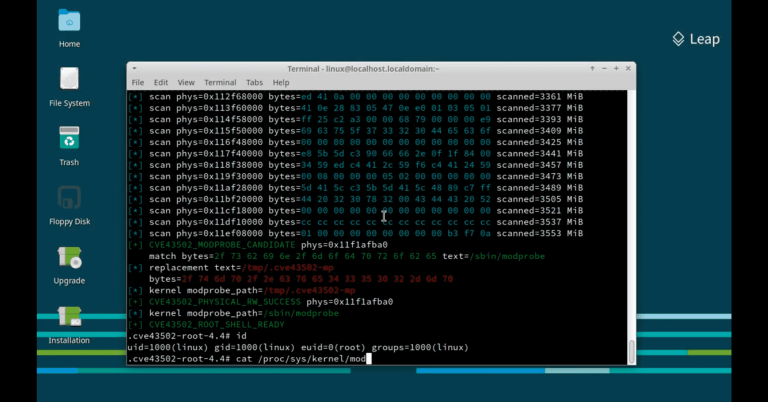
Public PoC Disclosed for ZcopyReaper Linux Vulnerability (CVE-2026-43502) ZcopyReaper Linux vulnerability PoC exploit code execution in the Linux kernel
  • Vulnerability Report

Public PoC Disclosed for ZcopyReaper Linux Vulnerability (CVE-2026-43502)

Do Son September 8, 2026 0
Read More Read more about Public PoC Disclosed for ZcopyReaper Linux Vulnerability (CVE-2026-43502)
Liquid Network Security Incident: The White Hat Dilemma Liquid Network hack diagram showing Bitcoin transfer and white hat bounty negotiation
  • Cybercriminals

Liquid Network Security Incident: The White Hat Dilemma

Do Son September 8, 2026 0
Read More Read more about Liquid Network Security Incident: The White Hat Dilemma
Windows 11 Battery Widget: New Connected Device Status Windows 11 battery widget displaying connected peripheral power levels
  • Windows

Windows 11 Battery Widget: New Connected Device Status

Do Son September 8, 2026 0
Read More Read more about Windows 11 Battery Widget: New Connected Device Status
Pegasus Spyware Hits Serbian Student Activist via Zero-Click iMessage Pegasus spyware zero-click iMessage infection on a Serbian student activist iPhone, part of the largest documented surveillance wave in Serbia
  • Malware

Pegasus Spyware Hits Serbian Student Activist via Zero-Click iMessage

Do Son September 8, 2026 0
Read More Read more about Pegasus Spyware Hits Serbian Student Activist via Zero-Click iMessage
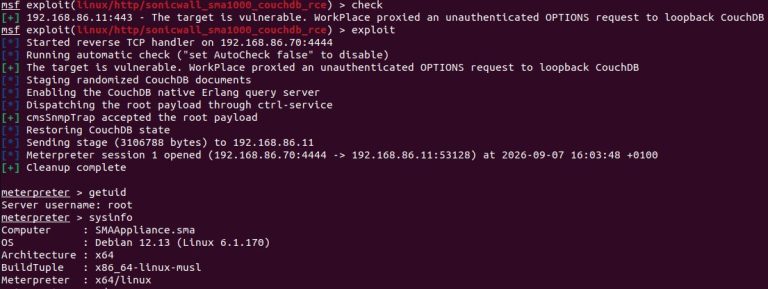
SonicWall SMA 1000 Vulnerabilities Exploited in Wild (PoC) SonicWall SMA 1000 vulnerabilities being exploited using the SonicWall SMA 1000 exploit chain
  • Vulnerability Report

SonicWall SMA 1000 Vulnerabilities Exploited in Wild (PoC)

Do Son September 8, 2026 0
Read More Read more about SonicWall SMA 1000 Vulnerabilities Exploited in Wild (PoC)
JetBrains Vulnerabilities: 29 Flaws Patched in Hub and YouTrack Security bulletin addressing critical JetBrains vulnerabilities and JetBrains vulnerabilities
  • Vulnerability Report

JetBrains Vulnerabilities: 29 Flaws Patched in Hub and YouTrack

Do Son September 8, 2026 0
Read More Read more about JetBrains Vulnerabilities: 29 Flaws Patched in Hub and YouTrack
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-58138CVSS 9.8
    Orkes Conductor 3.21.21 before 3.30.2 contains an unauthenticated remote code execution vulnerability that allows remote attackers to execute...
    Admin intel📅 Updated: Sep 20, 2026
  • CVE-2026-86124CVSS 9.8
    AutoAgent contains an unauthenticated remote code execution vulnerability in the TCP server that binds to all interfaces and...
    Admin intel📅 Updated: Sep 19, 2026
  • CVE-2025-39682CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: tls: fix handling of zero-length records on the...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2025-39964CVSS 7.8
    In the Linux kernel, the following vulnerability has been resolved: crypto: af_alg - Disallow concurrent writes in af_alg_sendmsg...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2026-53266CVSS 8.8
    In the Linux kernel, the following vulnerability has been resolved: netfilter: bridge: make ebt_snat ARP rewrite writable The...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2026-76460CVSS 10.0
    A vulnerability in an API of Cisco Identity Services Engine (ISE) could allow an unauthenticated, remote attacker to...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
  • CVE-2026-89026CVSS 9.8
    The Issabel Framework, the web framework supporting Issabel PBX software, before commit b97dbaf contains a hard-coded HS256 JWT...
    Admin intel📅 Updated: Sep 16, 2026
  • CVE-2026-58704
    In Cellular Modem, there is a possible permission bypass due to a logic error in the code. This...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-94301CVSS 9.8
    The fix for CVE-2026-47065/ZDRES-232 ("resolveProxyClass Not Overridden - acceptMatchers Filter Bypass via java.lang.reflect.Proxy"), released on 2026-06-02 and announced...
    📅 Updated: Sep 21, 2026
  • CVE-2026-90042CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ceph: properly decrypt filenames in vmalloc() buffers The...
    📅 Updated: Sep 21, 2026
  • CVE-2026-90036CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: NFSD: Prevent client use-after-free during blocked-lock reaping A...
    📅 Updated: Sep 21, 2026
  • CVE-2026-90037CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: NFSD: Prevent client use-after-free during close_lru reaping An...
    📅 Updated: Sep 21, 2026
  • CVE-2026-89708CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: nfsd: RCU-protect cl_cb_session to fix use-after-free on session...
    📅 Updated: Sep 21, 2026
  • CVE-2026-89676CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: nfsd: fix stale s2s_cp_stateids IDR entry for async...
    📅 Updated: Sep 21, 2026
  • CVE-2026-89659CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: NFSD: Prevent client use-after-free during delegation revoke A...
    📅 Updated: Sep 21, 2026
  • CVE-2026-89660CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: NFSD: Prevent client use-after-free during admin state revocation...
    📅 Updated: Sep 21, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.