CVE-2026-123747: OpenPrinting pappl-retrofit Publicly Disclosed Path Traversal and Proof-of-Concept Exploit Fixed
 Do Son
TL;DR
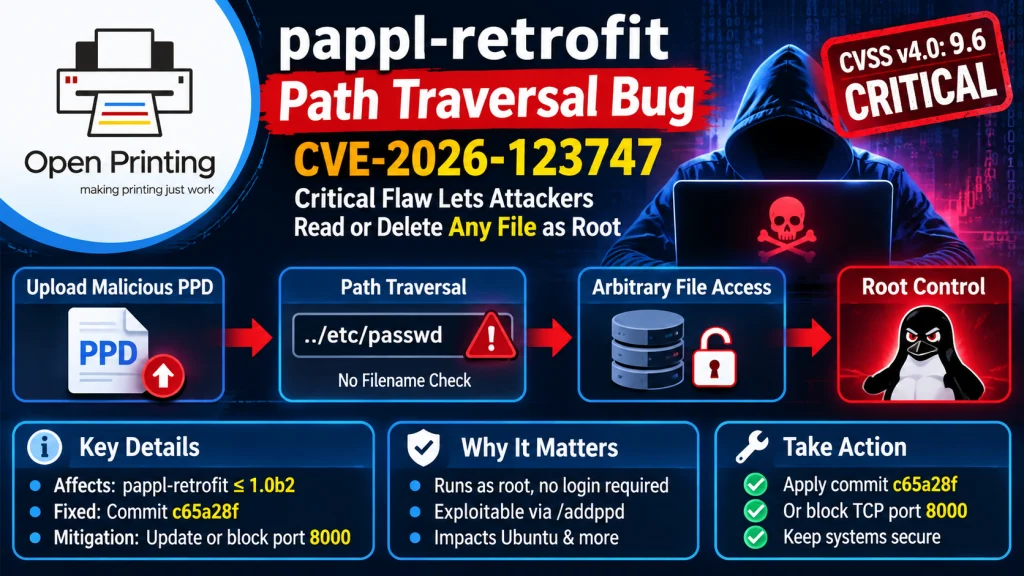
OpenPrinting devs fixed a critical pappl-retrofit path traversal bug after researchers publicly disclosed the full flaw details and proof-of-concept (PoC) exploit code. Tracked as CVE-2026-123747 (CVSS 9.6), the bug lets remote attackers upload or delete any file as root. Linux admins must apply commit c65a28f or block port 8000 right away.
- CVE: CVE-2026-123747
- CVSS: 7.3 (High · CVSSv3)
- Product: OpenPrinting pappl-retrofit
- Affected: ≤ 1.0b2
- Impact: Pappl-retrofit: directory traversal in the add-ppdfiles and delete-ppdfiles actions
- Status: No confirmed exploitation yet
- Action: See vendor advisory
Why It Matters
The pappl-retrofit tool adapts old CUPS printer drivers for modern Linux systems like Ubuntu. By default, the legacy-printer-app service runs as root with no login check and listens on 0.0.0.0:8000.
Analysts Danilo Egea Gondolfo, Jorge Castro, and 7A Security reported the flaw. Because the public report shares working PoC exploit commands, unpatched hosts face high risk. Currently, no active attacks in the wild have been confirmed. While exact install counts remain private, the tool ships in Ubuntu and Linux desktop repos.
How the Attack Works
Unsanitized PPD File Operations
First, this pappl-retrofit path traversal flaw stems from missing file name checks (CWE-22) on the /addppd page. When a user uploads or deletes a driver file, the app joins the name straight to the base folder path. As the report states, “To trigger the vulnerability one just need to add ../ to the file name.”
Consequently, an attacker can write or delete files in any system folder as root. As the author noted, “It can be used to upload a file to any directory in the system AND delete any file too.” Attackers can also upload a rogue driver with a cupsFilter rule and print a test page to run root commands.
Affected Versions
CVE-2026-123747 hits OpenPrinting pappl-retrofit versions 1.0b2 and older. On RHEL 10, CentOS Stream 10, and Fedora, a package bug leaves out the /var/lib/legacy-printer-app/ppd folder by default. That missing folder lowers the score to 7.3 High unless root creates the path.
Patch and Mitigation Steps
Devs fixed the pappl-retrofit path traversal flaw in master commit c65a28f (OCU-01-020). That patch blocks driver names that leave the upload folder. Admins should update to a build with commit c65a28f right away. Until patched, teams must stop the legacy-printer-app service or block TCP port 8000 with a firewall.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
