Skip to content
September 21, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
StyleSmuggler: Magento Zero-Day RCE Exploited in the Wild StyleSmuggler Magento zero-day allowing unauthenticated remote code execution against Adobe Commerce stores under active attack
  • Vulnerability Report

StyleSmuggler: Magento Zero-Day RCE Exploited in the Wild

Do Son September 5, 2026 0
Read More Read more about StyleSmuggler: Magento Zero-Day RCE Exploited in the Wild
US Offers $10M for IRGC Cyber Leader US Rewards for Justice poster offering $10 million for information on Iranian IRGC cyber commander Amir Yaryab
  • Cybercriminals

US Offers $10M for IRGC Cyber Leader

Do Son September 5, 2026 0
Read More Read more about US Offers $10M for IRGC Cyber Leader
Coder Registry Attack: Hijacked Cloudflare Pool Served Malicious Terraform Modules Coder registry attack serving malicious Terraform modules from a hijacked Cloudflare pool
  • Cybercriminals

Coder Registry Attack: Hijacked Cloudflare Pool Served Malicious Terraform Modules

Do Son September 5, 2026 0
Read More Read more about Coder Registry Attack: Hijacked Cloudflare Pool Served Malicious Terraform Modules
Google Workspace Integrates Gemini Live Features Google Workspace interface displaying Gemini Live integration across Gmail, Docs, and Keep applications
  • Technology

Google Workspace Integrates Gemini Live Features

Do Son September 5, 2026 0
Read More Read more about Google Workspace Integrates Gemini Live Features
CVE-2026-75754 (CVSS 10): ASUS Control Center Root RCE ASUS Control Center vulnerability CVE-2026-75754 allowing unauthenticated attackers to gain a root shell and full remote control
  • Vulnerability Report

CVE-2026-75754 (CVSS 10): ASUS Control Center Root RCE

Do Son September 4, 2026 0
Read More Read more about CVE-2026-75754 (CVSS 10): ASUS Control Center Root RCE
Your AI Security Tool Has One Approval Button. It Needs Four Diagram illustrating Langflow OSS vulnerabilities and CVE-2026-10134 execution paths
  • Technique

Your AI Security Tool Has One Approval Button. It Needs Four

Do Son September 4, 2026 0
Read More Read more about Your AI Security Tool Has One Approval Button. It Needs Four
The Gentlemen Ransomware Deploys in Under 24 Hours The Gentlemen ransomware attack chain showing GOLD SHERWOOD affiliates using GentleKiller EDR killer and Rclone data exfiltration
  • Malware

The Gentlemen Ransomware Deploys in Under 24 Hours

Do Son September 4, 2026 0
Read More Read more about The Gentlemen Ransomware Deploys in Under 24 Hours
Trezor Data Breach at ShipMonk Grows to 80,000 Customers Trezor data breach notice showing customer order data exposed through shipping provider ShipMonk in a third-party vendor breach
  • Data Leak

Trezor Data Breach at ShipMonk Grows to 80,000 Customers

Do Son September 4, 2026 0
Read More Read more about Trezor Data Breach at ShipMonk Grows to 80,000 Customers
FreeSWITCH api-chat RCE Exploited in the Wild, Patch Now FreeSWITCH api-chat vulnerability exploited in the wild for remote code execution via SIP MESSAGE on FusionPBX servers
  • Vulnerability

FreeSWITCH api-chat RCE Exploited in the Wild, Patch Now

Do Son September 4, 2026 0
Read More Read more about FreeSWITCH api-chat RCE Exploited in the Wild, Patch Now
Toy Ghouls Backdoor Uses HiveMQ and Element for C2 Rust supply chain attack on arrayref crate with proc-macro1 typosquat and DPRK infrastructure overlap
  • Cybercriminals

Toy Ghouls Backdoor Uses HiveMQ and Element for C2

Do Son September 4, 2026 0
Read More Read more about Toy Ghouls Backdoor Uses HiveMQ and Element for C2
AWS Password Spraying Campaign Targets Root Accounts Chart showing an AWS password spraying campaign targeting root logins with AWS password spraying
  • Cybercriminals

AWS Password Spraying Campaign Targets Root Accounts

Do Son September 4, 2026 0
Read More Read more about AWS Password Spraying Campaign Targets Root Accounts
Spring Ring Vishing Campaign Targets Microsoft Teams Anatomy of the Spring Ring vishing campaign and Microsoft Teams phishing attacks
  • Cybercriminals

Spring Ring Vishing Campaign Targets Microsoft Teams

Do Son September 4, 2026 0
Read More Read more about Spring Ring Vishing Campaign Targets Microsoft Teams
AiTM Phishing Campaign Targets Healthcare via Account Takeovers Layoff Phishing Scam Remcos RAT Malware Aruba Phishing, Phishing-as-a-Service PyPI, phishing CVE-2024-25608 PyPI Phishing, Credential Theft
  • Cybercriminals

AiTM Phishing Campaign Targets Healthcare via Account Takeovers

Do Son September 4, 2026 0
Read More Read more about AiTM Phishing Campaign Targets Healthcare via Account Takeovers
Apache Allura Security Vulnerabilities Patched in v1.21.0 Apache Allura security vulnerabilities update
  • Vulnerability Report

Apache Allura Security Vulnerabilities Patched in v1.21.0

Do Son September 4, 2026 0
Read More Read more about Apache Allura Security Vulnerabilities Patched in v1.21.0
CVE-2026-52924 PoC Exploit Disclosed: 9.8 CVSS Linux Root Privilege Escalation Linux CVE-2026-52924 details and Linux CVE-2026-52924 PoC exploit release
  • Vulnerability Report

CVE-2026-52924 PoC Exploit Disclosed: 9.8 CVSS Linux Root Privilege Escalation

Do Son September 4, 2026 0
Read More Read more about CVE-2026-52924 PoC Exploit Disclosed: 9.8 CVSS Linux Root Privilege Escalation
GPT-6 Astra Updates Codex Pricing GPT-6 Astra Codex pricing token cost chart
  • Technology

GPT-6 Astra Updates Codex Pricing

Do Son September 4, 2026 0
Read More Read more about GPT-6 Astra Updates Codex Pricing
TP-Link Archer AX55 Flaws Expose Routers to Code Execution TP-Link Archer AX55 vulnerability advisory showing EasyMesh buffer overflow and hardcoded RSA key flaws CVE-2026-18167 CVE-2026-18330
  • Vulnerability Report

TP-Link Archer AX55 Flaws Expose Routers to Code Execution

Do Son September 4, 2026 0
Read More Read more about TP-Link Archer AX55 Flaws Expose Routers to Code Execution
Plex Issues Urgent Security Update for Media Server and Desktop Plex security update notice for Media Server 1.43.3 and Plex Desktop 1.115.0
  • Vulnerability Report

Plex Issues Urgent Security Update for Media Server and Desktop

Do Son September 4, 2026 0
Read More Read more about Plex Issues Urgent Security Update for Media Server and Desktop
CERN to Move 2,200 Accelerator Control Machines to Debian 13 CERN Debian migration of accelerator control computers from Red Hat to Debian 13
  • Linux

CERN to Move 2,200 Accelerator Control Machines to Debian 13

Do Son September 4, 2026 0
Read More Read more about CERN to Move 2,200 Accelerator Control Machines to Debian 13
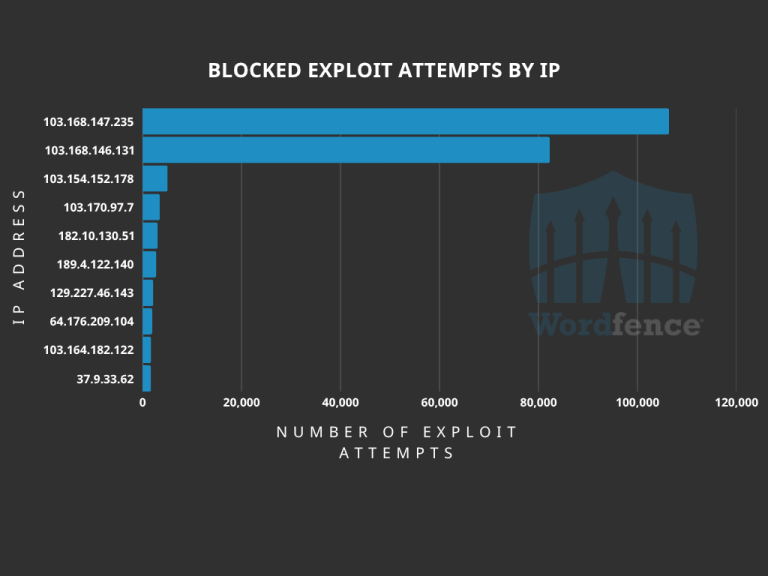
Super Forms Vulnerability Exploited in the Wild: 13,000 Sites Face 9.8 CVSS Remote Code Execution Super Forms vulnerability CVE-2026-14894 arbitrary file upload remote code execution exploited in the wild WordPress plugin diagram
  • Vulnerability Report

Super Forms Vulnerability Exploited in the Wild: 13,000 Sites Face 9.8 CVSS Remote Code Execution

Do Son September 4, 2026 0
Read More Read more about Super Forms Vulnerability Exploited in the Wild: 13,000 Sites Face 9.8 CVSS Remote Code Execution
Critical WHMCS Security Update Patches RCE Flaws WHMCS security update for CVE-2026-67399 remote code execution and CVE-2026-67398
  • Vulnerability Report

Critical WHMCS Security Update Patches RCE Flaws

Do Son September 4, 2026 0
Read More Read more about Critical WHMCS Security Update Patches RCE Flaws
BraZetsu Malware Framework Powers Initial Access Sales BraZetsu malware framework and BraZetsu malware framework operations diagram
  • Cybercriminals

BraZetsu Malware Framework Powers Initial Access Sales

Do Son September 4, 2026 0
Read More Read more about BraZetsu Malware Framework Powers Initial Access Sales
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-58138CVSS 9.8
    Orkes Conductor 3.21.21 before 3.30.2 contains an unauthenticated remote code execution vulnerability that allows remote attackers to execute...
    Admin intel📅 Updated: Sep 20, 2026
  • CVE-2026-86124CVSS 9.8
    AutoAgent contains an unauthenticated remote code execution vulnerability in the TCP server that binds to all interfaces and...
    Admin intel📅 Updated: Sep 19, 2026
  • CVE-2025-39682CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: tls: fix handling of zero-length records on the...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2025-39964CVSS 7.8
    In the Linux kernel, the following vulnerability has been resolved: crypto: af_alg - Disallow concurrent writes in af_alg_sendmsg...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2026-53266CVSS 8.8
    In the Linux kernel, the following vulnerability has been resolved: netfilter: bridge: make ebt_snat ARP rewrite writable The...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2026-76460CVSS 10.0
    A vulnerability in an API of Cisco Identity Services Engine (ISE) could allow an unauthenticated, remote attacker to...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
  • CVE-2026-89026CVSS 9.8
    The Issabel Framework, the web framework supporting Issabel PBX software, before commit b97dbaf contains a hard-coded HS256 JWT...
    Admin intel📅 Updated: Sep 16, 2026
  • CVE-2026-58704
    In Cellular Modem, there is a possible permission bypass due to a logic error in the code. This...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-69586CVSS 9.8
    Integer overflow or wraparound in Microsoft Windows PDF allows an unauthorized attacker to execute code over a network.
    📅 Updated: Sep 21, 2026
  • CVE-2026-69590CVSS 9.8
    Remote Code Execution in Windows Routing and Remote Access Service (RRAS) allows attacker to gain an unauthorized access...
    📅 Updated: Sep 21, 2026
  • CVE-2026-69595CVSS 9.8
    Use after free in Windows Services for NFS ONCRPC XDR Driver allows an unauthorized attacker to execute code...
    📅 Updated: Sep 21, 2026
  • CVE-2026-58491CVSS 9.3
    Warpgate is an open source SSH, HTTPS and MySQL bastion host for Linux. Prior to 0.25.5, the /@warpgate/api/sso/providers/:name/start...
    📅 Updated: Sep 21, 2026
  • CVE-2026-93765CVSS 9.1
    Mongoid contains an unsafe reflection weakness in the document persistence layer of its object-document mapping code. Input whose...
    📅 Updated: Sep 21, 2026
  • CVE-2026-85497CVSS 9.8
    CareCam CM2507 IP cameras store the device's root-account password using a fixed legacy password hash that provides insufficient...
    📅 Updated: Sep 21, 2026
  • CVE-2026-93742CVSS 9.9
    A weakness has been identified in Totolink A3002MU Hh-B20211125.1046. Affected by this issue is the function formWsc of...
    📅 Updated: Sep 21, 2026
  • CVE-2024-58385CVSS 9.8
    Yonyou U8 CRM contains an unauthenticated SQL injection vulnerability in the fillbacksettingedit.php configuration endpoint where the DontCheckLogin=1 parameter...
    📅 Updated: Sep 21, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.