 Do Son
Ivanti security advisories fix 13 flaws, including Ivanti Endpoint Manager RCE CVE-2026-121653 (CVSS 9.8) and CSA bug CVE-2026-121683.
Latest Security News
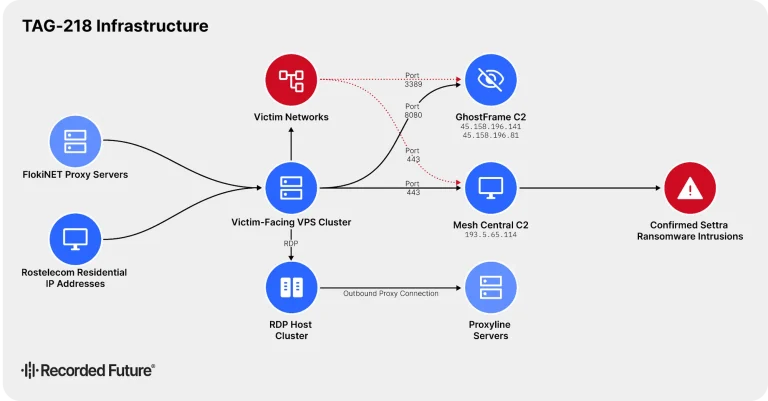
Recorded Future uncovered the GhostFrame ESXi implant Settra ransomware framework used by TAG-218 to hijack hypervisors and steal VM credentials.
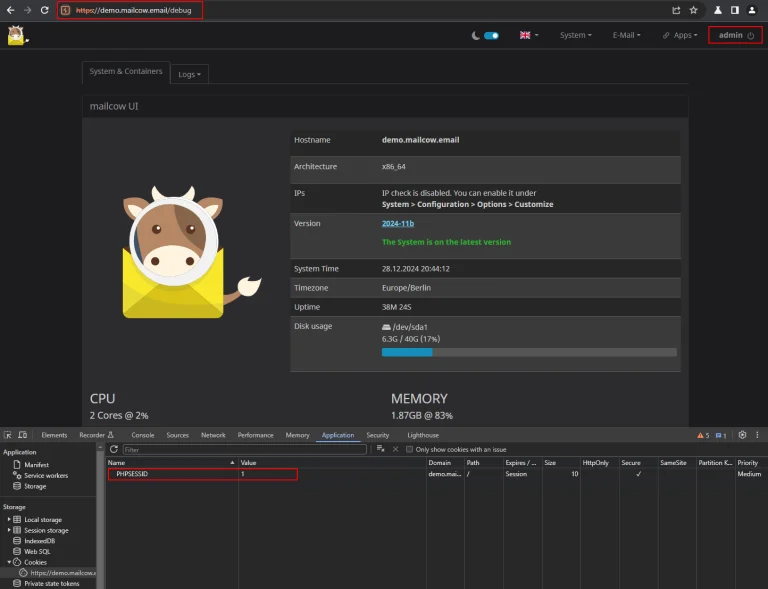
Details and proof-of-concept steps for five mailcow vulnerabilities are public, including a CVSS 9.1 cross-tenant RCE. Update to 2026-11.
Composer 2.11.2 and 2.2.32 fix three Composer vulnerabilities, including command execution via a crafted composer.lock file (CVSS 8.8).
The November 2026 OpenSSL security advisory fixes five Low-severity bugs in OpenSSL QUIC, AES-GCM-SIV and CMS. Releases are due December 1.
France attributed a destructive Iran refrigeration cyberattack impacting 700 sites to the IRGC group Shahid Kaveh, causing food spoilage and fires.
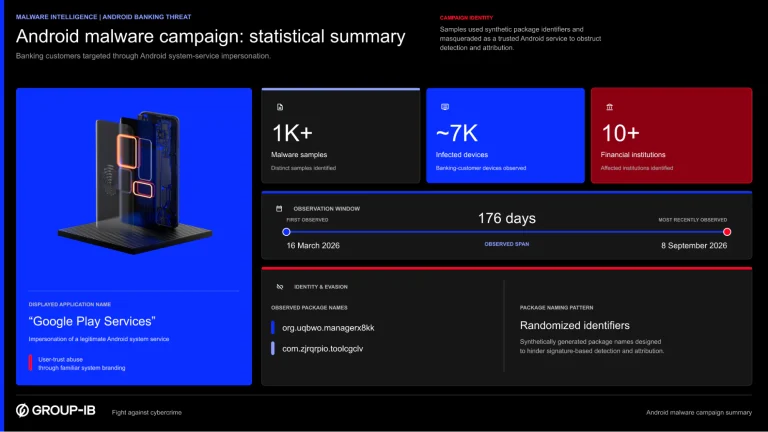
The Mirax Android RAT, a device takeover malware posing as Google Play Services, has infected thousands of phones to drain META bank accounts.
Bitdefender reveals the GhostMap Android flaw. See how the unpatched GhostMap Android flaw traps Android 10 to 17 phones in boot loops on app install.
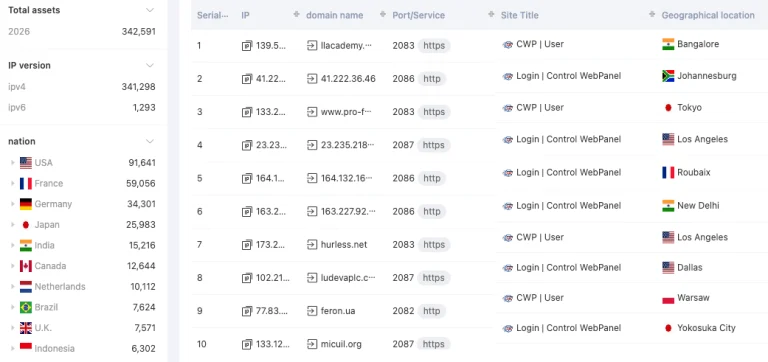
QiAnXin XLab uncovers the cwpdoor backdoor on Linux servers. See how the Control Web Panel cwpdoor backdoor hides in cwpsrv and suppresses access logs.
Apache Commons Codec 1.23.0 addresses CVE-2026-119078 and CVE-2026-124077, while Apache HTTP Server 2.4.70 fixes a heap buffer overflow.
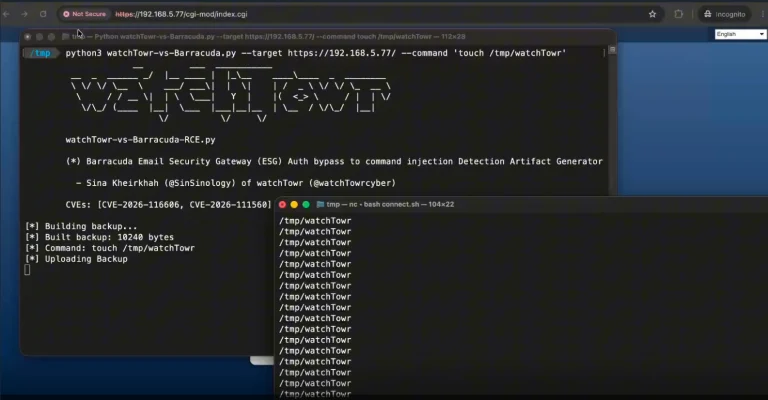
Attackers exploit a Barracuda ESG vulnerability chain (CVE-2026-116606, CVE-2026-111560) for root RCE after a proof-of-concept exploit went public.
Update Progress WS_FTP Server to 2025.0.5 now to patch CVE-2026-115338, CVE-2026-115341, and three other high-severity security vulnerabilities.
Latest Technology News
 cybernewswire
Miami, United States, 2nd November 2026, CyberNewswire
OpenAI announced new ChatGPT violence restrictions and teen safety protections, restricting weapon queries and terminating hazardous conversations.
Tech giants support a new AI training preference standard in robots.txt, giving publishers granular control over model training data.
Google Project Suncatcher achieved orbital AI inference using datacenter TPUs and Gemma 4 aboard a prototype satellite to generate space poetry.
OpenAI announced that ChatGPT Codex usage limits will merge under a shared token quota across Plus, Pro, and Business plans starting December 2026.
Anthropic unveiled the Claude Ultra subscription tier, removing 5-hour rate limits for verified accounts and bundling $200 in monthly API credits.
The rise of vibe manufacturing AI allows makers to transform conversational prompts into physical hardware, custom sheet metal, and printed circuit boards.
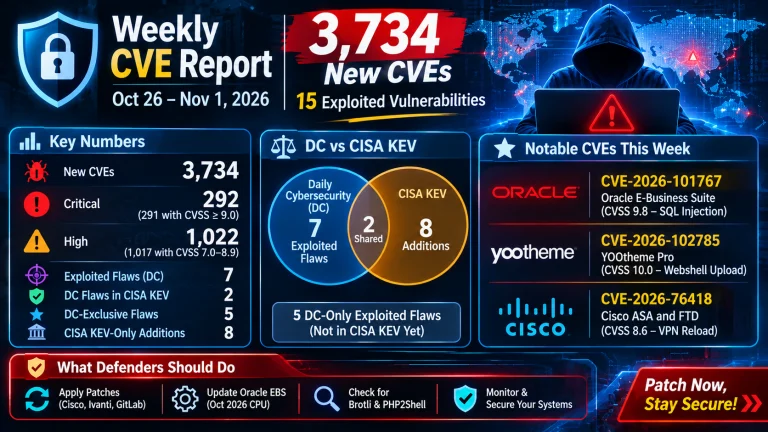
Our weekly CVE report for Oct 26-Nov 1, 2026 tracks 3,734 new CVEs and 15 exploited vulnerabilities, including Oracle EBS flaws not in CISA KEV.
Teams shipping new ads every week need creative testing platforms that can launch variations quickly, measure results...
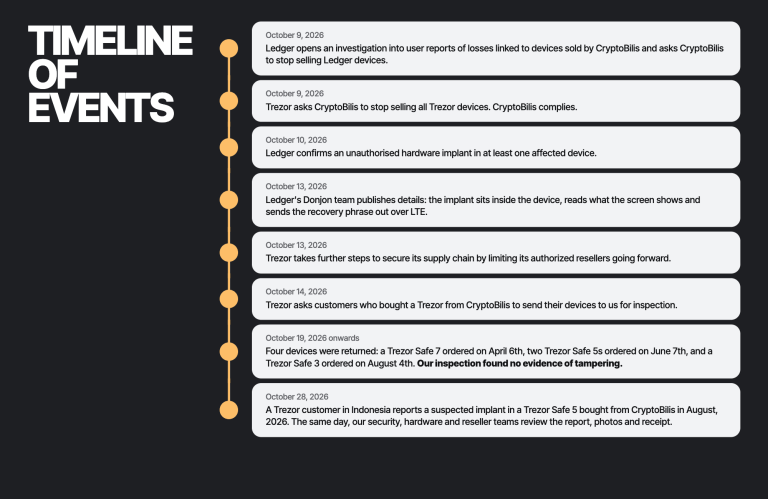
Trezor issued an alert after discovering a Trezor hardware wallet implant with a 4G module sold by compromised Southeast Asian reseller CryptoBilis.
Latest Security News
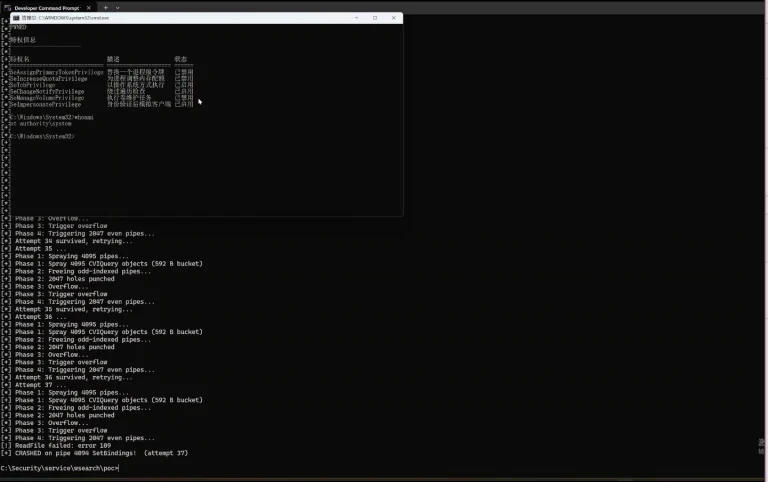
A proof-of-concept exploit for the Windows Search vulnerability CVE-2026-50679 is public. The heap overflow lets local users gain elevated privileges.
18 Apache Airflow vulnerabilities, including Celery code execution CVE-2026-68982, are fixed in Airflow 3.4.0, plus two Apache Storm flaws.
Logto vulnerabilities allow account takeover via Apple sign-in, MFA bypass and SAML login bypass. Upgrade to Logto 1.46.0 and patched packages now.
CISA KEV Catalog adds CVE-2026-123158, CVE-2026-116779, CVE-2026-123218, and CVE-2026-102895 after attackers exploit these four flaws in the wild.
Details and a proof-of-concept exploit for 33 N-central vulnerabilities are public. N-able took hosted N-central offline and is building a hotfix.
Google fixes Chrome zero-day CVE-2026-125350, exploited in the wild, plus 8 more flaws. Install the Chrome security update to 157.0.8103.50 now.
Roundcube Webmail 1.6.21 and 1.7.6 fix 17 bugs, including Sieve injection, SSRF and CSRF bypasses. Apply the Roundcube security update now.
QNAP warns that exploited Plex2Shell vulnerabilities in Plex Media Server 1.43.2 hit QNAP NAS users. Update to 1.43.3.10861 and check for compromise.
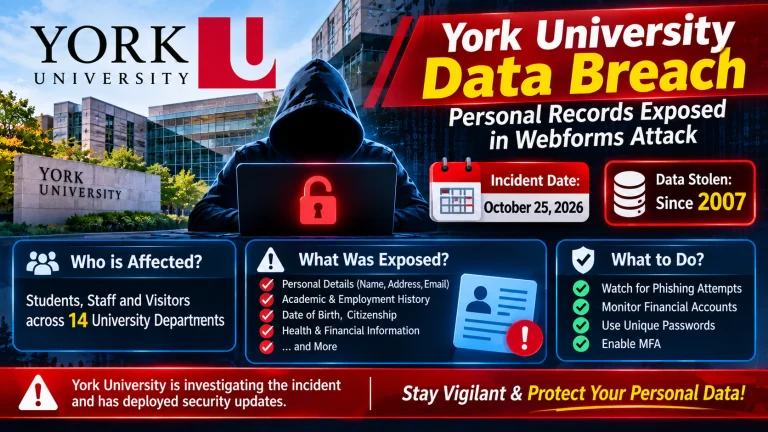
A York University data breach exposed records from 2007 to 2026 after a departmental webforms theft. Check which faculties and students are affected.
WP Duplicate vulnerability CVE-2026-123751 is exploited in the wild, letting attackers upload files and run code. No patch exists, so remove the plugin.
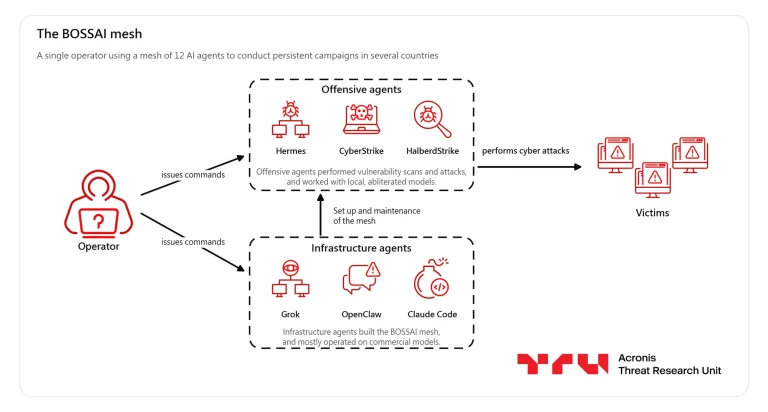
Acronis TRU uncovered the BOSSAI attack mesh Taiwan campaign using 12 AI agents to breach emergency services, banks, and universities in 11 countries.
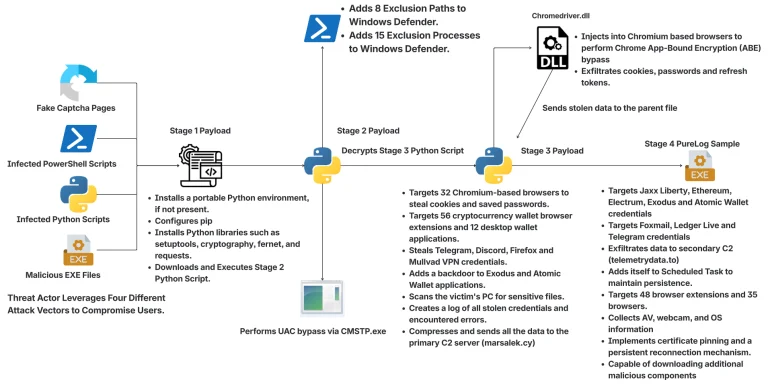
McAfee Labs uncovers Marsalek malware in fake game cheats. See how the dual-hook Marsalek malware drops PureLog to steal passwords from gamers and hackers.
Latest Technology News
OpenAI announced new ChatGPT violence restrictions and teen safety protections, restricting weapon queries and terminating hazardous conversations.
Tech giants support a new AI training preference standard in robots.txt, giving publishers granular control over model training data.
Google Project Suncatcher achieved orbital AI inference using datacenter TPUs and Gemma 4 aboard a prototype satellite to generate space poetry.
OpenAI announced that ChatGPT Codex usage limits will merge under a shared token quota across Plus, Pro, and Business plans starting December 2026.
Anthropic unveiled the Claude Ultra subscription tier, removing 5-hour rate limits for verified accounts and bundling $200 in monthly API credits.
The rise of vibe manufacturing AI allows makers to transform conversational prompts into physical hardware, custom sheet metal, and printed circuit boards.
Our weekly CVE report for Oct 26-Nov 1, 2026 tracks 3,734 new CVEs and 15 exploited vulnerabilities, including Oracle EBS flaws not in CISA KEV.
Teams shipping new ads every week need creative testing platforms that can launch variations quickly, measure results...
Trezor issued an alert after discovering a Trezor hardware wallet implant with a 4G module sold by compromised Southeast Asian reseller CryptoBilis.
New Microsoft 365 storage changes replace the 6TB individual allocation with a shared 2TB pool for Family plans without lowering subscription prices.