 Do Son
Apple issued the iOS 27.2.1 security update to fix critical iMessage eavesdropping flaws, zero-click Bluetooth pairing, and wireless memory bugs.
Latest Security News
Patch critical Mongoose security flaws CVE-2026-125120 (CVSS 9.8) and CVE-2026-125117 affecting 4.8 million weekly npm users against NoSQL injection.
November SAP Security Patch Day fixes 38 CVEs, including nine Critical SAP NetWeaver, Web Dispatcher and Gateway flaws rated up to CVSS 10.0.
CERT/CC details six FrodoBots EarthRover vulnerabilities, including root remote code execution via MQTT. Patch status, risks and mitigations.
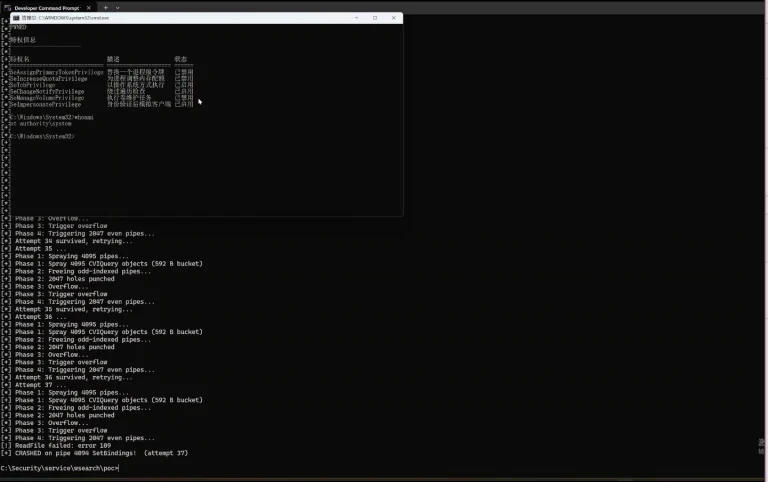
A proof-of-concept exploit for the Windows Search vulnerability CVE-2026-50679 is public. The heap overflow lets local users gain elevated privileges.
18 Apache Airflow vulnerabilities, including Celery code execution CVE-2026-68982, are fixed in Airflow 3.4.0, plus two Apache Storm flaws.
Logto vulnerabilities allow account takeover via Apple sign-in, MFA bypass and SAML login bypass. Upgrade to Logto 1.46.0 and patched packages now.
CISA KEV Catalog adds CVE-2026-123158, CVE-2026-116779, CVE-2026-123218, and CVE-2026-102895 after attackers exploit these four flaws in the wild.
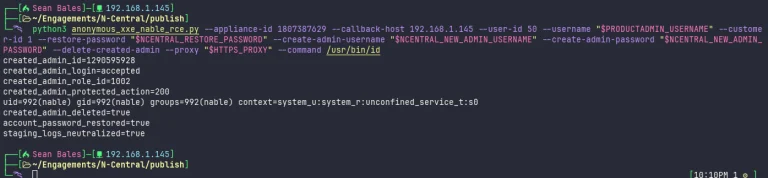
Details and a proof-of-concept exploit for 33 N-central vulnerabilities are public. N-able took hosted N-central offline and is building a hotfix.
Google fixes Chrome zero-day CVE-2026-125350, exploited in the wild, plus 8 more flaws. Install the Chrome security update to 157.0.8103.50 now.
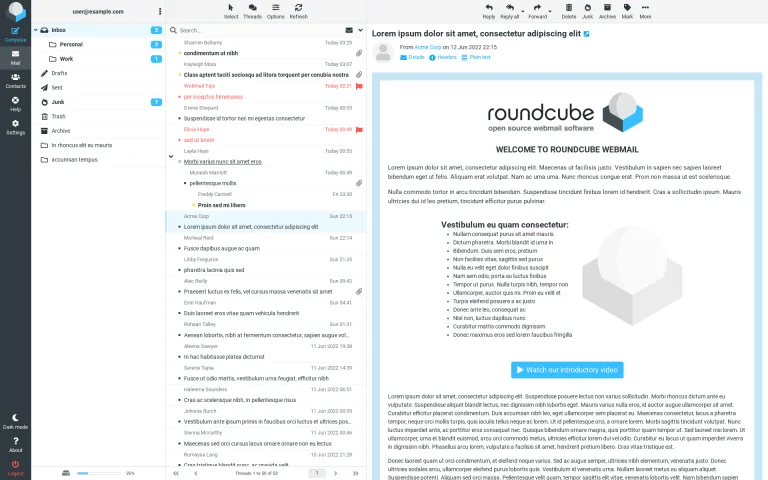
Roundcube Webmail 1.6.21 and 1.7.6 fix 17 bugs, including Sieve injection, SSRF and CSRF bypasses. Apply the Roundcube security update now.
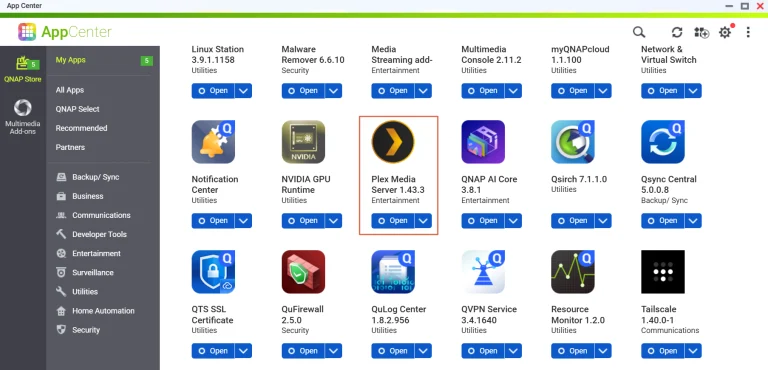
QNAP warns that exploited Plex2Shell vulnerabilities in Plex Media Server 1.43.2 hit QNAP NAS users. Update to 1.43.3.10861 and check for compromise.
Latest Technology News
New Microsoft 365 storage changes replace the 6TB individual allocation with a shared 2TB pool for Family plans without lowering subscription prices.
The new Claude CarPlay update introduces hands-free voice interaction for drivers, split-screen multitasking, and multi-account switching.

Players rarely open a game service with a product in mind. They open it with a question:...
Forex markets move continuously as currencies respond to economic data, interest-rate expectations, geopolitical developments, and changing market...
Reddit is testing a Reddit mandatory login policy to thwart unauthorized AI scrapers and counteract declining organic search traffic.
Won a contract but missing proof? Fast Cyber Essentials and a fast pen test help suppliers satisfy procurement without losing momentum.
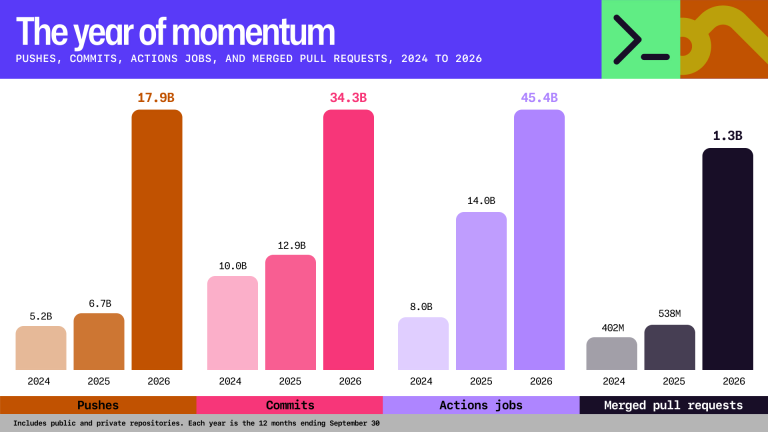
GitHub code activity reached historic highs in 2026, with over 7.3 billion monthly commits and 40% of pull requests drafted by AI coding agents.
The dramatic Stack Overflow question decline dropped monthly posts below 1,000 as developers embrace autonomous AI coding agents.
Learn how to identify automated visitors, set sensible access rules, and protect sensitive website actions without blocking useful automation.
Anthropic updated Claude Code permission modes with a toggle to suppress confirmation prompts for dangerous deletion commands during automated workflows.
Latest Security News
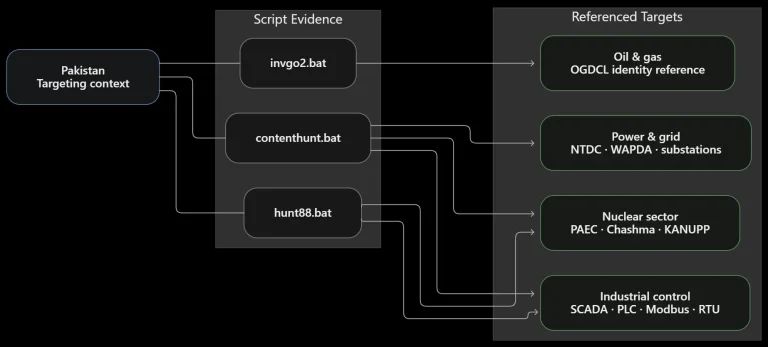
Researchers found an open server hosting a DoNot APT toolkit targeting Pakistan nuclear, power grid, and ICS networks with Inveigh and Go shells.
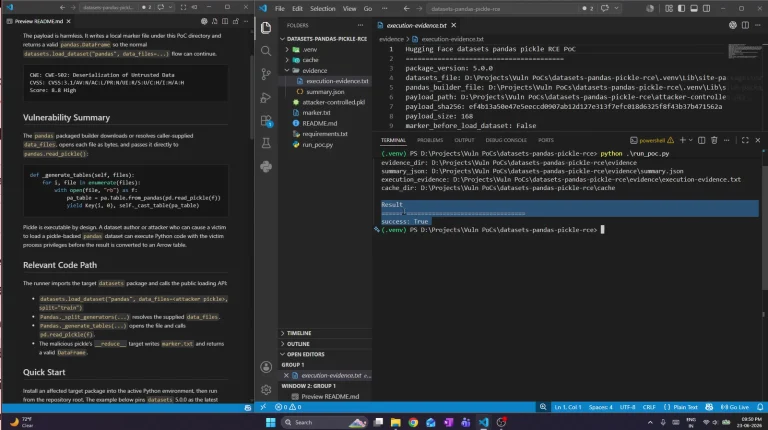
Hugging Face datasets RCE CVE-2026-57845 (CVSS 8.8) has a public proof-of-concept. The library sees 38M monthly downloads, and no fixed release exists.
Openwave Webtop vulnerability CVE-2026-111793 is exploited in the wild, per JPCERT/CC. Upgrade Webtop Media Transcoder to 1.1.22.0 or later.
ModSecurity vulnerabilities CVE-2026-104269 and CVE-2026-73857 now have public details and a proof-of-concept. Upgrade to libmodsecurity 3.0.17.
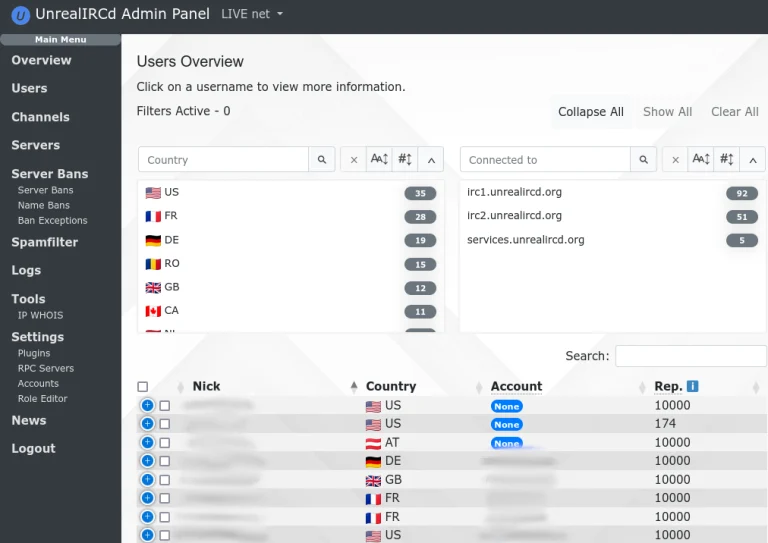
UnrealIRCd vulnerability CVE-2026-114713 is exploited in the wild, letting users run IRCOp commands. Hot-patch or upgrade to 6.2.7.1 now.
A uutils coreutils vulnerability (CVSS 9.9) let translation files inject code; details and a proof-of-concept are now public. Upgrade to uucore 0.12.0.
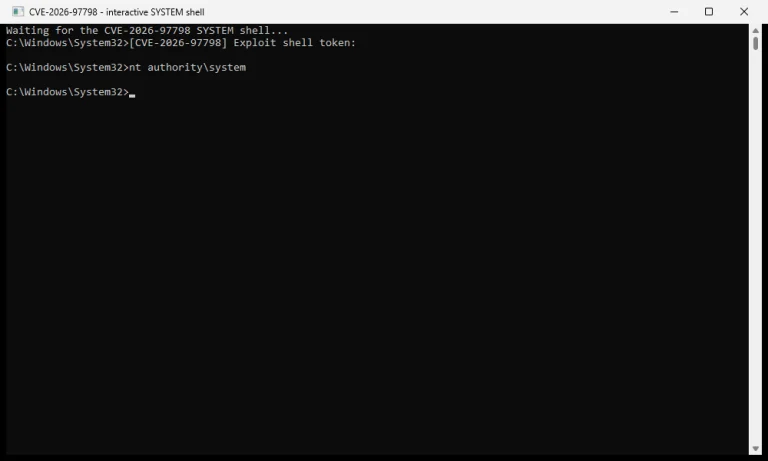
A proof-of-concept exploit for CVE-2026-97798, a Windows Error Reporting vulnerability, gives a SYSTEM shell. Install the October 2026 update now.
IBM API Connect vulnerabilities: 208 flaws, including authentication bypass CVE-2026-17301 and hard-coded credentials. Apply IBM's fixes now.
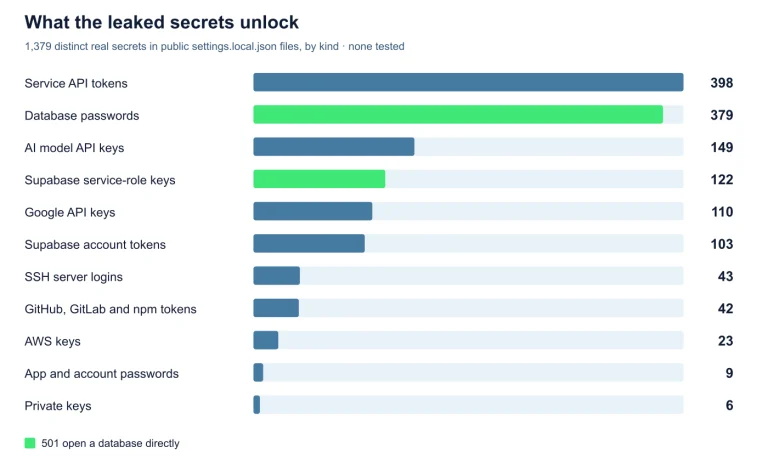
Apiiro found Claude Code leaking secrets in 1,994 repos via a GitHub settings.local.json exposure. Learn how to check and secure your credentials.
Anubis Ransomware Attackers Deploy Custom Lindnor Backdoor and 13 Security Killers Against US Target
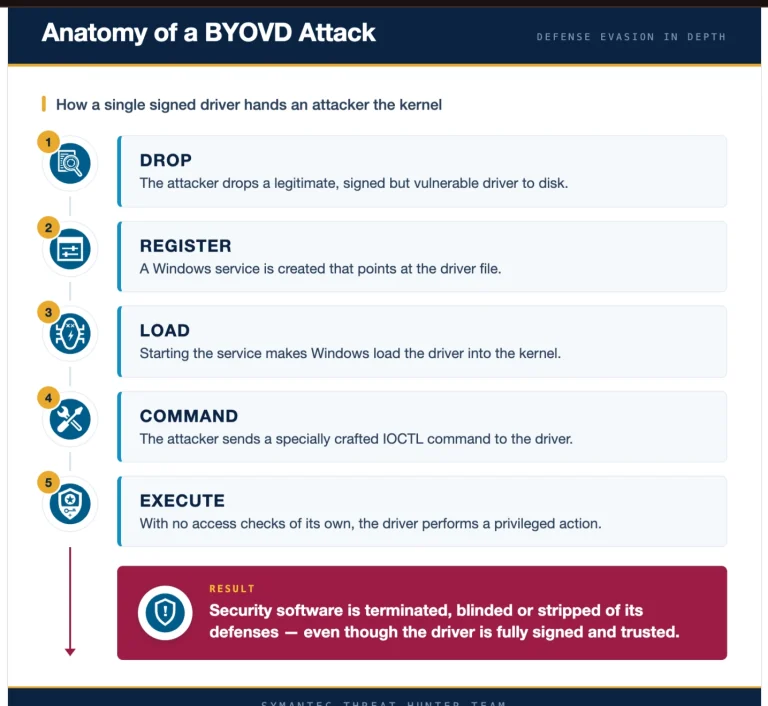
Anubis Ransomware Attackers Deploy Custom Lindnor Backdoor and 13 Security Killers Against US Target
Symantec uncovers the Lindnor backdoor in a foiled attack. See how the Anubis ransomware Lindnor backdoor chain used 13 EDR killers and 5 BYOVD drivers.
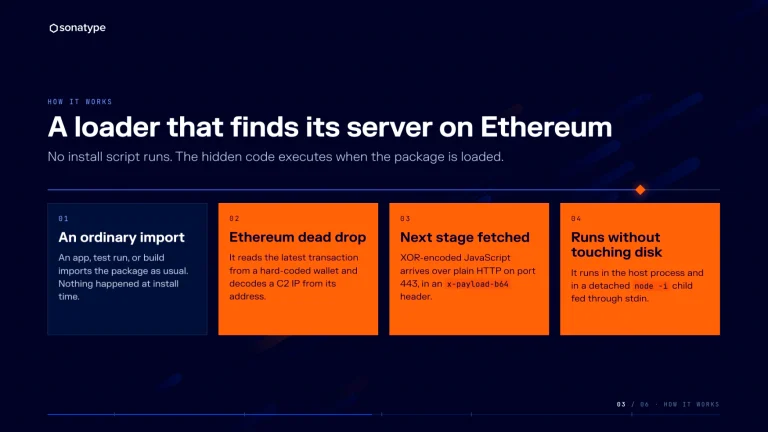
Sonatype uncovers the PolinRider loader in 12 releases across 10 hijacked packages. See how the npm PolinRider loader uses Ethereum to fetch malware.
Technical details and PoC exploit code for the critical Penpot file takeover flaw are now public. Upgrade to version 2.18.0 now.
Latest Technology News
The new Claude CarPlay update introduces hands-free voice interaction for drivers, split-screen multitasking, and multi-account switching.
Players rarely open a game service with a product in mind. They open it with a question:...
Forex markets move continuously as currencies respond to economic data, interest-rate expectations, geopolitical developments, and changing market...
Reddit is testing a Reddit mandatory login policy to thwart unauthorized AI scrapers and counteract declining organic search traffic.
Won a contract but missing proof? Fast Cyber Essentials and a fast pen test help suppliers satisfy procurement without losing momentum.
GitHub code activity reached historic highs in 2026, with over 7.3 billion monthly commits and 40% of pull requests drafted by AI coding agents.
The dramatic Stack Overflow question decline dropped monthly posts below 1,000 as developers embrace autonomous AI coding agents.
Learn how to identify automated visitors, set sensible access rules, and protect sensitive website actions without blocking useful automation.
Anthropic updated Claude Code permission modes with a toggle to suppress confirmation prompts for dangerous deletion commands during automated workflows.
Google is rolling out Google AI Mode ads across 13 international markets and launching multiturn ads in the US to offset rising AI compute costs.