Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
AI Drives 2026 Vulnerability Forecast to 66K CVEs, But Risk Stays Flat 2026 vulnerability forecast chart showing AI vulnerability discovery driving CVE growth
  • Vulnerability Report

AI Drives 2026 Vulnerability Forecast to 66K CVEs, But Risk Stays Flat

Do Son June 18, 2026 0

FIRST's 2026 vulnerability forecast warns AI vulnerability discovery could push CVEs to 66K, yet just 6.5% are truly actionable. Here's why.
China Influence Operations Target US AI Debate, OpenAI Warns China influence operations using banned ChatGPT accounts in OpenAI's June 2026 threat report targeting the US AI policy debate
  • Cybercriminals

China Influence Operations Target US AI Debate, OpenAI Warns

Do Son June 18, 2026 0

OpenAI's June 2026 threat report exposes China influence operations that used banned ChatGPT accounts to target US AI and tariff debates.

i18next Prototype Pollution Flaw (CVSS 9.1) Threatens 1M+ Weekly Downloads i18next prototype pollution flaw CVE-2026-48713 in i18next-fs-backend
  • Vulnerability Report

i18next Prototype Pollution Flaw (CVSS 9.1) Threatens 1M+ Weekly Downloads

Do Son June 18, 2026 0

CVE-2026-48713 exposes i18next prototype pollution in i18next-fs-backend, a CVSS 9.1 flaw threatening 1M+ weekly downloads. Update to 2.6.6 now.

Zyxel Patches Stack-Based Buffer Overflow in GS1900 Switches (CVE-2026-7273) Zyxel GS1900 vulnerability stack-based buffer overflow CVE-2026-7273 switch
  • Vulnerability Report

Zyxel Patches Stack-Based Buffer Overflow in GS1900 Switches (CVE-2026-7273)

Do Son June 18, 2026 0

Zyxel patched CVE-2026-7273, a stack-based buffer overflow in GS1900 switches. The Zyxel GS1900 vulnerability lets LAN attackers run OS commands.

Splunk AI Toolkit Vulnerabilities: Critical RCE & Data Risks Splunk AI Toolkit vulnerabilities including OS Command Injection CVE-2026-20266
  • Vulnerability Report

Splunk AI Toolkit Vulnerabilities: Critical RCE & Data Risks

Do Son June 17, 2026 0

New Splunk AI Toolkit vulnerabilities, including severe OS command injection (CVE-2026-20266), expose systems to attacks. Patch your instances immediately.
Active Gravity SMTP Vulnerability Exploited in the Wild Gravity SMTP Vulnerability CVE-2026-4020 exploit statistics
  • Vulnerability Report

Active Gravity SMTP Vulnerability Exploited in the Wild

Do Son June 17, 2026 0

Attackers are actively exploiting a critical Gravity SMTP vulnerability (CVE-2026-4020) causing sensitive information exposure. Update your plugin now.

Cisco ISE Vulnerabilities: Critical RCE and Info Disclosure Flaws Cisco ISE vulnerabilities diagram showing CVE-2026-20181 remote code execution and CVE-2026-20190 information disclosure.
  • Vulnerability Report

Cisco ISE Vulnerabilities: Critical RCE and Info Disclosure Flaws

Do Son June 17, 2026 0

Critical Cisco ISE vulnerabilities expose networks to Remote Code Execution (CVE-2026-20181) and data theft (CVE-2026-20190). Patch affected systems now.

Critical Apache Shiro LDAP Injection Flaw Uncovered Apache Shiro LDAP Injection showing the DefaultLdapRealm vulnerability flow and CVE-2026-49268 exploit path.
  • Vulnerability Report

Critical Apache Shiro LDAP Injection Flaw Uncovered

Do Son June 17, 2026 0

A critical Apache Shiro LDAP Injection vulnerability in DefaultLdapRealm, CVE-2026-49268, allows authentication bypass. Update your framework immediately.

SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies spycloud-phishing_report-flat_lay_1_1781535484R2j3cq4MNC
  • Press Release

SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies

cybernewswire June 17, 2026 0
Austin, TX, USA, 17th June 2026, CyberNewswire
Read More Read more about SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies
Heimdal Survey: Executives Four Times More Confident About AI Risk Than the Teams Managing It PR_Communicat_-_AI_Risk_Management_Report_1781617772Ho43XezgAG
  • Press Release

Heimdal Survey: Executives Four Times More Confident About AI Risk Than the Teams Managing It

cybernewswire June 17, 2026 0
London, United Kingdom, 17th June 2026, CyberNewswire
Read More Read more about Heimdal Survey: Executives Four Times More Confident About AI Risk Than the Teams Managing It
GoFlateLoader: The Bloated Golang Malware Smuggling Infostealers Past Scanners GoFlateLoader malware Golang loader, infostealer delivery, PE overlay evasion
  • Malware

GoFlateLoader: The Bloated Golang Malware Smuggling Infostealers Past Scanners

Do Son June 17, 2026 0

GoFlateLoader malware, a Golang loader, uses a giant PE overlay to evade scanners and deliver infostealers like Lumma, Vidar, and StealC.

Microsoft Copilot Cowork: Agentic AI System Launch Microsoft Copilot Cowork agentic AI system dashboard and features
  • Technology

Microsoft Copilot Cowork: Agentic AI System Launch

Do Son June 17, 2026 0

Microsoft officially launched Copilot Cowork, a revolutionary agentic AI system for enterprise tasks. Discover its features, pricing, and capabilities.
JDY Botnet Resurges: China-Nexus IoT Army Hunts New Vulnerabilities Within Hours JDY botnet Volt Typhoon, SOHO botnet, CVE-2026-35616
  • Malware

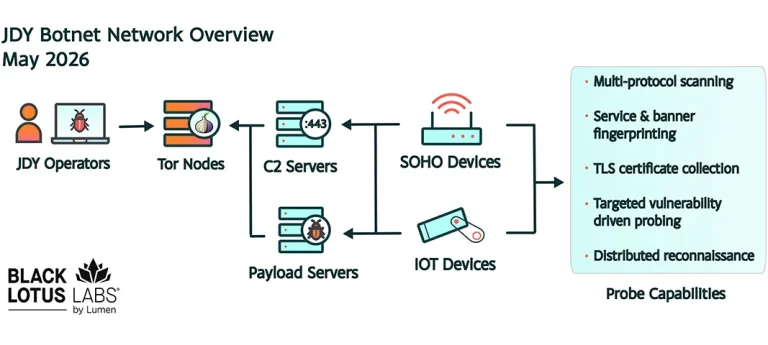
JDY Botnet Resurges: China-Nexus IoT Army Hunts New Vulnerabilities Within Hours

Do Son June 17, 2026 0

The JDY botnet, a China-nexus IoT network tied to Volt Typhoon, now spans 1,500+ devices and scans for new bugs like CVE-2026-35616 within hours.
Mastra Supply Chain Attack Compromises 140+ npm Packages Mastra supply chain attack delivering an npm infostealer through the typosquatted easy-day-js dependency during npm install
  • Malware

Mastra Supply Chain Attack Compromises 140+ npm Packages

Do Son June 17, 2026 0

A Mastra supply chain attack compromised 140+ npm packages, using the typosquatted easy-day-js dependency to drop a crypto-stealing infostealer.

AdGuard Email Tracking Protection: Stop Hidden Pixels AdGuard email tracking protection blocking hidden 1x1 pixel trackers
  • Technology

AdGuard Email Tracking Protection: Stop Hidden Pixels

Do Son June 17, 2026 0

Discover how the new AdGuard email tracking protection feature blocks hidden 1x1 pixels. Safeguard your inbox privacy and prevent covert surveillance today.

UK to Ban Social Media for Under-16s by Spring 2027 UK social media ban for under-16s with age verification requirements on Instagram TikTok and Snapchat
  • Technology

UK to Ban Social Media for Under-16s by Spring 2027

Do Son June 17, 2026 0

The UK will ban social media for under-16s by spring 2027, requiring age verification on platforms like Instagram, TikTok, and Snapchat.
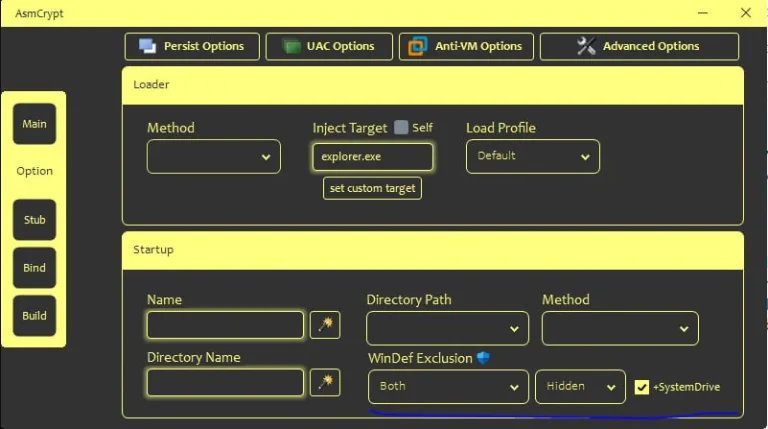
SilabRAT Malware: The $5,000-a-Month Crypto-Hunting RAT Hiding Behind HijackLoader SilabRAT malware SnappyClient, HijackLoader, Malware-as-a-Service
  • Malware

SilabRAT Malware: The $5,000-a-Month Crypto-Hunting RAT Hiding Behind HijackLoader

Do Son June 17, 2026 0

SilabRAT malware, aka SnappyClient, is a $5K/month MaaS RAT flagged as HijackLoader. It uses HVNC and cracks crypto wallets, per Group-IB.

WooCommerce Payment Skimmer Mimics Stripe to Steal Cards at Real Checkouts WooCommerce payment skimmer Magecart attack, card data theft, checkout backdoor
  • Cybercriminals

WooCommerce Payment Skimmer Mimics Stripe to Steal Cards at Real Checkouts

Do Son June 17, 2026 0

A WooCommerce payment skimmer mimics Stripe to steal card data during real checkouts. Inside this Magecart-style attack and how merchants can fight back.

Google Wear OS 7 Update: Gemini AI & Live Updates Google Wear OS 7 update featuring Live Updates and Gemini AI
  • Android

Google Wear OS 7 Update: Gemini AI & Live Updates

Do Son June 17, 2026 0

Discover the Google Wear OS 7 update. Explore new Live Updates, cross-device control, and Gemini AI integration for a smarter wearable experience.

ChatGPT Market Share Slips Below 50% As Rivals Grow ChatGPT market share graph showing competition from Gemini and Claude
  • Technology

ChatGPT Market Share Slips Below 50% As Rivals Grow

Do Son June 17, 2026 0

Discover why ChatGPT market share recently dropped below 50 percent. Explore how rival AI assistants like Gemini and Claude capture new active users.

Cloudflare DMARC Management Reaches General Availability Cloudflare DMARC Management dashboard for email authentication protocol
  • Technology

Cloudflare DMARC Management Reaches General Availability

Do Son June 17, 2026 0

Discover how Cloudflare DMARC Management enhances email security. Learn about the new general availability update, SPF auditing, and simplified remediation.

Google Unveils Android 17 and Innovative June Pixel Drop Google Android 17 features and June Pixel Drop multitasking bubbles
  • Android

Google Unveils Android 17 and Innovative June Pixel Drop

Do Son June 17, 2026 0

Discover how the new Android 17 operating system and June Pixel Drop redefine mobile productivity, privacy protection, and Gemini AI creativity.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-89292CVSS 9.2
    In Eclipse Mnestix Browser versions 1.6.0 up until but excluding 2.3.0 it was possible for an unauthenticated attacker...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121022CVSS 9.2
    Use of Default Password (CWE-1393) in the web client in AxxonSoft Axxon One before 3.0.0 on Windows and...
    📅 Updated: Nov 3, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 3, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Nov 3, 2026
  • CVE-2026-86473CVSS 9.1
    Apache Airflow: the Core API logout endpoint revokes only a session token presented as the _token cookie. When...
    📅 Updated: Nov 3, 2026
  • CVE-2026-42252CVSS 9.1
    Apache Airflow's official documentation at `core-concepts/dag-run.html` ("Passing Parameters when triggering Dags") showed a verbatim `BashOperator(bash_command="echo value: {{ dag_run.conf['conf1']...
    📅 Updated: Nov 3, 2026
  • CVE-2026-33264CVSS 9.8
    A bug in `BaseSerialization.deserialize()` allowed unrestricted `import_string()` of attacker-controlled class paths when the Scheduler / API Server loaded...
    📅 Updated: Nov 3, 2026
  • CVE-2025-57735CVSS 9.1
    When user logged out, the JWT token the user had authtenticated with was not invalidated, which could lead...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.