Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
IBM Patches Critical Authentication Bypass in Engineering Platform IBM Jazz Foundation vulnerability
  • Vulnerability Report

IBM Patches Critical Authentication Bypass in Engineering Platform

Do Son May 28, 2026 0

IBM patched a critical IBM Jazz Foundation vulnerability (CVE-2026-3660) with a 9.8 CVSS score. Learn how to secure your property files now.
Veeam Patches Critical Remote Code Execution and Privilege Escalation Flaws Veeam security vulnerabilities
  • Vulnerability Report

Veeam Patches Critical Remote Code Execution and Privilege Escalation Flaws

Do Son May 28, 2026 0

Learn about the new Veeam security vulnerabilities, including a critical 9.4 RCE flaw in Service Provider Console, and how to patch your systems.

The Sunset of OpenAI’s Promotional Quotas: A Shift in the ChatGPT Pro Pricing Matrix OpenAI subscription quota changes GPT-5.5 Agentic AI GPT-5.5 Instant release
  • Technology

The Sunset of OpenAI’s Promotional Quotas: A Shift in the ChatGPT Pro Pricing Matrix

Do Son May 28, 2026 0

OpenAI subscription quota changes take effect June 2026 as the double-allocation promo ends. Learn how your Codex limits and tier allocations will shift.
Critical Roundcube Webmail Security Updates Fix Severe Flaws Roundcube Webmail security updates Roundcube Webmail Security Roundcube 1.6.14 Update
  • Vulnerability Report

Critical Roundcube Webmail Security Updates Fix Severe Flaws

Do Son May 28, 2026 0

New Roundcube Webmail updates fix security flaws that could expose mailboxes. See which versions are affected and update your server now.

Popular npm Package shell-quote Patches Critical Command Injection Bug shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Popular npm Package shell-quote Patches Critical Command Injection Bug

Do Son May 28, 2026 0

CVE-2026-9277 (CVSS 9.2) lets attackers inject commands via the shell-quote npm package. Check your dependencies and upgrade now.
Host-Root Escape Vulnerability Uncovered in Kata Containers Kata Containers container escape
  • Vulnerability Report

Host-Root Escape Vulnerability Uncovered in Kata Containers

Do Son May 28, 2026 0

Explore the critical Kata Containers container escape vulnerability (CVE-2026-47243). Technical details and PoC exploit code are now fully public.
New Critical Flaw Discovered in Atril Document Viewer Atril single-click RCE
  • Vulnerability Report

New Critical Flaw Discovered in Atril Document Viewer

Do Son May 28, 2026 0

Learn about the critical Atril single-click RCE vulnerability (CVE-2026-46529). Public details and exploit code are now fully disclosed.

New Screening Serpens Cyberattacks Target Global Technology Professionals Screening Serpens cyberattacks
  • Cybercriminals

New Screening Serpens Cyberattacks Target Global Technology Professionals

Do Son May 27, 2026 0

Learn about the latest Screening Serpens cyberattacks exposed by Unit 42. Discover their new RAT variants and advanced defensive evasion tactics.

Link11 is fully committed to Europe and is opening a Customer Excellence Hub in Lisbon 03_Link11_Pressebox_G2_Portugal_ENG_1_1779867380zDaLoU1IH4
  • Press Release

Link11 is fully committed to Europe and is opening a Customer Excellence Hub in Lisbon

cybernewswire May 27, 2026 0
Frankfurt am Main, Germany, 27th May 2026, CyberNewswire
Read More Read more about Link11 is fully committed to Europe and is opening a Customer Excellence Hub in Lisbon
FBI Issues Alert on Kali365 Phishing Platform Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cybercriminals

FBI Issues Alert on Kali365 Phishing Platform

Do Son May 27, 2026 0

The FBI issued an alert on the new Kali365 phishing platform. Learn how this PhaaS kit steals Microsoft 365 tokens and bypasses MFA.

Linux Kernel Vulnerabilities Trigger Moxa Security Advisory Moxa Linux kernel vulnerabilities Moxa Vulnerability CVE-2024-12297 Moxa OpenSSH Vulnerability CVE-2023-38408 CVE-2023-5961 - CVE-2024-9138 and CVE-2024-9140
  • Vulnerability Report

Linux Kernel Vulnerabilities Trigger Moxa Security Advisory

Do Son May 27, 2026 0

Learn about the new Moxa Linux kernel vulnerabilities (CVE-2026-43284). Discover how to apply interim mitigations to prevent privilege escalation.
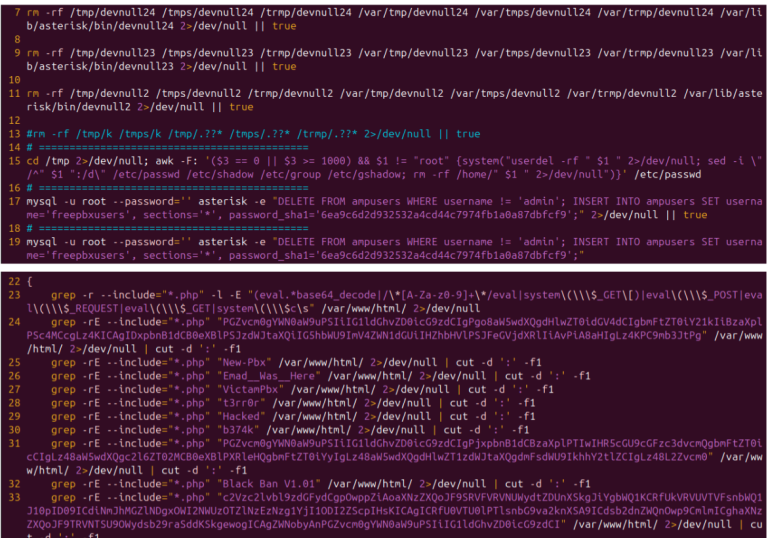
Massive FreePBX Exploitation Campaign Deploys JOMANGY Webshell FreePBX exploitation campaign
  • Cybercriminals
  • Vulnerability Report

Massive FreePBX Exploitation Campaign Deploys JOMANGY Webshell

Do Son May 27, 2026 0

Cyble researchers uncover a widespread FreePBX exploitation campaign by INJ3CTOR3 deploying the novel JOMANGY webshell for toll fraud.

NVIDIA Releases Critical Security Patches for AI Frameworks NVIDIA TensorRT-LLM vulnerabilities
  • Vulnerability Report

NVIDIA Releases Critical Security Patches for AI Frameworks

Do Son May 27, 2026 0

NVIDIA released updates fixing severe NVIDIA TensorRT-LLM vulnerabilities and Isaac Launchable flaws. Patch your active systems today.
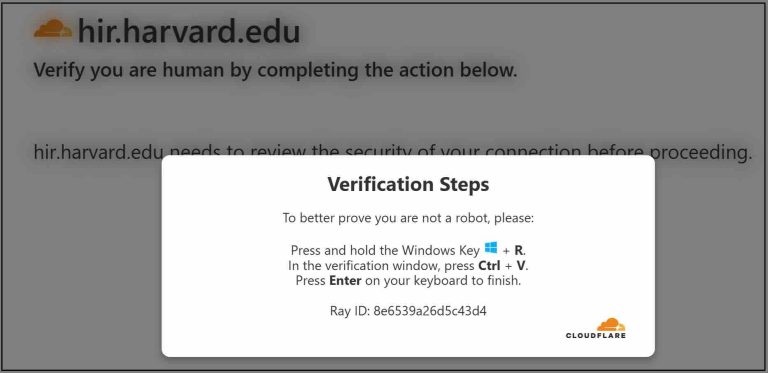
Global Ghost CMS Poisoning Campaign Exploits Enterprise Blogs Ghost CMS poisoning campaign
  • Malware
  • Vulnerability Report

Global Ghost CMS Poisoning Campaign Exploits Enterprise Blogs

Do Son May 27, 2026 0

XLab uncovers a massive Ghost CMS poisoning campaign utilizing CVE-2026-26980 to launch FakeCaptcha attacks. Learn how to secure your site.

Global Malicious AI Installer Campaign Targets Developer Workstations Layoff Phishing Scam Remcos RAT Malware Aruba Phishing, Phishing-as-a-Service PyPI, phishing CVE-2024-25608 PyPI Phishing, Credential Theft
  • Cybercriminals

Global Malicious AI Installer Campaign Targets Developer Workstations

Do Son May 27, 2026 0

EclecticIQ warns of a malicious AI installer campaign using SEO poisoning to deliver fileless infostealers to developer environments.

The Institutional Metamorphosis of Google: Sustaining Digital Hegemony in the Shadow of the Singularity Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

The Institutional Metamorphosis of Google: Sustaining Digital Hegemony in the Shadow of the Singularity

Do Son May 27, 2026 0

Google CEO Sundar Pichai reveals how Gemini-powered Agentic AI search will shift the web from traditional link clicks to autonomous background task execution.

The Attrition of Computational Allocation: Systemic Volatility and Quota Depreciation Within the Google Gemini Interface Gemini resource quotas error
  • Technology

The Attrition of Computational Allocation: Systemic Volatility and Quota Depreciation Within the Google Gemini Interface

Do Son May 27, 2026 0

A major Gemini resource quotas error is rapidly draining developers' weekly usage limits in minutes. Learn about the token tracking bug and Google's resets.
Critical Defect Exposed: Flaw In Apache Fory Bypasses Deserialization Protections Apache Fory vulnerability Apache Fory vulnerability patch PyFory deserialization policy bypass
  • Vulnerability Report

Critical Defect Exposed: Flaw In Apache Fory Bypasses Deserialization Protections

Do Son May 27, 2026 0

Discover how CVE-2026-48207, a critical PyFory deserialization policy bypass flaw, lets attackers execute remote code, and learn how to patch it now.

Overhaul Your Site Defense: Concrete CMS Security Fixes Arrive in Version 9.5.1 Concrete CMS security fixes
  • Vulnerability Report

Overhaul Your Site Defense: Concrete CMS Security Fixes Arrive in Version 9.5.1

Do Son May 27, 2026 0

Concrete CMS dropped critical Concrete CMS security fixes in version 9.5.1 to eliminate remote code execution vulnerabilities. Update now.

Unauthenticated Execution Threatens Kubernetes Clusters critical Fission router vulnerability
  • Vulnerability Report

Unauthenticated Execution Threatens Kubernetes Clusters

Do Son May 27, 2026 0

A critical Fission router vulnerability (CVE-2026-46614) allows unauthenticated function invocation in Kubernetes. Learn how to patch it now.

GitHub Patches Critical Flaws in Enterprise Server Update CVE-2024-4985 GitHub Enterprise Server vulnerabilities
  • Vulnerability Report

GitHub Patches Critical Flaws in Enterprise Server Update

Do Son May 27, 2026 0

GitHub patches critical GitHub Enterprise Server vulnerabilities (CVE-2026-9312). Learn about key rotation and critical SSRF fixes.
Dual Sandbox Bypasses Threaten PHP Applications critical Twig RCE flaws
  • Vulnerability Report

Dual Sandbox Bypasses Threaten PHP Applications

Do Son May 27, 2026 0

Twig project maintainers patched critical Twig RCE flaws allowing arbitrary code execution via sandbox bypasses. Update to 3.26.0.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121229CVSS 9.6
    Memory corruption in ANGLE in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121156CVSS 9.6
    Buffer overflow in Dawn in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.