Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
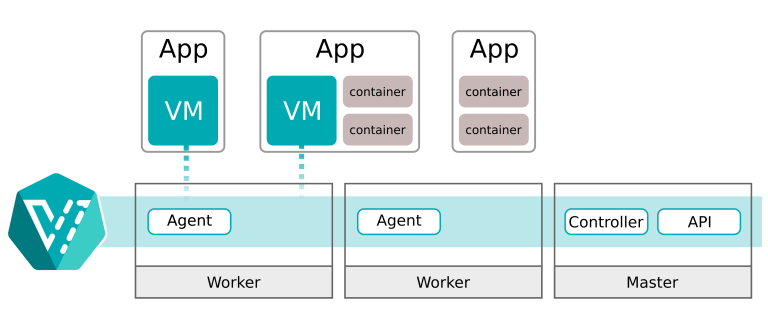
KubeVirt Privilege Escalation Flaw Exposes Kubernetes Clusters to Takeover KubeVirt privilege escalation flaw cluster takeover risk
  • Vulnerability Report

KubeVirt Privilege Escalation Flaw Exposes Kubernetes Clusters to Takeover

Do Son May 29, 2026 0

Discover how the critical KubeVirt privilege escalation flaw (CVE-2026-7374) allows container runtime hijacking and creates a cluster takeover risk.
The Algorithmic Backlash: DuckDuckGo Capitalizes on Google’s AI Overreach DuckDuckGo No-AI search surge
  • Technology

The Algorithmic Backlash: DuckDuckGo Capitalizes on Google’s AI Overreach

Do Son May 29, 2026 0

Frustrated by Google’s un-toggleable AI changes? A massive DuckDuckGo No-AI search surge proves iOS users are ditching AI Overviews for classic web results.

Samba Fixes Multiple Flaws with Maximum 10.0 CVSS Scores critical Samba vulnerabilities remote code execution flaws CVE-2023-34966
  • Vulnerability Report

Samba Fixes Multiple Flaws with Maximum 10.0 CVSS Scores

Do Son May 29, 2026 0

The Samba Team dropped fixes for critical Samba vulnerabilities. Read about the remote code execution flaws carrying perfect 10.0 CVSS scores.

New Jenkins Security Advisory Highlights Severe Plugin Flaws Jenkins RCE vulnerabilities Jenkins plugin security flaws CVE-2024-47855
  • Vulnerability Report

New Jenkins Security Advisory Highlights Severe Plugin Flaws

Do Son May 29, 2026 0

Discover the latest Jenkins plugin security flaws. Learn how unvalidated LDAP referrals and arbitrary file reads impact your controller servers.
Google Releases Massive Desktop Patch to Fix Critical Imperfections Google Chrome security update critical security fixes
  • Vulnerability Report

Google Releases Massive Desktop Patch to Fix Critical Imperfections

Do Son May 29, 2026 0

Install the new Google Chrome security update today. This release delivers 151 critical security fixes to patch severe memory bugs.

New GitLab Security Updates Fix Critical Flaws in Duo AI GitLab security updates Duo AI flaw fixed GitLab Runner Hijack, DoS Fix GitLab GraphQL Flaws, CVE-2025-11340 CVE-2024-9693 GitLab vulnerability, XSS
  • Vulnerability Report

New GitLab Security Updates Fix Critical Flaws in Duo AI

Do Son May 29, 2026 0

The latest GitLab security updates address high-severity bugs. Download the patch to ensure the Duo AI flaw fixed protects your DevSecOps pipeline.

Critical Patches Fix Synology Chat Server Vulnerabilities Synology Chat Server vulnerabilities Synology security update Synology DSM Update NAS Security Vulnerability Synology VPN Update SSL VPN Vulnerability Synology Telnet Flaw DSM Security Update Synology DSM Telnet vulnerability BeeStation Zero-Day, Pwn2Own RCE CVE-2024-11131 & CVE-2024-10442 CVE-2025-2848 Synology, NAS
  • Vulnerability Report

Critical Patches Fix Synology Chat Server Vulnerabilities

Do Son May 29, 2026 0

Synology released updates fixing critical Synology Chat Server vulnerabilities. Learn how to update your DSM package to prevent file leaks.
Critical WP Maps Pro Vulnerability Actively Exploited in the Wild WP Maps Pro vulnerability exploited in the wild
  • Vulnerability Report

Critical WP Maps Pro Vulnerability Actively Exploited in the Wild

Do Son May 28, 2026 0

The critical WP Maps Pro vulnerability is actively exploited in the wild. Learn how this flaw allows full site takeover and how to patch it now.
The CISO Whisperer’s Watch List For The Gartner Security & Risk Management Summit 2026 WhatsApp_Image_2026-05-28_at_71147_PM_1779984814qKf6qWW5A8
  • Press Release

The CISO Whisperer’s Watch List For The Gartner Security & Risk Management Summit 2026

cybernewswire May 28, 2026 0
New York, USA, 28th May 2026, CyberNewswire
Read More Read more about The CISO Whisperer’s Watch List For The Gartner Security & Risk Management Summit 2026
The Encryption Migration Business Case: When Regulated Institutions Should Modernize Secure Communications AISelect_20260527_134045_Docs
  • Technique

The Encryption Migration Business Case: When Regulated Institutions Should Modernize Secure Communications

Do Son May 28, 2026 0
Enterprise security teams do not usually replace email encryption because something dramatic happens overnight. They replace it...
Read More Read more about The Encryption Migration Business Case: When Regulated Institutions Should Modernize Secure Communications
Critical Defect Discovered in Langflow AI Architecture IBM WebSphere execution flaws WebSphere security bulletin patches request smuggling patch WebSphere remote code execution Langflow OSS vulnerability remote code execution patch
  • Vulnerability Report

Critical Defect Discovered in Langflow AI Architecture

Do Son May 28, 2026 0

A critical Langflow OSS vulnerability (CVE-2026-7524) allows remote code execution. Apply the remote code execution patch to secure your system.

Critical Privilege Escalation Flaw Fixed in OpenVPN Connect for macOS OpenVPN Connect macOS vulnerability macOS privilege escalation fix OVPNX - OpenVPN Zero-Day
  • Vulnerability Report

Critical Privilege Escalation Flaw Fixed in OpenVPN Connect for macOS

Do Son May 28, 2026 0

Learn about the critical OpenVPN Connect macOS vulnerability (CVE-2026-9560) that allows local privilege escalation, and how to patch it now.
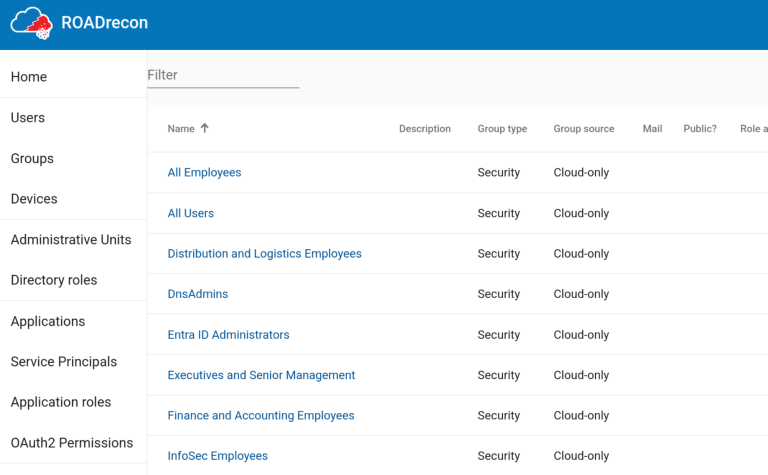
State-Sponsored Actors Operationalize ROADtools Framework in Cloud Campaigns ROADtools cloud attack toolkit
  • Cybercriminals

State-Sponsored Actors Operationalize ROADtools Framework in Cloud Campaigns

Do Son May 28, 2026 0

Discover how nation-state hackers leverage the ROADtools cloud attack toolkit to compromise Entra ID environments and bypass MFA controls.
North Korea-Aligned Void Dokkaebi Evolves with Binary Obfuscation Void Dokkaebi Cython malware
  • Malware

North Korea-Aligned Void Dokkaebi Evolves with Binary Obfuscation

Do Son May 28, 2026 0

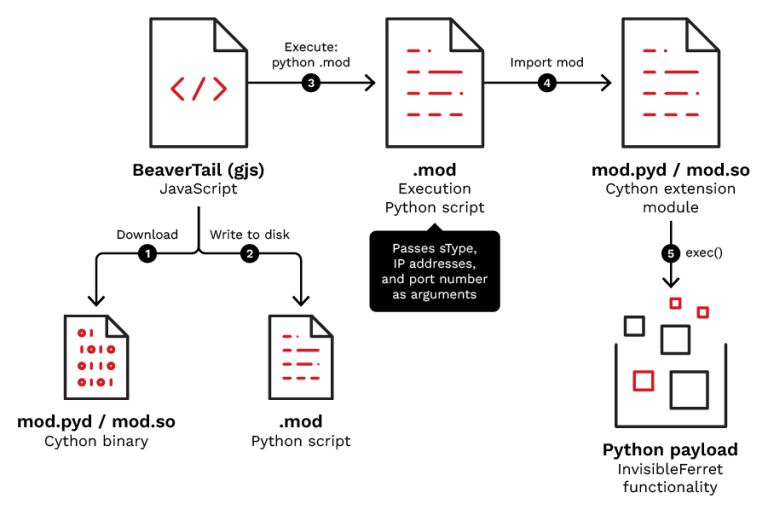
TrendAI Research exposes the new Void Dokkaebi Cython malware campaign. Learn how InvisibleFerret uses binary compilation to evade security teams.

CIFSwitch Local Root Exploit: Public Details and PoC Disclosed CIFSwitch local root exploit cifs-utils privilege escalation Linux Kernel Root Exploit CVE-2025-39946 PoC CVE-2023-2598 PoC Ubuntu LPE Vulnerability CVE-2026-3888
  • Linux
  • Vulnerability Report

CIFSwitch Local Root Exploit: Public Details and PoC Disclosed

Do Son May 28, 2026 0

Security researcher Asim Manizada has released public details and a PoC for the CIFSwitch local root exploit impacting many Linux systems.
New Showboat Linux Malware Targets Global Telecommunications Showboat Linux malware
  • Malware

New Showboat Linux Malware Targets Global Telecommunications

Do Son May 28, 2026 0

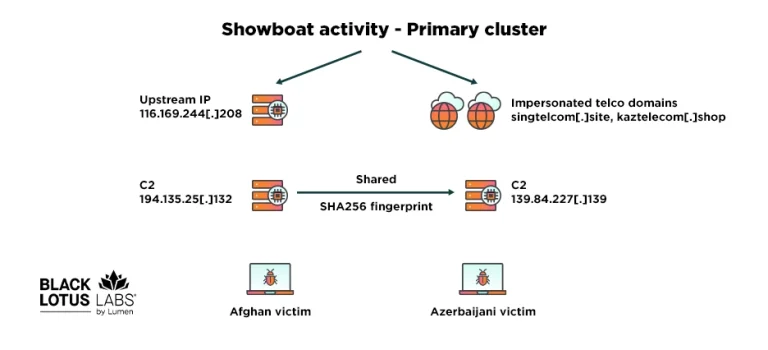
Discover the new Showboat Linux malware framework uncovered by Black Lotus Labs. Learn how PRC threat actors target telecommunications networks.
New CypherLoc Scareware Kit Implements Sophisticated Browser Locks CypherLoc scareware kit
  • Cybercriminals

New CypherLoc Scareware Kit Implements Sophisticated Browser Locks

Do Son May 28, 2026 0

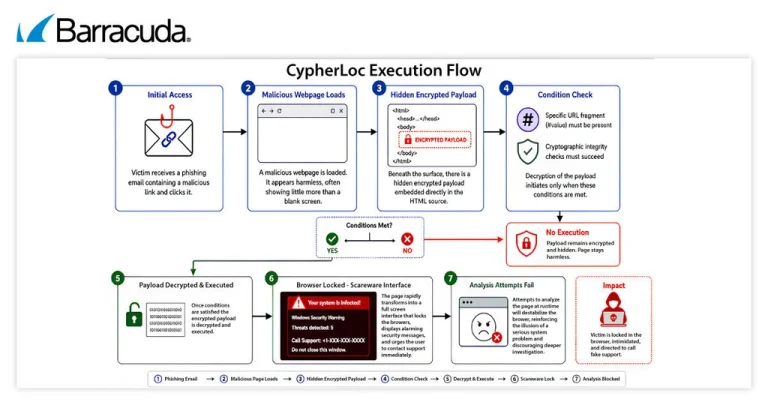
Barracuda Research warns of the CypherLoc scareware kit. Learn how this browser-locking threat uses psychological manipulation to scam users.
Emerging Deprecation Protocols Within the Codex Model Ecosystem OpenAI legacy model deprecation OpenAI Codex mobile integration
  • Technology

Emerging Deprecation Protocols Within the Codex Model Ecosystem

Do Son May 28, 2026 0

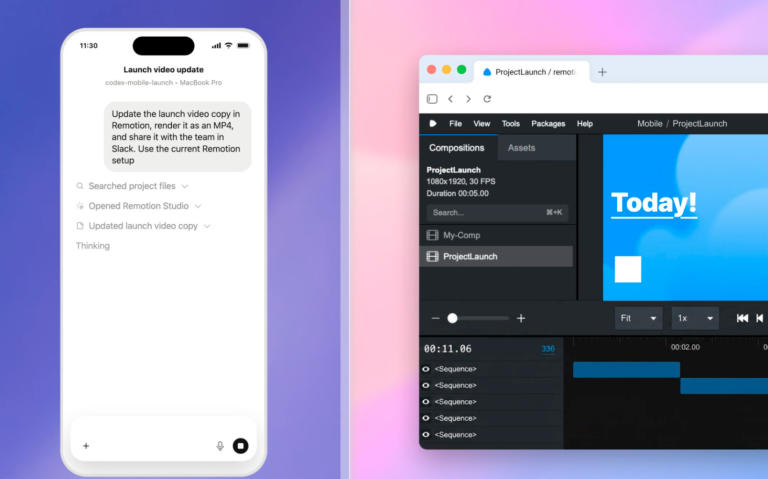
OpenAI confirms an upcoming legacy model deprecation on June 2, retiring GPT-5.2 and GPT-5.3-Codex from ChatGPT while forcing a shift to GPT-5.5.

Critical FortiClient EMS Exploitation Campaign Spreads New EKZ Infostealer Payload FortiClient EMS exploitation Cisco FIRESTARTER Backdoor Arcane Door Campaign Dell RecoverPoint Zero-Day UNC6201 Espionage Notepad++ Compromise Supply Chain Attack Magento SessionReaper CVE-2025-54236 ShadowRay 2.0, AI-Generated Malware WordPress Auth Bypass, CVE-2025-5947 Exploited EcoStruxure Vulnerabilities, Industrial Control System UNC5820 - CVE-2014-2120 - CVE-2021-44207
  • Vulnerability Report

Critical FortiClient EMS Exploitation Campaign Spreads New EKZ Infostealer Payload

Do Son May 28, 2026 0

Arctic Wolf warns of a new FortiClient EMS exploitation campaign using CVE-2026-35616 to deploy the stealthy EKZ Infostealer malware.

Telemetry Interception: The Unauthorized Routing of Motorola’s Amazon Gateway Motorola Smart Feed redirect Anthropic Amazon 5GW partnership Amazon Perplexity lawsuit AWS-LC Vulnerabilities Cryptographic Bypass AWS Middle East drone strikes Amazon layoffs 2026, Amazon AI restructuring Amazon Kindle DRM Policy, Publisher Control EPUB AWS Nova Forge AI Model Customization AWS Trainium3 EC2 Trn3 UltraServer Route 53 Accelerated Recovery AWS DNS Resilience AI Browser War, Amazon Comet Amazon layoffs, cost reduction AWS outage, DynamoDB DNS AWS outage, cloud dependency AWS VPN Client, Root Privilege Escalation WSA shutdown, Amazon Appstore Amazon Wondery, Podcast Restructuring Amazon Q2 2025 Generative AI AWS Client VPN, Privilege Escalation Amazon AI, Wearable AI
  • Technology

Telemetry Interception: The Unauthorized Routing of Motorola’s Amazon Gateway

Do Son May 28, 2026 0

Users uncover a weird Motorola Smart Feed redirect that forces the Amazon app through third-party tracking links. Motorola claims it was a glitch and fixed it.
Windows DNS Client RCE: 9.8 CVSS & Public PoC Disclosed Windows DNS Client RCE .NET 10 Auth Bypass CVE-2026-40372
  • Vulnerability

Windows DNS Client RCE: 9.8 CVSS & Public PoC Disclosed

Do Son May 28, 2026 0

A critical Windows DNS Client RCE vulnerability (CVE-2026-41096) with a 9.8 CVSS has public PoC exploit code. Learn how to detect and patch it.
IBM Patches Critical Authentication Bypass in Engineering Platform IBM Jazz Foundation vulnerability
  • Vulnerability Report

IBM Patches Critical Authentication Bypass in Engineering Platform

Do Son May 28, 2026 0

IBM patched a critical IBM Jazz Foundation vulnerability (CVE-2026-3660) with a 9.8 CVSS score. Learn how to secure your property files now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-121802CVSS 9.1
    @better-auth/expo before 1.7.16 allows certain account-takeover outcomes (e.g., unauthenticated changes of any account's email address), because it signs...
    📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-118762CVSS 9.3
    Monkeytype is a minimalistic and customizable typing test. Prior to 26.43.0, the .github/workflows/fix-formatting.yml workflow runs on pull_request_target with...
    📅 Updated: Nov 4, 2026
  • CVE-2025-49602CVSS 9.8
    An issue was discovered in Keyfactor EJBCA 9. When an administrator is removed from its administrator role while...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121615CVSS 10.0
    A vulnerability was determined in Linksys E5600 1.1.0.26. Affected is an unknown function of the file /cgi-bin/mesh_login.cgi of...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121609CVSS 10.0
    A vulnerability was identified in Qihoo 360 Whole Home Router M5 4.0.17.1566. This issue affects the function Home...
    📅 Updated: Nov 4, 2026
  • CVE-2026-51912CVSS 9.8
    OpenBMB XAgent v1.0.0 contains directory traversal vulnerability in main-upload_file-the-preserved-live-upload-file-witness-directly-reaches (ToolServer/ToolServerNode/main.py:46).
    📅 Updated: Nov 4, 2026
  • CVE-2026-107056CVSS 9.1
    Insecure permissions in the io.file.importer.ImportActivity component of OpenTracks versionCode 6751 allows unauthorized attackers to inject crafted tracking data...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.