Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Security Alert: ISC Releases Patches for Critical BIND 9 Flaws critical BIND 9 flaws Kea DHCP Vulnerability CVE-2026-3608 CVE-2022-1183 CVE-2025-40779 Kea DHCP, vulnerability
  • Vulnerability Report

Security Alert: ISC Releases Patches for Critical BIND 9 Flaws

Do Son May 26, 2026 0

Internet Systems Consortium released patches fixing six critical BIND 9 flaws that cause memory exhaustion and unexpected daemon crashes.

Android Carrier Billing Fraud Campaign Exposed by zLabs Android carrier billing fraud
  • Cybercriminals

Android Carrier Billing Fraud Campaign Exposed by zLabs

Do Son May 26, 2026 0

A sophisticated Android carrier billing fraud campaign hit users worldwide. Learn how fake apps trigger premium SMS abuse and how to stay safe.

New Tampered Chef Malware Campaigns Discovered in Productivity Software Tampered Chef malware
  • Malware

New Tampered Chef Malware Campaigns Discovered in Productivity Software

Do Son May 26, 2026 0

Researchers uncover the Tampered Chef malware cluster disguised as PDF editors and tools. Learn how these stealthy threats bypass corporate defenses.
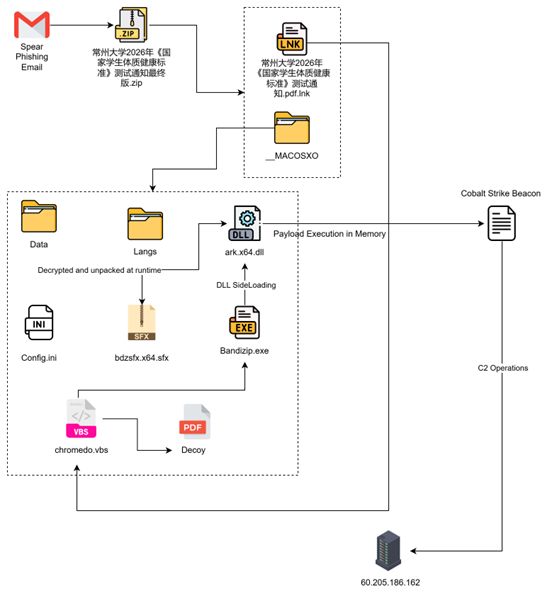
New Operation Dragon Whistle Phishing Campaign Targets Universities Operation Dragon Whistle phishing
  • Cybercriminals

New Operation Dragon Whistle Phishing Campaign Targets Universities

Do Son May 26, 2026 0

Discover how the Operation Dragon Whistle phishing campaign leverages student fitness lures to deploy stealthy memory-only malware.

Critical Dell Container Storage Modules Vulnerability Exposes Infrastructure Dell Container Storage Modules vulnerability
  • Vulnerability

Critical Dell Container Storage Modules Vulnerability Exposes Infrastructure

Do Son May 26, 2026 0

Fix the critical Dell Container Storage Modules vulnerability (CVE-2026-40710). Learn how hardcoded credentials expose systems and update now.

Apache CXF Framework Patches Three Severe Security Flaws Apache CXF vulnerabilities, JNDI injection flaws, CVE-2026-50634, CVE-2026-50633, CVE-2026-50628 Apache CXF vulnerabilities
  • Vulnerability Report

Apache CXF Framework Patches Three Severe Security Flaws

Do Son May 26, 2026 0

Discover the latest critical Apache CXF vulnerabilities, including RCE and XXE flaws, and learn how to secure your open source services framework.

Critical Memcached SASL Vulnerability Fixed in Version 1.6.42 Memcached SASL vulnerability
  • Vulnerability Report

Critical Memcached SASL Vulnerability Fixed in Version 1.6.42

Do Son May 26, 2026 0

Learn about the critical Memcached SASL vulnerability flaws fixed in version 1.6.42. Discover how timing side channels impacted authentication.
Important Security Flaw Patched in Apache ECharts Library Apache ECharts XSS vulnerability
  • Vulnerability Report

Important Security Flaw Patched in Apache ECharts Library

Do Son May 26, 2026 0

Learn about the Apache ECharts XSS vulnerability (CVE-2026-45249) in the Lines series tooltip rendering logic and find out how to secure your code.

New 7-Zip Heap Buffer Overflow Disclosed with Public PoC 7-Zip heap buffer overflow CVE-2025-0411 7-Zip path traversal
  • Vulnerability Report

New 7-Zip Heap Buffer Overflow Disclosed with Public PoC

Do Son May 26, 2026 0

CVE-2026-48095 (CVSS 8.8) is a heap buffer overflow in 7-Zip that a crafted archive can trigger. Update to the patched version now.

The Zero-Day Dispatch: Weekly Threat Intelligence Briefing (May 18 – May 24, 2026) Weekly Threat Intelligence
  • Weekly Recap

The Zero-Day Dispatch: Weekly Threat Intelligence Briefing (May 18 – May 24, 2026)

Do Son May 25, 2026 0

Read our weekly threat intelligence briefing. Discover active exploits, critical CVEs, and the latest CISA KEV additions for May 18–24, 2026.

New Knowledge Deliver RCE Vulnerability Exploited in the Wild Knowledge Deliver RCE vulnerability FortiClient EMS Vulnerability CVE-2026-35616 Cisco SD-WAN Vulnerability CVE-2026-20122 PCPcat, Next.js RCE Salesloft breach, Salesforce CRM WIREFIRE web shell
  • Vulnerability Report

New Knowledge Deliver RCE Vulnerability Exploited in the Wild

Do Son May 25, 2026 0

Learn how Mandiant uncovered the critical Knowledge Deliver RCE vulnerability (CVE-2026-5426) and how to protect your systems today.

Poisoned Code: Stealthy Malicious Go Module Backdoor Discovered in Long-Running Typosquat malicious Go module backdoor
  • Malware

Poisoned Code: Stealthy Malicious Go Module Backdoor Discovered in Long-Running Typosquat

Do Son May 25, 2026 0

Security researchers have exposed a malicious Go module backdoor hidden inside the shopsprint/decimal package that executes code using stealthy DNS TXT records.

Disrupted: How the “Trapdoor” Ad Fraud Ring Weaponized 455 Android Apps for 659 Million Daily Fake Bids Trapdoor Ad Fraud Pipeline HUMAN Satori Malware Disruption
  • Cybercriminals

Disrupted: How the “Trapdoor” Ad Fraud Ring Weaponized 455 Android Apps for 659 Million Daily Fake Bids

Do Son May 25, 2026 0

HUMAN's Satori team disrupted Trapdoor, an Android ad fraud ring using 455 apps and hidden WebViews to fake 659 million daily ad bids.
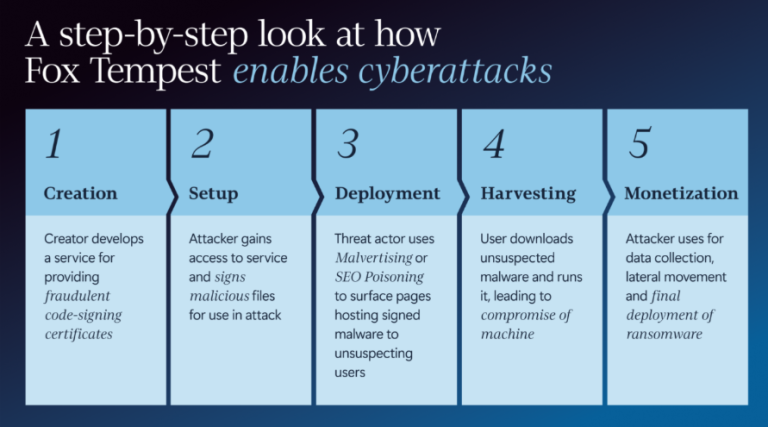
Microsoft Dismantles “Fox Tempest” Code-Signing Network Fueling Global Ransomware Fox Tempest Takedown Malware Signing as a Service
  • Cybercriminals

Microsoft Dismantles “Fox Tempest” Code-Signing Network Fueling Global Ransomware

Do Son May 25, 2026 0

Microsoft's DCU and Resecurity have disrupted Fox Tempest, a major MSaaS ring that forged code-signing certificates for ransomware delivery.

In-Memory Financial Theft: Inside Banana RAT’s Operator-Driven Attacks on Brazilian Banks Banana RAT Banking Trojan SHADOW-WATER-063 MaaS
  • Malware

In-Memory Financial Theft: Inside Banana RAT’s Operator-Driven Attacks on Brazilian Banks

Do Son May 25, 2026 0

TrendAI exposes Banana RAT, a fileless banking trojan by SHADOW-WATER-063 that uses in-memory execution and fake UI overlays to hijack Pix-QR transfers.

NLnet Labs Issues Urgent Security Release for Unbound Resolver Unbound DNSSEC validation vulnerability
  • Vulnerability Report

NLnet Labs Issues Urgent Security Release for Unbound Resolver

Do Son May 25, 2026 0

NLnet Labs patches a critical Unbound DNSSEC validation vulnerability allowing unauthenticated remote code execution. Update to 1.25.1.

Critical Unauthenticated RCE Flaw Threatens Kopia Backup Servers Kopia SSH ProxyCommand injection
  • Vulnerability Report

Critical Unauthenticated RCE Flaw Threatens Kopia Backup Servers

Do Son May 25, 2026 0

A critical unauthenticated RCE flaw (CVE-2026-45695) impacts Kopia backup servers. Learn how the Kopia SSH ProxyCommand injection exploit operates and how to patch it.

Critical TYPO3 Extension Exploit: Content Element Selector Flaw (CVE-2026-46725) Triggers Unauthenticated RCE TYPO3 Extension Vulnerability CVE-2026-46725 RCE
  • Vulnerability Report

Critical TYPO3 Extension Exploit: Content Element Selector Flaw (CVE-2026-46725) Triggers Unauthenticated RCE

Do Son May 25, 2026 0

Urgent: TYPO3 patches a critical 9.2 CVSS flaw (CVE-2026-46725) in Content Element Selector plugin. Unauthenticated attackers can achieve full server RCE.

Over-the-Air Root Risk: Seven Critical FreeBSD Security Advisories Fix Wi-Fi RCE and Kernel Flaws FreeBSD Wi-Fi RCE Vulnerability CVE-2026-45255 Patch FreeBSD dhclient Root Exploit CVE-2026-42511 FreeBSD Vulnerability - CVE-2024-7589 FreeBSD Jail Escape CVE-2025-15576
  • Vulnerability Report

Over-the-Air Root Risk: Seven Critical FreeBSD Security Advisories Fix Wi-Fi RCE and Kernel Flaws

Do Son May 25, 2026 0

The FreeBSD Project fixes seven vulnerabilities, including a zero-interaction Wi-Fi shell expansion RCE (CVE-2026-45255) and severe kernel leaks.

NGINX Fixes Critical Poolslip Flaw Allowing Remote Code Execution NGINX heap buffer overflow vulnerability NGINX Vulnerability Buffer Overflow CVE-2024-24989, CVE-2024-24990 NGINX ACME
  • Vulnerability Report

NGINX Fixes Critical Poolslip Flaw Allowing Remote Code Execution

Do Son May 25, 2026 0

An NGINX heap buffer overflow vulnerability known as poolslip allows remote code execution. Learn how to secure your network servers now.
Best AI Code Security Solutions: Top 10 Options in 2026 Salesforce vulnerability CVE-2025-9844 Salt Typhoon cyberattack
  • Technique

Best AI Code Security Solutions: Top 10 Options in 2026

Do Son May 24, 2026 0
Code security is becoming one of the most difficult operational problems in modern software development, not because...
Read More Read more about Best AI Code Security Solutions: Top 10 Options in 2026
ConnectWise Patches Severe Code Execution Flaw in Automate ConnectWise Automate vulnerability
  • Vulnerability Report

ConnectWise Patches Severe Code Execution Flaw in Automate

Do Son May 24, 2026 0

ConnectWise released a fix for a ConnectWise Automate vulnerability (CVE-2026-9089). Learn about the code download flaw and how to patch it now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-112346CVSS 9.3
    OpenHands Software Agent SDK before 1.52.0 contains an unauthenticated remote code execution vulnerability where the DockerWorkspace and Apptainer...
    📅 Updated: Nov 8, 2026
  • CVE-2026-10042CVSS 9.2
    manga-image-translator contains a remote code execution vulnerability in the shared API server mode due to unsafe deserialization of...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71325CVSS 9.3
    picklescan before 0.0.27 contains a parsing logic error in the _list_globals function when handling STACK_GLOBAL opcodes, failing to...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71323CVSS 9.3
    picklescan before 0.0.33 fails to block the ctypes module, allowing attackers to achieve remote code execution by invoking...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71320CVSS 9.3
    picklescan before 0.0.33 contains an incomplete deny-list that fails to block pydoc.locate and operator.methodcaller functions, allowing attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71321CVSS 9.3
    picklescan before 0.0.33 contains an arbitrary file writing vulnerability that allows attackers to bypass the dangerous blocklist by...
    📅 Updated: Nov 8, 2026
  • CVE-2024-58351CVSS 9.3
    Flowise before 2.1.4 allows configuration to be injected into the Chainflow during execution via the overrideConfig option, supported...
    📅 Updated: Nov 8, 2026
  • CVE-2020-37282CVSS 9.3
    office-converter through 1.0.2 contains an OS command injection vulnerability that allows attackers to execute commands by supplying a...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.