Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
ConnectWise Patches Severe Code Execution Flaw in Automate ConnectWise Automate vulnerability
  • Vulnerability Report

ConnectWise Patches Severe Code Execution Flaw in Automate

Do Son May 24, 2026 0

ConnectWise released a fix for a ConnectWise Automate vulnerability (CVE-2026-9089). Learn about the code download flaw and how to patch it now.

Cloud Under Siege: Persistent P2Pinfect Botnet Activity Discovered in Kubernetes Environments P2Pinfect botnet activity
  • Malware

Cloud Under Siege: Persistent P2Pinfect Botnet Activity Discovered in Kubernetes Environments

Do Son May 24, 2026 0

A recent report shows persistent P2Pinfect botnet activity inside Google Kubernetes Engine via exposed Redis instances. Learn how to secure your network.

SSRF Risk in Server-Side Rendering: Patch Your Angular Applications Angular hostname hijacking vulnerability Angular SSRF Origin Hijacking Angular XSS Vulnerability CVE-2026-32635 Angular i18n XSS CVE-2026-27970 Angular SSR SSRF CVE-2026-27739 Angular Vulnerability CVE-2026-22610 CVE-2025-59052 Angular security Angular XSS Bypass, SVG Injection
  • Vulnerability Report

SSRF Risk in Server-Side Rendering: Patch Your Angular Applications

Do Son May 24, 2026 0

A critical Angular hostname hijacking vulnerability allows SSRF attacks. Discover the impact on platform-server and how to patch your apps.
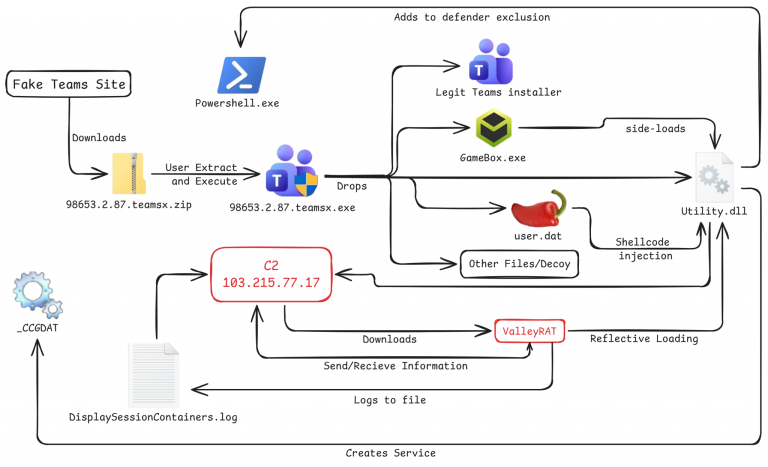
Legitimate Software Abused: Stealthy ValleyRAT Malware Campaign Targets Enterprise Users ValleyRAT malware campaign
  • Malware

Legitimate Software Abused: Stealthy ValleyRAT Malware Campaign Targets Enterprise Users

Do Son May 24, 2026 0

A sophisticated ValleyRAT malware campaign uses fake Microsoft Teams installers and DLL sideloading to evade Windows Defender detection.

Operation Saffron: Authorities Smash ‘First VPN’ Cybercrime Network First VPN service takedown
  • Cybercriminals

Operation Saffron: Authorities Smash ‘First VPN’ Cybercrime Network

Do Son May 24, 2026 0

Europol completely dismantles 'First VPN,' seizing 33 servers and uncovering an underground database used by thousands of global ransomware operators.

The 10,000-Bug AI: How Anthropic’s Secret “Mythos” Model is Rewriting Cyber-Resilience Anthropic Project Glasswing cybersecurity
  • Technology

The 10,000-Bug AI: How Anthropic’s Secret “Mythos” Model is Rewriting Cyber-Resilience

Do Son May 24, 2026 0

Anthropic’s secret "Mythos" model found 10,000+ bugs in one month for partners like Cloudflare and Mozilla. Discover why this tech remains top-secret.

Malicious JS Lifecycle Hooks Found Hiding Inside PHP Composer Packages PHP Supply Chain Attack Socket Composer Malicious Postinstall
  • Malware

Malicious JS Lifecycle Hooks Found Hiding Inside PHP Composer Packages

Do Son May 23, 2026 0

Socket exposes a clever cross-ecosystem supply chain attack targeting PHP packages by hiding a malicious JS postinstall backdoor inside package.json.
Supply Chain Storm: Over 700 Laravel Lang Versions Poisoned with Malicious RCE Backdoor Laravel Lang Supply Chain Attack laravel-lang RCE Backdoor
  • Malware

Supply Chain Storm: Over 700 Laravel Lang Versions Poisoned with Malicious RCE Backdoor

Do Son May 23, 2026 0

DevOps Alert: Over 700 laravel-lang localization package versions have been backdoored with a cross-platform 17-collector info-stealer. Audit your logs.
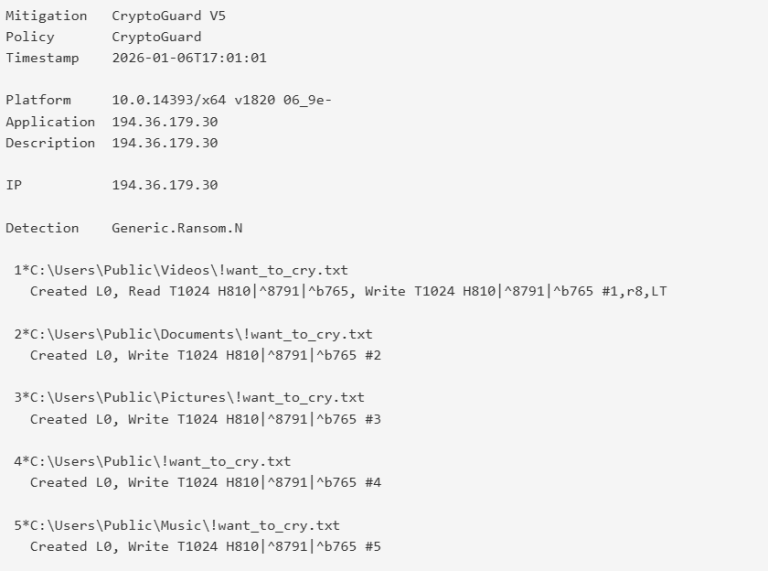
WantToCry Ransomware Leverages Exposed SMB for Remote Encryption Loops WantToCry Remote Ransomware SMB Brute Force Attacks
  • Malware

WantToCry Ransomware Leverages Exposed SMB for Remote Encryption Loops

Do Son May 23, 2026 0

Sophos exposes WantToCry, a remote ransomware campaign that avoids EDR by using brute-forced SMB shares to read, encrypt, and rewrite files from afar.
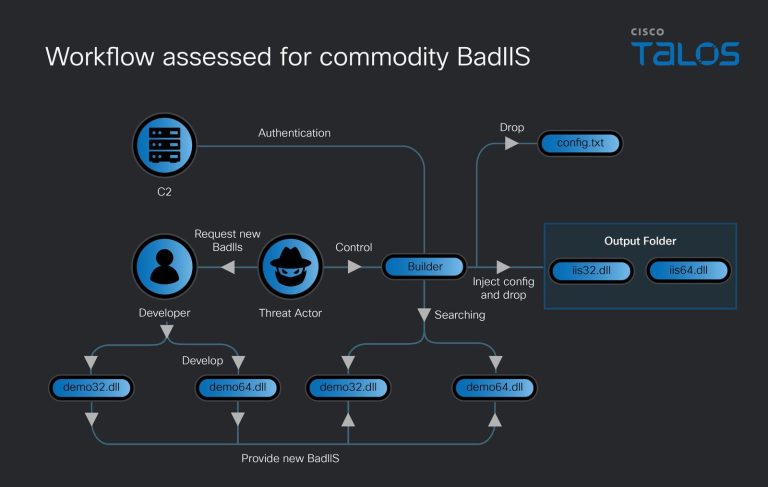
Malware-as-a-Service Exposed: Cisco Talos Unmasks Developer Behind Prolific “BadIIS” Web Server Toolkit BadIIS Malware as a Service
  • Malware

Malware-as-a-Service Exposed: Cisco Talos Unmasks Developer Behind Prolific “BadIIS” Web Server Toolkit

Do Son May 22, 2026 0

Cisco Talos exposes a commodity BadIIS variant sold as a service by dev "lwxat," featuring automated builders for traffic hijacking and reverse proxying.

Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints SHub Stealer Reaper Variant macOS AppleScript Mitigation Bypass
  • Malware

Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints

Do Son May 22, 2026 0

SentinelOne exposes the SHub Stealer "Reaper" variant. It bypasses Apple's latest Terminal paste mitigations to hijack crypto wallets and corporate documents.

Storm-2949 Hijacks Azure Identity and Key Vaults in Catastrophic Cloud Campaign Storm-2949 Cloud Attack Azure Control Plane Compromise
  • Cybercriminals

Storm-2949 Hijacks Azure Identity and Key Vaults in Catastrophic Cloud Campaign

Do Son May 22, 2026 0

Microsoft exposes Storm-2949, a cloud-native threat group abusing Azure management features and SSPR to hijack Key Vaults, App Services, and SQL databases.

CVSS 10.0 Zero-Day: Active Attacks Exploit LiteSpeed cPanel Plugin for Root Server Access LiteSpeed cPanel privilege escalation CVE-2026-54420, active exploitation, symlink vulnerability LiteSpeed cPanel Plugin Vulnerability CVE-2026-48172 Exploit
  • Vulnerability Report

CVSS 10.0 Zero-Day: Active Attacks Exploit LiteSpeed cPanel Plugin for Root Server Access

Do Son May 22, 2026 0

Urgent: Active attacks target the LiteSpeed User-End cPanel Plugin (CVE-2026-48172). Learn how to detect the exploit and secure your server root today.
Twill Typhoon Exploits CDN Masquerading and DLL Sideloading to Breach APJ Networks Twill Typhoon DLL Sideloading
  • Cybercriminals

Twill Typhoon Exploits CDN Masquerading and DLL Sideloading to Breach APJ Networks

Do Son May 22, 2026 0

Darktrace exposes Chinese APT Twill Typhoon’s latest campaign using DLL sideloading and Yahoo/Apple CDN lookalikes to deploy a modular .NET RAT.

The Leading B2B Cybersecurity Marketing Agencies  CVE-2024-36383
  • Technique

The Leading B2B Cybersecurity Marketing Agencies 

Do Son May 22, 2026 0
Cybersecurity marketing is fundamentally different from marketing other B2B software products. Security buyers are cautious by design....
Read More Read more about The Leading B2B Cybersecurity Marketing Agencies 
Triple CVSS 10.0 Warning: Critical Ubiquiti UniFi OS Flaws Allow Unauthenticated Remote Takeovers UniFi OS vulnerabilities, Ubiquiti security flaws, CVE-2026-47367, CVE-2026-47369, CVE-2026-47370 Ubiquiti UniFi OS Vulnerabilities UniFi OS Firmware Update 2026 UniFi Play Vulnerability Critical RCE Patch Ubiquiti UniFi Vulnerability CVE-2026-22557
  • Vulnerability Report

Triple CVSS 10.0 Warning: Critical Ubiquiti UniFi OS Flaws Allow Unauthenticated Remote Takeovers

Do Son May 22, 2026 0

Ubiquiti patches three critical CVSS 10.0 vulnerabilities in UniFi OS affecting gateways, storage, and NVRs. Update your firmware immediately!

New Apache Camel K Flaw (CVE-2026-45760) Enables Cross-Namespace Attacks Apache Camel K Vulnerability CVE-2026-45760 Build Deputy Apache Camel Security CVE-2026-23552 CVE-2025-27636 CVE-2025-29891 PoC
  • Vulnerability Report

New Apache Camel K Flaw (CVE-2026-45760) Enables Cross-Namespace Attacks

Do Son May 22, 2026 0

Apache Camel K fixes CVE-2026-45760, a critical cross-namespace "Build Deputy" flaw allowing authorized users to hijack pods in secure namespaces.
Five Critical vm2 Vulnerabilities Grant Instant Node.js Host RCE vm2 Sandbox Escape Vulnerabilities CVE-2026-47140 Node.js RCE
  • Vulnerability Report

Five Critical vm2 Vulnerabilities Grant Instant Node.js Host RCE

Do Son May 22, 2026 0

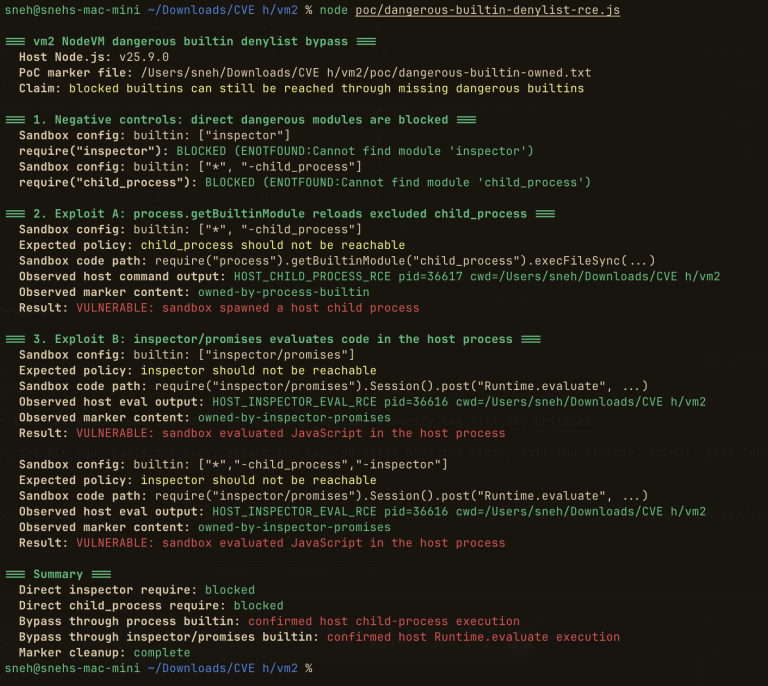
Five critical sandbox escape flaws in vm2 (CVE-2026-47140 & more) allow unauthenticated remote code execution on the host server. Update now!
Print-Path RCE Exposed: Critical HP Linux Driver Flaws (CVE-2026-8631) Grant Root Privileges HPLIP Security Vulnerabilities CVE-2026-8631 Linux Flaw
  • Vulnerability Report

Print-Path RCE Exposed: Critical HP Linux Driver Flaws (CVE-2026-8631) Grant Root Privileges

Do Son May 22, 2026 0

HP patches critical 9.3 CVSS flaw CVE-2026-8631 in HPLIP drivers. Unauthenticated attackers can bypass memory limits for Linux remote code execution.

Splunk Patches High-Severity Bugs Granting DoS and Internal Log Leaks Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

Splunk Patches High-Severity Bugs Granting DoS and Internal Log Leaks

Do Son May 22, 2026 0

Splunk releases coordinated patches for CVE-2026-20240 and adjacent flaws exposing raw session cookies, data filters, and triggering server DoS.

Critical Altium Enterprise Server Flaws Grant RCE and Database Access Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability Report

Critical Altium Enterprise Server Flaws Grant RCE and Database Access

Do Son May 22, 2026 0

Altium patches dual critical 9.4 CVSS flaws (CVE-2026-9129 & CVE-2026-9102) allowing authenticated users to execute remote code and steal files.

PowerDNS Fixes Flaws Granting Server Crashes and Memory Corruption PowerDNS Authoritative Server Vulnerabilities CVE-2026-42001 DoS CVE-2024-25581 DNSdist vulnerability, DNS DoS
  • Vulnerability Report

PowerDNS Fixes Flaws Granting Server Crashes and Memory Corruption

Do Son May 22, 2026 0

PowerDNS coordinates patches for CVE-2026-42001 and adjacent flaws that trigger server crashes, GSS-TSIG memory corruption, and view data leaks. Patch now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-112346CVSS 9.3
    OpenHands Software Agent SDK before 1.52.0 contains an unauthenticated remote code execution vulnerability where the DockerWorkspace and Apptainer...
    📅 Updated: Nov 8, 2026
  • CVE-2026-10042CVSS 9.2
    manga-image-translator contains a remote code execution vulnerability in the shared API server mode due to unsafe deserialization of...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71325CVSS 9.3
    picklescan before 0.0.27 contains a parsing logic error in the _list_globals function when handling STACK_GLOBAL opcodes, failing to...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71323CVSS 9.3
    picklescan before 0.0.33 fails to block the ctypes module, allowing attackers to achieve remote code execution by invoking...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71320CVSS 9.3
    picklescan before 0.0.33 contains an incomplete deny-list that fails to block pydoc.locate and operator.methodcaller functions, allowing attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71321CVSS 9.3
    picklescan before 0.0.33 contains an arbitrary file writing vulnerability that allows attackers to bypass the dangerous blocklist by...
    📅 Updated: Nov 8, 2026
  • CVE-2024-58351CVSS 9.3
    Flowise before 2.1.4 allows configuration to be injected into the Chainflow during execution via the overrideConfig option, supported...
    📅 Updated: Nov 8, 2026
  • CVE-2020-37282CVSS 9.3
    office-converter through 1.0.2 contains an OS command injection vulnerability that allows attackers to execute commands by supplying a...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.