
 Do Son
Seeing a new SecureBoot folder under C:\Windows? Microsoft confirms it is part of an essential KB5089549 update to replace expiring 2011 UEFI certificates.

TeamPCP has open-sourced the Shai-Hulud supply chain worm. Multiple malicious typosquatted NPM packages are already weaponizing the AI-synthesized code.

Critical 18-year-old "NGINX Rift" flaw CVE-2026-42945 is under active exploitation. Learn how to patch your proxies and block the unauthenticated heap overflow.

At WinHEC 2026, Microsoft launched the Driver Quality Initiative to penalize poorly optimized OEM hardware drivers that cause laptop overheating and sleep battery drain.

Microsoft pivots on its "by design" stance, updating Edge to version 148.0 to stop caching your entire plaintext password vault in active volatile memory.

Canonical has officially opened the GUI upgrade gate from Ubuntu 25.10 to Ubuntu 26.04 LTS. Learn why the path was delayed and what it means for 24.04 users.
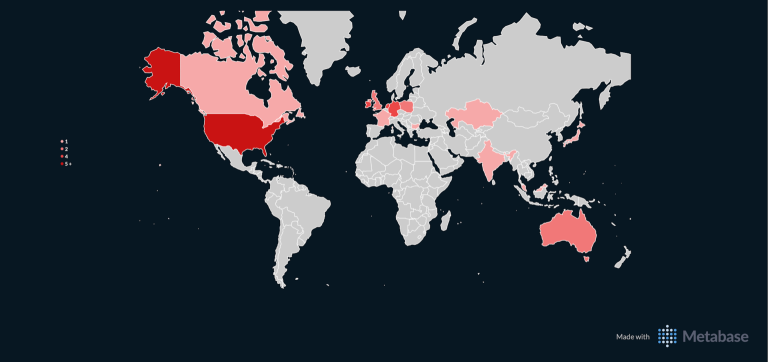
Urgent: CrowdSec warns CVE-2024-9643 in Four-Faith routers has hit mass exploitation phase. Attackers abuse hardcoded logins to build botnets. Patch now!

Urgent: Malicious Nx Console v18.95.0 briefly hit the VS Code Marketplace, targeting 2M+ installs with a macOS backdoor and token stealer. Audit now!

PostgreSQL releases updates for versions 14-18 fixing 11 vulnerabilities (CVSS 8.8). Plus, critical End-of-Life deadline issued for Postgres 14.

Technical details and GitHub PoC exploits disclosed for PostgreSQL pgcrypto CVE-2026-2005. Low-privilege users can seize root superuser RCE. Patch now!

CVE-2026-46442 in Flowise allows authenticated users to escape the NodeVM sandbox and execute system commands. Secure your AI infrastructure now!
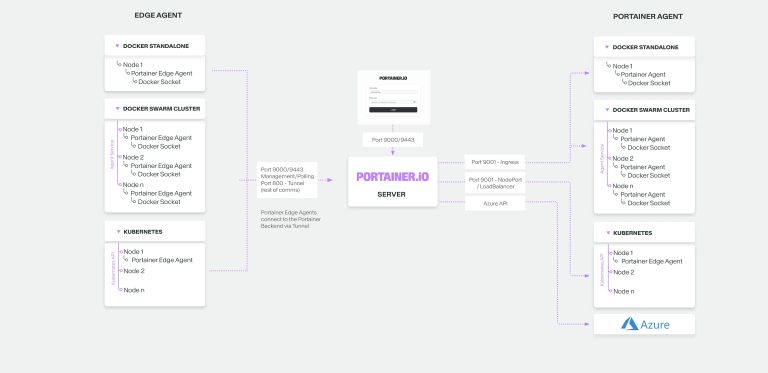
Portainer fixes two critical 9.4 CVSS flaws (CVE-2026-44848/49) allowing instant container escape to host root. Patch your environments now!
Marten .NET library suffers a critical 9.8 CVSS SQL injection flaw (CVE-2026-45288). Learn how to block the exploit and patch your databases now!

Cato CTRL intercepts "TencShell," a new stealth malware derived from open-source Rshell. Attackers use third-party access to breach networks!

McAfee Labs exposes a massive CountLoader campaign using EtherHiding and AMSI bypass to drop stealthy cryptocurrency clippers. Secure your assets!

Sysdig exposes "NATS-as-C2" infrastructure exploiting Langflow RCE (CVE-2026-33017). Learn how to defend your AI pipelines and block the exploit.

16GB Rocket database leak exposes The Gentlemen ransomware cartel. Check Point Research unmasks their RaaS tactics, AI tools, and active exploits.

Gamaredon targets critical systems by exploiting WinRAR vulnerability CVE-2025-8088 to drop GammaDrop malware. Secure your entry points now!
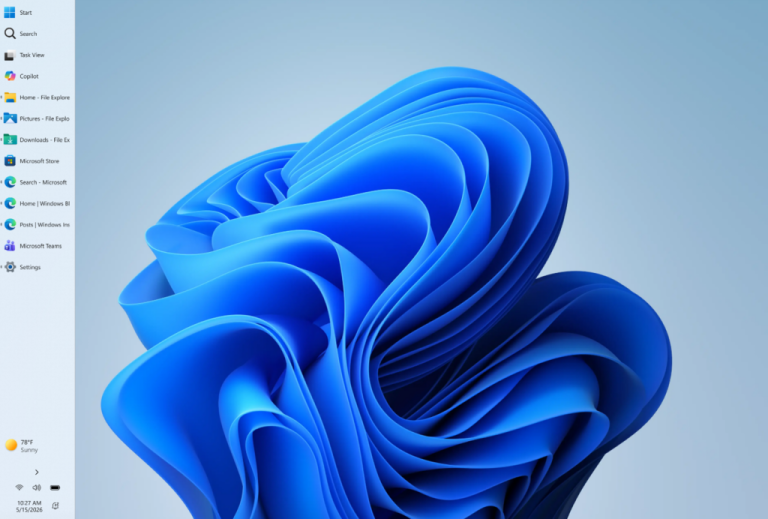
Microsoft restores the movable taskbar and introduces a resizable Start menu in Windows 11. Discover how to customize your workspace for peak productivity.

OpenAI launches Finances for ChatGPT Pro! Integrated with Plaid, the AI securely reads your real-time bank and investment data for custom wealth advice.

Critical CVE-2026-35194 flaw in Apache Flink allows RCE via SQL injection on TaskManagers. Upgrade your clusters immediately to secure your data!
Two critical flaws in Strapi CMS (CVE-2026-27886 & CVE-2026-22599) allow unauthenticated admin takeover and SQL injection. Update your nodes now!