
 Do Son
NVIDIA issued an urgent patch for a critical 9.8 CVSS flaw in the FLARE SDK. Stop unauthenticated RCE and data tampering. Upgrade to v2.7.2 immediately.

Google Translate celebrates 20 years by adding AI-driven pronunciation feedback. Practice English, Spanish, and Hindi with real-time phonetic corrections.

AWS and OpenAI expand their alliance, bringing GPT models, Codex, and managed AI agents to Amazon Bedrock with enterprise-grade security and consolidated billing.

AWS unveils Amazon Quick, a "borderless" desktop AI assistant with long-term memory. It integrates local files with Slack, Teams, and Salesforce for proactive work.

Apple’s iOS 27 leaks reveal a massive AI pivot: a Gemini-powered Siri App and generative "Extend" and "Reframe" tools to rival Google’s Magic Editor.

Google signs a secret deal with the Pentagon, allowing Gemini AI use for "any lawful purpose." With no veto power, 600 employees revolt over ethics and safety.

Citizen Lab reveals "Tall Tales," a PRC campaign using GLITTER CARP and SEQUIN CARP to hunt activists and ICIJ journalists via private contractors.

Amazon Connect evolves into a suite of Agentic AI solutions for supply chain, hiring, and health. Discover how AWS is leading the shift to Agent-as-a-Service.
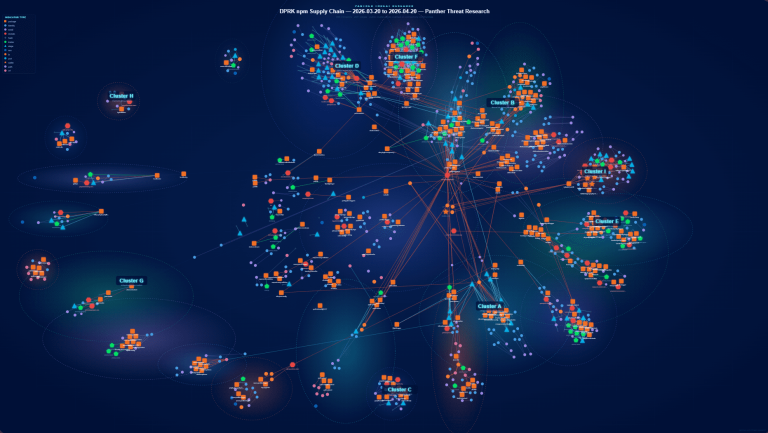
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
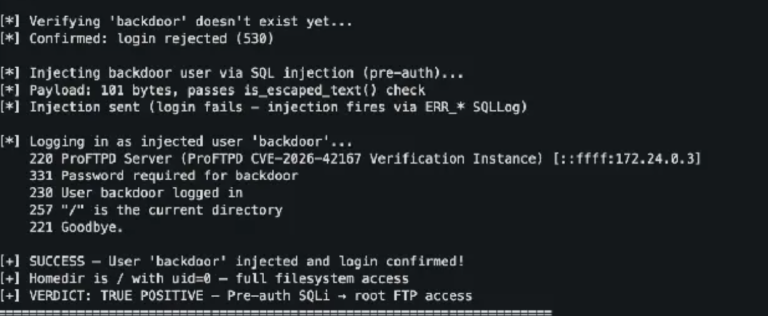
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
Critical SQLi in ProFTPD's mod_sql allows unauthenticated admin account injection. Full PoC code is public. Upgrade to v1.3.9a to secure your servers.

Checkmarx discloses a major GitHub breach via a Trivy supply chain flaw. Attackers injected malicious code and exfiltrated data for a month. Get the facts.
CISA warns as North Korean and Russian hackers weaponize ConnectWise and Windows Shell flaws. Patch by May 12, 2026, to prevent state-sponsored espionage.

Vimeo metadata and customer emails were exposed via a breach at third-party vendor Anodot. Internal systems remain secure. Learn how to manage vendor risk.
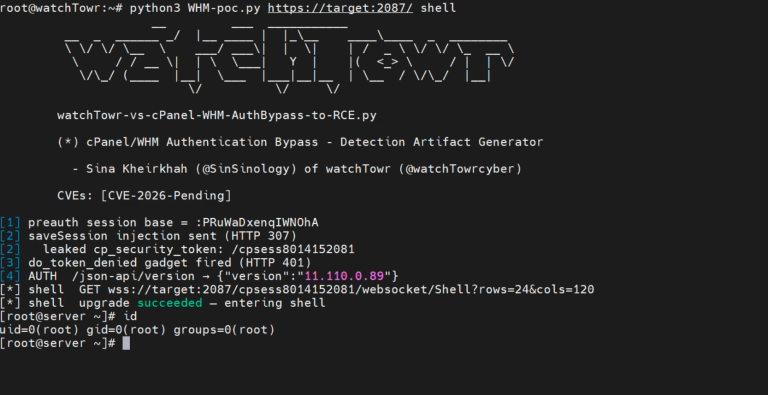
cPanel issues emergency patches for a critical authentication vulnerability affecting all supported versions. Run /scripts/upcp --force immediately to patch.

Google Chrome version 147 is here with 30 vital security fixes. High-severity Use After Free bugs and V8 flaws are patched. Update your browser today.

ClickUp discloses a configuration flaw exposing 893 emails and a live API token via Split.io feature flags. Learn how client-side SDKs became a public leak.

Wiz Research reveals CVE-2026-3854, a critical GitHub RCE. One git push could expose millions of repos. GHES users must patch to v3.19.3 immediately.
Langflow patches a critical 9.6 CVSS path traversal vulnerability (CVE-2026-42048). Learn how an unsafe bulk delete function put entire filesystems at risk.

Apache Thrift fixes critical cross-language vulnerabilities (MitM, memory corruption, DoS). Secure your Java, Go, and C++ stacks by upgrading to version 0.23.0.

Critical 9.0 CVSS RCE in Nginx UI (CVE-2026-42238) exploits a 10-minute unauthenticated window. Attackers can seize root control. Patch to the latest version now.

Critical RCE flaws hit Apache Camel via header injection and unsafe deserialization. Secure your integrations and upgrade to version 4.20.0 today.

BlueNoroff uses a "self-reinforcing" deepfake pipeline to target crypto CEOs. Fake Zoom meetings and stolen footage lead to a 5-minute system compromise.