
 Do Son
Esri issues an urgent fix for critical 9.8 CVSS flaws in ArcGIS. Over-scoped developer credentials could expose GIS data. Patch your portal immediately.
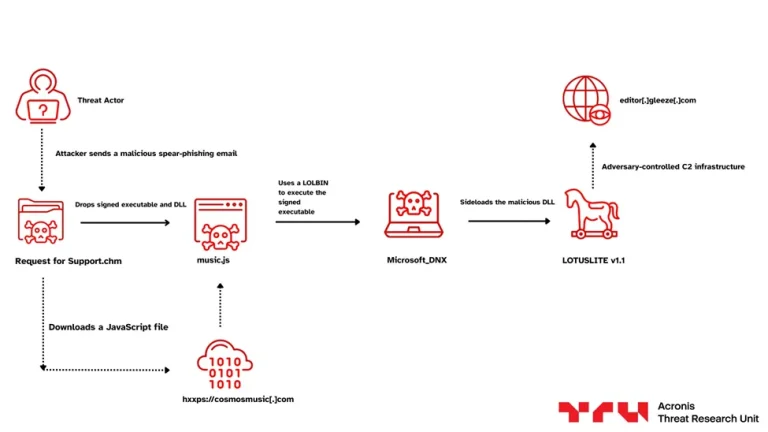
Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.

Kaspersky uncovers Lotus Wiper, a destructive malware targeting Venezuela's energy sector. Designed for pure sabotage, it leaves systems unrecoverable.

Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.
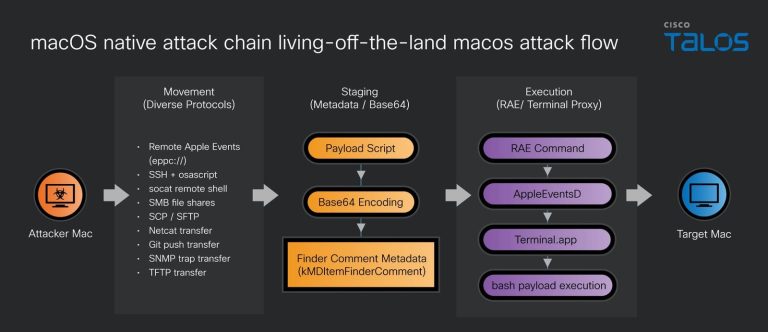
Cisco Talos reveals how attackers use native macOS features like Spotlight and SNMP to hijack enterprise workstations. Secure your DevOps environment today.
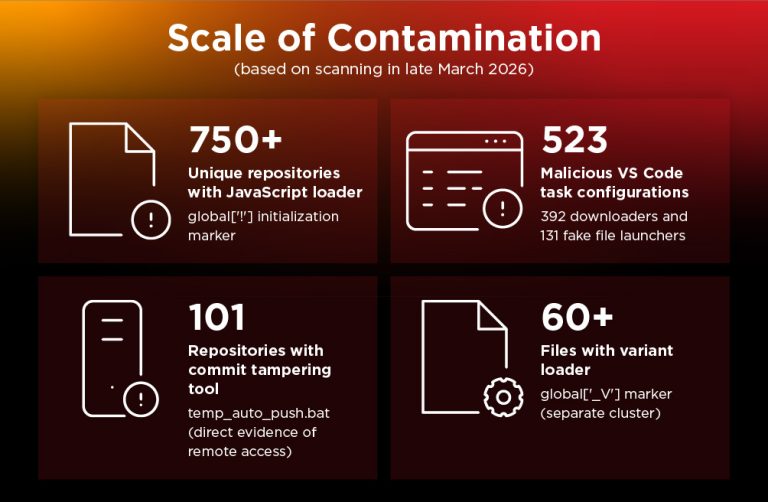
Void Dokkaebi turns developers into vectors. With 750+ infected repos and malicious VS Code tasks, this supply chain worm is hunting your CI/CD and crypto.

The critical "Pack2TheRoot" flaw (CVE-2026-41651) in PackageKit gives root access on Linux. It went undetected for 12 years. Update to version 1.3.5 now!
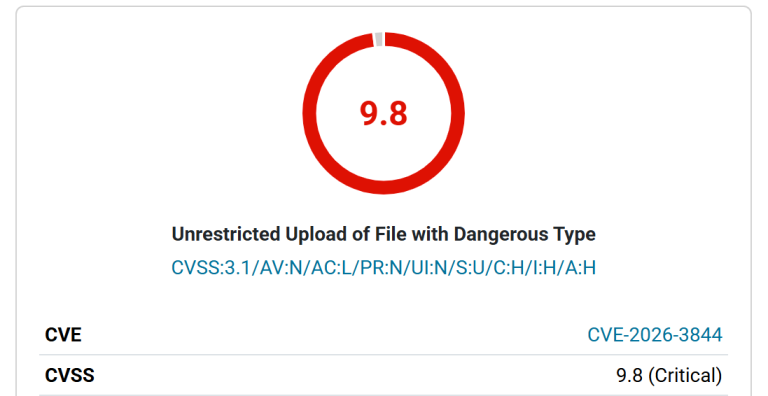
Critical 9.8 CVSS RCE hits 400,000+ WordPress sites using the Breeze plugin. Attackers are exploiting arbitrary file uploads. Update to v2.4.5 immediately!
CVE-2026-33626: A critical SSRF in LMDeploy exploited in under 13 hours. Learn how attackers hijack AI nodes and how to secure your inference cloud now.
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
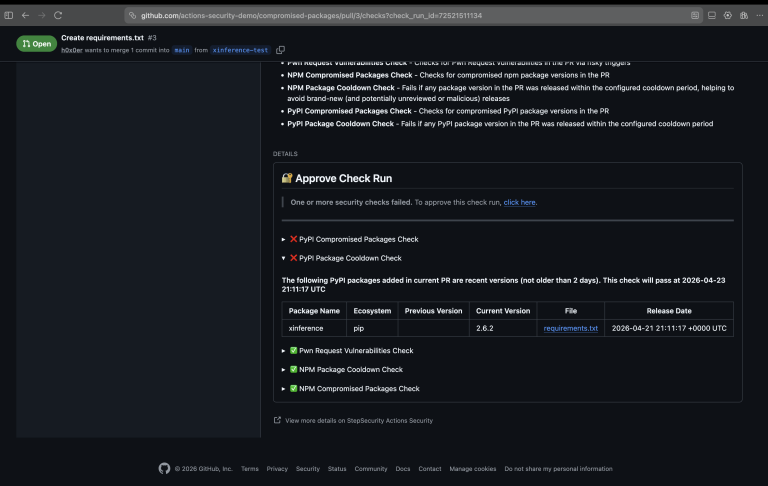
Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.
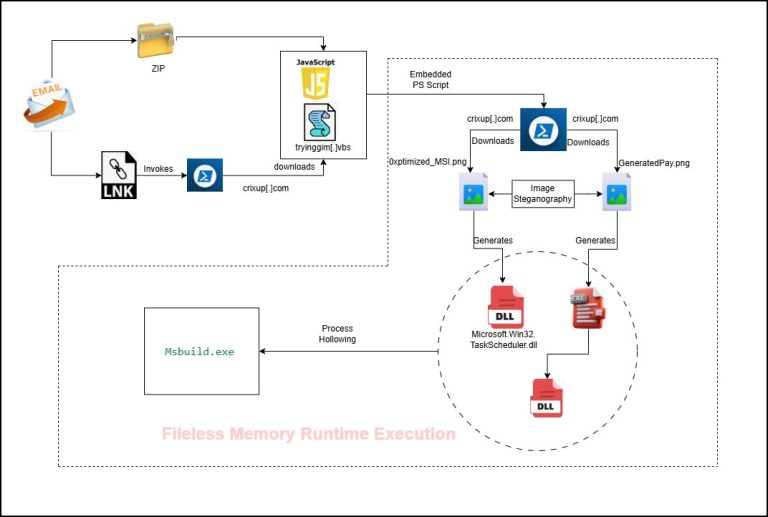
Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.

CISA adds BlueHammer (CVE-2026-33825) to the KEV catalog. This Microsoft Defender LPE exploit uses TOCTOU to hijack SAM databases. Patch by May 6, 2026.
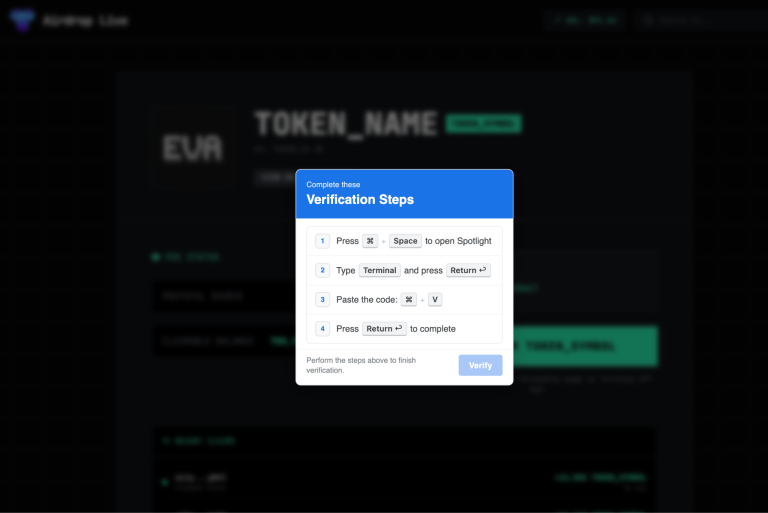
Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.
ElectricSQL reveals a critical 10.0 CVSS SQL injection (CVE-2026-40906). Attackers can hijack PostgreSQL and bypass tenant isolation. Patch to v1.5.0 now.

PHPUnit CVE-2026-41570 allows RCE via invisible newline injection in CI/CD pipelines. Secure your build servers—update to 12.5.22 or 13.1.6 today.

NVIDIA patches critical flaws in KAI Scheduler and CUDA-Q. CVE-2026-24189 and CVE-2026-24177 risk data leaks and DoS. Secure your GPU workloads—update today!

GitLab fixes high-severity GraphQL CSRF and Web IDE vulnerabilities in versions 18.11.1, 18.10.4, and 18.9.6. Protect your sessions and projects—patch now!
Critical 10.0 CVSS flaw in Firebird Database allows RCE via path traversal in the engine loader. Attackers gain root/SYSTEM privileges. Patch to 5.0.4+ now.

SpaceX secures a $600 billion option to acquire Cursor AI. Discover how the "Vibe Coding" pioneer is leveraging xAI’s Colossus supercomputer to build the world's most powerful models.

Mozilla used Anthropic’s Claude Mythos to fix 271 Firefox vulnerabilities. Discover how AI is finally flipping the script on the cybersecurity "cost asymmetry."

OpenAI launches ChatGPT Images 2.0! Discover the new "Thinking" mode, near-perfect multilingual text rendering, and flexible 2K resolutions for all users.