 Do Son
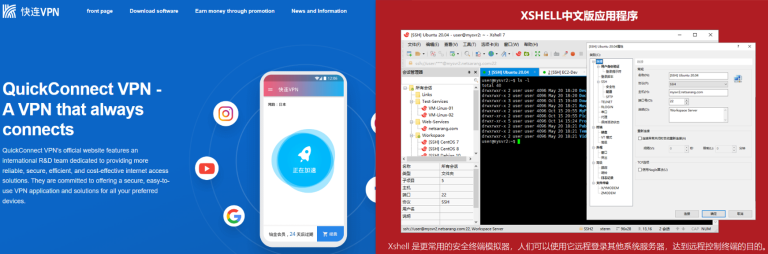
Kong RAT: A year-long SEO poisoning campaign targeting developers with trojanized SSH/VPN tools and .NET NativeAOT stealth. Learn how to stay protected.

Meta is testing "WhatsApp Plus," a new subscription tier offering exclusive themes, 20 pinned chats, and animated stickers. See what’s changing in 2026.

Anthropic and Amazon ink a historic $100B deal for 5GW of power. See how "Project Rainier" and Trainium chips are set to challenge the OpenAI-Microsoft throne.
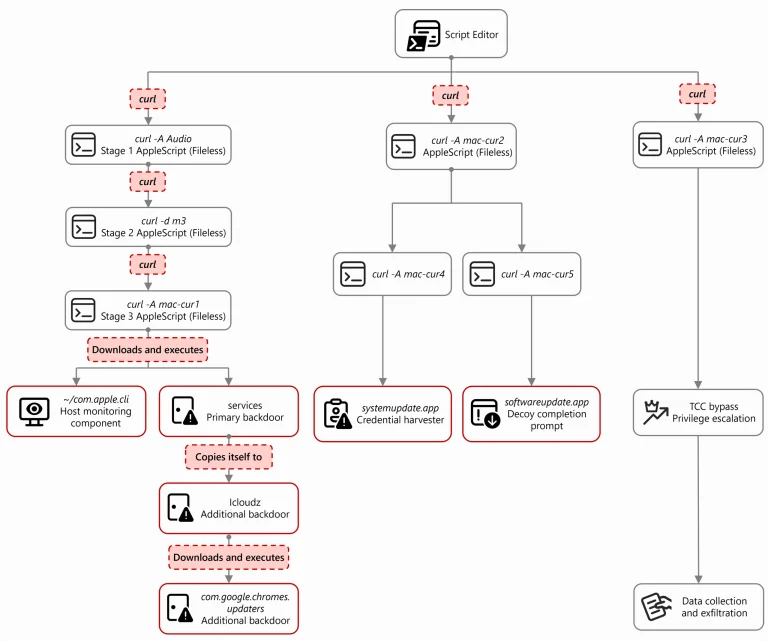
Microsoft uncovers Sapphire Sleet's macOS campaign. Using fake recruiters and AppleScript, they bypass TCC to steal crypto wallets, Telegram, and SSH keys.

Former ransomware negotiator Angelo Martino pleaded guilty to working with BlackCat to extort his own clients. $10M in luxury assets seized. Facing 20 years.
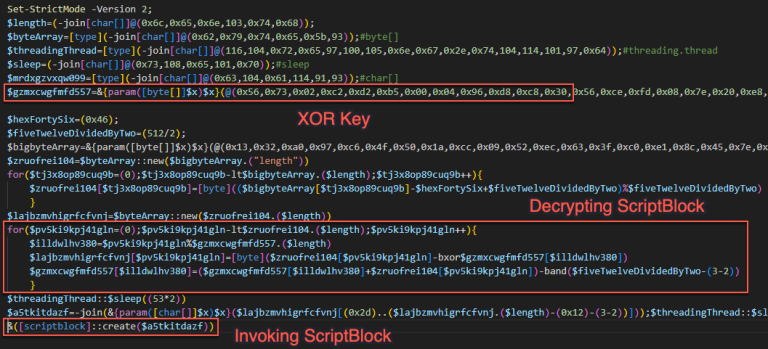
Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.

Atlassian’s new AI policy arrives Aug 17, 2026. Learn which tiers face mandatory data collection and how to protect your Jira and Confluence content.

Privacy expert Alexander Hanff warns that Claude Desktop installs a "native messaging bridge" without consent, potentially bypassing browser security sandboxes.

Tyler Buchanan pleads guilty in US court for an $8M cyber heist. Discover how SMS phishing and SIM swapping bypassed 2FA to drain corporate & crypto assets.

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.

Cyber attacks are increasing at an alarming rate, with organizations across the globe facing more frequent and...

Progress Kemp LoadMaster reveals 5 high-severity vulnerabilities, including a WAF bypass and OS command injection. Secure your ADC with the April 2026 patch.

BitSight unmasks RondoDox: a modular botnet using "nanomites" to dodge debuggers while hijacking 18 architectures for Monero mining and gaming DoS attacks.

ASUSTOR issues an urgent fix for CVE-2026-6644, a critical 9.4 CVSS flaw in ADM's VPN client allowing full NAS takeover. Patch to ADM 5.1.3.RGL1 now.

Darktrace uncovers ZionSiphon, a malware strain targeting water treatment via Modbus logic. Discover the new frontier of Israel-focused industrial sabotage.

 Nikolay Milyaev
Walk into a security operations center at almost any large enterprise in 2026 and the scene is...
Healthcare organizations face some of the highest-stakes cybersecurity risks of any industry. A successful ransomware attack, credential...

Technical details and PoC for Rclone’s critical 9.2 CVSS vulnerabilities (CVE-2026-41176/41179) are now public. Patch to version 1.73.5 to prevent RCE.

Apache Syncope CVE-2025-57738 allows root RCE via unsandboxed Groovy. Technical details and PoC are now public. Upgrade to v3.0.14 or 4.0.2 immediately.

Dolibarr ERP faces a critical 9.4 CVSS RCE flaw (CVE-2026-23500) in its PDF conversion logic. Unsanitized commands allow full system takeover. Upgrade to 23.0!
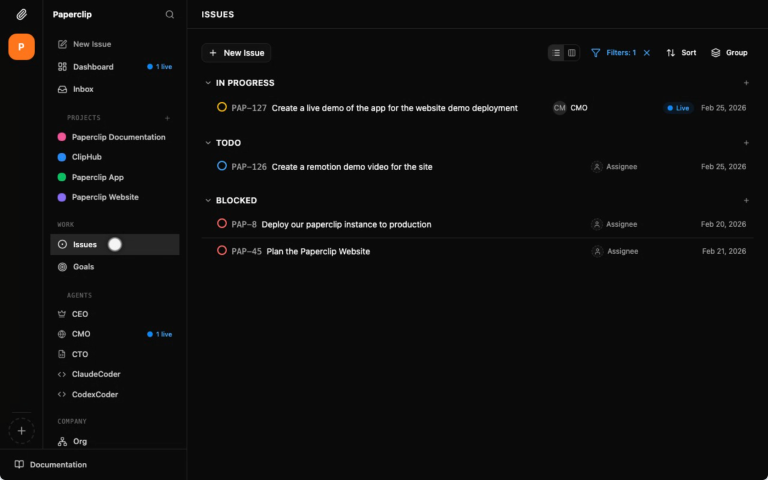
Paperclip’s 9.8 CVSS flaw and cross-tenant leaks expose AI agents to total takeover. Learn how a simple command could compromise your entire business.

Clerk reveals a critical 9.1 CVSS flaw in createRouteMatcher. Crafted requests can bypass middleware gating in Next.js, Nuxt, and Astro. Patch your apps now!