Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Critical 9.1 CVSS Bypass in Clerk’s Middleware Gating Clerk Middleware Bypass createRouteMatcher Vulnerability
  • Vulnerability Report

Critical 9.1 CVSS Bypass in Clerk’s Middleware Gating

Do Son April 20, 2026 0

Clerk reveals a critical 9.1 CVSS flaw in createRouteMatcher. Crafted requests can bypass middleware gating in Next.js, Nuxt, and Astro. Patch your apps now!
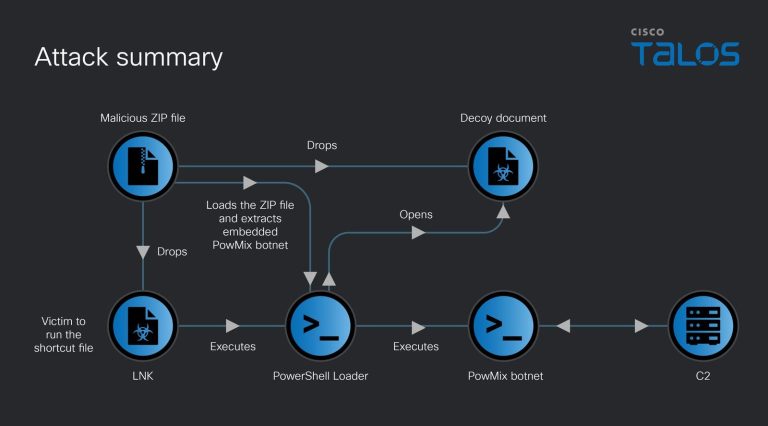
New “PowMix” Botnet Preys on Czech Workforce with Lure of Compliance PowMix Botnet AMSI Bypass
  • Malware

New “PowMix” Botnet Preys on Czech Workforce with Lure of Compliance

Do Son April 20, 2026 0

Cisco Talos uncovers PowMix, a stealthy botnet targeting Czech HR via AMSI bypass and Heroku-hosted C2. Learn how this malware evades modern EDR systems.

Cyber-Actors are “Laundering Trust” to Hijack the Global Supply Chain Load Board Phishing Signing-as-a-Service
  • Cybercriminals

Cyber-Actors are “Laundering Trust” to Hijack the Global Supply Chain

Do Son April 20, 2026 0

Proofpoint monitors a 30-day supply chain attack using "signing-as-a-service" to bypass Windows security. Protect your load boards and fleet payments now.
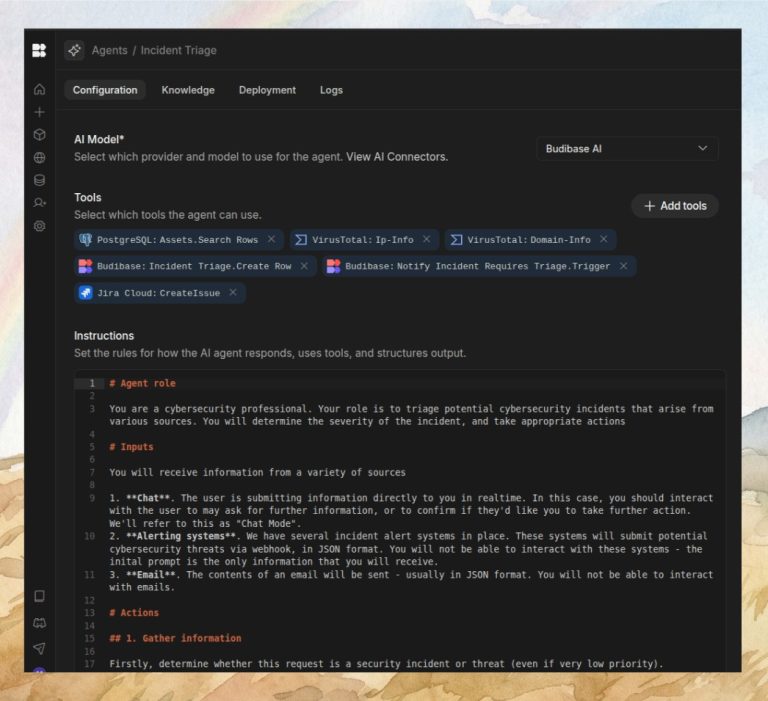
Critical 9.1 Auth Bypass Hits Budibase Operations Platform Budibase Authentication Bypass Regex URL Injection
  • Vulnerability Report

Critical 9.1 Auth Bypass Hits Budibase Operations Platform

Do Son April 20, 2026 0

A critical 9.1 CVSS flaw in Budibase lets attackers bypass auth via unanchored regex. Protect your user database—update to version 3.35.4 immediately.

Beyond the Glow: How iOS 27’s “Snow Leopard” Focus and Siri App Will Redefine the iPhone in 2026 iOS 27 rumors iOS 26.2.1 Update Apple Intelligence, iOS 26 iOS Notification Forwarding, EU DMA Compliance
  • Technology

Beyond the Glow: How iOS 27’s “Snow Leopard” Focus and Siri App Will Redefine the iPhone in 2026

Do Son April 20, 2026 0

iOS 27 is coming to WWDC 2026! Discover the new Siri "Search or Ask" interface, the standalone Siri App, and the long-awaited Home Screen Undo functionality.

The 32GB Ceiling Shatters: Microsoft Finally Ends the “Arbitrary” FAT32 Limit After 30 Years Windows 11 FAT32 limit Microsoft OOB update January 2026, Remote Desktop login shutdown bug Windows Edge Light PowerToys Ring Light
  • Windows

The 32GB Ceiling Shatters: Microsoft Finally Ends the “Arbitrary” FAT32 Limit After 30 Years

Do Son April 20, 2026 0

Microsoft has officially raised the FAT32 formatting limit to 2TB in Windows 11. Say goodbye to the 32GB restriction and third-party tools like Rufus.

Fabricked: The 100% Deterministic Attack Breaking AMD’s Confidential Computing Vault Fabricked Attack AMD SEV-SNP
  • Vulnerability Report

Fabricked: The 100% Deterministic Attack Breaking AMD’s Confidential Computing Vault

Do Son April 20, 2026 0

ETH Zurich researchers unmasked "Fabricked" (CVE-2025-54510), a flaw in AMD Infinity Fabric that bypasses SEV-SNP memory isolation. Patch your firmware today!

The Forbidden Model: Why the NSA is Secretly Using Anthropic’s Mythos AI Despite a Federal Ban Anthropic confidential IPO filing Anthropic Google $200 billion deal Anthropic Mythos Preview Anthropic Pentagon blacklist Claude Max 20x open-source Model Distillation Anthropic vs DeepSeek Claude Free tier update 2026
  • Technology

The Forbidden Model: Why the NSA is Secretly Using Anthropic’s Mythos AI Despite a Federal Ban

Do Son April 20, 2026 0

The NSA is bypassing Trump’s federal ban to use Anthropic’s Mythos Preview. Discover how this restricted "cyber-weapon" AI is transforming U.S. intelligence.

Beyond the IDE: How Google’s New Android CLI Enables 3x Faster Agent-Led Development Android CLI Android Security Zero-Interaction DoS CVE-2026-21385 Android Security Update UK CMA Apple Google regulation Google Aluminum OS Android 16 leak, ALOS Android ChromeOS merger Android sideloading certification 2026, Google developer verification APK Android AOSP biannual release, AOSP source code latency 2026 Android Zero-Day, Critical DoS Flaw Android Universal Clipboard Cross-Device Sync Gemini Nano Block, Unlocked Bootloader Android, Calling Cards Android Security Bulletin, RCE Vulnerability Android Linux GUI, Debian VM Android System Services, Google Transparency Android 16, Pixel Update
  • Android

Beyond the IDE: How Google’s New Android CLI Enables 3x Faster Agent-Led Development

Do Son April 20, 2026 0

Google launches the Android CLI for agent-centric workflows. Reduce LLM token usage by 70% and accelerate app development 3x with official AI-ready tools.

The Infinite Factory: How “Vibe Coding” Sparked a 104% Explosion in AI-Generated Apps Vibe Coding apps Vibe Coding App Store surge Vibe Coding App Store Apple 50th Anniversary hardware Brazil CADE Apple settlement, iOS third-party app stores Brazil Tim Cook Succession Apple CEO Rumors App Store Mini Apps 15% Commission Fee iOS Japan Sideloading, Third-Party App Stores Web App Store, App Discovery Apple Age Verification, Texas SB2420 Apple AI acquisitions App Store, Antitrust Apple WebKit, Japan Regulations App Store Age Ratings, Parental Controls Apple App Store, Epic Games Lawsuit
  • Technology

The Infinite Factory: How “Vibe Coding” Sparked a 104% Explosion in AI-Generated Apps

Do Son April 20, 2026 0

AI didn't kill the app—it became the production line. Discover how Vibe Coding fueled a 104% surge in new apps and the security risks facing Apple in 2026.

One Scan to Zero: The QR Code Trap Wiping Trust Wallets via Telegram Trust Wallet Drainer QR Code Phishing
  • Cybercriminals

One Scan to Zero: The QR Code Trap Wiping Trust Wallets via Telegram

Do Son April 20, 2026 0

A new QR code "drainer" targets Trust Wallet users on Telegram. It exploits the ERC-20 approve mechanism to wipe USDT. Learn how to protect your assets now.

The High-End Interregnum: Why Global Part Shortages Just Pushed the New Mac Studio to October Mac Studio M5 delay
  • Technology

The High-End Interregnum: Why Global Part Shortages Just Pushed the New Mac Studio to October

Do Son April 20, 2026 0

Apple’s next Mac Studio is reportedly delayed until October. Global memory shortages and a pivot toward MacBook production have left power users in the lurch.

The Protocol That Learns from IPv6: Why the New IPv8 Draft Is Built to Save IPv4 RFC 9620 IPv8 protocol draft
  • Technology

The Protocol That Learns from IPv6: Why the New IPv8 Draft Is Built to Save IPv4

Do Son April 20, 2026 0

Industry stakeholders submit the IPv8 draft to the IETF. Discover how its 64-bit address space and 100% IPv4 backward compatibility aim to end address exhaustion.

Zero-Day Alert: The “Red Sun” Vulnerability Turning Microsoft Defender into a Hacker’s Tool Red Sun vulnerability
  • Vulnerability Report

Zero-Day Alert: The “Red Sun” Vulnerability Turning Microsoft Defender into a Hacker’s Tool

Do Son April 20, 2026 0

Microsoft Defender faces a critical "Red Sun" vulnerability. Learn how this zero-day exploit bypasses security to grant hackers full administrative control.

Goodbye Lag: Microsoft’s “Windows K2” Project to Rebuild the Start Menu for Instant Speed Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

Goodbye Lag: Microsoft’s “Windows K2” Project to Rebuild the Start Menu for Instant Speed

Do Son April 20, 2026 0

Microsoft is rebuilding the Windows 11 Start menu with WinUI 3. Codenamed "K2," this update promises near-instant speed and the ability to hide "Recommended."

Root Access Unlocked: FortiSandbox CVE-2026-39808 Details and PoC Exploit Publicly Disclosed FortiSandbox RCE CVE-2026-39808 PoC
  • Vulnerability Report

Root Access Unlocked: FortiSandbox CVE-2026-39808 Details and PoC Exploit Publicly Disclosed

Do Son April 20, 2026 0

Critical 9.1 CVSS flaw in FortiSandbox: Full PoC & details for CVE-2026-39808 are now public. Unauthenticated root RCE is possible. Upgrade to 4.4.9 immediately.
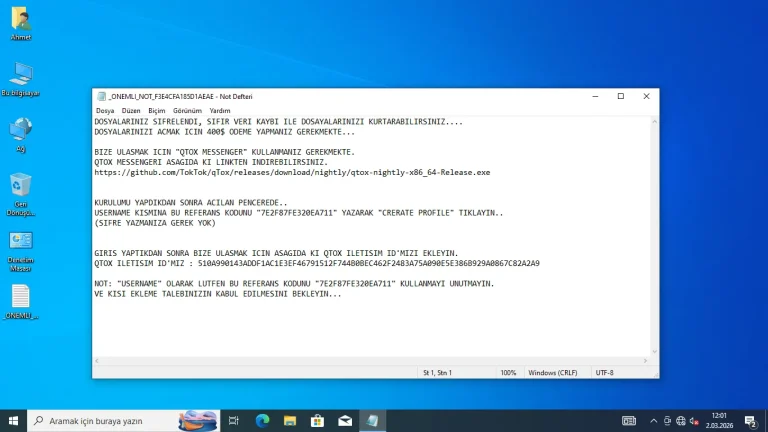
JanaWare’s 5-Year Geofenced Ransomware Reign JanaWare Ransomware Geofenced Malware
  • Malware

JanaWare’s 5-Year Geofenced Ransomware Reign

Do Son April 20, 2026 0

Acronis uncovers JanaWare, a persistent ransomware targeting Turkey since 2020. Discover how geofencing and polymorphism keep this threat in the shadows.
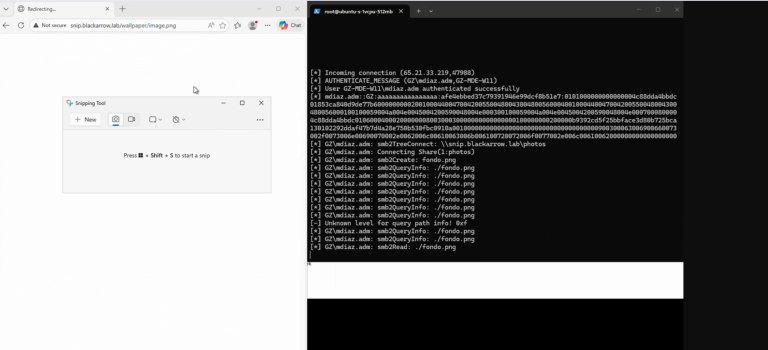
Windows Snipping Tool Can Leak Your Identity, PoC Available Snipping Tool Exploit CVE-2026-33829
  • Vulnerability

Windows Snipping Tool Can Leak Your Identity, PoC Available

Do Son April 20, 2026 0

Detailed PoC and exploit code for CVE-2026-33829 are now public. See how the Windows Snipping Tool can leak NTLM hashes and how to patch the flaw.
The CVE Watchtower: Weekly Threat Intelligence Briefing (April 13 – April 19, 2026) MCP Security Vulnerability Management
  • Weekly Recap

The CVE Watchtower: Weekly Threat Intelligence Briefing (April 13 – April 19, 2026)

Do Son April 20, 2026 0

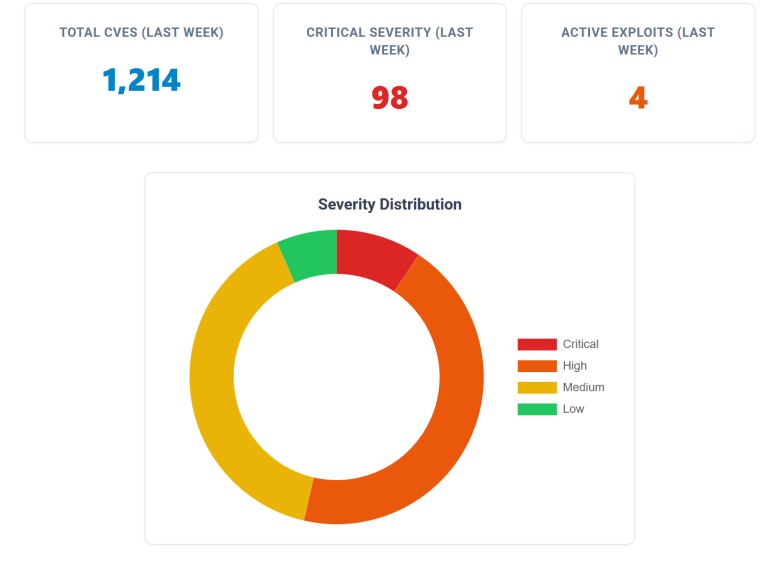
This week's digest: 1,214 new bugs, including active exploits on 2009 Excel fossils and critical 10.0 flaws in new AI/MCP infrastructure. Priority: Patch now.
More Than a Miner: The Evasive MiningDropper Framework Hijacking Android Worldwide MiningDropper Android Malware Framework
  • Malware

More Than a Miner: The Evasive MiningDropper Framework Hijacking Android Worldwide

Do Son April 20, 2026 0

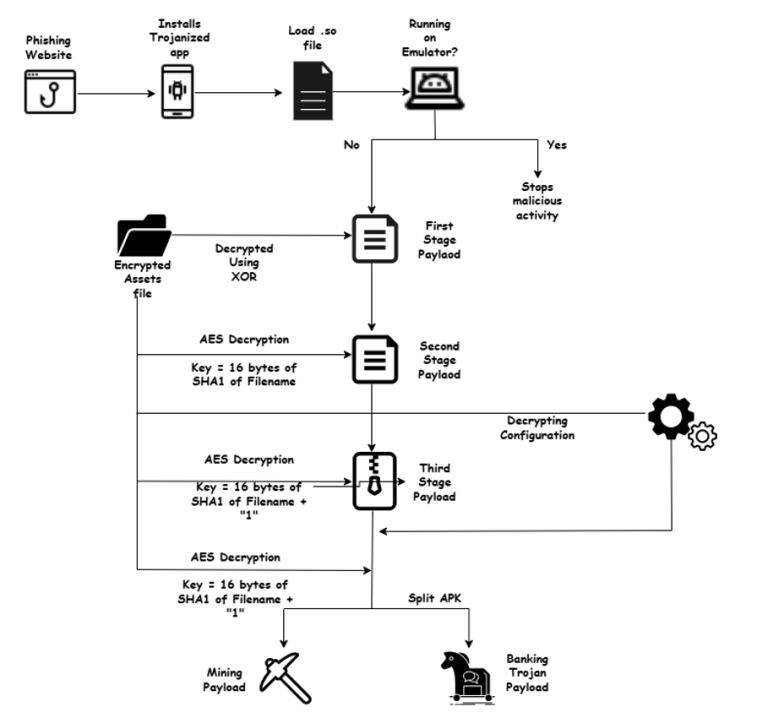
Cyble reveals MiningDropper, a modular Android threat delivering RATs and infostealers via multi-stage payloads. Protect your mobile devices now.
The Next.js Nightmare? Vercel Investigates “Critical” Internal Breach and Supply Chain Threat Vercel Supply Chain Next.js Security
  • Data Leak

The Next.js Nightmare? Vercel Investigates “Critical” Internal Breach and Supply Chain Threat

Do Son April 19, 2026 0

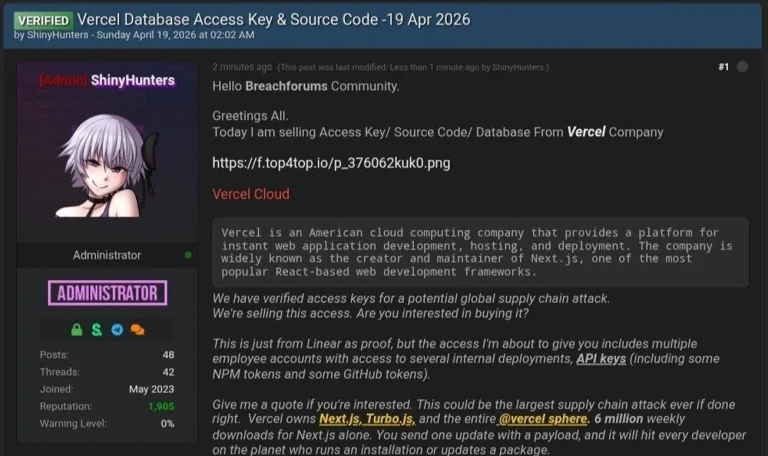
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.

Dgraph’s Debug Endpoint Hands Over Admin Tokens to Anyone Dgraph Vulnerability CVSS 10.0 Dgraph Admin Leak CVE-2026-40173
  • Vulnerability Report

Dgraph’s Debug Endpoint Hands Over Admin Tokens to Anyone

Do Son April 19, 2026 0

Dgraph (CVE-2026-40173) leaks admin tokens in plain text via unauthenticated debug endpoints. This critical 9.4 CVSS flaw allows full DB takeover. Patch now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-46408CVSS 9.8
    An issue was discovered in the methods push.lite.avtech.com.AvtechLib.GetHttpsResponse and push.lite.avtech.com.Push_HttpService.getNewHttpClient in AVTECH EagleEyes 2.0.0. The methods set ALLOW_ALL_HOSTNAME_VERIFIER,...
    📅 Updated: Nov 5, 2026
  • CVE-2025-52053CVSS 9.8
    TOTOLINK X6000R V9.4.0cu.1360_B20241207 was found to contain a command injection vulnerability in the sub_417D74 function via the file_name...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57174CVSS 9.8
    An issue was discovered in Siklu Communications Etherhaul 8010TX and 1200FX devices, Firmware 7.4.0 through 10.7.3 and possibly...
    📅 Updated: Nov 5, 2026
  • CVE-2025-56074CVSS 9.8
    A SQL Injection vulnerability was discovered in the foreigner-bwdates-reports-details.php file of PHPGurukul Park Ticketing Management System v2.0. This...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57432CVSS 9.8
    Blackmagic Web Presenter version 3.3 exposes a Telnet service on port 9977 that accepts unauthenticated commands. This service...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57601CVSS 9.8
    AiKaan Cloud Controller uses a single hardcoded SSH private key and the username `proxyuser` for remote terminal access...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57437CVSS 9.8
    The Blackmagic Web Presenter HD firmware version 3.3 exposes sensitive information via an unauthenticated Telnet service on port...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57441CVSS 9.8
    The Blackmagic ATEM Mini Pro 2.7 exposes sensitive device and stream configuration information via an unauthenticated Telnet service...
    📅 Updated: Nov 5, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.