
 Do Son
Critical 9.1 CVSS flaw in FortiSandbox: Full PoC & details for CVE-2026-39808 are now public. Unauthenticated root RCE is possible. Upgrade to 4.4.9 immediately.
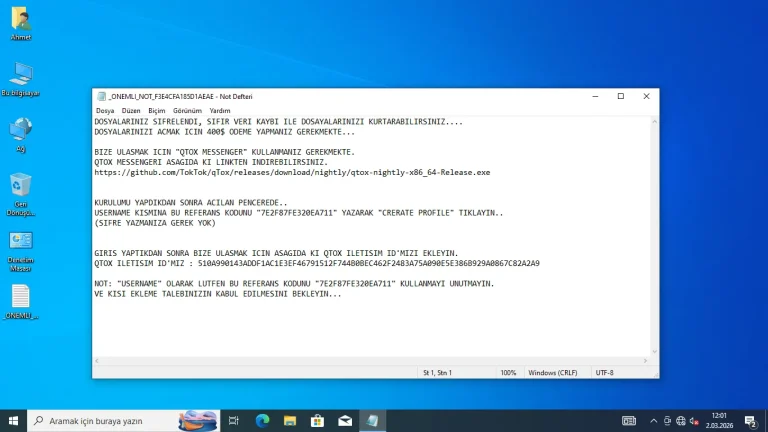
Acronis uncovers JanaWare, a persistent ransomware targeting Turkey since 2020. Discover how geofencing and polymorphism keep this threat in the shadows.
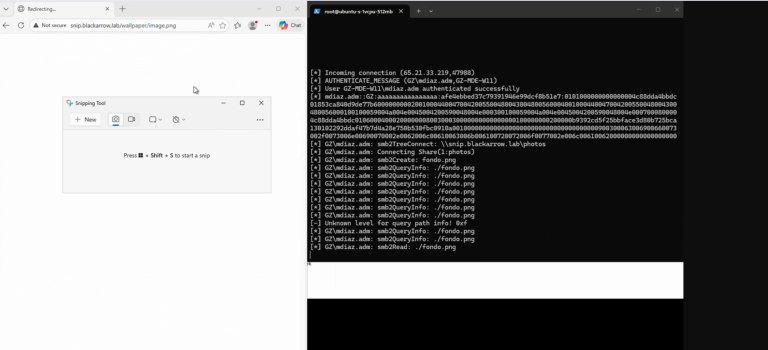
Detailed PoC and exploit code for CVE-2026-33829 are now public. See how the Windows Snipping Tool can leak NTLM hashes and how to patch the flaw.
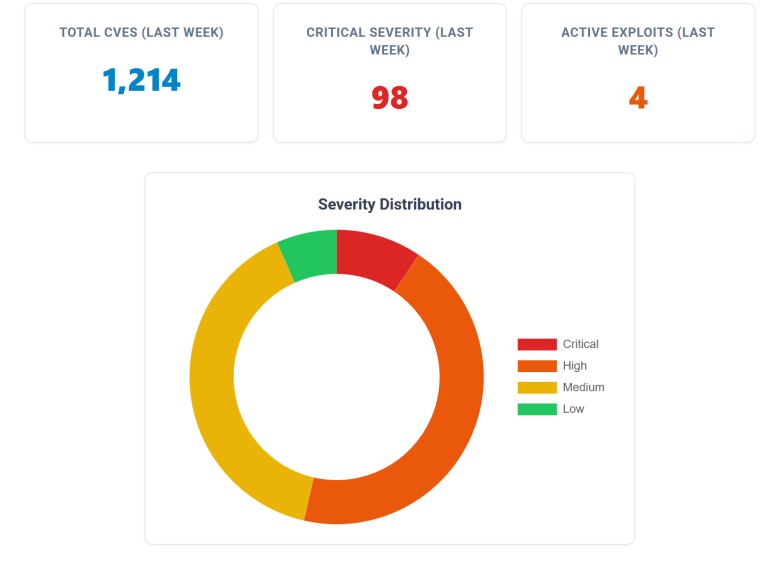
This week's digest: 1,214 new bugs, including active exploits on 2009 Excel fossils and critical 10.0 flaws in new AI/MCP infrastructure. Priority: Patch now.
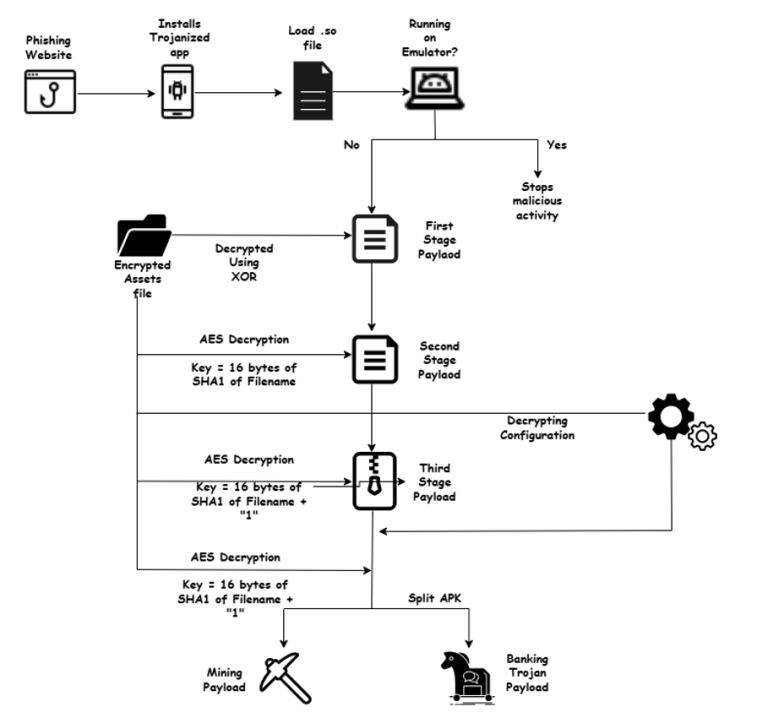
Cyble reveals MiningDropper, a modular Android threat delivering RATs and infostealers via multi-stage payloads. Protect your mobile devices now.
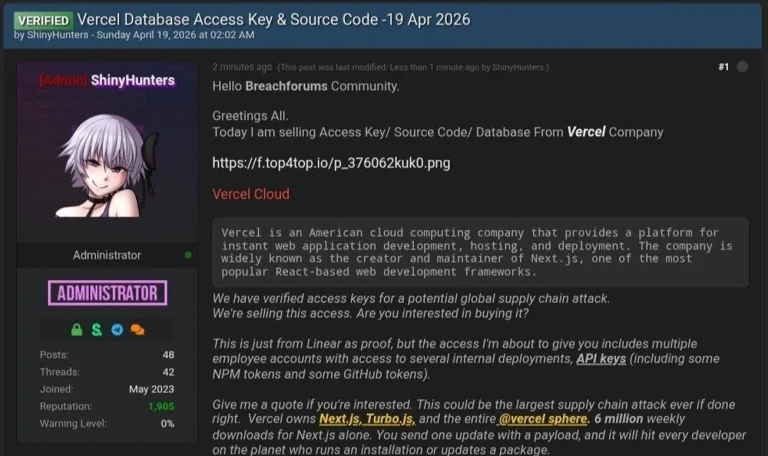
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.

Dgraph (CVE-2026-40173) leaks admin tokens in plain text via unauthenticated debug endpoints. This critical 9.4 CVSS flaw allows full DB takeover. Patch now!

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!

Apache Kafka faces a critical OAUTHBEARER bypass (CVE-2026-33557) and sensitive logging leaks. Secure your data pipelines—patch to v4.1.2 or v4.2.0 today.

The EU’s 2026 DMA draft orders Google to share query, click, and ranking data with rivals. Explore how this "data handover" aims to level the search market.
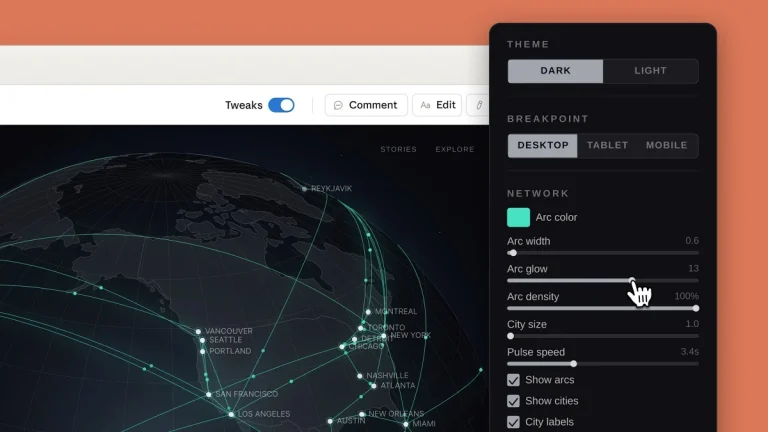
Anthropic launches Claude Design! Powered by the Opus 4.7 vision model, it creates UI prototypes and brand-aligned assets that follow your specific codebase.
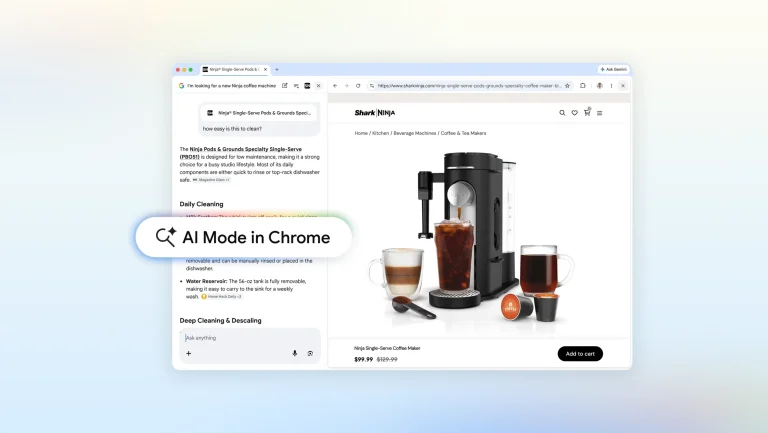
Google Chrome’s April 2026 update ends tab-switching. Use the new side-by-side AI Mode and "Plus" menu to synthesize data across tabs, PDFs, and images instantly.

AVEVA alerts on a 9.3 critical flaw in Pipeline Simulation. Unauthenticated users can hijack admin roles and alter data. Upgrade to version 2025 SP1 P01 now.
Thymeleaf 3.1.4 fixes two critical 9.1 CVSS vulnerabilities. Unauthenticated attackers can bypass security for SSTI. Audit your user input and patch today!

Critical 9.1 CVSS flaw in Horner Automation PLCs allows unauthenticated brute force attacks. Secure your industrial systems—patch XL4, XL7, and Cscape now!
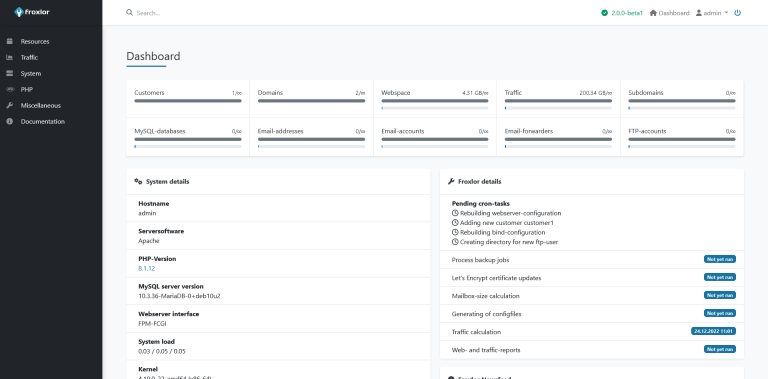
Froxlor faces two critical flaws, including a CVSS 10. Learn how path traversal and config injection allow persistent RCE. Patch your server management today!

Critical 9.1 flaw in upKeeper Instant Privilege allows standard users to gain LocalSystem rights via command injection. Patch to v1.6.0.4576 immediately.
Opera shatters vendor lock-in with "Browser Connector." Now, ChatGPT and Claude can read your active tabs and summarize web content directly within Opera One.
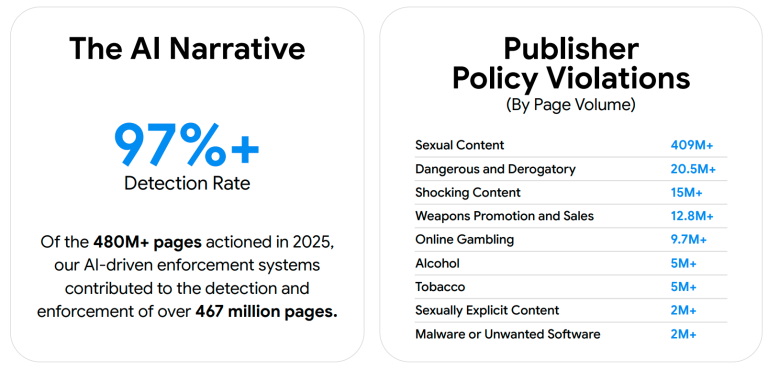
Google’s 2025 Ads Safety Report reveals how Gemini AI intercepted 99% of bad ads and reduced false account suspensions by 80%. Read the full scale of the defense.
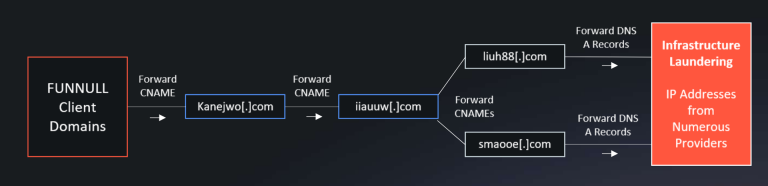
Triad Nexus has built a $300M fraud engine using "Infrastructure Laundering" on AWS and Google. See how they use geo-fencing and CNAME chains to evade the law.
Critical 9.3 RCE in OpenAM (CVE-2026-33439) allows unauthenticated attackers to execute OS commands via jato.clientSession. Patch your 16.0.5 servers now!
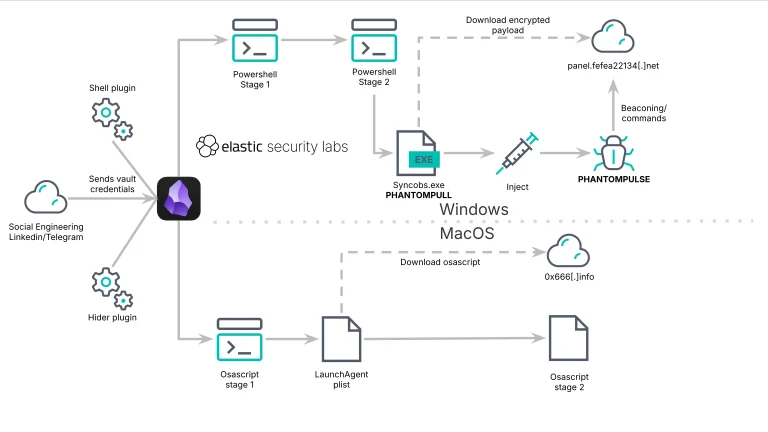
Elastic uncovers PHANTOMPULSE: A novel RAT abusing Obsidian plugins and blockchain C2. Stay safe from this AI-assisted campaign targeting crypto firms.