Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
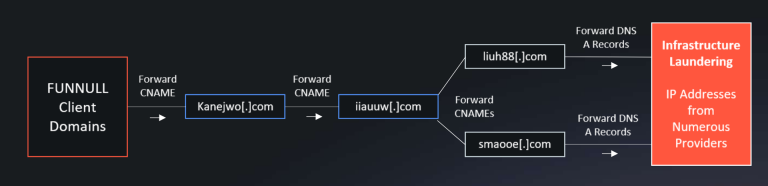
Triad Nexus’ $300M “Infrastructure Laundering” Machine Exposed Infrastructure Laundering Triad Nexus
  • Cybercriminals

Triad Nexus’ $300M “Infrastructure Laundering” Machine Exposed

Do Son April 17, 2026 0

Triad Nexus has built a $300M fraud engine using "Infrastructure Laundering" on AWS and Google. See how they use geo-fencing and CNAME chains to evade the law.
Critical Pre-Auth RCE Found in OpenAM Identity Platform OpenAM RCE CVE-2026-33439
  • Vulnerability Report

Critical Pre-Auth RCE Found in OpenAM Identity Platform

Do Son April 17, 2026 0

Critical 9.3 RCE in OpenAM (CVE-2026-33439) allows unauthenticated attackers to execute OS commands via jato.clientSession. Patch your 16.0.5 servers now!
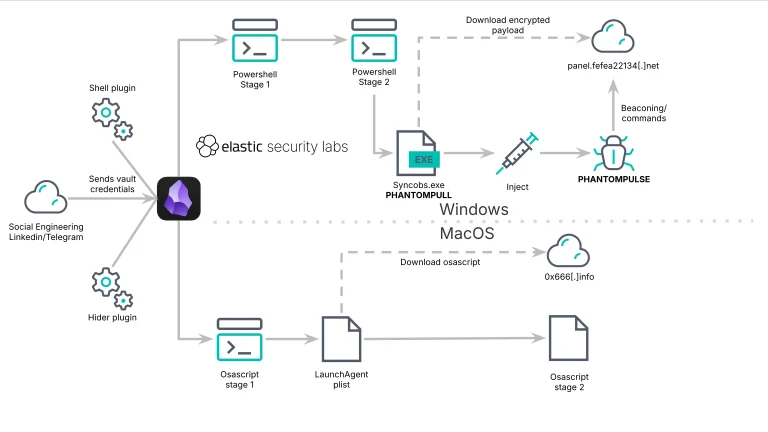
AI-Generated RAT “PHANTOMPULSE” Targets Crypto Sector via Social Engineering PHANTOMPULSE RAT Obsidian Malware Abuse
  • Malware

AI-Generated RAT “PHANTOMPULSE” Targets Crypto Sector via Social Engineering

Do Son April 17, 2026 0

Elastic uncovers PHANTOMPULSE: A novel RAT abusing Obsidian plugins and blockchain C2. Stay safe from this AI-assisted campaign targeting crypto firms.
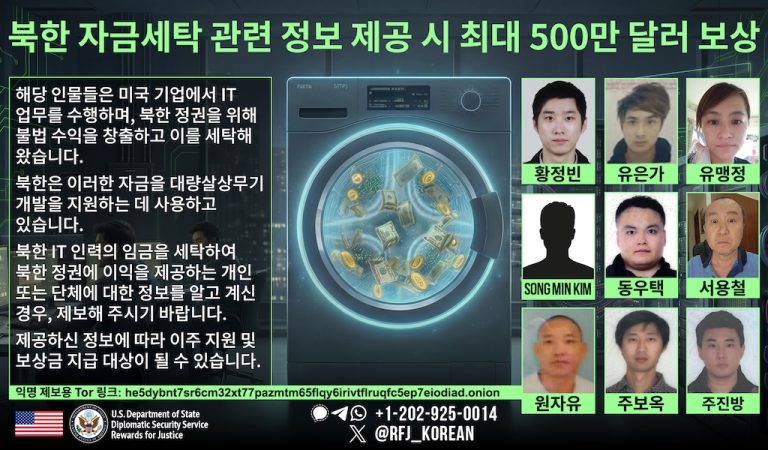
The “Laptop Farm” Fallout: Two NJ Men Sentenced for Facilitating $5M North Korean Work Scheme Laptop Farm North Korean IT Fraud
  • Cybercriminals

The “Laptop Farm” Fallout: Two NJ Men Sentenced for Facilitating $5M North Korean Work Scheme

Do Son April 17, 2026 0

Two NJ residents sentenced for running a "laptop farm" allowing North Korean workers to infiltrate 100+ U.S. companies and steal $5M in revenue.

Wormable Bugs: Microsoft April 2026 Patch Tuesday Fixes Two “Zero-Interaction” RCE Flaws Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability Report

Wormable Bugs: Microsoft April 2026 Patch Tuesday Fixes Two “Zero-Interaction” RCE Flaws

Do Son April 17, 2026 0

Microsoft’s April 2026 Patch Tuesday fixes two "wormable" CVEs (9.8 & 8.1 CVSS). Secure your network against zero-click RCE and lateral movement now.
220 Million at Risk: Critical 9.4 CVSS Remote Code Execution Hits protobuf.js protobuf.js RCE Protocol Buffers Vulnerability
  • Vulnerability Report

220 Million at Risk: Critical 9.4 CVSS Remote Code Execution Hits protobuf.js

Do Son April 17, 2026 0

A critical 9.4 CVSS vulnerability in protobuf.js puts 220 million monthly downloads at risk of RCE. Patch your Node.js and browser apps to version 8.0.1+.

High-Severity SSRF Flaw Uncovered in Angular’s Server-Side Rendering Angular hostname hijacking vulnerability Angular SSRF Origin Hijacking Angular XSS Vulnerability CVE-2026-32635 Angular i18n XSS CVE-2026-27970 Angular SSR SSRF CVE-2026-27739 Angular Vulnerability CVE-2026-22610 CVE-2025-59052 Angular security Angular XSS Bypass, SVG Injection
  • Vulnerability Report

High-Severity SSRF Flaw Uncovered in Angular’s Server-Side Rendering

Do Son April 17, 2026 0

Angular patches a critical 8.7 SSRF flaw in @angular/platform-server. Attackers can hijack SSR origins via URL normalization. Patch v19, v20, or v21 now!
CISA Adds Critical Apache ActiveMQ RCE Flaw to KEV Catalog CISA active exploit catalog known exploited vulnerabilities ActiveMQ RCE CVE-2026-34197 CISA KEV Catalog Actively Exploited Vulnerabilities CISA KEV Catalog CVE-2025-37164 GeoServer XXE, CISA KEV FortiWeb SQLi, CISA KEV Critical Vulnerabilities CVE-2024-20953
  • Vulnerability Report

CISA Adds Critical Apache ActiveMQ RCE Flaw to KEV Catalog

Do Son April 17, 2026 0

CISA adds CVE-2026-34197 to KEV. Apache ActiveMQ's Jolokia bridge flaw allows RCE via remote Spring XML loading. Remediate by April 30, 2026. Patch now!

The Invisible Patch: How PolinRider Rewrites Git History to Hide North Korean Malware PolinRider Malware Git History Falsification
  • Malware

The Invisible Patch: How PolinRider Rewrites Git History to Hide North Korean Malware

Do Son April 17, 2026 0

PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.
Critical Hardcoded Credential Bug Hits Nexus Repository 3 Nexus Repository Vulnerability Hardcoded Credentials
  • Vulnerability Report

Critical Hardcoded Credential Bug Hits Nexus Repository 3

Do Son April 16, 2026 0

Sonatype Nexus Repository (CVE-2026-5189) faces a critical 9.2 CVSS flaw. A hardcoded database credential grants full host access. Patch to v3.71.0 now!

Synology DSM Update Fixes High-Severity File Manipulation Flaws Synology Chat Server vulnerabilities Synology security update Synology DSM Update NAS Security Vulnerability Synology VPN Update SSL VPN Vulnerability Synology Telnet Flaw DSM Security Update Synology DSM Telnet vulnerability BeeStation Zero-Day, Pwn2Own RCE CVE-2024-11131 & CVE-2024-10442 CVE-2025-2848 Synology, NAS
  • Vulnerability Report

Synology DSM Update Fixes High-Severity File Manipulation Flaws

Do Son April 16, 2026 0

Synology patches critical DSM flaws (CVSS 8.0) allowing file manipulation and data leaks. Secure your NAS—upgrade to DSM 7.3, 7.2.2, or 7.2.1 immediately!

Critical 9.1 Bypass in OAuth2 Proxy Exposes Upstream Resources OAuth2 Proxy Auth Bypass CVE-2026-34457 OAuth2-Proxy, Authentication Bypass
  • Vulnerability Report

Critical 9.1 Bypass in OAuth2 Proxy Exposes Upstream Resources

Do Son April 16, 2026 0

A critical 9.1 CVSS flaw in OAuth2 Proxy allows unauthenticated users to bypass security via User-Agent spoofing. Secure your upstream apps—patch v7.15.2 today.
CVE-2026-38526: Critical CVSS 10 Vulnerability Discovered in Krayin CRM Krayin CRM RCE CVE-2026-38526
  • Vulnerability Report

CVE-2026-38526: Critical CVSS 10 Vulnerability Discovered in Krayin CRM

Do Son April 16, 2026 0

Krayin CRM faces a critical CVSS 10 RCE flaw in its TinyMCE upload endpoint. Authenticated users can seize server control. Patch version 2.2.x immediately!
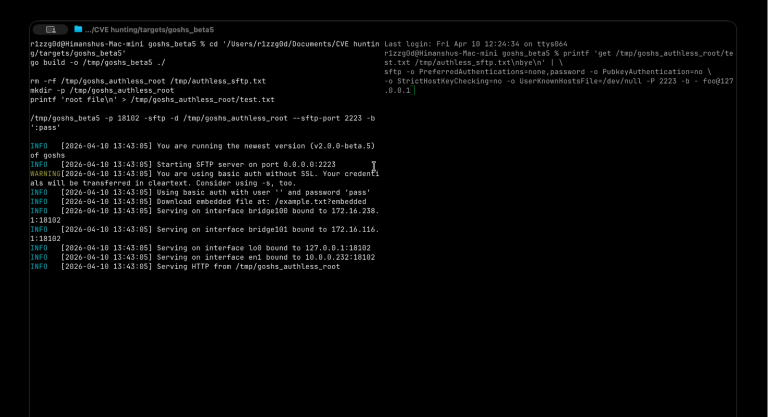
CVE-2026-40884: Critical 9.8 Bypass Hits goshs SFTP Servers goshs Authentication Bypass CVE-2026-40884
  • Vulnerability Report

CVE-2026-40884: Critical 9.8 Bypass Hits goshs SFTP Servers

Do Son April 16, 2026 0

Critical 9.8 flaw in goshs (CVE-2026-40884) allows unauthenticated SFTP access when using specific auth syntax. Secure your files—upgrade to v2.0.0-beta.6 now!

Google’s New Prepaid Credits Prevent Gemini API Key Disasters Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

Google’s New Prepaid Credits Prevent Gemini API Key Disasters

Do Son April 16, 2026 0

Google introduces Prepaid Credits and Project Spend Caps for the Gemini API. Protect your cloud account from leaked key overages and surprise billing cycles.

The New Lockdown: How Microsoft’s April 2026 Update Silos Remote Desktop to Kill Phishing Microsoft source code Windows RDP Security Update
  • Windows

The New Lockdown: How Microsoft’s April 2026 Update Silos Remote Desktop to Kill Phishing

Do Son April 16, 2026 0

Microsoft hardens RDP in the April 2026 update. Discover how new default isolation policies and security warnings stop malicious servers from stealing your data.
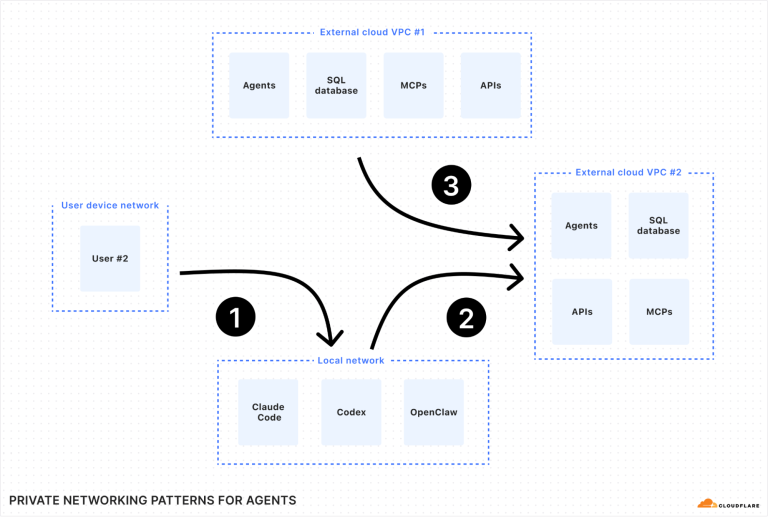
Cloudflare Mesh Challenges Tailscale with Post-Quantum Security for AI Agents Cloudflare Mesh
  • Technology

Cloudflare Mesh Challenges Tailscale with Post-Quantum Security for AI Agents

Do Son April 16, 2026 0

Cloudflare Mesh is here. Discover how this post-quantum encrypted network secures AI agents and infrastructure, offering a 50-node free tier to rival Tailscale.

Cloudflare Containers Now Feature Regional and Jurisdictional Constraints Cloudflare Containers Regional Placement Cloudflare Logs Lost
  • Technology

Cloudflare Containers Now Feature Regional and Jurisdictional Constraints

Do Son April 16, 2026 0

Cloudflare adds regional and jurisdictional constraints to Containers. Easily enforce GDPR and FedRAMP compliance by pinning data to specific global locales.
Bot Revolution: How Telegram’s New “Manager Mode” Lets AI Agents Spawn Their Own Sub-Bots Telegram Bot Manager Mode
  • Technology

Bot Revolution: How Telegram’s New “Manager Mode” Lets AI Agents Spawn Their Own Sub-Bots

Do Son April 16, 2026 0

Telegram launches Manager Mode! Now bots can create and manage sub-bots, enabling developers to deploy multi-tenant AI agent services with zero user setup.

The 17-Month Glitch: Microsoft Finally Fixes the Windows Server 2025 “Auto-Upgrade” Disaster Windows Server 2025 Accidental Upgrade Windows Server 2008 final support 2026, Premium Assurance expiration Windows Server, update bug Windows Server PPTP Vulnerability KB5051987 Hotpatching
  • Windows

The 17-Month Glitch: Microsoft Finally Fixes the Windows Server 2025 “Auto-Upgrade” Disaster

Do Son April 16, 2026 0

Microsoft resolves the bug causing Windows Server 2019/2022 to auto-upgrade to 2025. Learn about the KB5082063 fix and the 10-day rollback window.

Secure Boot & BitLocker Fixes: Everything You Need to Know About Windows 11 Update KB5083769 KB5083769 Update Windows 11 24H2 end of support File Explorer White Flash Windows 11 Dark Mode Bug Windows 11 SE, End of Support Windows Update, Automatic Upgrade CVE-2023-38146 Windows 10
  • Windows

Secure Boot & BitLocker Fixes: Everything You Need to Know About Windows 11 Update KB5083769

Do Son April 16, 2026 0

Microsoft releases KB5083769 for Windows 11, fixing BitLocker recovery loops and preparing for the critical June 2026 UEFI certificate expiration.

GitHub Abruptly Terminates All Copilot Pro Trials Amid Massive Abuse GitHub Copilot Pro trial suspension GitHub Actions Platform Fee, Self-Hosted Runner Tax 2026 GitHub Apple ID, Privacy Login GitHub Microsoft Github disruptions CVE-2025-30066 GitHub Outage, Service Disruption
  • Technology

GitHub Abruptly Terminates All Copilot Pro Trials Amid Massive Abuse

Do Son April 16, 2026 0

GitHub has suspended all Copilot Pro trials as of April 13, 2026. Learn how bad-faith exploitation forced a service-wide shutdown and what it means for you.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-86345CVSS 9.0
    A flaw was found in 389-ds-base. The server does not discard plaintext bytes already buffered from a client...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48752CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image or...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48751CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, instance snapshots ignore the `restricted.containers.lowlevel=block`...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48750CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, the `record-output` parameter of the...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48749CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image can...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48755CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.1.0, improper validation of user-provided backup...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48769CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, an arbitrary file write exists...
    📅 Updated: Nov 6, 2026
  • CVE-2026-63017CVSS 9.4
    Incorrect authorization in PowerSYSTEM Center allows a low-privileged, authenticated user to access resources normally limited to administrators.
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.