Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
OpenAI’s GPT-5.4-Cyber Challenges the “Superhuman” Hacking of Claude Mythos GPT-5.4-Cyber
  • Technology

OpenAI’s GPT-5.4-Cyber Challenges the “Superhuman” Hacking of Claude Mythos

Do Son April 16, 2026 0

OpenAI unveils GPT-5.4-Cyber to counter Anthropic’s Claude Mythos. Explore the "cyber-permissive" model that reverse-engineers malware for verified defenders.
Google I/O 2026 Unveils the Future of Autonomous Development Google I/O 2026
  • Technology

Google I/O 2026 Unveils the Future of Autonomous Development

Do Son April 16, 2026 0

Google I/O 2026 kicks off May 19! Explore the shift to agentic AI, Android 17, and autonomous developer workflows that redefine software engineering.

The Vertical AI Factory: Is NVIDIA Quietly Planning to Buy a PC Giant? NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Technology

The Vertical AI Factory: Is NVIDIA Quietly Planning to Buy a PC Giant?

Do Son April 16, 2026 0

NVIDIA denies rumors of a major PC manufacturer acquisition. Explore the strategy behind the "AI Factory" and the new N1 chips aimed at Windows on Arm.

The Price of Power: Why Claude is Now Asking for Your Government ID Anthropic Claude Lawsuit Claude Max limits, AI subscription lawsuit, Claude Pro vs Max Claude Mythos security audit Claude Identity Verification Anthropic DMCA GitHub takedown bugs Nuclear weapons Xcode, Claude AI Anthropic, Claude Sonnet 4 Claude AI, AI safety
  • Technology

The Price of Power: Why Claude is Now Asking for Your Government ID

Do Son April 16, 2026 0

Anthropic introduces mandatory identity audits for Claude users via Persona. Learn which IDs are accepted and how your biometric data is (and isn't) used.

High-Severity Use-After-Free Vulnerability Uncovered in Rsync Rsync Vulnerability Use-After-Free CVE-2022-29154 & CVE-2024-12084 CVE-2024-120845 PoC
  • Vulnerability

High-Severity Use-After-Free Vulnerability Uncovered in Rsync

Do Son April 16, 2026 0

Use-after-free flaw in Rsync versions 3.0.1–3.4.1 allows DoS and info leaks via malicious xattr traffic. Learn how a simple qsort fix secures your syncs.
VIPERTUNNEL Hijacks Python for Stealthy Ransomware Access VIPERTUNNEL Backdoor Python Persistence Tactics
  • Malware

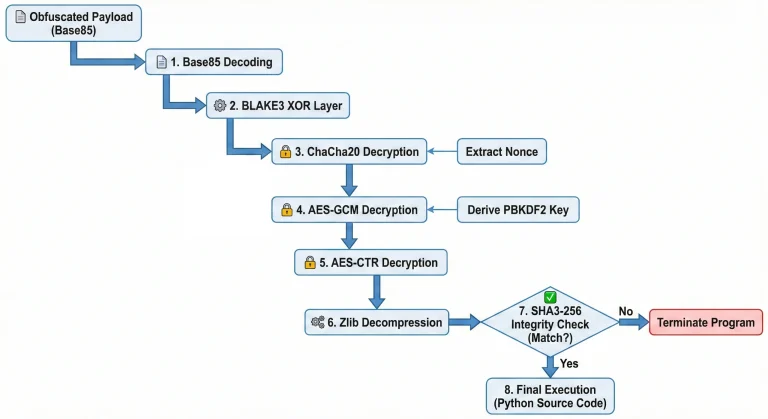
VIPERTUNNEL Hijacks Python for Stealthy Ransomware Access

Do Son April 16, 2026 0

InfoGuard unmasks VIPERTUNNEL, a Python backdoor using sitecustomize.py for stealthy persistence in DragonForce ransomware attacks. Learn how to detect it.

Sustainable Security: NIST Abandons “Analyze Everything” Goal for NVD NIST NVD Overhaul Risk-Based Triage
  • Vulnerability Report

Sustainable Security: NIST Abandons “Analyze Everything” Goal for NVD

Do Son April 16, 2026 0

Faced with a massive surge in CVEs, NIST has overhauled the NVD. Starting April 2026, only high-risk flaws get full analysis. Check the new triage rules.
The $9.5 Million Blind Spot: How a Fake Ledger App Evaded Apple’s Vetting to Empty User Wallets Fake Ledger Live App
  • Cybercriminals

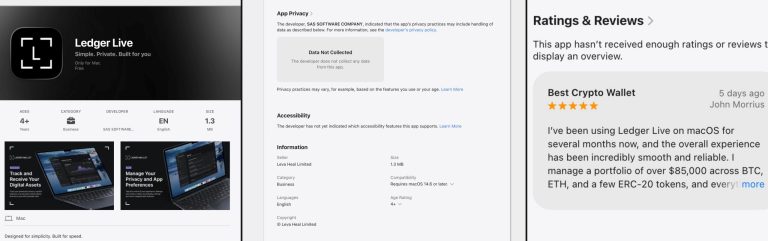
The $9.5 Million Blind Spot: How a Fake Ledger App Evaded Apple’s Vetting to Empty User Wallets

Do Son April 16, 2026 0

A malicious fake Ledger Live app on the Mac App Store has stolen $9.5M from users. Learn how the scam bypassed Apple's security and why your seed phrase is at risk.

Open Access: How a Simple Fiverr Config Error Exposed 30,000 Private Documents to Google Fiverr Data Leak Claude Code Leak Anthropic DMCA Takedown Coupang 33.7M Breach South Korea Data Leak Red Hat Breach, Customer Data Theft Farmers Insurance, Salesforce ESLint Plugin -Mamont Android banking Trojan
  • Data Leak

Open Access: How a Simple Fiverr Config Error Exposed 30,000 Private Documents to Google

Do Son April 16, 2026 0

Fiverr fails to fix a critical flaw exposing 30,000+ private PDFs, including taxpayer info, to Google Search. Learn how public Cloudinary URLs caused the leak.

Microsoft Opens “Expedited Channel” After Open-Source Developer Accounts Vanish Microsoft OpenAI $97 billion savings Microsoft Developer Account Suspension Microsoft Managed Desktop
  • Technology

Microsoft Opens “Expedited Channel” After Open-Source Developer Accounts Vanish

Do Son April 16, 2026 0

Microsoft launches a manual review channel to restore suspended developer accounts. If your driver signing is paralyzed, find out how to reclaim your access.

North Korea’s “OtterCookie” Hides Inside Benign npm Wrappers Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Data Leak

North Korea’s “OtterCookie” Hides Inside Benign npm Wrappers

Do Son April 16, 2026 0

Panther uncovers "OtterCookie," a North Korean npm campaign hiding malware in benign wrappers. It steals crypto wallets and installs SSH backdoors. Audit now!

Hardened Signals: Google’s Pixel 10 Uses Rust to Kill Modem Exploits Pixel 10 Modem Security Rust Memory Safety
  • Android

Hardened Signals: Google’s Pixel 10 Uses Rust to Kill Modem Exploits

Do Son April 16, 2026 0

Google’s Pixel 10 series is the first to use a memory-safe Rust DNS parser in its modem. Learn how this proactive shift eliminates critical cellular exploits.
The $500 Countermove: Can Microsoft’s College Bundle Stop the MacBook Neo Defection? Microsoft College Offer 2026
  • Technology

The $500 Countermove: Can Microsoft’s College Bundle Stop the MacBook Neo Defection?

Do Son April 16, 2026 0

Microsoft fights back! Buy a Windows 11 laptop and get $500 in perks, including Xbox Game Pass and Microsoft 365. Is it enough to beat the $500 MacBook Neo?
Desktop AI War: Google Launches Native Gemini for Mac with “Screen Awareness” and Video Gen Google Gemini Go app Google AI software engineering interview Google Gemini for Mac
  • Technology

Desktop AI War: Google Launches Native Gemini for Mac with “Screen Awareness” and Video Gen

Do Son April 16, 2026 0

Google releases Gemini for Mac. With Option+Space shortcuts, screen awareness, and Nano Banana 2 integration, it’s a direct challenge to Apple Intelligence.
Cisco Patches Critical CVSS 9.9 RCE Flaws in Identity Services Engine Cisco ISE Root Escalation * Read-Only Admin Exploit Cisco Secure FMC Vulnerability CVE-2026-20131 Cisco Meeting Management Vulnerability CVE-2026-20098 Cisco vulnerability, RCE flaw CVE-2025-20265 Cisco Meraki, VPN Vulnerability Cisco Nexus Dashboard - CVE-2024-20424 CVE-2025-20115 Cisco Vulnerability CVE-2018-0171 Privilege Escalation Cisco Unified Intelligence Center
  • Vulnerability Report

Cisco Patches Critical CVSS 9.9 RCE Flaws in Identity Services Engine

Do Son April 16, 2026 0

Cisco alerts on a critical 9.9 CVSS flaw in ISE. Even "Read-Only" admins can escalate to root and trigger a total network lockout. Patch immediately.
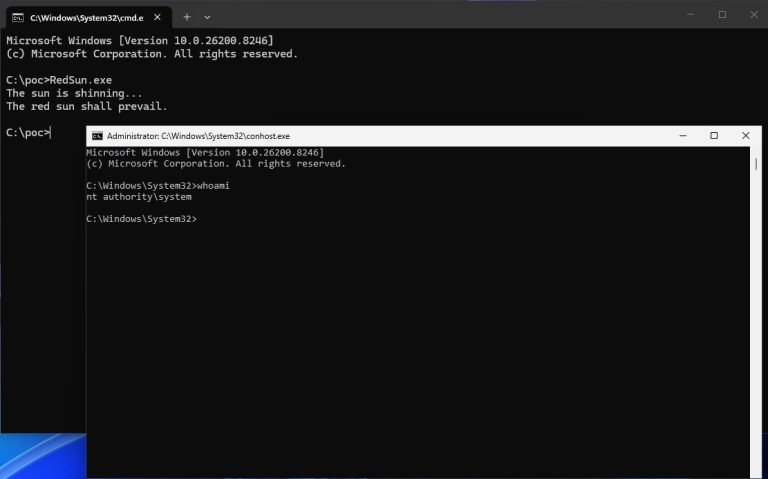
RedSun: New Windows Defender Zero-Day Turns Protector into Attacker, PoC Publishes RedSun Zero-Day Windows Defender EoP
  • Vulnerability Report

RedSun: New Windows Defender Zero-Day Turns Protector into Attacker, PoC Publishes

Do Son April 16, 2026 0

Windows Defender "RedSun" zero-day revealed! This unpatched EoP flaw turns antivirus into a delivery tool for malicious payloads. PoC is public—patch now!
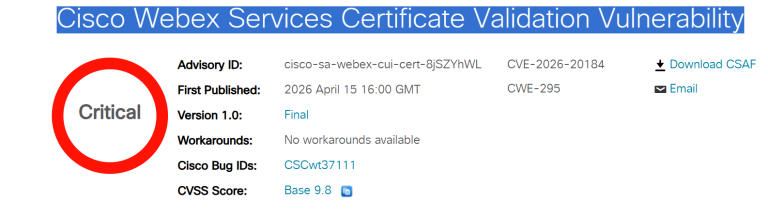
Critical 9.8 Webex Flaw Lets Attackers Impersonate Any User Cisco Webex SSO Webex Impersonation Flaw
  • Vulnerability Report

Critical 9.8 Webex Flaw Lets Attackers Impersonate Any User

Do Son April 16, 2026 0

Cisco Webex CVE-2026-20184 allows unauthenticated user impersonation via SSO flaw. Fix requires a manual certificate update in Control Hub. Act now!

Splunk Issues Urgent Fixes for RCE and Clear-Text Token Leaks Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

Splunk Issues Urgent Fixes for RCE and Clear-Text Token Leaks

Do Son April 16, 2026 0

Splunk fixes CVE-2026-20204, a critical RCE flaw where low-privilege users can hijack servers via temp files. Patch Enterprise and Cloud instances now!
Chrome 147 Update: Google Patches Critical $90,000 ANGLE Flaw and 30 Other Security Gaps Chrome Security Update $90K Bug Bounty
  • Vulnerability Report

Chrome 147 Update: Google Patches Critical $90,000 ANGLE Flaw and 30 Other Security Gaps

Do Son April 16, 2026 0

Google patches 31 Chrome flaws, including a $90K graphics engine bug. Update to version 147.0.7727.101 now to block critical sandbox escapes and RCE risks.
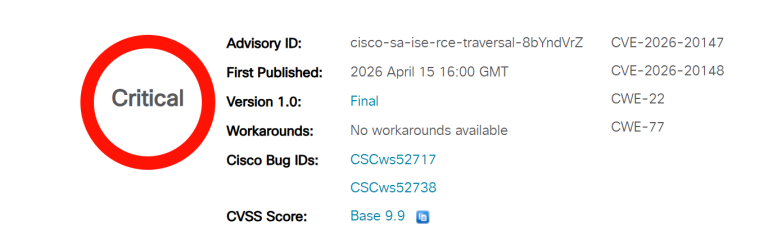
Root Access via Admin: The 9.9 RCE Crisis Threatening Cisco ISE Networks Cisco ISE RCE Identity Services Engine Vulnerability
  • Vulnerability Report

Root Access via Admin: The 9.9 RCE Crisis Threatening Cisco ISE Networks

Do Son April 16, 2026 0

Cisco warns of a critical 9.1 RCE flaw in Identity Services Engine (ISE). Attackers can escalate to root access—apply official security patches now!
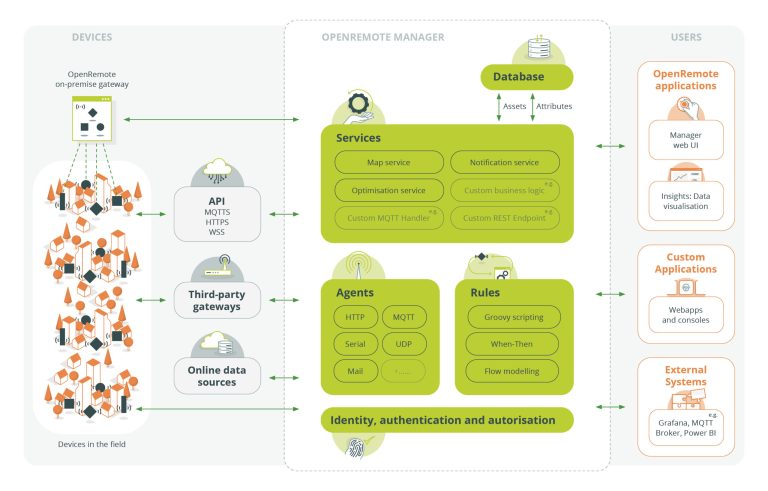
IoT Under Fire: Critical CVSS 10 Expression Injection Hits OpenRemote Platform OpenRemote RCE IoT Security
  • Vulnerability Report

IoT Under Fire: Critical CVSS 10 Expression Injection Hits OpenRemote Platform

Do Son April 15, 2026 0

OpenRemote CVE-2026-39842 is a critical CVSS 10 flaw allowing RCE via JavaScript and Groovy injection. Secure your IoT assets—upgrade to v1.22.0 now!
Critical 9.1 SQL Injection Threatens Vendure Core Stores Vendure SQL Injection Shop API Vulnerability
  • Vulnerability Report

Critical 9.1 SQL Injection Threatens Vendure Core Stores

Do Son April 15, 2026 0

Vendure Core faces a critical 9.1 SQL Injection via the Shop API. Unauthenticated attackers can hijack databases—upgrade to 3.6.2, 3.5.7, or 2.3.4 now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-86345CVSS 9.0
    A flaw was found in 389-ds-base. The server does not discard plaintext bytes already buffered from a client...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48752CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image or...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48751CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, instance snapshots ignore the `restricted.containers.lowlevel=block`...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48750CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, the `record-output` parameter of the...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48749CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image can...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48755CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.1.0, improper validation of user-provided backup...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48769CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, an arbitrary file write exists...
    📅 Updated: Nov 6, 2026
  • CVE-2026-63017CVSS 9.4
    Incorrect authorization in PowerSYSTEM Center allows a low-privileged, authenticated user to access resources normally limited to administrators.
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.