Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Ubuntu 26.10 Set to Deliver Linux Kernel 7.2 and Rapid Innovation Ubuntu 26.10 Stonking Stingray Ubuntu Security Alert: Three Ways to Bypass User Namespace Restrictions
  • Linux

Ubuntu 26.10 Set to Deliver Linux Kernel 7.2 and Rapid Innovation

Do Son April 21, 2026 0

Canonical unveils the "Stonking Stingray." Ubuntu 26.10 arrives Oct 15, 2026, featuring Linux Kernel 7.2 and GNOME 51. See the full development roadmap here.
The NTFS Resurrection: Linux Kernel 7.1 Delivers a Native Driver with 110% Faster Write Speeds CVE-2022-41850 Linux Kernel 7.1 NTFS driver
  • Linux

The NTFS Resurrection: Linux Kernel 7.1 Delivers a Native Driver with 110% Faster Write Speeds

Do Son April 21, 2026 0

Linux Kernel 7.1 introduces a ground-up NTFS driver rewrite. Experience up to 110% faster multi-threaded writes and 4x faster drive mounting in 2026.
SEO Poisoning & NativeAOT: Unmasking the “Kong RAT” Campaign Targeting IT Professionals Kong RAT SEO Poisoning
  • Malware

SEO Poisoning & NativeAOT: Unmasking the “Kong RAT” Campaign Targeting IT Professionals

Do Son April 21, 2026 0

Kong RAT: A year-long SEO poisoning campaign targeting developers with trojanized SSH/VPN tools and .NET NativeAOT stealth. Learn how to stay protected.

Meta Unveils a New Premium Tier to Personalize Your WhatsApp Experience WhatsApp Plus subscription
  • Technology

Meta Unveils a New Premium Tier to Personalize Your WhatsApp Experience

Do Son April 21, 2026 0

Meta is testing "WhatsApp Plus," a new subscription tier offering exclusive themes, 20 pinned chats, and animated stickers. See what’s changing in 2026.

The 100-Billion-Dollar Power Play: Anthropic and Amazon Forge an 8.5GW AI Empire Motorola Smart Feed redirect Anthropic Amazon 5GW partnership Amazon Perplexity lawsuit AWS-LC Vulnerabilities Cryptographic Bypass AWS Middle East drone strikes Amazon layoffs 2026, Amazon AI restructuring Amazon Kindle DRM Policy, Publisher Control EPUB AWS Nova Forge AI Model Customization AWS Trainium3 EC2 Trn3 UltraServer Route 53 Accelerated Recovery AWS DNS Resilience AI Browser War, Amazon Comet Amazon layoffs, cost reduction AWS outage, DynamoDB DNS AWS outage, cloud dependency AWS VPN Client, Root Privilege Escalation WSA shutdown, Amazon Appstore Amazon Wondery, Podcast Restructuring Amazon Q2 2025 Generative AI AWS Client VPN, Privilege Escalation Amazon AI, Wearable AI
  • Technology

The 100-Billion-Dollar Power Play: Anthropic and Amazon Forge an 8.5GW AI Empire

Do Son April 21, 2026 0

Anthropic and Amazon ink a historic $100B deal for 5GW of power. See how "Project Rainier" and Trainium chips are set to challenge the OpenAI-Microsoft throne.
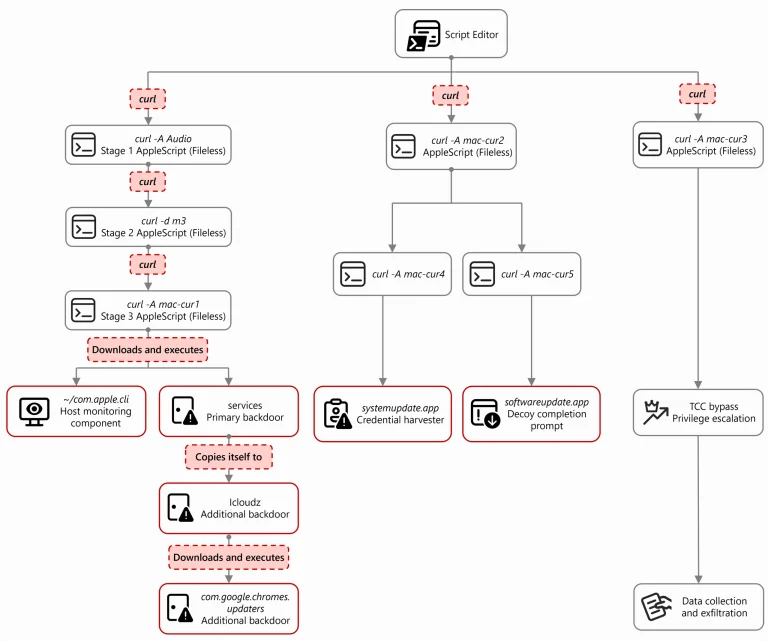
Beyond Gatekeeper: How Sapphire Sleet’s AppleScript Trap Hijacks macOS and Crypto Wallets Sapphire Sleet macOS TCC Bypass Malware
  • Malware

Beyond Gatekeeper: How Sapphire Sleet’s AppleScript Trap Hijacks macOS and Crypto Wallets

Do Son April 21, 2026 0

Microsoft uncovers Sapphire Sleet's macOS campaign. Using fake recruiters and AppleScript, they bypass TCC to steal crypto wallets, Telegram, and SSH keys.

The Negotiator Turned Traitor: Insider Betrayal in the BlackCat Ransomware Ring NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Cybercriminals

The Negotiator Turned Traitor: Insider Betrayal in the BlackCat Ransomware Ring

Do Son April 21, 2026 0

Former ransomware negotiator Angelo Martino pleaded guilty to working with BlackCat to extort his own clients. $10M in luxury assets seized. Facing 20 years.
AI Hype Hijacked: How a Fake Claude Installer Blinds Windows Security Claude AI Phishing MSIX Malware
  • Malware

AI Hype Hijacked: How a Fake Claude Installer Blinds Windows Security

Do Son April 21, 2026 0

Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.

The Price of Privacy: Atlassian to Train AI on Jira and Confluence Data Starting August 2026 CVE-2024-21687 & CVE-2024-21686 Atlassian AI data contribution
  • Data Leak

The Price of Privacy: Atlassian to Train AI on Jira and Confluence Data Starting August 2026

Do Son April 21, 2026 0

Atlassian’s new AI policy arrives Aug 17, 2026. Learn which tiers face mandatory data collection and how to protect your Jira and Confluence content.

The Ghost in the Browser: Is Claude Desktop Clandestinely Installing a Surveillance Bridge? Claude Cowork quota update Claude Desktop native messaging bridge Anthropic Opus 4.5 Claude Excel Integration
  • Data Leak

The Ghost in the Browser: Is Claude Desktop Clandestinely Installing a Surveillance Bridge?

Do Son April 21, 2026 0

Privacy expert Alexander Hanff warns that Claude Desktop installs a "native messaging bridge" without consent, potentially bypassing browser security sandboxes.

Scotland Man Pleads Guilty in Massive $8 Million Crypto-Heist and Phishing Campaign Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Cybercriminals

Scotland Man Pleads Guilty in Massive $8 Million Crypto-Heist and Phishing Campaign

Do Son April 21, 2026 0

Tyler Buchanan pleads guilty in US court for an $8M cyber heist. Discover how SMS phishing and SIM swapping bypassed 2FA to drain corporate & crypto assets.

CISA Warns of Active Exploitation in Cisco, PaperCut, and Zimbra TP-Link, CISA CVE-2023-32315 CISA KEV Catalog Active Exploitation
  • Vulnerability Report

CISA Warns of Active Exploitation in Cisco, PaperCut, and Zimbra

Do Son April 21, 2026 0

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.

Cybersecurity: How to Keep NoSQL Databases Safe tech
  • Technique

Cybersecurity: How to Keep NoSQL Databases Safe

Do Son April 21, 2026 0
Cyber attacks are increasing at an alarming rate, with organizations across the globe facing more frequent and...
Read More Read more about Cybersecurity: How to Keep NoSQL Databases Safe
Progress Kemp LoadMaster Alert: Multiple RCE and WAF Bypass Flaws Patched Kemp LoadMaster flaws command injection remote execution Kemp LoadMaster Vulnerability WAF Bypass Technique Progress WhatsUp Gold Vulnerabilities
  • Vulnerability Report

Progress Kemp LoadMaster Alert: Multiple RCE and WAF Bypass Flaws Patched

Do Son April 21, 2026 0

Progress Kemp LoadMaster reveals 5 high-severity vulnerabilities, including a WAF bypass and OS command injection. Secure your ADC with the April 2026 patch.

RondoDox Botnet Hijacks Everything from IoT to Fortnite RondoDox Botnet Nanomite Anti-Debugging
  • Malware

RondoDox Botnet Hijacks Everything from IoT to Fortnite

Do Son April 21, 2026 0

BitSight unmasks RondoDox: a modular botnet using "nanomites" to dodge debuggers while hijacking 18 architectures for Monero mining and gaming DoS attacks.

ASUSTOR Issues Critical Patch: Command Injection Vulnerability Threatens ADM Users ASUSTOR ADM Vulnerability CVE-2026-6644
  • Vulnerability Report

ASUSTOR Issues Critical Patch: Command Injection Vulnerability Threatens ADM Users

Do Son April 21, 2026 0

ASUSTOR issues an urgent fix for CVE-2026-6644, a critical 9.4 CVSS flaw in ADM's VPN client allowing full NAS takeover. Patch to ADM 5.1.3.RGL1 now.

ZionSiphon: The “Defanged” Malware Aiming for the Water Supply Energy Meter RCE CVE-2025-41709 ICS Exposure, Power Grid Security CVE-2025-1393 & CVE-2024-23943
  • Malware

ZionSiphon: The “Defanged” Malware Aiming for the Water Supply

Do Son April 21, 2026 0

Darktrace uncovers ZionSiphon, a malware strain targeting water treatment via Modbus logic. Discover the new frontier of Israel-focused industrial sabotage.

Detection as Code: The Quiet Discipline Reshaping How Large Enterprises Run Their SOCs WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Technique

Detection as Code: The Quiet Discipline Reshaping How Large Enterprises Run Their SOCs

Nikolay Milyaev April 20, 2026 0
Walk into a security operations center at almost any large enterprise in 2026 and the scene is...
Read More Read more about Detection as Code: The Quiet Discipline Reshaping How Large Enterprises Run Their SOCs
Top 10 MDR Providers for Healthcare Organizations WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Technique

Top 10 MDR Providers for Healthcare Organizations

Do Son April 20, 2026 0
Healthcare organizations face some of the highest-stakes cybersecurity risks of any industry. A successful ransomware attack, credential...
Read More Read more about Top 10 MDR Providers for Healthcare Organizations
Rclone Critical Vulnerability Alert: Public PoC Released for Administrative Auth Bypass and RCE rclone command execution execute local commands Rclone RCE CVE-2026-41176
  • Vulnerability

Rclone Critical Vulnerability Alert: Public PoC Released for Administrative Auth Bypass and RCE

Do Son April 20, 2026 0

Technical details and PoC for Rclone’s critical 9.2 CVSS vulnerabilities (CVE-2026-41176/41179) are now public. Patch to version 1.73.5 to prevent RCE.

Public PoC and Technical Details Disclosed for Apache Syncope RCE Apache Syncope RCE CVE-2025-57738
  • Vulnerability Report

Public PoC and Technical Details Disclosed for Apache Syncope RCE

Do Son April 20, 2026 0

Apache Syncope CVE-2025-57738 allows root RCE via unsandboxed Groovy. Technical details and PoC are now public. Upgrade to v3.0.14 or 4.0.2 immediately.

Critical 9.4 CVSS Flaw Leaves Dolibarr ERP Open to RCE Dolibarr RCE CVE-2026-23500
  • Vulnerability Report

Critical 9.4 CVSS Flaw Leaves Dolibarr ERP Open to RCE

Do Son April 20, 2026 0

Dolibarr ERP faces a critical 9.4 CVSS RCE flaw (CVE-2026-23500) in its PDF conversion logic. Unsanitized commands allow full system takeover. Upgrade to 23.0!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17150CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17239CVSS 9.9
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.