Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Critical Zero-Day: Unauthenticated RCE Exploited in Weaver E-cology 10.0 Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Vulnerability Report

Critical Zero-Day: Unauthenticated RCE Exploited in Weaver E-cology 10.0

Do Son April 8, 2026 0

Weaver E-cology 10.0 faces a critical 9.3 CVSS RCE (CVE-2026-22679). Unauthenticated attackers can hijack servers via a debug endpoint. Patch immediately!

Exploited in the Wild: Critical 9.3 CVSS Flaw Turns Tianxin Systems into Hacker Gateways PAN-OS Root RCE CL-STA-1132 Exploitation Tianxin RCE CVE-2021-4473 React Native Supply Chain Attack AstrOOnauta Malware Gladinet Zero-Day, LFI RCE Chain WordPress Theme, Account Takeover CVE-2024-50623 - European Space Agency cyberattack
  • Vulnerability Report

Exploited in the Wild: Critical 9.3 CVSS Flaw Turns Tianxin Systems into Hacker Gateways

Do Son April 8, 2026 0

Shadowserver warns of active exploitation of CVE-2021-4473 in Tianxin systems. This 9.3 CVSS flaw allows unauthenticated RCE. Patch your firmware immediately!

Team Cymru Mapped the Yurei Ransomware Toolkit Before It Could Strike Yurei Ransomware Open-Source Malware
  • Malware

Team Cymru Mapped the Yurei Ransomware Toolkit Before It Could Strike

Do Son April 8, 2026 0

Team Cymru unmasks Yurei ransomware, a "Stranger Things" themed operation built on open-source code. Learn how proactive telemetry mapped their toolkit.

Zero-Day Alert: Sophisticated PDF Exploit Targets Adobe Reader for Massive Data Theft Adobe Reader Zero-Day PDF Exploit
  • Vulnerability Report

Zero-Day Alert: Sophisticated PDF Exploit Targets Adobe Reader for Massive Data Theft

Do Son April 8, 2026 0

A critical Adobe Reader zero-day allows attackers to steal local files and achieve system control via malicious PDFs. Learn how the unpatched exploit works.
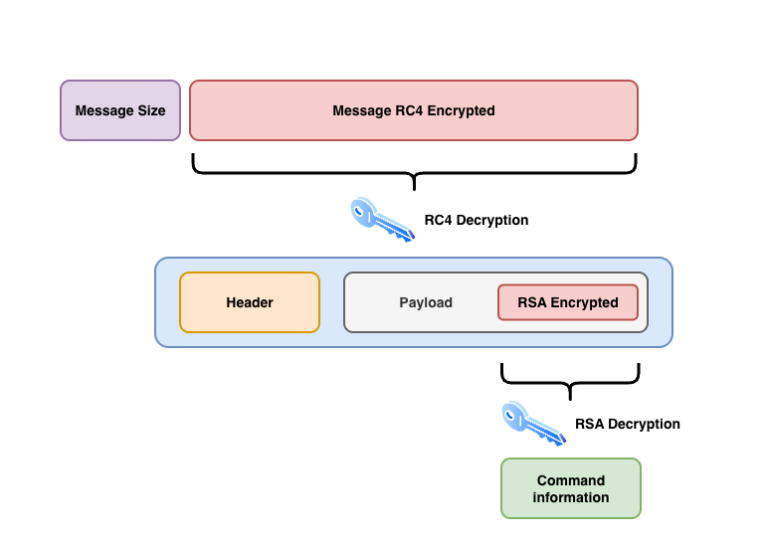
Phorpiex’s New P2P Upgrade Makes This 15-Year-Old Botnet Unstoppable Phorpiex Botnet P2P Malware Resilience
  • Malware

Phorpiex’s New P2P Upgrade Makes This 15-Year-Old Botnet Unstoppable

Do Son April 8, 2026 0

Bitsight unmasks the Phorpiex "Twizt" variant: a self-healing P2P botnet with RSA-encrypted payloads and LFI scanners. See how this 2011 threat stays relevant.
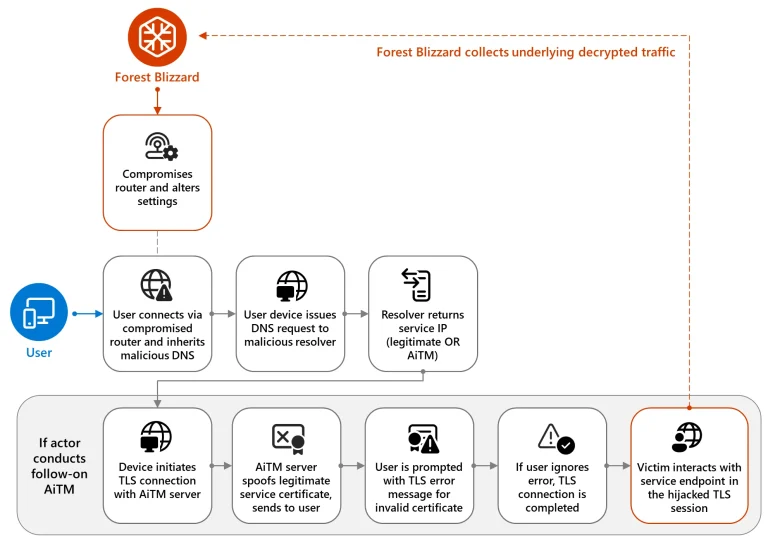
Russian Military Hackers Hijack Thousands of Home Routers for Global Espionage Forest Blizzard DNS Hijacking
  • Cybercriminals

Russian Military Hackers Hijack Thousands of Home Routers for Global Espionage

Do Son April 8, 2026 0

Microsoft exposes Forest Blizzard’s hijacking of 5,000+ SOHO routers for DNS spying and AiTM attacks on Microsoft 365 and governments. Patch your router now!

North Korean State Actors Linked to Massive $285 Million Drift Protocol Heist Drift Protocol Solana DeFi Hack
  • Cybercriminals

North Korean State Actors Linked to Massive $285 Million Drift Protocol Heist

Do Son April 8, 2026 0

Attackers drained $285M from Drift Protocol in just 12 minutes using a fake token and pre-signed transactions. Learn how the 2026 DeFi heist went down.

Critical Security Update: IBM Patches Multiple Vulnerabilities in Verify Identity and Access IBM Verify Root Escalation
  • Vulnerability Report

Critical Security Update: IBM Patches Multiple Vulnerabilities in Verify Identity and Access

Do Son April 8, 2026 0

IBM patches critical flaws in Verify Identity Access, including a 9.3 CVSS root escalation and 8.1 auth bypass. Secure your identity gateway—update now!

The Python Pivot: Kimsuky’s New Multi-Stage LNK Maze for Stealthy Backdoors Kimsuky Multi-stage LNK
  • Malware

The Python Pivot: Kimsuky’s New Multi-Stage LNK Maze for Stealthy Backdoors

Do Son April 8, 2026 0

ASEC uncovers Kimsuky’s evolved LNK-to-Python chain abusing Dropbox for stealthy persistence. Learn how to detect this complex multi-stage backdoor.

Critical Alert: Iranian-Affiliated Actors Target U.S. Infrastructure via Industrial Control Systems Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cyber Security

Critical Alert: Iranian-Affiliated Actors Target U.S. Infrastructure via Industrial Control Systems

Do Son April 8, 2026 0

FBI and CISA warn of Iranian APTs hijacking internet-facing PLCs to disrupt U.S. energy and water systems. Learn the 2026 TTPs and how to defend your OT.

The AI Collective: Telegram Unlocks Autonomous “Bot-to-Bot” Dialogue for Multi-Agent Workflows Telegram Bot-to-Bot communication
  • Technology

The AI Collective: Telegram Unlocks Autonomous “Bot-to-Bot” Dialogue for Multi-Agent Workflows

Do Son April 8, 2026 0

Telegram’s new "Bot-to-Bot" mode allows AI agents to talk to each other. Automate complex tasks by pairing "executor" and "overseer" bots in a single chat.

The “Entertainment Only” Paradox: Why Microsoft’s Copilot Legal Terms Just Ignited a Viral Controversy Microsoft Copilot Terms of Service Satya Nadella SN Scratchpad, Microsoft Microslop backlash
  • Technology

The “Entertainment Only” Paradox: Why Microsoft’s Copilot Legal Terms Just Ignited a Viral Controversy

Do Son April 8, 2026 0

Microsoft faces backlash over Copilot terms labeling the AI as "entertainment only." Discover why this legacy clause contradicts its 2026 marketing narrative.

The Cloud-Only Safety Net: Microsoft to Bypass Local Recycle Bins in Major OneDrive Overhaul OneDrive cloud deletion 2026 OneDrive Facial Recognition, Three-Time Limit OneDrive Suspension, Data Loss
  • Technology

The Cloud-Only Safety Net: Microsoft to Bypass Local Recycle Bins in Major OneDrive Overhaul

Do Son April 8, 2026 0

Starting May 2026, OneDrive cloud deletions will no longer land in your local Recycle Bin. Learn how this mandatory update changes file recovery forever.

AI Against AI: Anthropic Unveils “Project Glasswing” to Stop the Next Great Cyber War Anthropic Project Glasswing
  • Technology

AI Against AI: Anthropic Unveils “Project Glasswing” to Stop the Next Great Cyber War

Do Son April 8, 2026 0

Anthropic launches Project Glasswing, using the unreleased "Claude Mythos" model to find thousands of zero-days and defend global infrastructure from AI threats.

Alert: Social Engineering Campaign Targets Open Source Developers via Slack Social Engineering Developer Security
  • Cybercriminals

Alert: Social Engineering Campaign Targets Open Source Developers via Slack

Do Son April 8, 2026 0

Attackers are impersonating Linux leaders on Slack to drop malware via fake Google Workspace links. Protect your dev environment—verify before acting!

OpenSSL Issues Major Security Advisory: RSA and Memory Vulnerabilities Fixed OpenSSL Vulnerability RSA Memory Leak OpenSSL Vulnerability CVE-2025-15467 CVE-2022-2274 OpenSSL Vulnerabilities, Timing Side-Channel
  • Vulnerability Report

OpenSSL Issues Major Security Advisory: RSA and Memory Vulnerabilities Fixed

Do Son April 8, 2026 0

OpenSSL's April 2026 advisory reveals 7 flaws, including a moderate RSA memory leak (CVE-2026-31790). Learn if your version is affected and how to patch.

APT28 Hijacks Home Routers to Steal Corporate Credentials GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cybercriminals

APT28 Hijacks Home Routers to Steal Corporate Credentials

Do Son April 8, 2026 0

NCSC unmasks APT28’s "digital funnel" using router DNS hijacking to steal OAuth tokens and passwords. Protect your remote workforce—patch your routers now.
Venom Stealer Bypasses Chrome and “Auto-Cracks” Tonkeeper Wallets Venom Stealer Crypto Drainer MaaS
  • Malware

Venom Stealer Bypasses Chrome and “Auto-Cracks” Tonkeeper Wallets

Do Son April 8, 2026 0

Venom Stealer is a new C++ MaaS targeting crypto wallets like Tonkeeper. It features silent UAC elevation and Chrome encryption bypass. Learn how to defend.
The 1,700-Package Blitz: North Korea’s “Contagious Interview” Infiltrates Every Major Dev Registry Contagious Interview Malicious Packages
  • Malware

The 1,700-Package Blitz: North Korea’s “Contagious Interview” Infiltrates Every Major Dev Registry

Do Son April 8, 2026 0

North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.
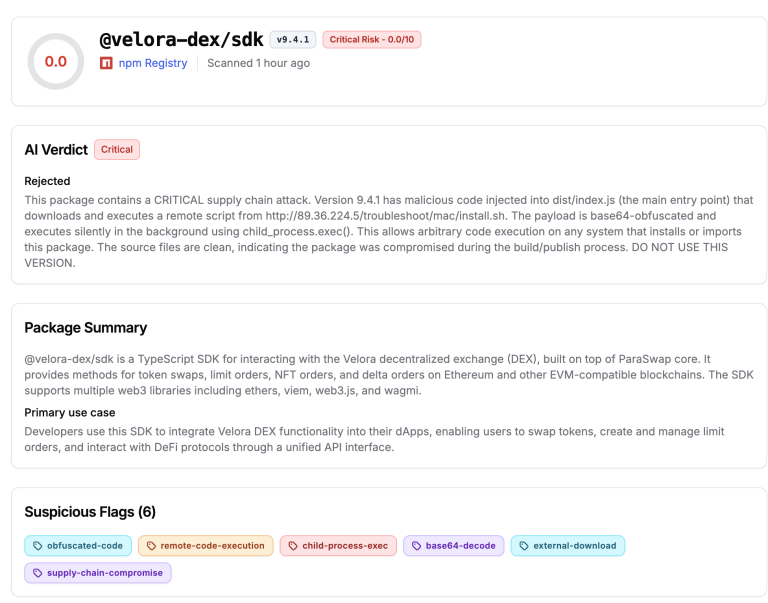
Malicious VeloraDEX SDK Compromises Developer Machines via npm npm Supply Chain Attack @velora-dex/sdk Malware
  • Malware

Malicious VeloraDEX SDK Compromises Developer Machines via npm

Do Son April 8, 2026 0

A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.
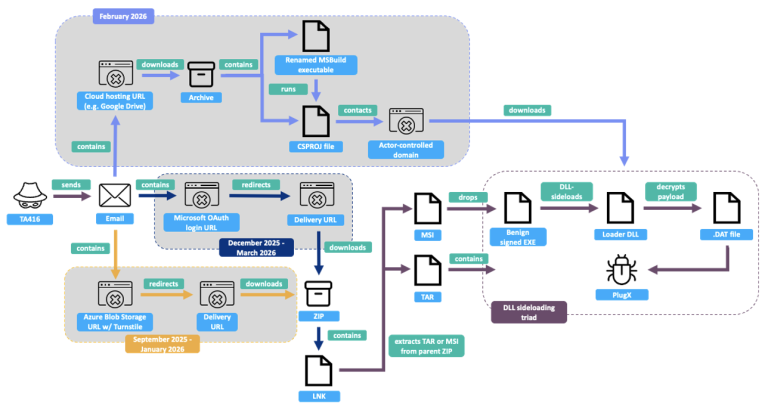
From Taiwan to Tehran: How TA416 Pivots its PlugX Backdoor to Global Flashpoints TA416 PlugX Backdoor
  • Cyber Security
  • Malware

From Taiwan to Tehran: How TA416 Pivots its PlugX Backdoor to Global Flashpoints

Do Son April 8, 2026 0

Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.
Budibase Patches Critical RCE and SSRF Vulnerabilities Budibase RCE SSRF Vulnerability Budibase Vulnerabilities Authentication Bypass
  • Vulnerability Report

Budibase Patches Critical RCE and SSRF Vulnerabilities

Do Son April 7, 2026 0

Critical 9.6 CVSS flaws in Budibase allow unauthenticated RCE and data exfiltration via SSRF. Secure your internal tools—update to v3.33.4 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-123488CVSS 9.3
    Craft CMS 4.0.0 before 4.18.9 and 5.0.0 before 5.11.2 contains an unauthenticated SQL injection vulnerability in the element...
    📅 Updated: Nov 6, 2026
  • CVE-2026-93754CVSS 9.8
    The payever – WooCommerce Gateway plugin for WordPress is vulnerable to arbitrary file upload leading to remote code...
    📅 Updated: Nov 6, 2026
  • CVE-2026-59105CVSS 9.3
    Jumis (formerly Tildes Jumis) creates and uses a Microsoft SQL Server login named ##Tilde_JumisAdmin## whose password is derived...
    📅 Updated: Nov 6, 2026
  • CVE-2026-118636CVSS 9.8
    **UNSUPPORTED WHEN ASSIGNED**  JavaNativeMessageDecoder in the MINA 3.0 codec module calls ObjectInputStream.readObject() on frame bytes with no class...
    📅 Updated: Nov 6, 2026
  • CVE-2026-19256CVSS 9.8
    The All In One Login WordPress plugin before 2.5.0 does not adequately restrict the number of attempts that...
    📅 Updated: Nov 6, 2026
  • CVE-2026-115230CVSS 9.8
    The WHIZZ WordPress plugin through 1.1.8 does not validate the password-reset key before updating a user's password, relying...
    📅 Updated: Nov 6, 2026
  • CVE-2026-110955CVSS 9.8
    The Wurdey WordPress plugin through 1.0.0 does not verify a request signature before logging a user in, allowing...
    📅 Updated: Nov 6, 2026
  • CVE-2026-113584CVSS 9.8
    The placester WordPress plugin through 1.4.3 does not perform any capability, nonce or ownership check on an AJAX...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.