Skip to content
November 5, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
The App Store of Agents: Apple to Launch Standalone Siri App and “AI Extensions” in iOS 27 iOS 27 Apple Intelligence Apple AI Extensions bazaar Siri iOS 27 Gemini integration Apple AI server Baltra Siri AI delay iOS 26.4 Apple Google Gemini Siri partnership, Siri powered by Google Gemini 2026 Siri Gemini, Apple Intelligence Siri, Apple AI Apple "Veritas", Siri AI Siri Gemini Supercharged Siri, AI assistant Siri Integration, App Intents Apple Siri Apple AI Strategy, ChatGPT Rival
  • Technology

The App Store of Agents: Apple to Launch Standalone Siri App and “AI Extensions” in iOS 27

Do Son March 30, 2026 0

Apple’s iOS 27 will debut a standalone Siri app and an "AI Extensions" bazaar. Turn Siri into the ultimate gateway for ChatGPT, Gemini, and Claude in 2026.
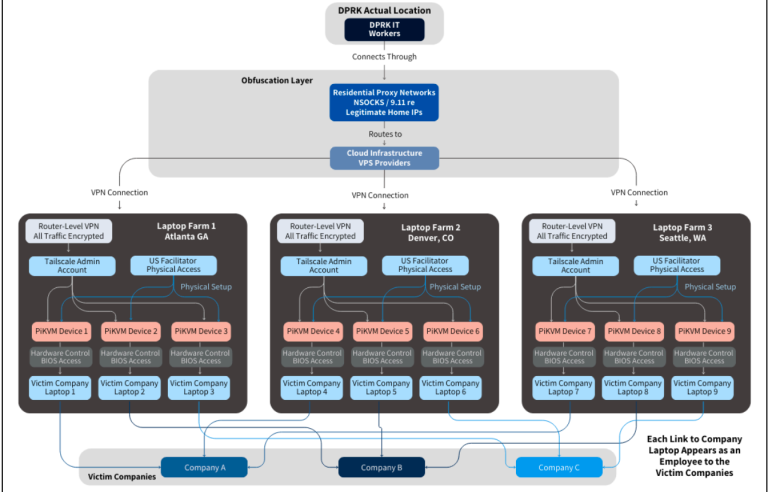
Infiltrating the Infiltrators: Inside the Florida “Laptop Farm” and the DPRK’s Failed Strike on a Cyber Firm Conceptual network diagram of DPRK scam
  • Cybercriminals

Infiltrating the Infiltrators: Inside the Florida “Laptop Farm” and the DPRK’s Failed Strike on a Cyber Firm

Do Son March 30, 2026 0

Nisos exposes a North Korean IT worker scheme involving a Florida-based laptop farm, AI-generated resumes, and PiKVM devices. Don't fall for the ruse.
The Spider’s Web: How Iranian Hackers Compromised FBI Director Kash Patel’s Personal Gmail Kash Patel email hack
  • Data Leak

The Spider’s Web: How Iranian Hackers Compromised FBI Director Kash Patel’s Personal Gmail

Do Son March 30, 2026 0

FBI Director Kash Patel’s personal Gmail was breached by the Iran-linked Handala Hack Team. Discover how "SpiderKash" footprints led to a major OSINT leak.

The Vibe Coding Invasion: Why Your AI-Built App is Stuck in Apple’s “Review Purgatory” Vibe Coding apps Vibe Coding App Store surge Vibe Coding App Store Apple 50th Anniversary hardware Brazil CADE Apple settlement, iOS third-party app stores Brazil Tim Cook Succession Apple CEO Rumors App Store Mini Apps 15% Commission Fee iOS Japan Sideloading, Third-Party App Stores Web App Store, App Discovery Apple Age Verification, Texas SB2420 Apple AI acquisitions App Store, Antitrust Apple WebKit, Japan Regulations App Store Age Ratings, Parental Controls Apple App Store, Epic Games Lawsuit
  • Technology

The Vibe Coding Invasion: Why Your AI-Built App is Stuck in Apple’s “Review Purgatory”

Do Son March 30, 2026 0

"Vibe Coding" has flooded the App Store with AI-generated apps. Discover why Apple’s review process is facing an existential crisis and longer wait times in 2026.

The Quantum Apocalypse 2029: Why Google is Rushing to Build an “Unholy Fortress” for Android Google Q-Day 2029
  • Android
  • Technology

The Quantum Apocalypse 2029: Why Google is Rushing to Build an “Unholy Fortress” for Android

Do Son March 30, 2026 0

Google has moved "Q-Day" to 2029. Discover the radical Android 17 roadmap to implement Post-Quantum Cryptography (PQC) and stop the Quantum Apocalypse.

Meta’s $27 Billion AI Gamble: Funding Seven Power Stations to Fuel Its Louisiana “Data Citadel” Instagram account recovery flaw Meta incident notification Meta AI data center Louisiana Meta AI news partnerships Meta AI Shopping Assistant Meta Vibes standalone app Meta Oversight Board account ban, Instagram permanent suspension review Meta Compute initiative 2026, personal superintelligence nuclear power Meta AI News Licensing Publisher Content Deal Meta Project Mercury Omnilingual ASR 1600 Languages Meta $600B Investment, AI Data Centers Meta AI strategy, Llama models Meta AI Glasses, Smart Glasses
  • Technology

Meta’s $27 Billion AI Gamble: Funding Seven Power Stations to Fuel Its Louisiana “Data Citadel”

Do Son March 30, 2026 0

Meta is bankrolling seven natural gas plants and 240 miles of transmission lines for its $27B Louisiana AI center. Is this true CSR or a regulatory shield?
The Stealth Skimmer: How Hackers Weaponized WebRTC to Bypass PCI Security and Siphon Credit Cards WebRTC Web Skimming
  • Vulnerability Report

The Stealth Skimmer: How Hackers Weaponized WebRTC to Bypass PCI Security and Siphon Credit Cards

Do Son March 30, 2026 0

A 2026 "technological ascension" in web skimming uses WebRTC to steal credit cards via UDP, bypassing CSP and WAF. Five global billion-dollar firms hit.

The Great iOS Update: Dual Accounts, AI Magic, and Storage Surgery Finally Hit WhatsApp for iPhone WhatsApp iPhone dual account 2026
  • Technology

The Great iOS Update: Dual Accounts, AI Magic, and Storage Surgery Finally Hit WhatsApp for iPhone

Do Son March 30, 2026 0

WhatsApp for iPhone finally adds "Dual Account" support! Discover the 2026 update featuring Meta AI image editing, easy migration, and smart storage tools.

No More Starting Over: How to Move Your ChatGPT and Claude “Memories” to Google Gemini Google Gemini Memory Import
  • Technology

No More Starting Over: How to Move Your ChatGPT and Claude “Memories” to Google Gemini

Do Son March 30, 2026 0

Google's new Gemini migration tool lets you import ChatGPT and Claude memories and ZIP chat histories. Switch AI assistants in 2026 without losing your data!

The “Headless” Revolution: How Google’s AAOS SDV is Rewiring the Brain of the Modern Car Google AAOS SDV platform
  • Android

The “Headless” Revolution: How Google’s AAOS SDV is Rewiring the Brain of the Modern Car

Do Son March 30, 2026 0

Google unveils AAOS SDV: a "headless" Android OS for Software-Defined Vehicles. Discover how it will power everything from climate control to digital twins.
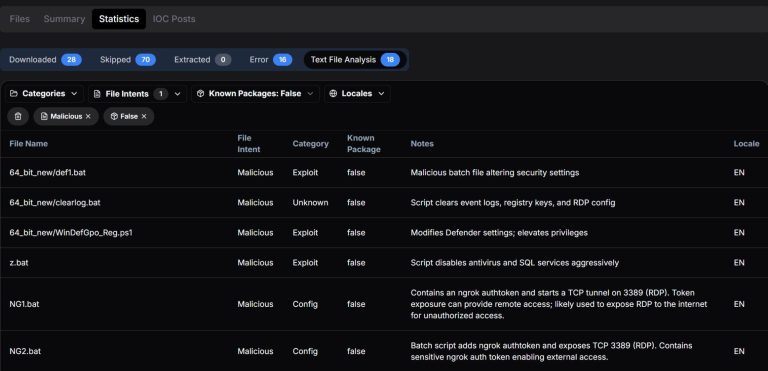
The “Gentlemen” Ransomware Toolkit and the Lethal z1.bat Pre-Encryption Weapon TheGentlemen Ransomware z1.bat script
  • Malware

The “Gentlemen” Ransomware Toolkit and the Lethal z1.bat Pre-Encryption Weapon

Do Son March 30, 2026 0

Hunt.io uncovers a Gentlemen ransomware toolkit on a bulletproof host. Learn how the z1.bat script destroys defenses and backups before encryption.

The CVE Watchtower: Weekly Threat Intelligence Briefing (March 23 – March 29, 2026) Vulnerability Triage CISA KEV List
  • Weekly Recap

The CVE Watchtower: Weekly Threat Intelligence Briefing (March 23 – March 29, 2026)

Do Son March 30, 2026 0

1,740 new vulnerabilities, 147 critical. From F5 crashes to a Trivy supply chain attack, here’s your high-priority triage list for March 2026.
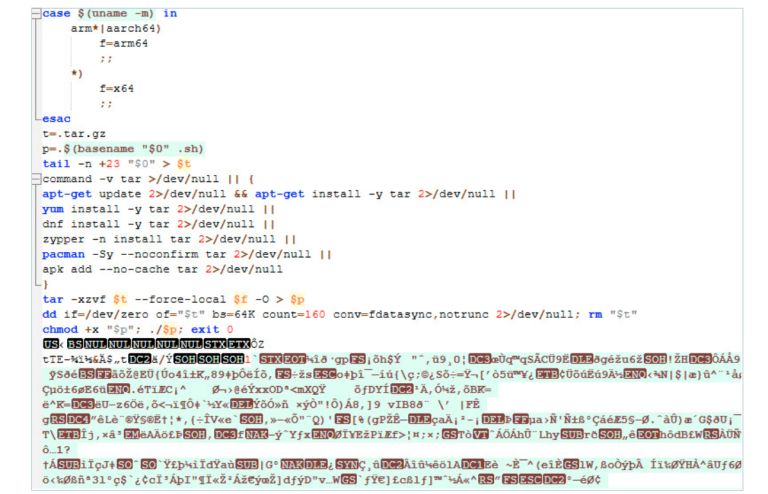
Pay2Key’s New Linux Ransomware Strips Server Defenses to Hijack x64 and ARM64 Infrastructure Pay2Key Linux Ransomware Linux Server Security
  • Malware

Pay2Key’s New Linux Ransomware Strips Server Defenses to Hijack x64 and ARM64 Infrastructure

Do Son March 30, 2026 0

Morphisec uncovers Pay2Key’s Linux evolution. This dual-arch ransomware disables SELinux and AppArmor to encrypt x64/ARM64 servers. Secure your infra today!

Unmasking the PhantomVAI Framework’s Fileless Assault on Corporate Defenses SonicWall Reconnaissance Akira Ransomware residential proxy malware TraderTraitor BreachForums Honeypot, French Interior Ministry Leak
  • Malware

Unmasking the PhantomVAI Framework’s Fileless Assault on Corporate Defenses

Do Son March 30, 2026 0

LevelBlue SpiderLabs unmasks the PhantomVAI framework: a multi-stage, fileless attack hiding XWorm and Remcos RAT inside obfuscated VBS and PNG files.

SQL to SSH: Critical 9.1 CVSS RCE in Grafana Turns Monitoring into a Remote Hijack CVE-2022-29170 Grafana RCE SQL Expressions Flaw
  • Vulnerability Report

SQL to SSH: Critical 9.1 CVSS RCE in Grafana Turns Monitoring into a Remote Hijack

Do Son March 29, 2026 0

Grafana patches a critical 9.1 RCE (CVE-2026-27876) in SQL expressions that allows SSH hijacking. Update to 12.4.2 now to secure your monitoring host.

Inside the AI-Driven “Lure Factory” Flooding GitHub with Trojans AI-Generated Malware GitHub Trojan Campaign
  • Malware

Inside the AI-Driven “Lure Factory” Flooding GitHub with Trojans

Do Son March 29, 2026 0

Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.

Tax Audits and WhatsApp Clones: How “Silver Fox” is Redefining Cyber-Espionage in South Asia WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

Tax Audits and WhatsApp Clones: How “Silver Fox” is Redefining Cyber-Espionage in South Asia

Do Son March 29, 2026 0

Sekoia TDR reveals Silver Fox's latest tactics. From tax-themed phishing to WhatsApp clones, this China-based group combines espionage with financial theft.
CISA Issues Three-Days Patch Mandate for Critical 9.8 F5 BIG-IP RCE State-Sponsored Exploitation CISA KEV Catalog F5 BIG-IP RCE CISA KEV Catalog SolarWinds WHD Exploit CVE-2025-40551 Zimbra XSS Zero-Day CVE-2025-27915 Exploited Windows Security Vulnerabilities
  • Vulnerability Report

CISA Issues Three-Days Patch Mandate for Critical 9.8 F5 BIG-IP RCE

Do Son March 29, 2026 0

CISA adds F5 BIG-IP RCE (CVE-2025-53521) to its KEV Catalog. With a 9.8 CVSS score and active exploits, federal agencies must patch by March 30, 2026.

Critical 9.4 CVSS RCE Flaws in n8n Turn Workflows into Backdoors n8n RCE Automation Security n8n Vulnerability Prototype Pollution RCE
  • Vulnerability Report

Critical 9.4 CVSS RCE Flaws in n8n Turn Workflows into Backdoors

Do Son March 27, 2026 0

n8n patches critical 9.4 CVSS RCE flaws in Merge and GSuiteAdmin nodes. Attackers can hijack servers via SQL sandbox escapes or prototype pollution. Update now!

Critical 9.8 CVSS Flaw in Pharos Mosaic Controllers Grants Root Access to Unauthenticated Attackers shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Critical 9.8 CVSS Flaw in Pharos Mosaic Controllers Grants Root Access to Unauthenticated Attackers

Do Son March 27, 2026 0

CISA warns of a 9.8 CVSS flaw in Pharos Mosaic Show Controllers (CVE-2026-2417). Unauthenticated attackers can gain root access. Update to version 2.16 now.
RedLine Infostealer Kingpin Extradited to U.S. to Face Federal Charges RedLine Infostealer Operation Magnus
  • Cybercriminals

RedLine Infostealer Kingpin Extradited to U.S. to Face Federal Charges

Do Son March 27, 2026 0

RedLine architect Hambardzum Minasyan is extradited to the U.S. to face 50 years in prison for his role in the global malware empire and Operation Magnus.

Critical 9.3 CVSS Auth Bypass and XSS Flaws Hit MantisBT MantisBT Vulnerability Authentication Bypass
  • Vulnerability Report

Critical 9.3 CVSS Auth Bypass and XSS Flaws Hit MantisBT

Do Son March 27, 2026 0

MantisBT patches a critical 9.3 CVSS auth bypass (CVE-2026-30849) and high-severity XSS flaws. Learn how MySQL type conversion opens the door. Update now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-121241CVSS 9.6
    Use after free in Navigation in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121249CVSS 9.6
    Buffer overflow in ANGLE in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to execute arbitrary code...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121257CVSS 9.6
    Use after free in TabStrip in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to potentially execute...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121234CVSS 9.6
    Privilege elevation in Contacts in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121202CVSS 9.6
    Use after free in Autofill in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121214CVSS 9.6
    Use after free in Passwords in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to potentially execute...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121189CVSS 9.6
    Use after free in Browser in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to execute arbitrary...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121200CVSS 9.6
    Incorrect reference resolution in DevTools in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 5, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.