
 Do Son
Google is ending direct APK sideloading. By 2027, all Android apps must be cryptographically signed or face a mandatory 24-hour waiting period for installation.

Google Drive's AI now detects 14x more ransomware. Learn how to use the new "infallible temporal anchor" for one-click file restoration in March 2026.

GitHub Copilot was caught secretly injecting ads for Raycast and Microsoft Teams into 11,000+ PRs. See how they hid the code and why developers are furious.
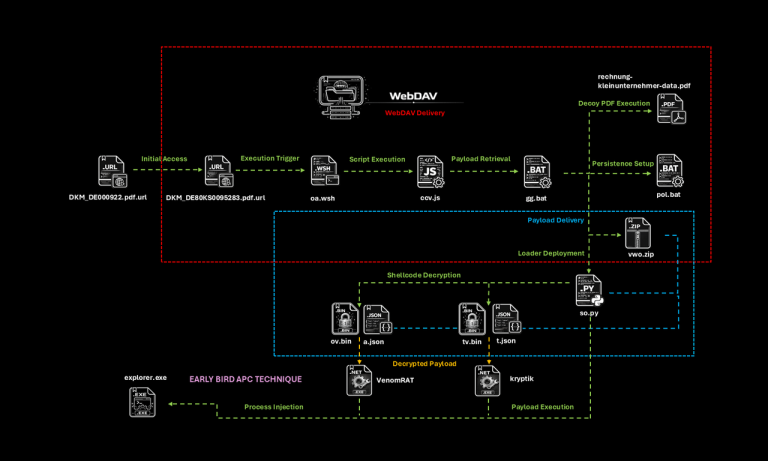
G DATA analysts chat with a malware author via Notepad while analyzing "Kiss Loader," a new threat using Early Bird APC injection and VenomRAT. Read more!

Unity is officially dismantling its $4.4B ironSource acquisition. By April 30, 2026, the network will shut down as Unity pivots to its new Vector architecture.
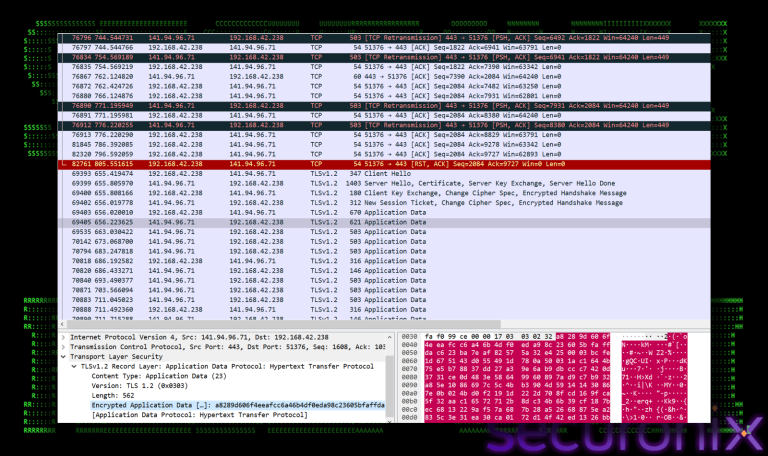
Securonix uncovers FAUX#ELEVATE, a 25-second attack using 10MB "inflated" VBScripts to steal credentials and mine crypto in French corporate environments.

Axios versions 1.14.1 & 0.30.4 have been poisoned. A hijacked maintainer account is dropping a RAT via postinstall scripts. Revert to safe versions now!
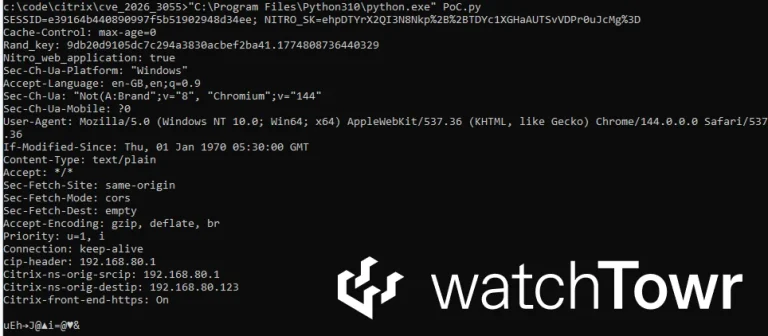
CISA adds Citrix NetScaler CVE-2026-3055 to KEV. This 9.3 CVSS flaw "bleeds" admin sessions via SAML. Federal agencies must patch by April 2, 2026.
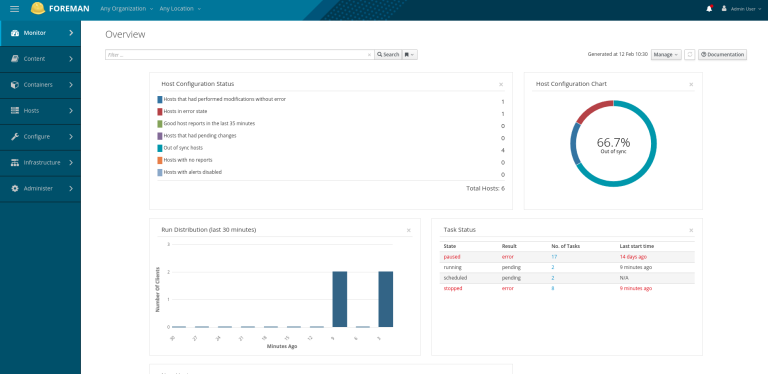
Foreman patches a critical 8.0 CVSS command injection flaw (CVE-2026-1961). Malicious hostnames can trigger RCE via WebSocket proxies. Update to 3.18.1 now!
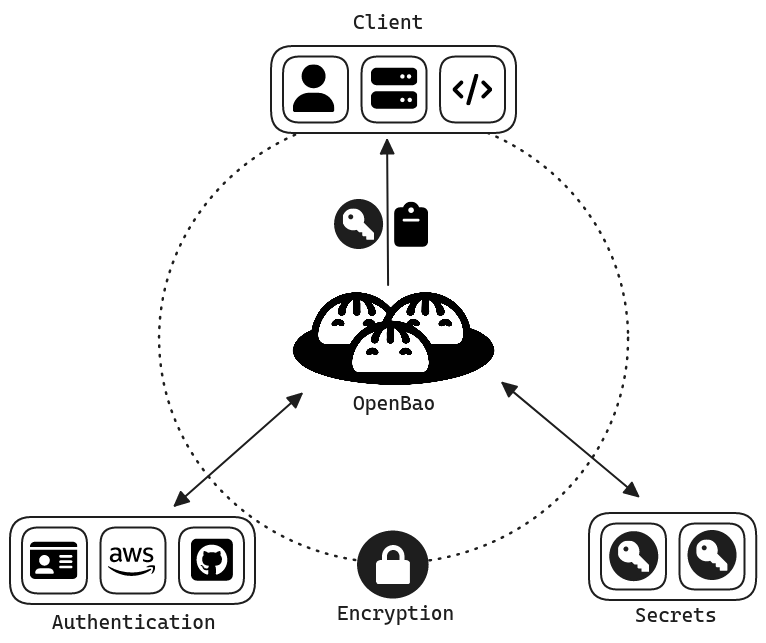
OpenBao patches critical 9.6 and 9.4 CVSS flaws in OIDC flows. Learn how "direct mode" enables session hijacking and XSS token theft. Update to 2.5.2 now.
Node-convict (CVE-2026-33864) faces a 9.4 CVSS Prototype Pollution flaw. Bypass filters and hijack Node.js apps. Update to version 6.2.5 now to stay secure.
OpenTelemetry patches a critical 9.3 RCE flaw (CVE-2026-33701) in its Java agent. Unfiltered RMI deserialization allows full system takeover. Update to 2.26.1.

Researchers reveal critical RCE and ARM-specific flaws in libpng (CVE-2026-33636 & 33416). Affecting decades of apps, these bugs require an immediate update.
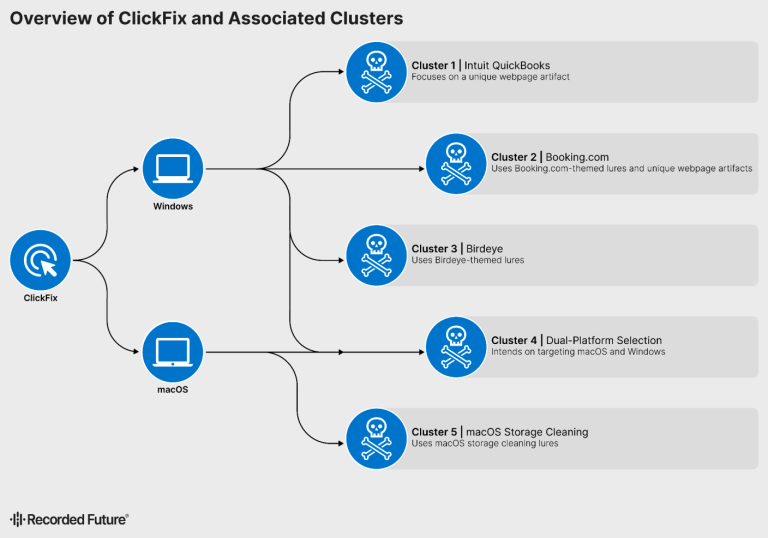
ClickFix has evolved into a high-ROI malware template used by APT28. Learn how this social engineering trick bypasses security by mimicking system errors.

The European Commission confirms a cyber-attack on its Europa.eu cloud platform. Data was stolen, but core administrative systems remain untouched.
Vim patches a critical 8.2 CVSS bug chain in modelines and tabpanels. Opening a malicious file triggers instant RCE. Update to 9.2.0272 now to stay safe.
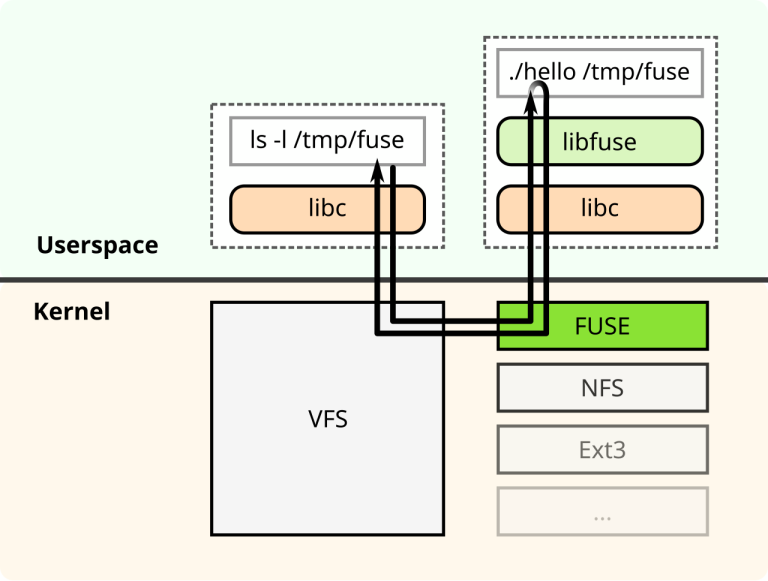
Researchers uncover two flaws in libfuse's io_uring transport (CVE-2026-33150 & 33179). Impacting Kubernetes CSI drivers, these bugs allow RCE and DoS. Patch now!

Linux legend Greg Kroah-Hartman reveals how AI is catching bugs in the kernel. Discover why 40 out of 60 AI fixes were "genuinely efficacious" in 2026.

Microsoft pulled the KB5079391 update for Windows 11 just two hours after release. Learn about the 0x80073712 error loop and how to protect your system.
Scriban’s 9.1 CVSS flaw allows sandbox escapes in .NET apps via a cache bypass. Over 40M downloads affected. Update to version 7.0.0 to secure your templates.

Apple’s iOS 27 will debut a standalone Siri app and an "AI Extensions" bazaar. Turn Siri into the ultimate gateway for ChatGPT, Gemini, and Claude in 2026.