Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
NVIDIA Patches Critical RCE and DoS Flaws Across ML Frameworks NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Vulnerability Report

NVIDIA Patches Critical RCE and DoS Flaws Across ML Frameworks

Do Son March 26, 2026 0

NVIDIA issues critical updates for Megatron-LM, Triton, and NeMo to fix RCE and DoS flaws. Upgrade now to secure your AI development and inference servers.

Public Flaws in Cisco IOx Allow Unauthenticated Log Injection and Admin XSS Cisco IOx Log Manipulation Cisco Small Business - CVE-2024-20393 and CVE-2024-20470
  • Vulnerability Report

Public Flaws in Cisco IOx Allow Unauthenticated Log Injection and Admin XSS

Do Son March 26, 2026 0

Cisco alerts of public flaws in IOx app hosting. Unauthenticated actors can manipulate logs (CVE-2026-20113), plus a stored XSS risk (CVE-2026-20112). Patch now!

The Backup Backdoor: How a Simple File Edit Grants Full SYSTEM Control in IDrive for Windows IDrive Vulnerability Privilege Escalation
  • Vulnerability Report

The Backup Backdoor: How a Simple File Edit Grants Full SYSTEM Control in IDrive for Windows

Do Son March 26, 2026 0

A critical flaw in IDrive for Windows (CVE-2026-1995) allows low-privilege users to seize SYSTEM control via weak folder permissions. Audit your PC today.

F5 Out-of-Band Security Alert: Multiple Vulnerabilities Unveiled in NGINX Plus and Open Source NGINX heap buffer overflow vulnerability NGINX Vulnerability Buffer Overflow CVE-2024-24989, CVE-2024-24990 NGINX ACME
  • Vulnerability Report

F5 Out-of-Band Security Alert: Multiple Vulnerabilities Unveiled in NGINX Plus and Open Source

Do Son March 25, 2026 0

F5 warns of high-severity flaws in NGINX Plus and Open Source (CVSS 8.8). Fixes for DAV and MP4 buffer overflows are now available. Update your servers today!
Node.js Issues Security Updates: High-Severity DoS and Permission Bypasses Patched CVE-2024-21892 Node.js Security Update Server Crash Vulnerability
  • Vulnerability Report

Node.js Issues Security Updates: High-Severity DoS and Permission Bypasses Patched

Do Son March 25, 2026 0

Node.js releases critical updates for 20.x to 25.x, fixing high-severity flaws like the __proto__ header crash and TLS errors. Update to v25.8.2 now.

Squid Caching Proxy Alert: Critical ICP Protocol Flaws Threaten Web Infrastructure CVE-2024-25617 CVE-2025-59362 Squid Proxy ICP Vulnerability
  • Vulnerability Report

Squid Caching Proxy Alert: Critical ICP Protocol Flaws Threaten Web Infrastructure

Do Son March 25, 2026 0

Squid Proxy patches critical 9.2 CVSS DoS and memory leak flaws in ICP. Standard access rules won't block the attack—upgrade to version 7.5 now.

GitLab Critical Alert: High-Severity Flaws Allow App Impersonation and AI Token Leaks GitLab Security Update Account Impersonation GitLab Security Update CVE-2026-1090 GitLab vulnerability GitLab vulnerability, GitLab patches
  • Vulnerability Report

GitLab Critical Alert: High-Severity Flaws Allow App Impersonation and AI Token Leaks

Do Son March 25, 2026 0
GitLab has released a critical security advisory alongside versions 18.10.1, 18.9.3, and 18.8.7 for its Community (CE)...
Read More Read more about GitLab Critical Alert: High-Severity Flaws Allow App Impersonation and AI Token Leaks
AI Infrastructure at Risk: NVIDIA Fixes Critical 9.0 RCE Flaw in Apex Library (CVE-2025-33244) NVIDIA GPU Security CUDA-Q Vulnerability NVIDIA Apex Vulnerability AI Infrastructure Security NVIDIA Cumulus Linux CVE-2025-33179 NVIDIA Arm divestment NVIDIA DGX Spark, CVE-2025-33187 NVIDIA Isaac-GROOT, Code Injection Megatron-LM Vulnerability, AI Code Injection NVIDIA China NVIDIA GPUs, Hardware Kill Switches NVIDIA Megatron-LM, LLM Vulnerabilities NVIDIA Base Command Manager - CVE-2024-0138
  • Vulnerability Report

AI Infrastructure at Risk: NVIDIA Fixes Critical 9.0 RCE Flaw in Apex Library (CVE-2025-33244)

Do Son March 25, 2026 0

NVIDIA patches a critical 9.0 CVSS vulnerability (CVE-2025-33244) in the Apex library. Protect your AI models from RCE—upgrade to PyTorch 2.6+ now.

2026 Cybersecurity Excellence Awards Winners Announced during RSA Conference as AI Security Dominates PR-image_1774418653gzG1LV4yJZ
  • Press Release

2026 Cybersecurity Excellence Awards Winners Announced during RSA Conference as AI Security Dominates

cybernewswire March 25, 2026 0
San Francisco, USA, 25th March 2026, CyberNewswire
Read More Read more about 2026 Cybersecurity Excellence Awards Winners Announced during RSA Conference as AI Security Dominates
Project 20/20: Microsoft’s Radical Plan to Cure Windows 11’s “Memory Hunger” Windows 11 Project 20/20
  • Windows

Project 20/20: Microsoft’s Radical Plan to Cure Windows 11’s “Memory Hunger”

Do Son March 25, 2026 0

Microsoft resurrects "Project 20/20" to cut Windows 11 memory and storage by 20%. Discover the 2026 plan to ditch WebView2 for a faster, leaner WinUI 3 system.
Critical 9.4 CVSS Flaw Exposes Harbor Registries to Total Hijack Harbor Registry Supply Chain Attack
  • Vulnerability Report

Critical 9.4 CVSS Flaw Exposes Harbor Registries to Total Hijack

Do Son March 25, 2026 0

GoHarbor's Harbor faces a critical 9.4 CVSS flaw (CVE-2026-4404). Default admin passwords allow total registry compromise and image poisoning. Update now.

Code in the Wild: Full Technical Deep-Dive and Public GitHub PoC Released for Critical Linux TLS Root Exploit CIFSwitch local root exploit cifs-utils privilege escalation Linux Kernel Root Exploit CVE-2025-39946 PoC CVE-2023-2598 PoC Ubuntu LPE Vulnerability CVE-2026-3888
  • Vulnerability

Code in the Wild: Full Technical Deep-Dive and Public GitHub PoC Released for Critical Linux TLS Root Exploit

Do Son March 25, 2026 0

Full disclosure: Technical details and a GitHub PoC for CVE-2025-39946 are live. This Linux TLS vulnerability allows root escalation via memory shaping.
Beyond the Hook: Unmasking SnappyClient, the HijackLoader-Linked Stealth Stealer Targeting Crypto SnappyClient HijackLoader
  • Malware

Beyond the Hook: Unmasking SnappyClient, the HijackLoader-Linked Stealth Stealer Targeting Crypto

Do Son March 25, 2026 0

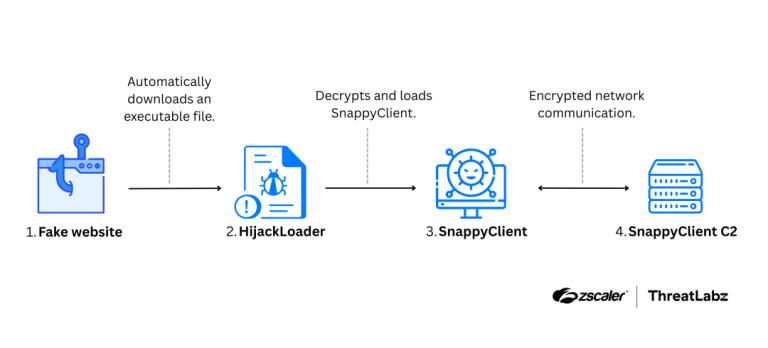
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.
Larva-26002 Threat Actor Escalates Attacks on MS-SQL Servers ICE Cloud Malware Larva-26002
  • Malware

Larva-26002 Threat Actor Escalates Attacks on MS-SQL Servers

Do Son March 25, 2026 0

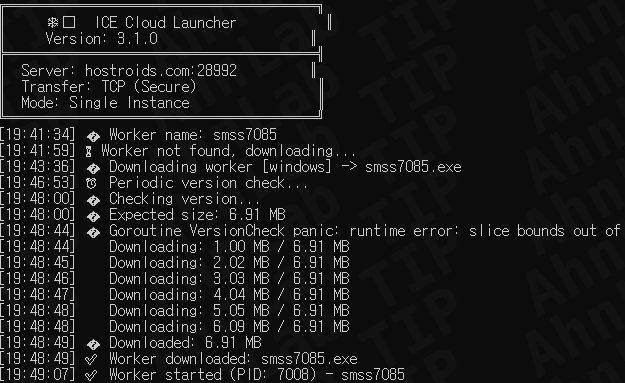
Larva-26002 strikes again with "ICE Cloud," a Go-based scanner using AI-assisted code to hijack MS-SQL servers. Discover the technical breakdown and defense.
Streaming Nightmare: Unpatched CVSS 10.0 Flaws Leave AVideo Servers Wide Open AVideo RCE YPTSocket Vulnerability AVideo Vulnerabilities Streaming Platform Security AVideo Vulnerabilities CVE-2026-28501
  • Vulnerability Report

Streaming Nightmare: Unpatched CVSS 10.0 Flaws Leave AVideo Servers Wide Open

Do Son March 25, 2026 0

AVideo faces a security crisis with 5 unpatched critical flaws (CVSS 10.0). Attackers can hijack streams and execute code. Learn how to protect your server.

The Sunset of Sora: Why OpenAI is Killing its Video Giant to Build an AI Super-App OpenAI Sora shutdown 2026
  • Technology

The Sunset of Sora: Why OpenAI is Killing its Video Giant to Build an AI Super-App

Do Son March 25, 2026 0

OpenAI is shuttering Sora as a standalone product. Discover the 2026 strategic shift toward an AI super-app and the end of the Disney video partnership.
The Digital Fortress Falls: Why Russia Blocked Archive.today and Wikipedia Severed Its Links Archive.today Russia block
  • Technology

The Digital Fortress Falls: Why Russia Blocked Archive.today and Wikipedia Severed Its Links

Do Son March 25, 2026 0

Russia’s Roskomnadzor has blocked Archive.today using DPI technology, while Wikipedia has banned the site over hidden DDoS code. Is the paywall-killer dead?

Beyond the SCSI Bottleneck: How to Unlock the Hidden Native NVMe Driver in Windows 11 Windows 11 native NVMe driver NVMe IOPS performance boost
  • Windows

Beyond the SCSI Bottleneck: How to Unlock the Hidden Native NVMe Driver in Windows 11

Do Son March 25, 2026 0

Boost your SSD speed! Discover how to enable the hidden native NVMe driver in Windows 11 to bypass SCSI translation and supercharge your IOPS performance.

3 Steps to Reduce Phishing MTTR to Minutes in Your SOC Screenshot 2026-03-24 at 13.36.12
  • Technique

3 Steps to Reduce Phishing MTTR to Minutes in Your SOC

Do Son March 25, 2026 0
Phishing no longer needs a fake login page to succeed. Today’s attacks increasingly abuse legitimate services, trusted...
Read More Read more about 3 Steps to Reduce Phishing MTTR to Minutes in Your SOC
VoidStealer Debuts Novel Debugger Bypass for Chrome and Edge Encryption VoidStealer ABE Bypass
  • Malware

VoidStealer Debuts Novel Debugger Bypass for Chrome and Edge Encryption

Do Son March 25, 2026 0

Gen Threat Labs uncovers VoidStealer, the first malware using a debugger-based bypass to extract Chrome and Edge encryption keys via hardware breakpoints.
95 Million Downloads Hijacked: The LiteLLM PyPI Backdoor Targeting AI Developers LiteLLM PyPI Supply Chain Attack
  • Malware

95 Million Downloads Hijacked: The LiteLLM PyPI Backdoor Targeting AI Developers

Do Son March 25, 2026 0

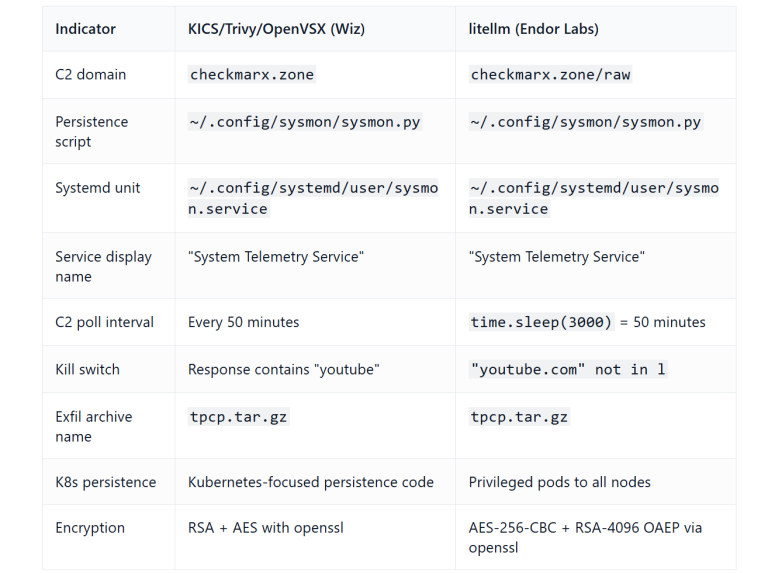
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.
From Viewer to SYSTEM: Critical 10.0 CVSS Flaw in GeoVision ERM Allows Full Host Takeover GeoVision CVE-2026-4606 Local Privilege Escalation
  • Vulnerability Report

From Viewer to SYSTEM: Critical 10.0 CVSS Flaw in GeoVision ERM Allows Full Host Takeover

Do Son March 25, 2026 0

GeoVision fixes a critical 10.0 CVSS flaw in GV-Edge Recording Manager. CVE-2026-4606 allows local users to gain SYSTEM-level control. Update to V2.3.2 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.