Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Siri’s Secret Engine: Why 90% of Apple’s AI Servers are Idle as Google Gemini Takes the Reins iOS 27 Apple Intelligence Apple AI Extensions bazaar Siri iOS 27 Gemini integration Apple AI server Baltra Siri AI delay iOS 26.4 Apple Google Gemini Siri partnership, Siri powered by Google Gemini 2026 Siri Gemini, Apple Intelligence Siri, Apple AI Apple "Veritas", Siri AI Siri Gemini Supercharged Siri, AI assistant Siri Integration, App Intents Apple Siri Apple AI Strategy, ChatGPT Rival
  • Technology

Siri’s Secret Engine: Why 90% of Apple’s AI Servers are Idle as Google Gemini Takes the Reins

Do Son March 4, 2026 0

Apple’s AI infrastructure faces a 90% dormancy crisis. To save Siri, Apple is turning to Google Gemini while secretly developing the 3nm "Baltra" AI chip.
Critical RCE Vulnerability Discovered in OpenStack Vitrage Root Cause Analysis Service OpenStack Vitrage RCE CVE-2026-28370
  • Vulnerability Report

Critical RCE Vulnerability Discovered in OpenStack Vitrage Root Cause Analysis Service

Do Son March 4, 2026 0

Nokia discovers a critical 9.1 RCE flaw (CVE-2026-28370) in OpenStack Vitrage's RCA service. Patch immediately to prevent total host server takeovers.
Critical Auth Bypass in Apache Artemis: Attackers Can Hijack Message Queues ActiveMQ security flaws Jolokia web console exploit ActiveMQ RCE Jolokia Spring Vulnerability ActiveMQ MQTT Vulnerability CVE-2025-66168 Apache Artemis Vulnerability CVE-2026-27446
  • Vulnerability

Critical Auth Bypass in Apache Artemis: Attackers Can Hijack Message Queues

Do Son March 4, 2026 0

A critical flaw (CVE-2026-27446) in Apache Artemis allows unauthenticated attackers to hijack message queues via rogue brokers. Update to 2.52.0 immediately.

Django Releases Security Patches to Address DoS and Permission Vulnerabilities Django Security Update CVE-2026-25673 Django Security Update SQL Injection Vulnerability Django SQL Injection, PostgreSQL Flaw CVE-2022-34265 PoC Django, SQL injection
  • Vulnerability Report

Django Releases Security Patches to Address DoS and Permission Vulnerabilities

Do Son March 4, 2026 0

Django releases security updates (6.0.3, 5.2.12, 4.2.29) to fix a Windows DoS flaw (CVE-2026-25673) and file permission risks. Upgrade your framework now.

CISA Adds Qualcomm and VMware Flaws to Known Exploited Catalog Ivanti EPMM Vulnerability CVE-2026-1340 CISA KEV Catalog CVE-2026-21385 CISA KEV Update CVE-2008-0015 CISA KEV, Array Networks Command Injection CVE-2025-0111 & CVE-2025-23209 CISA, Known Exploited Vulnerabilities
  • Vulnerability Report

CISA Adds Qualcomm and VMware Flaws to Known Exploited Catalog

Do Son March 4, 2026 0

CISA adds actively exploited Qualcomm (CVE-2026-21385) and VMware (CVE-2026-22719) flaws to its KEV catalog. See the impact and patch deadlines inside.

Cyber Retaliation Escalates: Iranian Hacktivists Target Critical Infrastructure Following Military Strikes Iranian Hacktivists Operation Epic Fury Cyber New Generation Warfare Russian Hybrid Escalation Plex data breach Water Systems Cybersecurity - Threat Actor Naming Standard
  • Cyber Security

Cyber Retaliation Escalates: Iranian Hacktivists Target Critical Infrastructure Following Military Strikes

Do Son March 4, 2026 0

Sophos X-Ops CTU warns of a surge in Iranian hacktivist cyber retaliation, including DDoS and targeted doxxing, following Operation Epic Fury.
Critical Vulnerabilities in AVideo: From SQL Injection to Remote Code Execution AVideo RCE YPTSocket Vulnerability AVideo Vulnerabilities Streaming Platform Security AVideo Vulnerabilities CVE-2026-28501
  • Vulnerability Report

Critical Vulnerabilities in AVideo: From SQL Injection to Remote Code Execution

Do Son March 4, 2026 0

AVideo patches two critical flaws (CVE-2026-28501 & 28502) allowing unauthenticated SQL injection and remote code execution. Update to version 23 now.

WordPress Security Alert: Critical Privilege Escalation Flaw in Popular Membership Plugin WordPress Privilege Escalation CVE-2026-1492 Sneeit Framework RCE, Unauthenticated Code Execution Post SMTP, Account Takeover WordPress Vulnerability, Unpatched XSS WordPress Vulnerability, PHP Object Injection WordPress AI Engine, Privilege Escalation CVE-2024-43153 & CVE-2024-43234
  • Vulnerability Report

WordPress Security Alert: Critical Privilege Escalation Flaw in Popular Membership Plugin

Do Son March 4, 2026 0

A critical 9.8 CVSS flaw (CVE-2026-1492) in the WordPress User Registration & Membership plugin lets unauthenticated attackers create admin accounts.
OAuth Hijack: Phishing Campaigns Weaponize Legitimate Redirection to Bypass Defenses OAuth Phishing Redirect URI Abuse
  • Cybercriminals

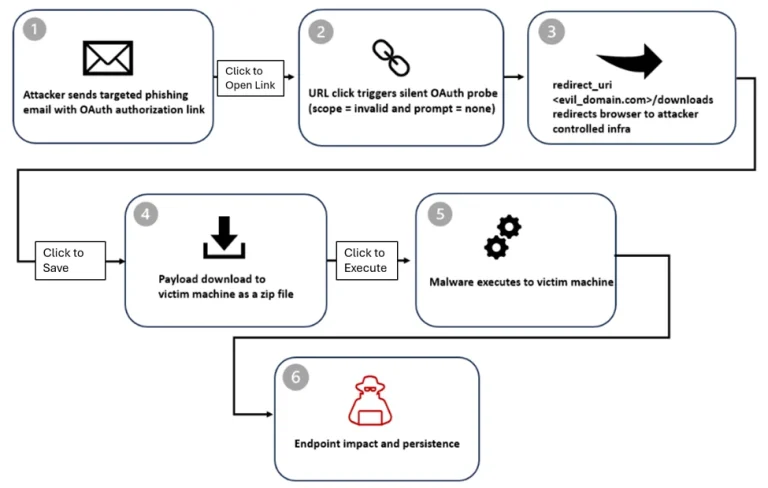
OAuth Hijack: Phishing Campaigns Weaponize Legitimate Redirection to Bypass Defenses

Do Son March 4, 2026 0

Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.

ClickFix Alert: Fake Venture Capitalists Target Web3 Pros with “Terminal” Phishing ClickFix Malware Crypto VC Scam
  • Malware

ClickFix Alert: Fake Venture Capitalists Target Web3 Pros with “Terminal” Phishing

Do Son March 4, 2026 0

Moonlock Lab uncovers a North Korean-aligned malware campaign targeting Web3 pros. Attackers use fake VC profiles and ClickFix CAPTCHAs to deploy malware.

Trojanized FileZilla FTP Client Targets Developer Credentials via DLL Sideloading FileZilla Malware DLL Hijacking
  • Malware

Trojanized FileZilla FTP Client Targets Developer Credentials via DLL Sideloading

Do Son March 4, 2026 0

Malwarebytes uncovers a trojanized FileZilla campaign using DLL hijacking and DNS-over-HTTPS to silently steal FTP credentials and bypass security.
Critical RCE Flaw in Qwik Framework Allows Server Takeover via Single Request Qwik RCE CVE-2026-27971
  • Vulnerability Report

Critical RCE Flaw in Qwik Framework Allows Server Takeover via Single Request

Do Son March 4, 2026 0

Qwik framework patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-27971) where unsafe deserialization in server$ RPC allows total server takeover.
The BurrowShell Threat: Inside ‘Sloppy Lemming’s’ Stealthy Cyber Espionage Campaign in South Asia Sloppy Lemming BurrowShell Malware
  • Cyber Security
  • Malware

The BurrowShell Threat: Inside ‘Sloppy Lemming’s’ Stealthy Cyber Espionage Campaign in South Asia

Do Son March 4, 2026 0

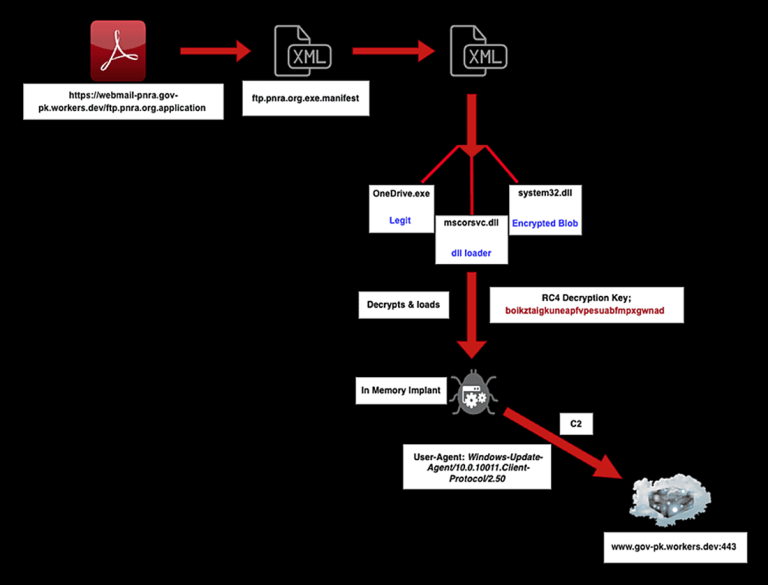
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.

AuraStealer: The “Result-Oriented” Malware Rising from the Post-Lumma Void AuraStealer Malware Infostealer
  • Malware

AuraStealer: The “Result-Oriented” Malware Rising from the Post-Lumma Void

Do Son March 4, 2026 0

Following the Lumma takedown, the sophisticated AuraStealer malware is rapidly gaining ground, using TikTok scams and stealth to harvest data.

The Trojan Prompt: How an Autonomous AI Hijacked Aqua Trivy to Weaponize Developer Copilots AI Prompt Injection Aqua Trivy Breach AI Assistant Apertus, open-source AI .ai domain milestone
  • Vulnerability Report

The Trojan Prompt: How an Autonomous AI Hijacked Aqua Trivy to Weaponize Developer Copilots

Do Son March 4, 2026 0

Socket reveals how an AI bot hijacked the Aqua Trivy VS Code extension, using prompt injection to turn developer AI assistants into stealthy data thieves.

PlugX Evolves: New “Meeting Invitation” Phishing Campaign Leverages Trusted Security Software Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Malware

PlugX Evolves: New “Meeting Invitation” Phishing Campaign Leverages Trusted Security Software

Do Son March 4, 2026 0

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

Archipelo and Checkmarx Announce Partnership Connecting AppSec Detection with DevSPM image_18_1772539903dkCSeaHBoZ
  • Press Release

Archipelo and Checkmarx Announce Partnership Connecting AppSec Detection with DevSPM

cybernewswire March 3, 2026 0
San Francisco, CA, United States, 3rd March 2026, CyberNewswire
Read More Read more about Archipelo and Checkmarx Announce Partnership Connecting AppSec Detection with DevSPM
Cyber Escalation: Multi-Vector Attacks Surge Following “Operation Epic Fury” GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cyber Security

Cyber Escalation: Multi-Vector Attacks Surge Following “Operation Epic Fury”

Do Son March 3, 2026 0

Unit 42 details the cyber fallout of Operation Epic Fury. Despite internet blackouts, autonomous hacktivists claim breaches of Israeli defense networks.

Security Alert: “Hackerbot-Claw” Autonomous Campaign Exploits GitHub Actions hackerbot-claw campaign Cisco RCE Exploit CVE-2026-20045 SonicWall VPN, Akira Ransomware Nobelium Apache Tomcat, Apache Camel
  • Vulnerability Report

Security Alert: “Hackerbot-Claw” Autonomous Campaign Exploits GitHub Actions

Do Son March 3, 2026 0

OpenSSF warns of "hackerbot-claw," an autonomous AI bot exploiting GitHub Actions to hijack repositories. Secure your CI/CD pipeline before it’s too late.

Anthropic Launches “Memory Import” to Rescue Your ChatGPT Context Amid #QuitGPT Exodus Claude Memory Import
  • Technology

Anthropic Launches “Memory Import” to Rescue Your ChatGPT Context Amid #QuitGPT Exodus

Do Son March 3, 2026 0

Anthropic’s new "Memory Import" tool lets you move your ChatGPT context to Claude in minutes. Perfect for those joining the #QuitGPT movement this March.

Samsung Wallet Adopts Aliro Standard to Unlock Your Home with a Galaxy Tap Samsung Wallet Digital Home Key
  • Technology

Samsung Wallet Adopts Aliro Standard to Unlock Your Home with a Galaxy Tap

Do Son March 3, 2026 0

Samsung Wallet now supports "Digital Home Key" via the Aliro standard. Unlock your door with a Galaxy tap, secured by EAL6+ hardware and Samsung Knox.

Apple Unveils the iPhone 17e with A19 Power and MagSafe for $599 A19 processor
  • Technology

Apple Unveils the iPhone 17e with A19 Power and MagSafe for $599

Do Son March 3, 2026 0

Apple’s new iPhone 17e brings the A19 chip, MagSafe, and Apple Intelligence to a $599 price point. With 256GB base storage, it’s the new king of value.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.