Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Red Lines in the Rubble: OpenAI Enters the “Department of War” as Claude AI Powers Strikes on Iran OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

Red Lines in the Rubble: OpenAI Enters the “Department of War” as Claude AI Powers Strikes on Iran

Do Son March 3, 2026 0

OpenAI signs a classified deal with the "Department of War" as the US military continues using banned Anthropic tech for high-stakes airstrikes in Iran.

Urgent Patch Required: HPE AutoPass License Server Hits Maximum Severity Risk HPE AutoPass Vulnerability, CVE-2026-23600 CVE-2024-22442 - HPE vulnerability HPE Storage Vulnerability CVE-2026-23594
  • Vulnerability Report

Urgent Patch Required: HPE AutoPass License Server Hits Maximum Severity Risk

Do Son March 3, 2026 0

HPE warns of a critical CVSS 10.0 vulnerability (CVE-2026-23600) in AutoPass License Server. Remote attackers can bypass authentication. Patch to 9.19 now!

North Korean “StegaBin” Campaign Targets Developers with Steganographic Malware North Korean Laptop Farm DPRK Insider Threat North Korea WMD Cyber Funding, Australia Sanctions Insider threat, North Korean hackers Kimsuky, cyber-espionage NPM Malware, North Korea Cyber-espionage North Korea, Remote IT Job Scam Laptop Farm - DriverEasy - Kimsuky Watering Hole Attack
  • Malware

North Korean “StegaBin” Campaign Targets Developers with Steganographic Malware

Do Son March 3, 2026 0

Socket uncovers "StegaBin," a North Korean malware campaign hiding C2 URLs in Pastebin essays to steal developer secrets via 26 typosquatted npm packages.

Security Alert: Android March 2026 Update Targets Actively Exploited Zero-Day Android CLI Android Security Zero-Interaction DoS CVE-2026-21385 Android Security Update UK CMA Apple Google regulation Google Aluminum OS Android 16 leak, ALOS Android ChromeOS merger Android sideloading certification 2026, Google developer verification APK Android AOSP biannual release, AOSP source code latency 2026 Android Zero-Day, Critical DoS Flaw Android Universal Clipboard Cross-Device Sync Gemini Nano Block, Unlocked Bootloader Android, Calling Cards Android Security Bulletin, RCE Vulnerability Android Linux GUI, Debian VM Android System Services, Google Transparency Android 16, Pixel Update
  • Android
  • Vulnerability Report

Security Alert: Android March 2026 Update Targets Actively Exploited Zero-Day

Do Son March 3, 2026 0

Google’s March 2026 Android update fixes 129 flaws, including CVE-2026-21385—a high-severity Qualcomm vulnerability currently being exploited in the wild.

CVE-2026-2256: Unpatched Flaw in MS-Agent Lets Hackers Hijack AI Assistants shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

CVE-2026-2256: Unpatched Flaw in MS-Agent Lets Hackers Hijack AI Assistants

Do Son March 3, 2026 0

An unpatched zero-day flaw (CVE-2026-2256) in the MS-Agent framework allows hackers to use prompt injection to execute OS commands and hijack AI systems.
Beyond the Router: How the Zerobotv9 Botnet is Hijacking Enterprise Automation Zerobotv9 Botnet n8n Vulnerability VMware ESXi Ransomware
  • Malware

Beyond the Router: How the Zerobotv9 Botnet is Hijacking Enterprise Automation

Do Son March 3, 2026 0

Akamai SIRT reveals Zerobotv9, a new Mirai-based botnet targeting enterprise n8n workflow platforms and Tenda routers via critical vulnerabilities.

High-Severity XSS Flaw in Angular i18n Turns Language Files into Backdoors Angular hostname hijacking vulnerability Angular SSRF Origin Hijacking Angular XSS Vulnerability CVE-2026-32635 Angular i18n XSS CVE-2026-27970 Angular SSR SSRF CVE-2026-27739 Angular Vulnerability CVE-2026-22610 CVE-2025-59052 Angular security Angular XSS Bypass, SVG Injection
  • Vulnerability Report

High-Severity XSS Flaw in Angular i18n Turns Language Files into Backdoors

Do Son March 3, 2026 0

Angular patches a high-severity 7.6 CVSS XSS flaw (CVE-2026-27970). Attackers can weaponize i18n translation files to steal data and hijack user sessions.

From Chat App to Dark Web: How Telegram Became the New Hub for Cybercrime CVE-2024-22394
  • Cybercriminals

From Chat App to Dark Web: How Telegram Became the New Hub for Cybercrime

Do Son March 3, 2026 0

Cyfirma reveals how Telegram has replaced the dark web as the ultimate digital black market, making tools like malware and data theft available to anyone.

The Fake Security Checkup: How a Rogue ‘Google’ App Hijacks Your Digital Life PWA Malware Google-prism
  • Cybercriminals

The Fake Security Checkup: How a Rogue ‘Google’ App Hijacks Your Digital Life

Do Son March 3, 2026 0

Cybercriminals are using a fake Google security checkup (google-prism) to trick you into installing powerful PWA malware. Learn how to spot the trap.

The Invisible Trap: How Hackers Weaponize the Internet’s Root Infrastructure (.arpa) to Bypass Security Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cybercriminals

The Invisible Trap: How Hackers Weaponize the Internet’s Root Infrastructure (.arpa) to Bypass Security

Do Son March 3, 2026 0

Infoblox uncovers a novel phishing tactic abusing the .arpa TLD. Attackers hijack internet "plumbing" to bypass firewalls and deliver brand-impersonation scams.

OpenAI Exposes the Massive Global Underworld of Malicious AI OpenAI Threat Report Cyber Special Operations
  • Cybercriminals

OpenAI Exposes the Massive Global Underworld of Malicious AI

Do Son March 3, 2026 0

OpenAI’s Feb 2026 report reveals "cyber special operations," Cambodian "Date Bait" scams, and Russian content farms using AI to automate global disruption.
Bridging the Gap: North Korean APT37 Deploys ‘Ruby Jumper’ to Infiltrate Isolated Air-Gapped Networks CVE-2024-3393 - Zservers sanctions
  • Malware

Bridging the Gap: North Korean APT37 Deploys ‘Ruby Jumper’ to Infiltrate Isolated Air-Gapped Networks

Do Son March 3, 2026 0

Zscaler unmasked APT37's "Ruby Jumper" campaign, which uses weaponized USBs and cloud services to bypass network isolation and steal data from air-gapped systems.

The High Cost of ‘Free’: How PiviGames Became a Lovecraftian Malware Hub for HijackLoader and ACRStealer Lotus Wiper Digital Sabotage G_Wagon Malware NPM Supply Chain Attack IMAPLoader malware ResolverRAT Malware Evasion
  • Malware

The High Cost of ‘Free’: How PiviGames Became a Lovecraftian Malware Hub for HijackLoader and ACRStealer

Do Son March 3, 2026 0

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.

Criminal IP to Present Decision-Ready Threat Intelligence at RSAC™ 2026 1200_720_1_1772088331SAvTYOiwF2
  • Press Release

Criminal IP to Present Decision-Ready Threat Intelligence at RSAC™ 2026

cybernewswire March 2, 2026 0
Torrance, United States / California, 2nd March 2026, CyberNewswire
Read More Read more about Criminal IP to Present Decision-Ready Threat Intelligence at RSAC™ 2026
Link11 Releases European Cyber Report 2026: DDoS Attacks Become a Constant Threat Link11_ECR_Eng_1772103046oiPBPragVC
  • Press Release

Link11 Releases European Cyber Report 2026: DDoS Attacks Become a Constant Threat

cybernewswire March 2, 2026 0
Frankfurt am Main, Germany, 2nd March 2026, CyberNewswire
Read More Read more about Link11 Releases European Cyber Report 2026: DDoS Attacks Become a Constant Threat
Cloud Under Fire: Unidentified “Objects” Strike AWS Data Center in UAE Amid Regional Tensions Amazon Redshift JDBC Driver RCE CVE-2026-8178 AWS Bahrain fire 2026 AWS UAE data center fire Amazon North Korean hacker keystroke latency, Arizona laptop farm infiltration
  • Technology

Cloud Under Fire: Unidentified “Objects” Strike AWS Data Center in UAE Amid Regional Tensions

Do Son March 2, 2026 0

An AWS data center in the UAE (mec1-az2) was struck by "objects" on March 1, triggering a fire and power outage amid regional missile and drone activity.

The Antigravity Reinstatement: Google Relents on Ban Wave but Issues Final Warning on OpenClaw Proxies Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

The Antigravity Reinstatement: Google Relents on Ban Wave but Issues Final Warning on OpenClaw Proxies

Do Son March 2, 2026 0

Google has refreshed Antigravity and started reinstating accounts suspended for token proxying. Learn how to recover your access and avoid permanent bans.

Critical Backup Flaws Expose Vitess Environments to Complete Takeover Vitess Backup Poisoning CVE-2026-27969
  • Vulnerability Report

Critical Backup Flaws Expose Vitess Environments to Complete Takeover

Do Son March 2, 2026 0

Vitess patches critical flaws (CVE-2026-27969 & 27965) where poisoned backup manifests lead to path traversal and RCE during restoration. Update to v23.0.3 now.
Critical 9.8 Flaw in Langflow’s AI CSV Agent Opens a Direct Path to Root Shell Langflow Vulnerability CVE-2026-42048 Langflow RCE CVE-2026-27966 Langflow Vulnerabilities CVE-2026-33017
  • Vulnerability Report

Critical 9.8 Flaw in Langflow’s AI CSV Agent Opens a Direct Path to Root Shell

Do Son March 2, 2026 0

Langflow 1.8.0 patches a critical 9.8 CVSS RCE vulnerability (CVE-2026-27966) where a hardcoded "allow_dangerous_code" setting enables prompt injection attacks.

Critical Flaws in Vikunja Expose Users to Persistent Account Takeovers Vikunja Persistent Takeover CVE-2026-28268
  • Vulnerability Report

Critical Flaws in Vikunja Expose Users to Persistent Account Takeovers

Do Son March 2, 2026 0

Vikunja v2.0.1 patches critical flaws (CVE-2026-27575 & 28268) where "immortal" reset tokens and persistent sessions allow attackers to hijack accounts forever.
The Cryptography Trojan: Malicious Go Module Impersonates Foundational Library to Steal Passwords and Deploy Root Backdoors Go Supply Chain Attack Rekoobe Backdoor
  • Malware

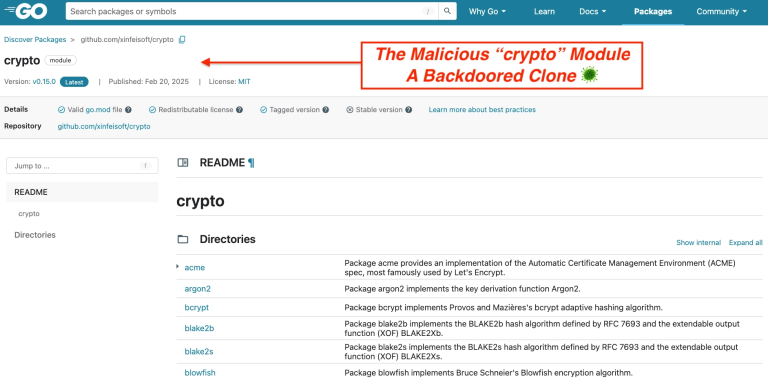
The Cryptography Trojan: Malicious Go Module Impersonates Foundational Library to Steal Passwords and Deploy Root Backdoors

Do Son March 2, 2026 0

Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.
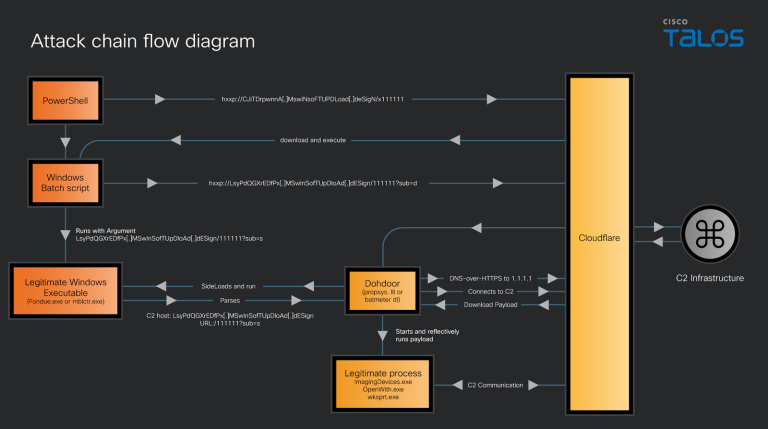
Dohdoor: New Stealth Backdoor Targets US Healthcare and Education Dohdoor Backdoor UAT-10027
  • Malware

Dohdoor: New Stealth Backdoor Targets US Healthcare and Education

Do Son March 2, 2026 0

Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.