Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
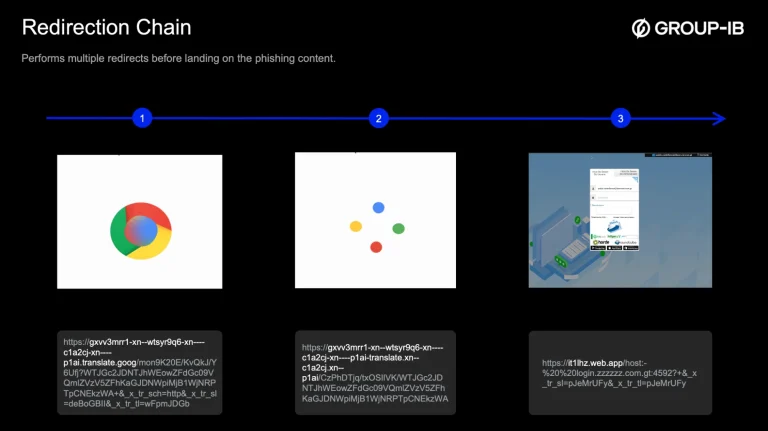
The GTFire Scheme: How Cybercriminals are Weaponizing Google’s Trusted Services for Global Phishing GTFire Phishing Campaign Google Firebase Abuse
  • Cybercriminals

The GTFire Scheme: How Cybercriminals are Weaponizing Google’s Trusted Services for Global Phishing

Do Son March 2, 2026 0

Group-IB uncovers "GTFire," a massive credential-harvesting operation abusing Google Firebase and Translate to bypass security filters in 100+ countries.
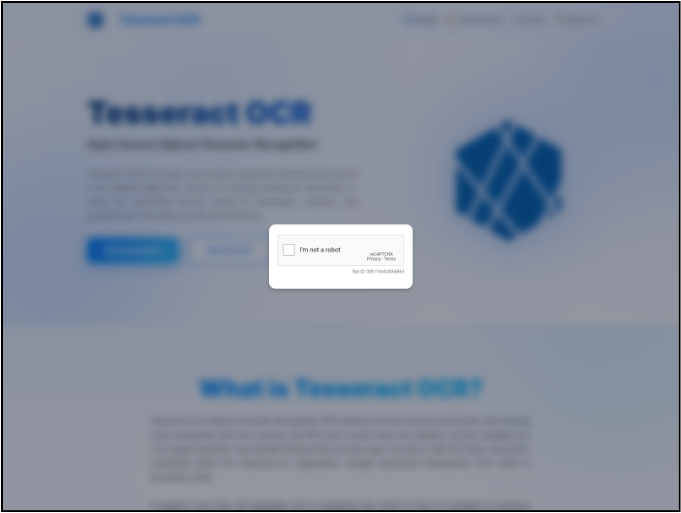
OCRFix: When Fake CAPTCHAs, AI, and Blockchains Collide to Build a Botnet OCRFix Malware Campaign ClickFix Tactic
  • Malware

OCRFix: When Fake CAPTCHAs, AI, and Blockchains Collide to Build a Botnet

Do Son March 2, 2026 0

CYJAX uncovers "OCRFix," a stealthy campaign using fake Tesseract OCR sites, ClickFix social engineering, and EtherHiding to bypass security via blockchain.

CVE-2026-27728 (CVSS 10): Critical Command Injection Flaw in OneUptime Probe Enables Full Server Takeover OneUptime RCE CVE-2026-27728
  • Vulnerability Report

CVE-2026-27728 (CVSS 10): Critical Command Injection Flaw in OneUptime Probe Enables Full Server Takeover

Do Son March 2, 2026 0

OneUptime 10.0.7 patches a critical 10.0 CVSS vulnerability (CVE-2026-27728). Attackers can use traceroute probes to execute root commands and steal data.

Critical Path Traversal Flaw in basic-ftp Exposes Node.js Apps to Arbitrary File Writes shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Critical Path Traversal Flaw in basic-ftp Exposes Node.js Apps to Arbitrary File Writes

Do Son March 2, 2026 0

Node.js library basic-ftp patches a critical 9.1 CVSS path traversal flaw (CVE-2026-27699). Malicious FTP servers can overwrite any file on the client machine.

Steering the Server: Critical 9.2 Severity SSRF Flaw in Angular SSR Allows Internal Network Probing Angular hostname hijacking vulnerability Angular SSRF Origin Hijacking Angular XSS Vulnerability CVE-2026-32635 Angular i18n XSS CVE-2026-27970 Angular SSR SSRF CVE-2026-27739 Angular Vulnerability CVE-2026-22610 CVE-2025-59052 Angular security Angular XSS Bypass, SVG Injection
  • Vulnerability Report

Steering the Server: Critical 9.2 Severity SSRF Flaw in Angular SSR Allows Internal Network Probing

Do Son March 2, 2026 0

Angular patches a critical 9.2 CVSS SSRF vulnerability (CVE-2026-27739). Attackers can manipulate Host headers to steal credentials and probe internal networks.

The New Voice of Fraud: Cybercrime ‘Supergroup’ Recruits Female Callers to Breach Corporate IT Help Desks CRussian Market, "Fly" (Flyded) hange Healthcare Cyberattack - CVE-2024-50603 Exploit
  • Cybercriminals

The New Voice of Fraud: Cybercrime ‘Supergroup’ Recruits Female Callers to Breach Corporate IT Help Desks

Do Son March 2, 2026 0

The Scattered Lapsus$ Hunters "supergroup" is paying $1,000 per successful vishing call. Discover how they use female recruits to bypass corporate IT security.

WPA Hash Analysis: Turning Bitcoin’s 50% Drop into Cloud Mining Opportunities for Investors Screenshot_20260303_002337_Docs
  • Technique

WPA Hash Analysis: Turning Bitcoin’s 50% Drop into Cloud Mining Opportunities for Investors

Do Son March 2, 2026 0
The last 50% percent reduction of the price of bitcoin has dramatically changed the trend of crypto...
Read More Read more about WPA Hash Analysis: Turning Bitcoin’s 50% Drop into Cloud Mining Opportunities for Investors
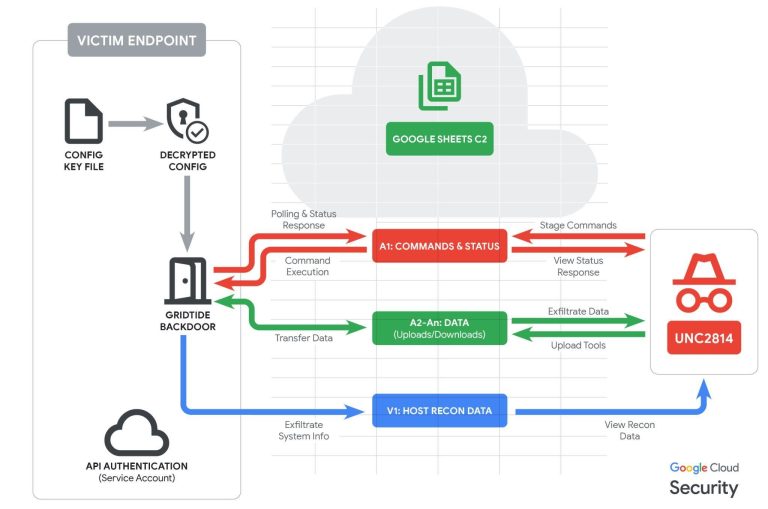
Google Dismantles UNC2814’s Global Espionage Network Fueled by Google Sheets UNC2814 Espionage GRIDTIDE Backdoor
  • Cybercriminals

Google Dismantles UNC2814’s Global Espionage Network Fueled by Google Sheets

Do Son March 2, 2026 0

Google and Mandiant disrupt UNC2814, a China-nexus group using the GRIDTIDE backdoor to hide command-and-control traffic inside Google Sheets across 42 nations.

Critical CISA Advisory Unmasks Severe Flaws in EV2GO Charging Networks EV2GO Charging Platform ICSA-26-057-04 Lazarus Group, Crypto Hacks LazyStealer
  • Vulnerability Report

Critical CISA Advisory Unmasks Severe Flaws in EV2GO Charging Networks

Do Son February 28, 2026 0

CISA issues an urgent ICS advisory (ICSA-26-057-04) for the EV2GO charging platform. Critical 9.4 severity flaws allow for session hijacking and station impersonation.

Massive SonicWall Reconnaissance Campaign Signals Imminent Ransomware Strikes SonicWall Reconnaissance Akira Ransomware residential proxy malware TraderTraitor BreachForums Honeypot, French Interior Ministry Leak
  • Cybercriminals

Massive SonicWall Reconnaissance Campaign Signals Imminent Ransomware Strikes

Do Son February 28, 2026 0

GreyNoise detects a coordinated surge in SonicWall reconnaissance. With over 84,000 scans, attackers are mapping VPNs for Akira and Fog ransomware strikes.

API-Free Autonomy: Anthropic Acquires Vercept to Give Claude “Human-Like Eyes” for Desktop Mastery Anthropic Vercept acquisition Claude AI model Anthropic ad-free Claude
  • Technology

API-Free Autonomy: Anthropic Acquires Vercept to Give Claude “Human-Like Eyes” for Desktop Mastery

Do Son February 27, 2026 0

Anthropic has acquired Vercept to solve the "perception problem" in AI. Claude can now see and navigate any software interface with human-level precision.

Standard Hardware, Military Guard: NATO Certifies Retail iPhones for Restricted State Intelligence FCC Chinese lab ban iPhone NATO certification iPhone 18 Pro Deep Red iOS 27 Snow Leopard update 2026 smartphone memory shortage, IDC mobile market forecast iPhone Satellite Natural Usage iPhone 17 Speaker Issue, USB-C Static iPhone 17 Pro, MagSafe Scratches iPhone 17 Pro, professional filmmaking
  • Technology

Standard Hardware, Military Guard: NATO Certifies Retail iPhones for Restricted State Intelligence

Do Son February 27, 2026 0

In a historic first, NATO has certified retail iPhones and iPads running iOS 26 for "Restricted" data, proving Apple’s consumer hardware is officially war-ready.

Google Unveils Nano Banana 2 to Standardize 4K AI Imaging Across Gemini Nano Banana 2
  • Technology

Google Unveils Nano Banana 2 to Standardize 4K AI Imaging Across Gemini

Do Son February 27, 2026 0

Google’s Nano Banana 2 is here! Powered by Gemini 3.1 Flash, it delivers 4K fidelity, 5-character consistency, and Pro-level speed across all Google apps.
Tim Cook’s “Big Week”: Apple Prepares to Unleash M5 MacBooks and the Disruptive iPhone 17e Apple Experience March 4 Apple Spring Event 2026
  • Technology

Tim Cook’s “Big Week”: Apple Prepares to Unleash M5 MacBooks and the Disruptive iPhone 17e

Do Son February 27, 2026 0

Apple’s "Big Week" starts March 2. Get ready for the M5 MacBook lineup, the budget-friendly iPhone 17e, and a rumored sub-$700 vibrant entry-level MacBook.

Apple Releases Xcode 26.3 with Native Claude and Codex AI Agents Xcode 26.3 Agentic Coding
  • Technology

Apple Releases Xcode 26.3 with Native Claude and Codex AI Agents

Do Son February 27, 2026 0

Xcode 26.3 is out! Transform your workflow with Agentic Coding. Native Claude and Codex integration lets AI agents write, build, and test your apps for you.

Clockwork Twitch: Amazon’s New Policy Freezes Ad Timers if You Mute, Minimize, or Look Away Twitch ad attention mandate
  • Technology

Clockwork Twitch: Amazon’s New Policy Freezes Ad Timers if You Mute, Minimize, or Look Away

Do Son February 27, 2026 0

Amazon is forcing "undivided attention" on Twitch. New rules freeze ad timers if you mute, minimize, or switch tabs. Is this the end of background viewing?

Powering the Core: Anthropic Offers 10,000 Free “Claude Max 20x” Subscriptions to Open-Source Heroes Anthropic confidential IPO filing Anthropic Google $200 billion deal Anthropic Mythos Preview Anthropic Pentagon blacklist Claude Max 20x open-source Model Distillation Anthropic vs DeepSeek Claude Free tier update 2026
  • Technology

Powering the Core: Anthropic Offers 10,000 Free “Claude Max 20x” Subscriptions to Open-Source Heroes

Do Son February 27, 2026 0

Anthropic is giving away 10,000 free 6-month Claude Max 20x subscriptions to elite open-source maintainers. Apply by June 30, 2026, to claim your AI power.
Hackers Impersonate Stripe.net to Hijack the Global Payment Supply Chain Stripe.net Typosquatting NuGet Supply Chain Attack
  • Cybercriminals

Hackers Impersonate Stripe.net to Hijack the Global Payment Supply Chain

Do Son February 27, 2026 0

ReversingLabs uncovers a malicious NuGet package mimicking Stripe.net. Discover how attackers are targeting the financial sector via supply chain poisoning.

The Explorer Trap: How Hackers Turn Windows File Explorer into a Silent Portal for Remote Access Trojans Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Cybercriminals

The Explorer Trap: How Hackers Turn Windows File Explorer into a Silent Portal for Remote Access Trojans

Do Son February 27, 2026 0

Cofense uncovers a stealthy campaign abusing legacy WebDAV in Windows File Explorer to bypass browsers and EDR, delivering XWorm and Async RAT via UNC paths.

Critical XSS Flaw in RustFS Exposes S3 Storage to Total Admin Account Takeovers RustFS XSS Vulnerability CVE-2026-27822
  • Vulnerability Report

Critical XSS Flaw in RustFS Exposes S3 Storage to Total Admin Account Takeovers

Do Son February 27, 2026 0

RustFS patches a critical 9.1 CVSS XSS flaw (CVE-2026-27822). Attackers can steal S3 credentials via a malicious file preview. Update to 1.0.0-alpha.83 now!

Beyond Ukraine: Mercenary Akula Spearphishing Hits European Finance with Russian Remote Admin Tools Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cybercriminals

Beyond Ukraine: Mercenary Akula Spearphishing Hits European Finance with Russian Remote Admin Tools

Do Son February 27, 2026 0

BlueVoyant uncovers a shift in Mercenary Akula (UAC-0050) tactics, targeting European financial institutions via spoofed judicial lures and RMS malware.

Unmasking 1Campaign: The Professionalized ‘Cloaking’ Service Powering Global Malvertising Scams 1Campaign Cloaking Platform Google Ads Malvertising
  • Cybercriminals

Unmasking 1Campaign: The Professionalized ‘Cloaking’ Service Powering Global Malvertising Scams

Do Son February 27, 2026 0

Varonis uncovers 1Campaign, a sophisticated tool by 'DuppyMeister' that helps hackers bypass Google Ads security to deliver phishing and crypto drainers.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.