
 Do Son
Tenable uncovers "ambar-src," a malicious npm package mimicking "ember-source." It uses preinstall scripts to deploy reverse shells and Apfell malware.
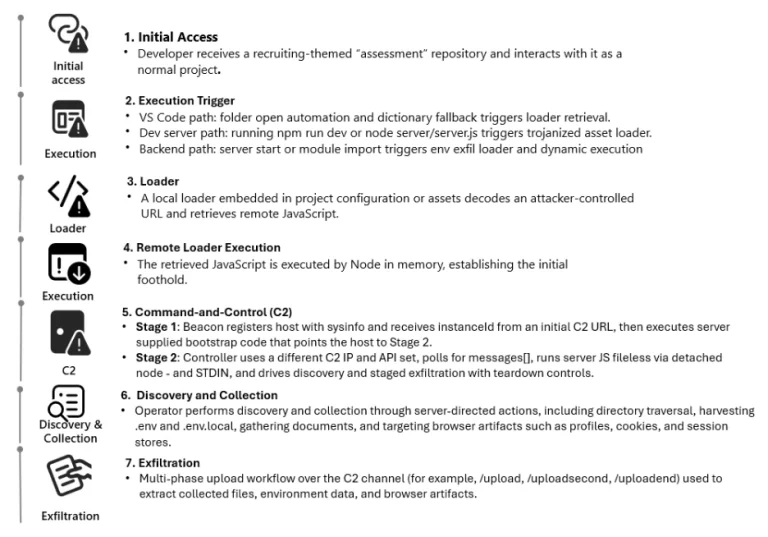
Microsoft warns of a new campaign targeting engineers via fake Next.js technical assessments. Malware hides in VS Code tasks and npm scripts to steal secrets.

Documentation doesn’t usually get much attention. It’s rarely the exciting part of any operation. But when something...

Centreon issues urgent patches for a 9.9 CVSS path traversal and a 9.1 RCE vulnerability in CLAPI. Secure your monitoring infrastructure—update now!
Perplexity Computer Max is here. For $200/month, this "Digital Employee" orchestrates GPT-5.2, Opus 4.6, and Gemini to automate your entire professional workflow.

Gemini 3 turns the Galaxy S26 into a proactive agent. From "Multi-step tasks" that book your Uber to AI scam detection, the Google-Samsung alliance is evolving.

Samsung’s Galaxy S26 series is here. Featuring the "Hey Plex" Perplexity integration, a 200MP f/1.4 camera, and a 6.9-inch Privacy Display on the Ultra.

Apache Superset 6.0.0 addresses high-severity flaws, including a PostgreSQL read-only bypass and dataset access control leaks. Secure your BI platform today!

FreeBSD patches a critical jail escape (CVE-2025-15576) and a kernel heap overflow (CVE-2026-3038). Learn how nullfs and routing sockets put hosts at risk.

n8n patches three critical 9.4 CVSS vulnerabilities (CVE-2026-27497, 27577, 27495) allowing remote code execution via Merge nodes and sandboxes. Update now!

Parse Server patches a critical 9.1 CVSS vulnerability (CVE-2026-27804). Attackers can forge Google tokens using "alg: none" to hijack any linked user account.

ServiceNow patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-0542) in its AI sandbox. Unauthenticated users could execute code remotely. Patch now!
Trend Micro issues a critical patch for Apex One to fix 9.8 severity vulnerabilities (CVE-2025-71210) that allow remote code execution. Update your console now!

NVIDIA warns of three high-severity vulnerabilities (CVE-2025-33179, 33180, 33181) in Cumulus Linux. Low-privileged users can escalate to admin control.

Juniper Networks warns of a critical 9.8 CVSS root vulnerability (CVE-2026-21902) in PTX Series routers. Unauthenticated attackers can gain complete control.


Recorded Future’s Insikt Group warns of a two-year escalation in Russian hybrid warfare. From cyber sabotage to airspace incursions, NATO faces a new doctrine.

Cisco Talos warns of CVE-2026-20127, a CVSS 10 flaw in Catalyst SD-WAN exploited since 2023. UAT-8616 bypassed authentication to hijack global network fabrics.

Threat hunters expose North Korean state actors using Medusa ransomware to fund global espionage. U.S. healthcare and non-profits are the primary targets.

Critical SQL injection flaw (CVE-2026-26198) in ormar Python ORM allows unauthenticated attackers to leak entire databases. Update to version 0.23.0 immediately!

 cybernewswire
Alisa Viejo, CA, United States, 25th February 2026, CyberNewswire

Windows kernel vulnerability CVE-2026-21241 (afd.sys) exposed! A new PoC exploit shows how local attackers can win a race condition to gain SYSTEM privileges.