Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Critical 9.2 Severity Path Traversal Flaw Compromises ASUSTOR FTP Backups Labkotec LID-3300IP CVE-2026-1775 ASUSTOR ADM Vulnerability CVE-2026-3179 Russian Cyberattacks - Security Operations Center
  • Vulnerability Report

Critical 9.2 Severity Path Traversal Flaw Compromises ASUSTOR FTP Backups

Do Son February 25, 2026 0

ASUSTOR patches a critical 9.2 severity flaw (CVE-2026-3179) and a MitM vulnerability in ADM's FTP Backup. Update to version 5.1.2.REO1 now to secure your data.

Accidental Overlord: How a PS5 Controller Mod Unlocked a 7,000-Unit Robot Vacuum Army Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability Report

Accidental Overlord: How a PS5 Controller Mod Unlocked a 7,000-Unit Robot Vacuum Army

Do Son February 25, 2026 0

Hobby coder Sammy Azdoufal used Claude Code to mod his DJI Romo vacuum and accidentally gained control of 7,000 units. Is your smart home watching you?

Apple Shatters Tradition with a Touchscreen OLED MacBook Pro MacBook Pro OLED touch screen MacBook Pro Touchscreen, M6 Chip OLED M5 MacBook Pro, 24-Hour Battery
  • Technology

Apple Shatters Tradition with a Touchscreen OLED MacBook Pro

Do Son February 25, 2026 0

Apple’s 2026 MacBook Pro is a game-changer. Featuring an OLED touchscreen, Dynamic Island, and a touch-adaptive interface, it’s the Mac we were told would never exist.

Google’s $40B Gamble on Water-Free AI Cooling in the Arid Heart of Texas Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

Google’s $40B Gamble on Water-Free AI Cooling in the Arid Heart of Texas

Do Son February 25, 2026 0

Google unveils a "thirstless" AI data center in Texas using Advanced Air-Cooling. Part of a $40B plan, it aims to prove AI can thrive without depleting aquifers.

Fintech Shakeup: Stripe Explores Acquisition of Rival PayPal in $159B Valuation Surge Stripe PayPal acquisition
  • Technology

Fintech Shakeup: Stripe Explores Acquisition of Rival PayPal in $159B Valuation Surge

Do Son February 25, 2026 0

Stripe is reportedly exploring an acquisition of PayPal as its valuation hits $159B. Could this merger redefine the future of global digital payments?

OpenAI Responses API Now Ingests Excel, Word, and PowerPoint Directly ChatGPT advertising US only OpenAI GPT-5.4 launch OpenAI Responses API file support ChatGPT Ads pricing ChatGPT conversational advertising, OpenAI monetization strategy 2026 OpenAI Code Red, ChatGPT Sycophancy Crisis AI music ChatGPT memory, targeted ads ChatGPT User Milestone, Generative AI Adoption ChatGPT ads, AI monetization GPT-5, OpenAI
  • Technology

OpenAI Responses API Now Ingests Excel, Word, and PowerPoint Directly

Do Son February 25, 2026 0

Stop flattening CSVs! The OpenAI Responses API now natively supports Word, Excel, and PowerPoint files for seamless, structure-aware AI analysis.

The Self-Correcting Architect: OpenAI Launches GPT-5.3-Codex to Lead the Agentic Coding Era GPT-5.3-Codex release
  • Technology

The Self-Correcting Architect: OpenAI Launches GPT-5.3-Codex to Lead the Agentic Coding Era

Do Son February 25, 2026 0

OpenAI's GPT-5.3-Codex is here. With 400K context, xhigh reasoning, and self-optimization, it’s the first agentic model designed to build and debug itself.

Workstation in Your Pocket: Claude Code Unveils “Remote Control” for Total Mobile Dev Autonomy Claude Code Remote Control
  • Technology

Workstation in Your Pocket: Claude Code Unveils “Remote Control” for Total Mobile Dev Autonomy

Do Son February 25, 2026 0

Claude Code Remote Control turns your phone into a secure portal to your local workstation. Run terminal commands and modify files anywhere with zero-cloud risk.

27-Year-Old Telnet Flaw Resurfaces to Grant Attackers Instant Root Access shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

27-Year-Old Telnet Flaw Resurfaces to Grant Attackers Instant Root Access

Do Son February 25, 2026 0

Researcher Justin Swartz uncovers a regression of the 1999 telnetd flaw. Remote attackers can bypass authentication and seize root control via environment variables.

Death of the XSS Bug? Firefox 148 Debuts the Sanitizer API to Neutralize Malicious Scripts Firefox built-in VPN Firefox VPN data limit, Firefox VPN countries, Mozilla VPN subscription Sanitizer API Firefox 148 Security Firefox WebRTC Vulnerability CVE-2025-14321 PoC Firefox VPN Feature, Browser-Only VPN Firefox Add-ons Rollback Firefox Encryption Firefox MKV support Firefox ESR, Windows 7
  • Technology

Death of the XSS Bug? Firefox 148 Debuts the Sanitizer API to Neutralize Malicious Scripts

Do Son February 25, 2026 0

Mozilla Firefox 148 launches the standardized Sanitizer API. Discover how the new setHTML() method systematically strips XSS attacks to protect web users.
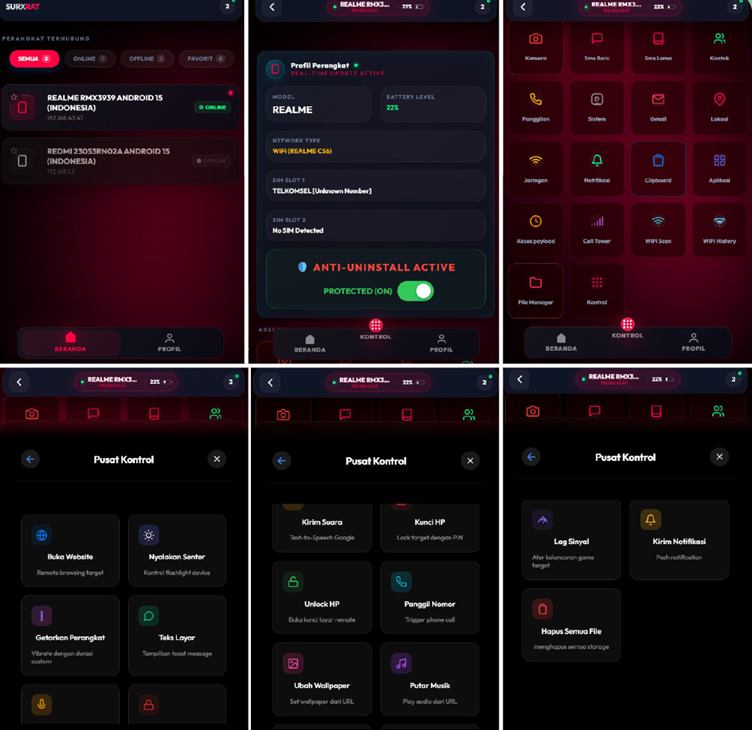
The AI Evolution of Mobile Malware: SURXRAT V5 Combines Surveillance, Ransomware, and LLMs SURXRAT V5 AI-Assisted Android Malware
  • Malware

The AI Evolution of Mobile Malware: SURXRAT V5 Combines Surveillance, Ransomware, and LLMs

Do Son February 25, 2026 0

Cyble Research unmasks SURXRAT V5, a professionalized Android RAT experimenting with AI-assisted modules and hybrid monetization via Firebase infrastructure.

Sanctions and Stolen Secrets: U.S. Cracks Down on ‘Operation Zero’ Exploit Brokerage Operation Zero Exploit Brokers VOLTZITE Threat Group
  • Cyber Security

Sanctions and Stolen Secrets: U.S. Cracks Down on ‘Operation Zero’ Exploit Brokerage

Do Son February 25, 2026 0

US Treasury sanctions Sergey Zelenyuk and Operation Zero for brokering stolen government exploits and selling zero-days to foreign intelligence agencies.

Unpatched ActiveMQ Flaw Leads to Repeat Breach and LockBit Ransomware LockBit 3.0 Ransomware
  • Cybercriminals

Unpatched ActiveMQ Flaw Leads to Repeat Breach and LockBit Ransomware

Do Son February 25, 2026 0

The DFIR Report reveals how a persistent attacker exploited CVE-2023-46604 twice in 18 days to deploy LockBit ransomware. Patch your ActiveMQ servers now!

The High Cost of Free: Cracked Music Plugins Weaponized to Infect macOS with Odyssey Malware Odyssey Malware MacSyncStealer
  • Malware

The High Cost of Free: Cracked Music Plugins Weaponized to Infect macOS with Odyssey Malware

Do Son February 25, 2026 0

Security researchers uncover a massive macOS malware campaign using "cracked" audio plugins and "ClickFix" tactics to deliver Odyssey and MacSyncStealer.
Rooting Out Risk: CISA Warns of Critical 9.1 Severity Flaws in Gardyn Smart Gardening Systems Gardyn Home Kit Vulnerabilities IoT Command Injection Vivotek Vulnerability CVE-2026-22755 Command Injection Ofuji Fishing data breach
  • Vulnerability Report

Rooting Out Risk: CISA Warns of Critical 9.1 Severity Flaws in Gardyn Smart Gardening Systems

Do Son February 25, 2026 0

CISA warns of critical flaws (CVE-2025-29631) in Gardyn Home Kits allowing unauthenticated RCE and admin access. Update your app and firmware immediately!
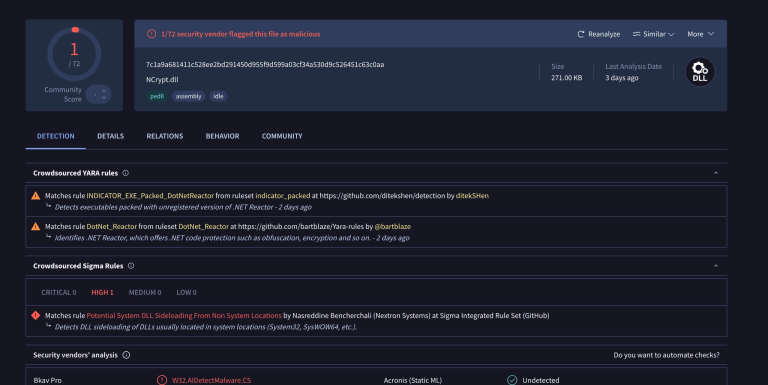
Malicious NuGet Packages Weaponize ASP.NET Identity for Production Backdoors NuGet Supply Chain Attack ASP.NET Identity Theft
  • Malware

Malicious NuGet Packages Weaponize ASP.NET Identity for Production Backdoors

Do Son February 25, 2026 0

Socket researchers uncover a NuGet supply chain attack using "NCryptYo" to hijack ASP.NET apps. Attackers inject backdoors into production authorization layers.

Stealth & Persistence: MuddyWater’s New Rust-Based Payload Mimics Cloudflare and Reddit GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cyber Security
  • Malware

Stealth & Persistence: MuddyWater’s New Rust-Based Payload Mimics Cloudflare and Reddit

Do Son February 25, 2026 0

Genians report reveals MuddyWater APT's shift to Rust-based malware and RMM tool abuse for long-term espionage across government and critical infrastructure.

Total Takeover: Critical Zyxel Flaw (CVSS 9.8) Exposes Routers to Remote Command Injection CVE-2022-43389 - CVE-2024-12398 Zyxel UPnP Vulnerability CVE-2025-13942
  • Vulnerability Report

Total Takeover: Critical Zyxel Flaw (CVSS 9.8) Exposes Routers to Remote Command Injection

Do Son February 25, 2026 0

Zyxel issues urgent patches for a critical 9.8 severity flaw (CVE-2025-13942) in UPnP functions that allows remote attackers to execute OS commands. Patch now!

Sendmarc Releases DMARCbis Fireside Chat Featuring Co-Editor Todd Herr DMARCbis_discussion_press_release_1771937669dXv9v1JLJA
  • Press Release

Sendmarc Releases DMARCbis Fireside Chat Featuring Co-Editor Todd Herr

cybernewswire February 24, 2026 0
Wilmington, North America, 24th February 2026, CyberNewswire
Read More Read more about Sendmarc Releases DMARCbis Fireside Chat Featuring Co-Editor Todd Herr
Root Access Granted: Four Critical RCE Flaws Patched in SolarWinds Serv-U CVE-2024-28075 & CVE-2024-23473 SolarWinds Serv-U RCE CVE-2025-40538
  • Vulnerability Report

Root Access Granted: Four Critical RCE Flaws Patched in SolarWinds Serv-U

Do Son February 24, 2026 0

SolarWinds patches four critical 9.1 CVSS RCE vulnerabilities in Serv-U. Attackers can create admin users and execute code as root. Update to 15.5.4 now!

Critical VMware Aria Operations Flaw Allows RCE During System Upgrades VMware Aria Operations CVE-2026-22719 VMware Fusion - CVE-2024-38811 VMware security, CVE-2025-22247
  • Vulnerability Report

Critical VMware Aria Operations Flaw Allows RCE During System Upgrades

Do Son February 24, 2026 0

Broadcom warns of a high-severity RCE flaw (CVE-2026-22719) in VMware Aria Operations. Attackers can execute commands during system migrations. Patch now!

The Distillation War: Anthropic Accuses DeepSeek and Chinese Rivals of ‘Industrial-Scale’ Data Theft Anthropic confidential IPO filing Anthropic Google $200 billion deal Anthropic Mythos Preview Anthropic Pentagon blacklist Claude Max 20x open-source Model Distillation Anthropic vs DeepSeek Claude Free tier update 2026
  • Technology

The Distillation War: Anthropic Accuses DeepSeek and Chinese Rivals of ‘Industrial-Scale’ Data Theft

Do Son February 24, 2026 0

Anthropic claims DeepSeek and other Chinese AI firms used 24,000 accounts to "pilfer" Claude's data. Inside the high-stakes battle for LLM training secrets.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.