Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Machine-Speed Intrusions: How One Hacker Used DeepSeek and Claude to Scale a Global Campaign Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Cybercriminals

Machine-Speed Intrusions: How One Hacker Used DeepSeek and Claude to Scale a Global Campaign

Do Son February 24, 2026 0

Researcher @goyaramen exposes "ARXON," an AI-automated pipeline using LLMs to manage simultaneous global attacks on Fortinet devices. The future of scale is here.

Chrome Alert: High-Severity Flaws in Media and Tint Engine Trigger Emergency Update Chrome Security Update Use After Free Chrome Security Update Critical Vulnerabilities Chrome Security Update CVE-2026-3062 Chrome Security Update V8 Engine Vulnerability Chrome Security Update CVE-2026-1862 CVE-2026-0628 Chrome 143 Update Chrome Safe Browsing UAF, CVE-2025-11756 Chrome Memory Flaws, CVE-2025-11460 Google Chrome, vulnerability CVE-2025-10200, CVE-2025-10201 Big Sleep CVE-2025-9478 Chrome Update, Security Vulnerabilities
  • Vulnerability Report

Chrome Alert: High-Severity Flaws in Media and Tint Engine Trigger Emergency Update

Do Son February 24, 2026 0

Google releases Chrome v145.0.7632.116 to patch high-severity flaws in Media, DevTools, and the Tint graphics engine. Update now to prevent memory leaks.

Operation Olalampo: MuddyWater Unleashes AI-Assisted Rust Malware and Telegram C2 in MENA Espionage Surge Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cyber Security
  • Malware

Operation Olalampo: MuddyWater Unleashes AI-Assisted Rust Malware and Telegram C2 in MENA Espionage Surge

Do Son February 24, 2026 0

Group-IB exposes Operation Olalampo: MuddyWater's new MENA campaign using AI-assisted Rust malware (CHAR) and Telegram bots for stealthy C2 communication.

No Patch for the EOL: CISA Warns of Critical 9.8 Severity Flaw in USR-W610 IoT Devices shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

No Patch for the EOL: CISA Warns of Critical 9.8 Severity Flaw in USR-W610 IoT Devices

Do Son February 24, 2026 0

CISA warns of critical flaws in EOL USR-W610 IoT servers. CVE-2026-25715 allows full admin control via blank passwords. No patches planned; isolate now.
Silver Fox APT Unleashes ‘Winos 4.0’ Malware via BYOVD Attacks Winos 4.0 Malware Silver Fox APT RapperBot BVIEC cyberattack - CNC group DAMASCENED PEACOCK, malware analysis
  • Malware

Silver Fox APT Unleashes ‘Winos 4.0’ Malware via BYOVD Attacks

Do Son February 24, 2026 0

FortiGuard Labs exposes a massive Silver Fox APT campaign targeting Taiwan. Hackers use tax-themed phishing and BYOVD attacks to deploy Winos 4.0 malware.

Hackers Weaponize Facebook Ads with Fake Windows 11 Updates Fake Windows 11 Ads Info-Stealing Malware
  • Malware

Hackers Weaponize Facebook Ads with Fake Windows 11 Updates

Do Son February 24, 2026 0

Malwarebytes exposes a deceptive campaign using fake Windows 11 Facebook ads to trick users into downloading stealthy info-stealing malware.

Hired to Hack: North Korean Fake IT Workers Hijack Exec Identities in ‘Contagious Interview’ Scams Open VSX Malware String-Fragment Reconstruction DarkCloud Stealer, steganography APT 35 Charming Kitten cyclops
  • Cybercriminals

Hired to Hack: North Korean Fake IT Workers Hijack Exec Identities in ‘Contagious Interview’ Scams

Do Son February 24, 2026 0

GitLab reveals how North Korean fake IT workers use 'Contagious Interview' scams to bypass hiring, steal data, and hijack executive digital identities.

CVE-2026-27212: Critical Swiper Prototype Pollution Flaw (CVSS 9.4) Exposes Global Apps Swiper npm Vulnerability CVE-2026-27212
  • Vulnerability Report

CVE-2026-27212: Critical Swiper Prototype Pollution Flaw (CVSS 9.4) Exposes Global Apps

Do Son February 24, 2026 0

Critical prototype pollution flaw (CVE-2026-27212) in the Swiper npm package allows RCE, DoS, and auth bypass. Update to version 12.1.2 immediately.

First-Ever TPM Sniffing Attack Extracts LUKS Keys from Industrial Linux Devices TPM Sniffing CVE-2026-0714
  • Vulnerability Report

First-Ever TPM Sniffing Attack Extracts LUKS Keys from Industrial Linux Devices

Do Son February 24, 2026 0

Researchers extract LUKS decryption keys in plaintext from Moxa UC-1222A devices via a novel TPM bus sniffing attack (CVE-2026-0714). Secure your hardware.
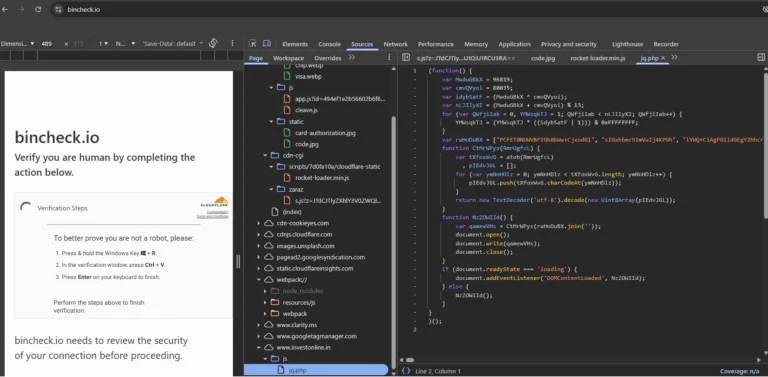
The ‘Human Verification’ Trap: ClickFix Campaign Hijacks Trusted Sites to Deploy MIMICRAT MIMICRAT Malware ClickFix Campaign
  • Malware

The ‘Human Verification’ Trap: ClickFix Campaign Hijacks Trusted Sites to Deploy MIMICRAT

Do Son February 24, 2026 0

Elastic Security Labs uncovers a ClickFix campaign turning human helpfulness into a weapon. Fake verifications deploy the fileless MIMICRAT via PowerShell.

Stargate in Shambles: Sam Altman Abandons the $500B SoftBank Dream for an Oracle “Plan B” OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

Stargate in Shambles: Sam Altman Abandons the $500B SoftBank Dream for an Oracle “Plan B”

Do Son February 23, 2026 0

OpenAI’s $500B Stargate venture has stalled. Sam Altman is now pivoting to a $30B Oracle "Plan B" to survive the brutal 2026 battle for energy and silicon.

“Hey Plex”: Samsung’s Galaxy S26 Challenges Google with a Bold New AI Multi-Agent Universe Galaxy S26 AI Camera Galaxy Unpacked 2026
  • Technology

“Hey Plex”: Samsung’s Galaxy S26 Challenges Google with a Bold New AI Multi-Agent Universe

Do Son February 23, 2026 0

Samsung’s Galaxy S26 debuts a "multi-agent" AI world. Call "Hey Plex" for real-time web search as Samsung Notes and Gallery sync with Perplexity’s brain.

Google Ignites Developer Fury with Mass OpenClaw Ban Wave Chrome hidden weights.bin download Gemini Nano privacy controversy 2026 Google Antigravity account suspension Gemini Lyria 3 integration Google Gemini enterprise sales, Google Cloud AI revenue 2026 Google Gemini daily limits 2026, Gemini Thinking model quotas Google Gemini 3 Agentic Development Platform
  • Technology

Google Ignites Developer Fury with Mass OpenClaw Ban Wave

Do Son February 23, 2026 0

Google has suspended thousands of Antigravity accounts linked to OpenClaw. Paid developers are hitting 403 errors with zero warning. Is your AI workflow safe?

Total Takeover Threat: Critical IceWarp Flaws Trigger Emergency Server Patches shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability

Total Takeover Threat: Critical IceWarp Flaws Trigger Emergency Server Patches

Do Son February 23, 2026 0

IceWarp urges immediate patching for critical flaws allowing unauthorized server access, XSS, and arbitrary file reading. Update your instances today.

Critical Undertow Flaw (CVSS 9.6) Strikes HPE Telco Service Activator CVE-2024-42509 & CVE-2024-47460 HPE Aruba Fabric Composer CVE-2026-23592 Aruba AOS-CX CVE-2026-23813
  • Vulnerability Report

Critical Undertow Flaw (CVSS 9.6) Strikes HPE Telco Service Activator

Do Son February 23, 2026 0

Critical Undertow HTTP server flaw CVE-2025-12543 (CVSS 9.6) impacts HPE Telco Service Activator, allowing cache poisoning and session hijacking. Patch now.
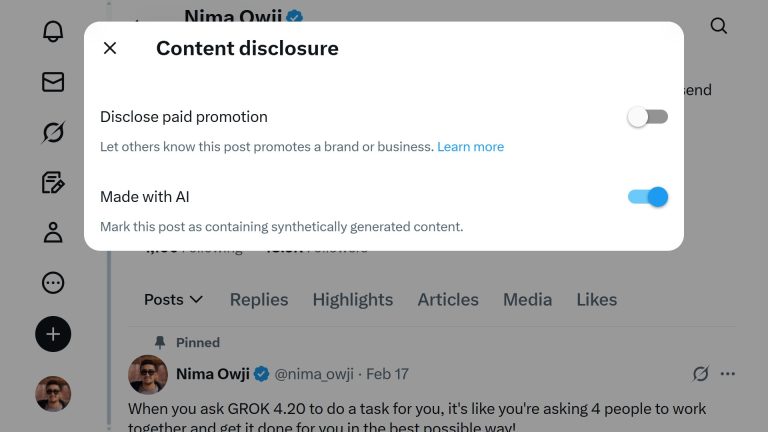
The AI Disclosure: X Trials Mandatory Labels as Community Notes Gets Suspension Power X AI-generated content labels
  • Technology

The AI Disclosure: X Trials Mandatory Labels as Community Notes Gets Suspension Power

Do Son February 23, 2026 0

X is testing a new "AI-Generated" toggle for all posts. Fail to disclose synthetic content, and Community Notes could trigger a permanent account suspension.

The AI Auditor: Anthropic Unveils Claude Code Security to Hunt Flaws Human Eyes Miss Claude Code Security Claude Opus 4.1, AI Model Update Anthropic OpenAI, API Access Revocation Claude AI, Rate Limits Claude Memory, AI Personalization Claude 4 whistleblowing, AI ethical risks
  • Technology

The AI Auditor: Anthropic Unveils Claude Code Security to Hunt Flaws Human Eyes Miss

Do Son February 23, 2026 0

Anthropic's Claude Code Security moves beyond pattern matching to "reason" through code, unearthing 500+ vulnerabilities missed by decades of human review.

Crimson Comeback: Apple Tests a “Deep Red” iPhone 18 Pro as the iPhone Fold Goes Minimalist FCC Chinese lab ban iPhone NATO certification iPhone 18 Pro Deep Red iOS 27 Snow Leopard update 2026 smartphone memory shortage, IDC mobile market forecast iPhone Satellite Natural Usage iPhone 17 Speaker Issue, USB-C Static iPhone 17 Pro, MagSafe Scratches iPhone 17 Pro, professional filmmaking
  • Technology

Crimson Comeback: Apple Tests a “Deep Red” iPhone 18 Pro as the iPhone Fold Goes Minimalist

Do Son February 23, 2026 0

Apple is testing a "Deep Red" finish for the iPhone 18 Pro to follow Cosmic Orange's success. Meanwhile, the iPhone Fold sticks to classic Black and White.
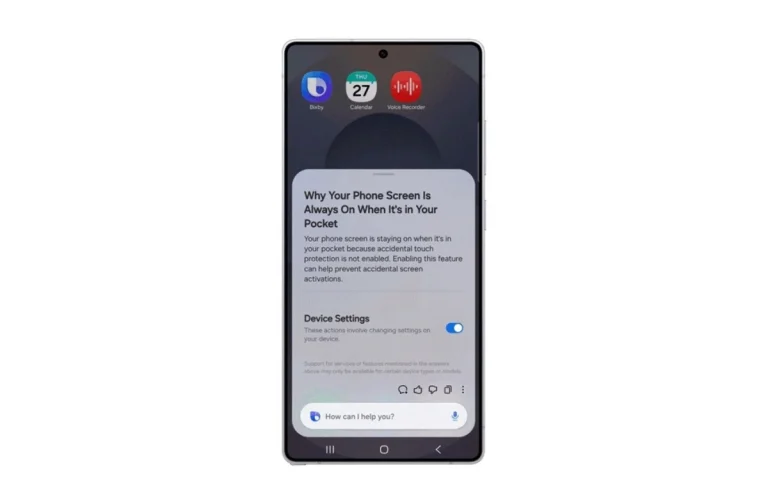
The Bixby Redemption: Samsung Unveils a “Conversational Agent” to End Menu-Diving Forever Samsung Bixby One UI 8.5
  • Android

The Bixby Redemption: Samsung Unveils a “Conversational Agent” to End Menu-Diving Forever

Do Son February 23, 2026 0

Bixby is back! The One UI 8.5 beta transforms Bixby into a Conversational Agent that understands natural language and controls your phone without menu-diving.

The Face of ChatGPT: Inside Jony Ive’s $300 Smart Speaker that Watches and Advises OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Technology

The Face of ChatGPT: Inside Jony Ive’s $300 Smart Speaker that Watches and Advises

Do Son February 23, 2026 0

Jony Ive and OpenAI are building a camera-equipped smart speaker for 2027. Discover the $6.5B design deal bringing "Face ID" and visual AI into your home.

Interactive Cinema: YouTube Brings Gemini-Powered “Ask” AI to the Biggest Screen in Your House YouTube TV Gemini Ask YouTube TV Bundles, Streaming Cable Model
  • Technology

Interactive Cinema: YouTube Brings Gemini-Powered “Ask” AI to the Biggest Screen in Your House

Do Son February 23, 2026 0

YouTube’s Gemini "Ask" feature hits smart TVs and consoles! Ask voice questions about recipes or lyrics without pausing. The passive TV era is officially over.
Nurturing the Giants: Inside NVIDIA’s “Inception” Strategy to Capture India’s AI Boom NVIDIA India AI startups
  • Technology

Nurturing the Giants: Inside NVIDIA’s “Inception” Strategy to Capture India’s AI Boom

Do Son February 23, 2026 0

NVIDIA is playing the long game in India. By partnering with the $75M Activate fund, they are locking in the next generation of AI giants before they even exist.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.