Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Hackers Exploit Critical BeyondTrust Flaw to Deploy VShell and SparkRAT Across Multiple Sectors BeyondTrust Vulnerability CVE-2026-1731 UPBIT $369M Hack CVE-2024-55591 Ivanti VPN vulnerability, cyber espionage
  • Malware
  • Vulnerability Report

Hackers Exploit Critical BeyondTrust Flaw to Deploy VShell and SparkRAT Across Multiple Sectors

Do Son February 23, 2026 0

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.

Poisoned Pages: Critical Calibre Path Traversal Flaws Expose Readers to RCE Calibre Vulnerability CVE-2026-26065 Calibre RCE, FB2 File Flaw
  • Vulnerability Report

Poisoned Pages: Critical Calibre Path Traversal Flaws Expose Readers to RCE

Do Son February 23, 2026 0

Critical path traversal flaws (CVE-2026-26065, CVE-2026-26064) in the Calibre e-book manager allow RCE via malicious PDB and ODT files. Update to 9.3.0.
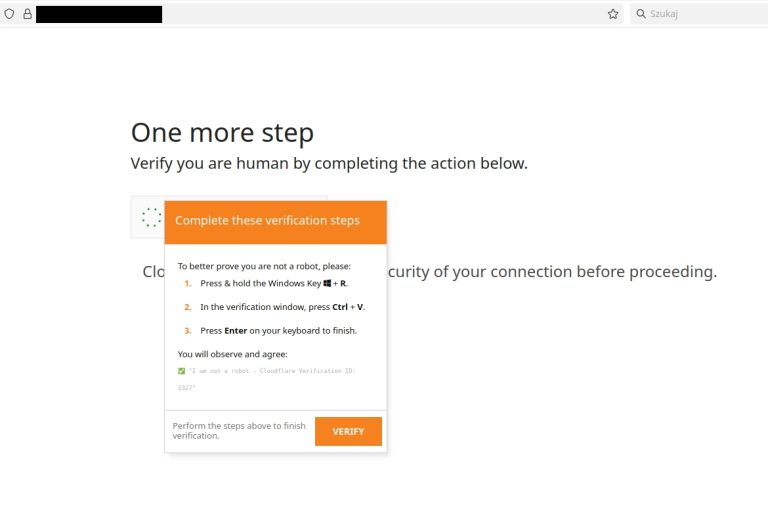
The CAPTCHA Trap: How a Fake “ClickFix” Prompt Unleashed Latrodectus & Supper Malware ClickFix CAPTCHA Latrodectus Malware
  • Malware

The CAPTCHA Trap: How a Fake “ClickFix” Prompt Unleashed Latrodectus & Supper Malware

Do Son February 23, 2026 0

CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.
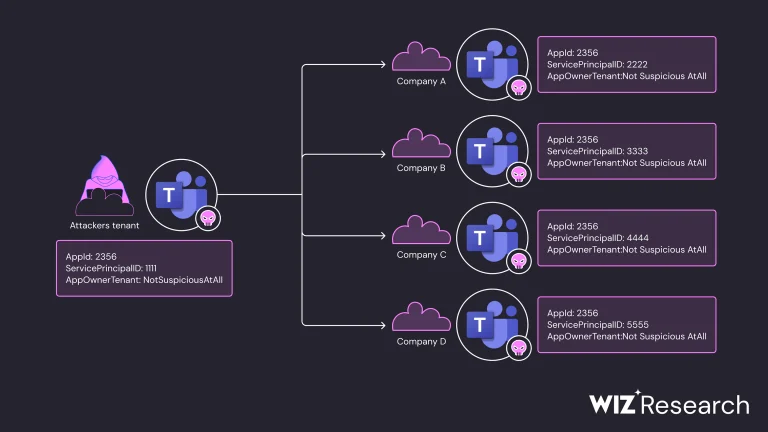
The Invisible Backdoor: AI Exposes Malicious OAuth Apps Hiding in Microsoft Entra ID Malicious OAuth Apps Entra ID Homoglyph Attack
  • Cybercriminals

The Invisible Backdoor: AI Exposes Malicious OAuth Apps Hiding in Microsoft Entra ID

Do Son February 23, 2026 0

Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.
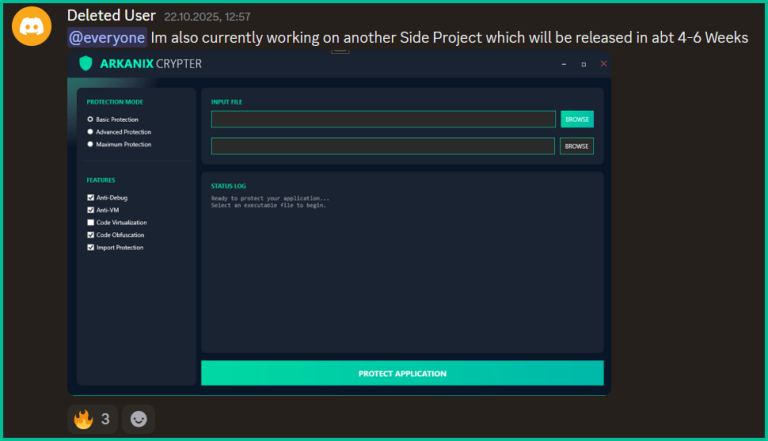
The Startup Stealer: How AI and Discord Powered the Arkanix MaaS Operation Arkanix Stealer Malware-as-a-Service (MaaS)
  • Malware

The Startup Stealer: How AI and Discord Powered the Arkanix MaaS Operation

Do Son February 23, 2026 0

Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
Cash Out: FBI Warns of $20M ATM ‘Jackpotting’ Surge Driven by Ploutus Malware ATM Jackpotting Ploutus Malware
  • Malware

Cash Out: FBI Warns of $20M ATM ‘Jackpotting’ Surge Driven by Ploutus Malware

Do Son February 23, 2026 0

The FBI warns of a massive surge in ATM jackpotting attacks. Cybercriminals are using Ploutus malware to bypass the XFS layer and drain cash reserves.
The ‘ClickFix’ Trap: GrayCharlie Hijacks US Law Firms to Deploy NetSupport RAT GrayCharlie Malware ClickFix Attack
  • Malware

The ‘ClickFix’ Trap: GrayCharlie Hijacks US Law Firms to Deploy NetSupport RAT

Do Son February 23, 2026 0

Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.

Sandbox Bypassed: jsPDF Flaw Exposes Millions to Object Injection CVE-2026-31938 jsPDF Vulnerability CVE-2026-25755 jsPDF, CVE-2025-68428 jsPDF Vulnerability CVE-2026-24133
  • Vulnerability Report

Sandbox Bypassed: jsPDF Flaw Exposes Millions to Object Injection

Do Son February 23, 2026 0

A critical PDF Object Injection flaw (CVE-2026-25755) in jsPDF allows attackers to bypass AcroJS sandboxes. Update to version 4.2.0 immediately.
The Fake IT Threat: “TrustConnect” Malware-as-a-Service Masquerades as Legitimate RMM Software TrustConnect Malware Fake RMM MaaS
  • Cybercriminals

The Fake IT Threat: “TrustConnect” Malware-as-a-Service Masquerades as Legitimate RMM Software

Do Son February 23, 2026 0

Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

Weaponizing Windows Errors: PoC Dropped for Critical Privilege Escalation Flaw in WER Service C Windows SecureBoot folder KB5089549 Windows 11 BSOD Microsoft Windows, Rust programming WINS Service Deprecation Windows Server DNS Migration Windows Driver Standard OEM Kernel Privileges Windows Agentic OS Task Manager Bug, Windows 11 Performance Windows 11, Microsoft, WinRE, Update Bug, Tech Support Windows 11 OOBE, Microsoft Account Mandatory Windows 11, SSD failures Windows 11 Recovery, Black Screen of Death Windows 11 Update Issue, KB5062324 Windows 11, Indicator Bar
  • Vulnerability

Weaponizing Windows Errors: PoC Dropped for Critical Privilege Escalation Flaw in WER Service

Do Son February 23, 2026 0

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.

Industrialized Theft: GoldFactory Malware Hijacks Tax Season via Fake ‘Coretax’ Apps Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cybercriminals

Industrialized Theft: GoldFactory Malware Hijacks Tax Season via Fake ‘Coretax’ Apps

Do Son February 23, 2026 0

Group-IB exposes an industrialized mobile banking fraud campaign in Indonesia. GoldFactory hackers use fake Coretax apps and Gigabud.RAT to drain accounts.
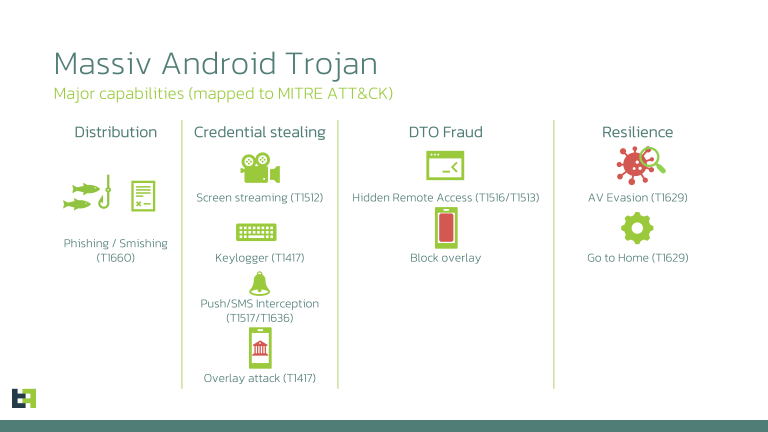
Streaming Fraud: “Massiv” Android Trojan Uses Fake IPTV Apps for Complete Device Takeover Massiv Android Malware IPTV Banking Trojan
  • Malware

Streaming Fraud: “Massiv” Android Trojan Uses Fake IPTV Apps for Complete Device Takeover

Do Son February 23, 2026 0

ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.

Maintaining the critical minimum through energy monitoring during storm disruptions CVE-2024-31070 & CVE-2024-36491
  • Technique

Maintaining the critical minimum through energy monitoring during storm disruptions

Do Son February 21, 2026 0

Technical analysis of energy monitoring and load prioritization strategies for maintaining smart home stability during grid outages.

Inside the ‘Upworksell’ Syndicate: Hacker Gets 60 Months for Funneling US Tech Jobs to North Korea Romanian hacker sentenced identity theft conviction Pig-Butchering Crackdown Operation Level Up Oleksandr Didenko North Korean IT Workers Coinbase TaskUs insider breach, Hyderabad police Coinbase arrest Scattered Spider, Cybercrime Scattered Spider group
  • Cybercriminals

Inside the ‘Upworksell’ Syndicate: Hacker Gets 60 Months for Funneling US Tech Jobs to North Korea

Do Son February 20, 2026 0

Ukrainian hacker Oleksandr Didenko receives a 60-month sentence for orchestrating a massive laptop farm scheme aiding North Korean IT operatives.

Exploited in the Wild & PoC Disclosed: Emergency Chrome Zero-Day (CVE-2026-2441) Patched Chrome security update exploit in the wild Chrome Zero-Day CVE-2026-3909 Chrome Zero-Day PoC CVE-2026-2441 Chrome Zero-Day CVE-2026-2441 Chrome Zero-Day, Active Exploitation CVE-2025-10585 Chrome vulnerability, zero-day exploit CVE-2025-6558 Chrome Zero-Day, V8 Vulnerability Chrome Zero-Day, Security Update
  • Vulnerability Report

Exploited in the Wild & PoC Disclosed: Emergency Chrome Zero-Day (CVE-2026-2441) Patched

Do Son February 20, 2026 0

Google patches Chrome zero-day CVE-2026-2441, an actively exploited memory flaw. With PoC exploit code now publicly disclosed, update to v145 immediately.

Bypassing the Bouncer: Apache Tomcat Patches SNI & Legacy Protocol Flaws Tomcat Security Update CVE-2026-24733 CVE-2023-41081 -CVE-2024-56337
  • Vulnerability Report

Bypassing the Bouncer: Apache Tomcat Patches SNI & Legacy Protocol Flaws

Do Son February 20, 2026 0

Apache Tomcat rolls out urgent updates for versions 9, 10, and 11 to fix legacy HTTP/0.9 protocol confusion and SNI certificate bypass flaws. Patch now.

The Dev Environment Trap: 128 Million Users at Risk as Top VS Code Extensions Unmask Critical Flaws VS Code extension vulnerabilities 2026
  • Vulnerability Report

The Dev Environment Trap: 128 Million Users at Risk as Top VS Code Extensions Unmask Critical Flaws

Do Son February 20, 2026 0

Critical flaws in Live Server, Code Runner, and more expose 128M+ developers to file theft and remote code execution. Is your VS Code workspace secure?

Google Unveils Gemini 3.1 Pro with 1 Million Tokens for Deep-Data Mastery Google Gemini Pentagon deal Google AI Pro 5TB storage Gemini 3.1 Pro launch
  • Technology

Google Unveils Gemini 3.1 Pro with 1 Million Tokens for Deep-Data Mastery

Do Son February 20, 2026 0

Google debuts Gemini 3.1 Pro! With a 1M token context window and native multi-modal power, it’s the new gold standard for complex analysis and big data.
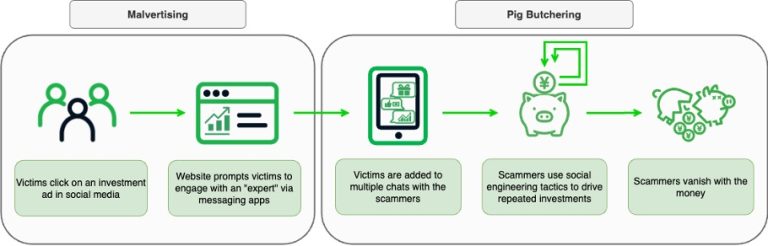
Infoblox Exposes Hybrid Malvertising & “Pig Butchering” Scam Hybrid Crypto Scam Pig Butchering Malvertising
  • Cybercriminals

Infoblox Exposes Hybrid Malvertising & “Pig Butchering” Scam

Do Son February 20, 2026 0

Infoblox Threat Intel exposes a highly scalable hybrid scam merging automated malvertising with "pig butchering" to drain global crypto investors' funds.

PoC Publicly Disclosed: Critical Grandstream VoIP Flaw (CVSS 9.3) Grants Stealthy Root Access Grandstream VoIP Zero-Day CVE-2026-2329 PoC
  • Vulnerability Report

PoC Publicly Disclosed: Critical Grandstream VoIP Flaw (CVSS 9.3) Grants Stealthy Root Access

Do Son February 20, 2026 0

Rapid7 publicly discloses a critical zero-day and PoC (CVE-2026-2329) for Grandstream GXP1600 VoIP phones allowing remote root access. Patch now.

Trojan Routers: Texas Sues TP-Link Over Alleged CCP Surveillance and Supply Chain Deception TP-Link Lawsuit CCP Surveillance
  • Malware

Trojan Routers: Texas Sues TP-Link Over Alleged CCP Surveillance and Supply Chain Deception

Do Son February 20, 2026 0

Texas AG Ken Paxton sues TP-Link, alleging the Wi-Fi giant's routers act as Trojan horses for CCP surveillance. State bans TP-Link gear for employees.
How to Secure Multiple Bybit Accounts Without Triggering Suspicious Activity Flags CVE-2025-20059
  • Technique

How to Secure Multiple Bybit Accounts Without Triggering Suspicious Activity Flags

Do Son February 20, 2026 0
In the increasingly regulated world of crypto derivatives, managing multiple exchange accounts has become a common practice....
Read More Read more about How to Secure Multiple Bybit Accounts Without Triggering Suspicious Activity Flags
❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.