Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
New Offensive OT Framework Targeting Energy Infrastructure Emerges on Dark Web ICS Offensive Framework APT IRAN
  • Cybercriminals

New Offensive OT Framework Targeting Energy Infrastructure Emerges on Dark Web

Do Son February 2, 2026 0

New "APT IRAN" framework targets energy grids & military networks. Lab52 links the tool to the IRGC. See the threat to critical infrastructure.

Silent Intruder: “EncystPHP” Web Shell Burrows into FreePBX Systems EncystPHP Web Shell FreePBX Vulnerability
  • Cybercriminals
  • Vulnerability Report

Silent Intruder: “EncystPHP” Web Shell Burrows into FreePBX Systems

Do Son February 2, 2026 0

INJ3CTOR3 hackers target FreePBX with EncystPHP web shell via CVE-2025-64328. Malware uses cron jobs for persistence. Patch immediately.

“Exfil Out&Look” Flaw Lets Spies Steal Emails via OWA Undetected Exfil Out&Look Microsoft 365 Logging Gap Outlook Classic KB5074109 freeze, January 2026 POP3 PST bug Outlook Classic POP3 freeze, KB5074109 Windows 11 bug Outlook, CPU Usage Outlook lag Outlook Lite discontinued
  • Vulnerability Report

“Exfil Out&Look” Flaw Lets Spies Steal Emails via OWA Undetected

Do Son February 2, 2026 0

New "Exfil Out&Look" attack uses OWA add-ins to steal emails without leaving logs. Microsoft has no immediate fix for this blind spot.

Hidden in Plain Sight: TA584 Deploys “Tsundere Bot” & Invisible Registry Keys TA584 Tsundere Bot Invisible Registry Persistence
  • Cybercriminals

Hidden in Plain Sight: TA584 Deploys “Tsundere Bot” & Invisible Registry Keys

Do Son February 2, 2026 0

TA584 triples activity with new "Tsundere Bot" malware. Attackers use invisible Registry keys to hide persistence. Read the Proofpoint analysis.
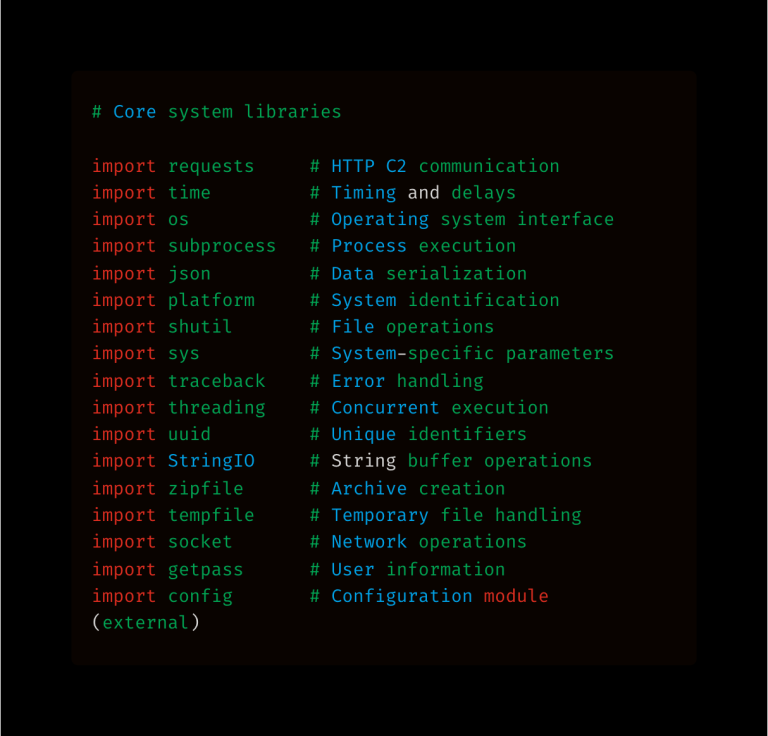
Wrapped in Stealth: Python RAT Hides Inside ELF Binary to Evade Detection Python-based RAT Adaptive Beaconing
  • Malware

Wrapped in Stealth: Python RAT Hides Inside ELF Binary to Evade Detection

Do Son February 2, 2026 0

K7 Labs uncovers a stealthy Python-based RAT disguised as an ELF binary. Features adaptive beaconing and anti-forensics to stay hidden. Read the analysis.

AI-Coded Malware: Vietnamese “Huna” Actor Targets Job Seekers with PureRAT AccountDumpling Phishing Google AppSheet Abuse AI-Generated Malware PureRAT Campaign RondoDoX Botnet, Next.js React2Shell EchoGather, Paper Werewolf Salt Typhoon, Telecom Espionage BreachForums, Conor Fitzpatrick Ransomware Negotiation, DOJ Investigation MirrorFace group - Earth Kasha Emperor Dragonfly
  • Malware

AI-Coded Malware: Vietnamese “Huna” Actor Targets Job Seekers with PureRAT

Do Son February 2, 2026 0

New AI-generated malware campaign targets job seekers. Vietnamese actor "Huna" uses fake job offers to deliver PureRAT via Dropbox.

EdTech startups and the role of LMS in their growth tech
  • Technique

EdTech startups and the role of LMS in their growth

Do Son January 31, 2026 0
What are EdTech startups? EdTech startups are typically presented as young tech companies that build digital products...
Read More Read more about EdTech startups and the role of LMS in their growth
VPNs & Fake Updates: Google Dismantles Massive IPIDEA Proxy Network IPIDEA Proxy Network Residential Proxy Disruption
  • Cybercriminals

VPNs & Fake Updates: Google Dismantles Massive IPIDEA Proxy Network

Do Son January 31, 2026 0

Google disrupts IPIDEA proxy network. Fake VPNs and hijacked apps turned millions of devices into unwitting exit nodes. Play Protect is removing them.

From User to SYSTEM: PoC Released for Zabbix Privilege Escalation CVE-2024-42330 Zabbix Privilege Escalation CVE-2025-27237
  • Vulnerability

From User to SYSTEM: PoC Released for Zabbix Privilege Escalation

Do Son January 30, 2026 0

Exploit code released for Zabbix flaw CVE-2025-27237. Low-level users can gain SYSTEM privileges on Windows via OpenSSL config. Update now.

“Update” to Nightmare: eScan Antivirus Hacked to Distribute Malware TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

“Update” to Nightmare: eScan Antivirus Hacked to Distribute Malware

Do Son January 30, 2026 0

Critical supply chain attack hits eScan antivirus. Hackers hijacked updates to install malware and disable the AV. Manual patch required.

Smart Buildings at Risk: Critical Johnson Controls Flaw (CVSS 10) Allows Remote SQL Injection shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Smart Buildings at Risk: Critical Johnson Controls Flaw (CVSS 10) Allows Remote SQL Injection

Do Son January 30, 2026 0

CISA warns of CVSS 10 flaw CVE-2025-26385 in Johnson Controls Metasys. Remote SQL execution possible. Patch now or close TCP port 1433.

Exploited in the Wild: Critical Ivanti EPMM RCE Flaws (CVSS 9.8) Under Attack Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Vulnerability Report

Exploited in the Wild: Critical Ivanti EPMM RCE Flaws (CVSS 9.8) Under Attack

Do Son January 30, 2026 0

Ivanti confirms critical EPMM RCE flaws (CVE-2026-1281) are exploited in the wild. Unauthenticated attackers can compromise MDM. Patch immediately.

Cluster Admin for All: Critical Kyverno Flaw (CVSS 10) Shatters Isolation Kyverno SSRF Kubernetes Policy Engine Kyverno Privilege Escalation CVE-2026-22039
  • Vulnerability Report

Cluster Admin for All: Critical Kyverno Flaw (CVSS 10) Shatters Isolation

Do Son January 30, 2026 0

Critical Kyverno flaw CVE-2026-22039 (CVSS 10) allows policy creators to gain cluster admin rights. Update to v1.16.3 to fix privilege escalation & DoS.

“SessionReaper” Harvests Roots: Mass Exploitation Campaign Hits Over 200 Magento Sites FortiClient EMS exploitation Cisco FIRESTARTER Backdoor Arcane Door Campaign Dell RecoverPoint Zero-Day UNC6201 Espionage Notepad++ Compromise Supply Chain Attack Magento SessionReaper CVE-2025-54236 ShadowRay 2.0, AI-Generated Malware WordPress Auth Bypass, CVE-2025-5947 Exploited EcoStruxure Vulnerabilities, Industrial Control System UNC5820 - CVE-2014-2120 - CVE-2021-44207
  • Cybercriminals
  • Vulnerability Report

“SessionReaper” Harvests Roots: Mass Exploitation Campaign Hits Over 200 Magento Sites

Do Son January 30, 2026 0

"SessionReaper" (CVE-2025-54236) targets Magento stores. Attackers use zombie tokens to gain root access. 200+ sites compromised. Patch now.
Scam Alert: “Amazon Ads Blocker” Extension Hijacks Creator Commissions Amazon Ads Blocker Affiliate Link Hijacking Malicious browser extensions
  • Cybercriminals

Scam Alert: “Amazon Ads Blocker” Extension Hijacks Creator Commissions

Do Son January 30, 2026 0

"Amazon Ads Blocker" extension exposed for stealing creator revenue. It hijacks affiliate links to divert commissions to the developer. Uninstall it now.

Guest-to-Host Escape: NVIDIA Patches Critical vGPU & Driver Flaws NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Vulnerability Report

Guest-to-Host Escape: NVIDIA Patches Critical vGPU & Driver Flaws

Do Son January 30, 2026 0

NVIDIA patches high-severity flaws (CVE-2025-33217) in GPU drivers & vGPU software. Flaws allow code execution. Update Windows/Linux drivers now.
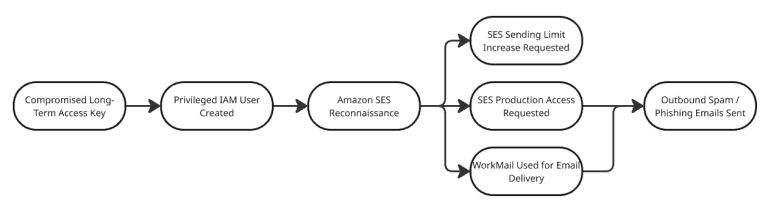
The “WorkMail Pivot”: Hackers Abuse AWS WorkMail to Bypass SES Sandbox AWS WorkMail Abuse SES Sandbox Bypass
  • Cybercriminals

The “WorkMail Pivot”: Hackers Abuse AWS WorkMail to Bypass SES Sandbox

Do Son January 30, 2026 0

Attackers are bypassing AWS SES sandbox limits by pivoting to WorkMail. Rapid7 reveals how this abuse creates a blind spot for defenders.

The Great Recalibration: Amazon Cuts 16,000 More Roles in Massive Shift to AI-First Future Motorola Smart Feed redirect Anthropic Amazon 5GW partnership Amazon Perplexity lawsuit AWS-LC Vulnerabilities Cryptographic Bypass AWS Middle East drone strikes Amazon layoffs 2026, Amazon AI restructuring Amazon Kindle DRM Policy, Publisher Control EPUB AWS Nova Forge AI Model Customization AWS Trainium3 EC2 Trn3 UltraServer Route 53 Accelerated Recovery AWS DNS Resilience AI Browser War, Amazon Comet Amazon layoffs, cost reduction AWS outage, DynamoDB DNS AWS outage, cloud dependency AWS VPN Client, Root Privilege Escalation WSA shutdown, Amazon Appstore Amazon Wondery, Podcast Restructuring Amazon Q2 2025 Generative AI AWS Client VPN, Privilege Escalation Amazon AI, Wearable AI
  • Technology

The Great Recalibration: Amazon Cuts 16,000 More Roles in Massive Shift to AI-First Future

Do Son January 30, 2026 0

Amazon confirms 16,000 new layoffs in Jan 2026, completing a 30,000-person cut. Discover how the titan is swapping managers for Generative AI tech.

The AI Squeeze: NVIDIA Overtakes Apple as TSMC’s Top Revenue Source NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Technology

The AI Squeeze: NVIDIA Overtakes Apple as TSMC’s Top Revenue Source

Do Son January 30, 2026 0

NVIDIA replaces Apple as TSMC's largest customer in Jan 2026. Discover how the $33B AI chip boom is rewriting the rules of the silicon industry.

The Fake Region Block: YouTube’s Cryptic New War on Ad-Blockers YouTube ad block content unavailable 2026, YouTube regional restriction bypass YouTube Collaboration, Creator Features YouTube Shorts, AI Video Generation
  • Technology

The Fake Region Block: YouTube’s Cryptic New War on Ad-Blockers

Do Son January 30, 2026 0

YouTube is faking regional blocks to break ad-blockers in Jan 2026! Discover the "technical frustration" strategy behind the new "unavailable" errors.

Locked Out of the Crate: Microsoft’s “Smart” Security Cripples ASUS ROG Ally Smart App Control blocking Armoury Crate, ROG Ally Defender false positive 2026 Microsoft Zero-Day, Cloud Files UAF Microsoft Access end of life CVE-2025-21298 Azure Vulnerabilities
  • Windows

Locked Out of the Crate: Microsoft’s “Smart” Security Cripples ASUS ROG Ally

Do Son January 29, 2026 0

Microsoft Defender's Smart App Control is blocking ASUS Armoury Crate in Jan 2026. Learn why your ROG Ally controls are broken and how to fix it.
The Final Hang-Up: Microsoft Disables Legacy Modem Drivers for Security Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

The Final Hang-Up: Microsoft Disables Legacy Modem Drivers for Security

Do Son January 29, 2026 0

Windows 11 intentionally kills dial-up modems in Jan 2026! Discover why Microsoft removed Agere and Motorola drivers to fix critical security flaws.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102940CVSS 9.6
    OpenEMR is a free and open source electronic health records and medical practice management application. Prior to 8.4.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-123279CVSS 9.0
    In JetBrains Datalore before 2026.4 code execution was possible in a notebook's computation by view-only collaborators
    📅 Updated: Nov 6, 2026
  • CVE-2026-123294CVSS 9.6
    In JetBrains Hub before 2026.2.52556 privilege escalation was possible by changing email authentication details during the verification flow
    📅 Updated: Nov 6, 2026
  • CVE-2026-123831CVSS 9.6
    In JetBrains CLion before 2026.2, 2026.1.4 code execution was possible in Safe Mode via Meson project settings
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.