Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The 13-Year Lifeline: Apple Updates the iPhone 5s to Save iMessage Apple iOS 12.5.8 certificate update, iPhone 5s legacy support 2026 CVE-2022-42856 vulnerability
  • Technology

The 13-Year Lifeline: Apple Updates the iPhone 5s to Save iMessage

Do Son January 29, 2026 0

Apple released iOS 12.5.8 in Jan 2026. This critical update extends iMessage and FaceTime support for the 13-year-old iPhone 5s until 2027.

The $40M Insider Heist: Son of Federal Contractor Investigated for Seized Crypto Theft CMDSS ZachXBT crypto theft, John Daghita U.S. Marshals investigation Bitfinex Hacker - DMM Bitcoin Cyberattack
  • Cybercriminals

The $40M Insider Heist: Son of Federal Contractor Investigated for Seized Crypto Theft

Do Son January 29, 2026 0

ZachXBT unmasks an alleged $40M theft of U.S. government crypto in Jan 2026. The suspect? The son of the USMS contractor hired to protect it.

SolarWinds Web Help Desk Hit with Multiple RCE and Auth Bypass Vulnerabilities CVE-2024-23476 & CVE-2024-23479 SolarWinds Web Help Desk Unauthenticated RCE
  • Vulnerability Report

SolarWinds Web Help Desk Hit with Multiple RCE and Auth Bypass Vulnerabilities

Do Son January 28, 2026 0

Critical SolarWinds Web Help Desk flaws (CVSS 9.8) allow unauthenticated RCE and auth bypass. Hardcoded credentials also found. Patch immediately.

Beyond ChromeOS: Google’s “Aluminum OS” Desktop Android Leaks Online Android CLI Android Security Zero-Interaction DoS CVE-2026-21385 Android Security Update UK CMA Apple Google regulation Google Aluminum OS Android 16 leak, ALOS Android ChromeOS merger Android sideloading certification 2026, Google developer verification APK Android AOSP biannual release, AOSP source code latency 2026 Android Zero-Day, Critical DoS Flaw Android Universal Clipboard Cross-Device Sync Gemini Nano Block, Unlocked Bootloader Android, Calling Cards Android Security Bulletin, RCE Vulnerability Android Linux GUI, Debian VM Android System Services, Google Transparency Android 16, Pixel Update
  • Android

Beyond ChromeOS: Google’s “Aluminum OS” Desktop Android Leaks Online

Do Son January 28, 2026 0

Google's secret Aluminum OS leaked in Jan 2026! See the first visual evidence of the Android 16 desktop merger and its deep Gemini AI integration.

Labels for Machines: Google Proposes ai-disclosure Tags for Every Web Element Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

Labels for Machines: Google Proposes ai-disclosure Tags for Every Web Element

Do Son January 28, 2026 0

Google proposes the ai-disclosure tag in Jan 2026. Discover how this new Chrome standard will label AI-generated text across the web.

AI for All: Google Launches $7.99 AI Plus Tier with Gemini 3 Pro Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

AI for All: Google Launches $7.99 AI Plus Tier with Gemini 3 Pro

Do Son January 28, 2026 0

Google launches AI Plus for $7.99 in Jan 2026. Get Gemini 3 Pro, Nano Banana Pro, and 200GB storage at half the price of AI Pro.

The Egress Explosion: Google Cloud to Double Interconnect Prices in May 2026 Railway app Google Cloud suspension Google Cloud CDN Interconnect pricing 2026, GCP data transfer cost increase Google Cloud Disrupted ImageRunner Alphabet earnings, Google AI
  • Technology

The Egress Explosion: Google Cloud to Double Interconnect Prices in May 2026

Do Son January 28, 2026 0

Google Cloud will double CDN Interconnect and Peering rates on May 1, 2026. Discover how the 100% price hike impacts Cloudflare and your cloud bill.

Pivoting the Pin: Pinterest Cuts 15% of Staff to Fuel AI Ambitions Pinterest AI layoffs 2026, Pinterest workforce reduction 15% OpenAI Pinterest acquisition 2026, multimodal AI training data Pinterest Assistant, AI Search, Visual Discovery
  • Technology

Pivoting the Pin: Pinterest Cuts 15% of Staff to Fuel AI Ambitions

Do Son January 28, 2026 0

Pinterest announced a 15% layoff in Jan 2026. Discover how the visual discovery platform is pivoting 700+ jobs into an aggressive AI-forward strategy.

Sandbox Shattered: Critical n8n Flaw (CVSS 9.9) Allows Remote Code Execution n8n Node RCE Vulnerabilities CVE-2026-44791 Prototype Pollution n8n RCE Vulnerabilities CVE-2026-27497 CVE-2026-25053 n8n RCE Vulnerability CVE-2026-21877 n8n RCE, CVE-2025-68613 n8n Git RCE, core.hooksPath Exploit
  • Vulnerability Report

Sandbox Shattered: Critical n8n Flaw (CVSS 9.9) Allows Remote Code Execution

Do Son January 28, 2026 0

Critical n8n RCE (CVE-2026-1470) lets attackers bypass sandbox defenses via malicious expressions. CVSS 9.9. Check versions 1.123.17 & 2.x now.

HPE Aruba Patches High-Severity RCE and OpenSSL Flaws CVE-2024-42509 & CVE-2024-47460 HPE Aruba Fabric Composer CVE-2026-23592 Aruba AOS-CX CVE-2026-23813
  • Vulnerability Report

HPE Aruba Patches High-Severity RCE and OpenSSL Flaws

Do Son January 28, 2026 0

HPE patches critical RCE (CVE-2026-23592) in Fabric Composer. Authenticated attackers can seize the OS via backup tools. Update to v7.3.0 immediately.

Snatch-and-Run Stopped: Android’s New AI Locks Stolen Phones Instantly Android Theft Protection Theft Detection Lock
  • Android

Snatch-and-Run Stopped: Android’s New AI Locks Stolen Phones Instantly

Do Son January 28, 2026 0

New Android anti-theft updates use AI to detect "snatch-and-run" theft and instantly lock your screen. Identity Check adds biometric layers to stop thieves.

46 Months for $37 Million: Chinese National Sentenced for Role in Cambodian Crypto Scam Ring FIFA website spoofing scams FBI World Cup alert Pig Butchering Scam Jingliang Su Sentencing Meta China Scam Ads, Zuckerberg Revenue Conflict Trading Bot Scam BEC Scam Rental Payment Fraud
  • Cybercriminals

46 Months for $37 Million: Chinese National Sentenced for Role in Cambodian Crypto Scam Ring

Do Son January 28, 2026 0

Jingliang Su sentenced to 46 months for laundering $36.9M in "pig butchering" proceeds. The scheme funneled crypto to Cambodian fraud hubs.

Pre-Auth RCE Risk: OpenSSL Patches High-Severity Stack Overflow (CVE-2025-15467) OpenSSL Vulnerability RSA Memory Leak OpenSSL Vulnerability CVE-2025-15467 CVE-2022-2274 OpenSSL Vulnerabilities, Timing Side-Channel
  • Vulnerability Report

Pre-Auth RCE Risk: OpenSSL Patches High-Severity Stack Overflow (CVE-2025-15467)

Do Son January 28, 2026 0

OpenSSL patches 12 flaws, including high-severity CVE-2025-15467 allowing pre-auth RCE via CMS. Update to 3.6.1/3.0.19 immediately to secure systems.

Under Attack: Critical Fortinet Auth Bypass (CVE-2026-24858) Exploited in the Wild GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability Report

Under Attack: Critical Fortinet Auth Bypass (CVE-2026-24858) Exploited in the Wild

Do Son January 28, 2026 0

Fortinet warns of critical flaw CVE-2026-24858 exploited in the wild. Attackers use FortiCloud SSO to bypass auth on FortiOS/Manager. Patch now.

Chrome Patches High-Severity Background Fetch Flaw (CVE-2026-1504) Chrome security update, CVE-2026-12007, CVE-2026-12008, CVE-2026-12010 Chrome Security Update CVE-2026-1504 Chrome WebGPU Overflow, V8 RCE
  • Vulnerability Report

Chrome Patches High-Severity Background Fetch Flaw (CVE-2026-1504)

Do Son January 28, 2026 0

Chrome 144 fixes high-severity flaw CVE-2026-1504 in Background Fetch API. Malicious sites could abuse downloads. Update immediately to stay safe.
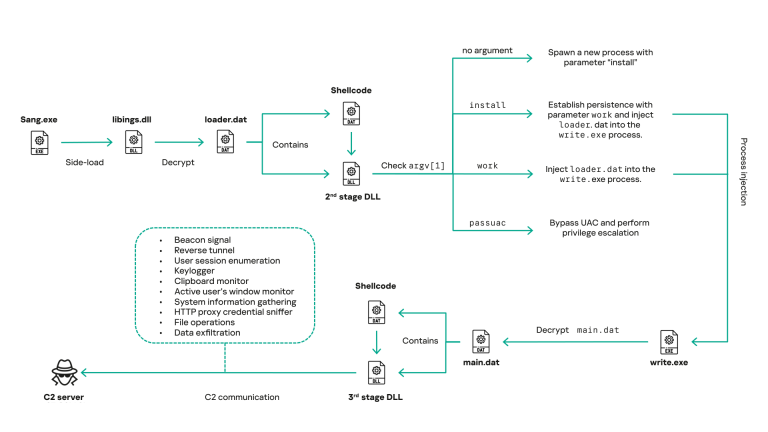
HoneyMyte Evolved: Spies Use Pixeldrain & CoolClient for Real-Time Surveillance HoneyMyte Espionage CoolClient Backdoor
  • Cyber Security
  • Malware

HoneyMyte Evolved: Spies Use Pixeldrain & CoolClient for Real-Time Surveillance

Do Son January 28, 2026 0

HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.

The “PayTool” Trap: Massive Fraud Cluster Impersonates Canada Gov & Air Canada WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

The “PayTool” Trap: Massive Fraud Cluster Impersonates Canada Gov & Air Canada

Do Son January 28, 2026 0

New "PayTool" fraud cluster targets Canadians via fake Gov & Air Canada sites. CloudSEK reveals how this PhaaS operation steals Interac logins.

Router Takeover: High-Severity Command Injection Flaw Hits TP-Link Archer MR600 Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

Router Takeover: High-Severity Command Injection Flaw Hits TP-Link Archer MR600

Do Son January 28, 2026 0

TP-Link patches CVE-2025-14756 (CVSS 8.5) in Archer MR600 routers. This command injection flaw allows full device takeover. Update firmware now.

“Gopher Strike”: New Pakistan-Linked Cyber Campaigns Target Indian Government Zyxel security - Mitel MiCollab Vulnerability
  • Cyber Security
  • Malware

“Gopher Strike”: New Pakistan-Linked Cyber Campaigns Target Indian Government

Do Son January 28, 2026 0

New "Gopher Strike" & "Sheet Attack" campaigns hit Indian govt. Linked to Pakistan, attackers use GitHub C2 & GenAI malware to evade detection.

Digital El Dorado: How the Tiny Island of Anguilla Hit the 1 Million .ai Domain Jackpot AI Prompt Injection Aqua Trivy Breach AI Assistant Apertus, open-source AI .ai domain milestone
  • Technology

Digital El Dorado: How the Tiny Island of Anguilla Hit the 1 Million .ai Domain Jackpot

Do Son January 28, 2026 0

Anguilla’s .ai domain has officially surpassed 1 million registrations, generating over $70M for the island and funding major national infrastructure.

The “Iron Man” Moment: Why Silicon Valley is Buying Out Mac Minis to Run Clawdbot Clawdbot AI agent
  • Technology

The “Iron Man” Moment: Why Silicon Valley is Buying Out Mac Minis to Run Clawdbot

Do Son January 28, 2026 0

Clawdbot is the viral "Local-First" AI agent turning Mac minis into personal digital employees. See why GitHub's latest star is a must-have for 2026.

Geopolitical Gridlock: Why China is Putting Meta’s $2 Billion Manus AI Deal Under the Microscope Meta Manus AI acquisition block Meta acquisition Manus AI agent, Manus $100M ARR startup
  • Technology

Geopolitical Gridlock: Why China is Putting Meta’s $2 Billion Manus AI Deal Under the Microscope

Do Son January 28, 2026 0

China launches a national security probe into Meta’s $2B acquisition of AI startup Manus. Algorithmic export and data sovereignty now threaten the deal.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.