Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Fake Region Block: YouTube’s Cryptic New War on Ad-Blockers YouTube ad block content unavailable 2026, YouTube regional restriction bypass YouTube Collaboration, Creator Features YouTube Shorts, AI Video Generation
  • Technology

The Fake Region Block: YouTube’s Cryptic New War on Ad-Blockers

Do Son January 30, 2026 0

YouTube is faking regional blocks to break ad-blockers in Jan 2026! Discover the "technical frustration" strategy behind the new "unavailable" errors.

Locked Out of the Crate: Microsoft’s “Smart” Security Cripples ASUS ROG Ally Smart App Control blocking Armoury Crate, ROG Ally Defender false positive 2026 Microsoft Zero-Day, Cloud Files UAF Microsoft Access end of life CVE-2025-21298 Azure Vulnerabilities
  • Windows

Locked Out of the Crate: Microsoft’s “Smart” Security Cripples ASUS ROG Ally

Do Son January 29, 2026 0

Microsoft Defender's Smart App Control is blocking ASUS Armoury Crate in Jan 2026. Learn why your ROG Ally controls are broken and how to fix it.
The Final Hang-Up: Microsoft Disables Legacy Modem Drivers for Security Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

The Final Hang-Up: Microsoft Disables Legacy Modem Drivers for Security

Do Son January 29, 2026 0

Windows 11 intentionally kills dial-up modems in Jan 2026! Discover why Microsoft removed Agere and Motorola drivers to fix critical security flaws.

The $799 Gamble: Apple Absorbs Memory Costs to Freeze iPhone 18 Prices iPhone 18 price prediction Ming-Chi Kuo, NAND flash price hike Apple 2026 iPhone 17 Wi-Fi issues iPhone 17, A19 processor
  • Technology

The $799 Gamble: Apple Absorbs Memory Costs to Freeze iPhone 18 Prices

Do Son January 29, 2026 0

Ming-Chi Kuo predicts iPhone 18 prices will stay flat in 2026. Discover how Apple plans to absorb rising memory costs to crush its competition.

The Instant Browser: Google Tests New Auto-Launch Toggle for Chrome Google Chrome Canary startup toggle, Chrome foreground process boot 2026
  • Technology

The Instant Browser: Google Tests New Auto-Launch Toggle for Chrome

Do Son January 29, 2026 0

Google Chrome is testing a new auto-launch toggle in Jan 2026. Learn how to enable the foreground startup feature for near-instant boot response.

The Insider Exit Ramp: Why You Should Switch Windows 11 Channels Now Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

The Insider Exit Ramp: Why You Should Switch Windows 11 Channels Now

Do Son January 29, 2026 0

Windows 11 Build 26300.7674 is here! Learn how to use this rare 2026 "migration window" to switch from the Dev Channel to the Beta Channel safely.
The Digital Sanctuary: Apple’s 10 Essential Privacy Rules for 2026 Coruna Exploit Kit iOS Security Update Apple Zero-Day CVE-2026-20700 Apple Data Privacy Day 2026, iPhone privacy features guide iOS Privilege Escalation, CVE-2025-24085 PoC Apple Manufacturing Academy, US Investment CVE-2024-44258 - symlink vulnerability
  • Data Leak

The Digital Sanctuary: Apple’s 10 Essential Privacy Rules for 2026

Do Son January 29, 2026 0

Celebrate Data Privacy Day 2026 with Apple’s 10 best security tools. From Private Cloud Compute to Locked Apps, take control of your digital footprint.

Locking Down the Chat: WhatsApp Debuts “Strict Mode” to Combat Pegasus Spyware WhatsApp Strict Account Settings 2026, Pegasus spyware defense WhatsApp
  • Technology

Locking Down the Chat: WhatsApp Debuts “Strict Mode” to Combat Pegasus Spyware

Do Son January 29, 2026 0

WhatsApp launches Strict Account Settings in Jan 2026. A "lockdown mode" to protect high-risk users from Pegasus spyware and zero-click attacks.
The End of Manual Syntax? LinkedIn Adds Verified “Vibe Coding” Skills LinkedIn Vibe Coding skill endorsement, Replit Lovable AI verification 2026 Skill Sprints career development, Ryan Roslansky LinkedIn career advice 2025 LinkedIn, AI training
  • Technology

The End of Manual Syntax? LinkedIn Adds Verified “Vibe Coding” Skills

Do Son January 29, 2026 0

LinkedIn launched verified Vibe Coding skills in Jan 2026. Showcase tool-backed credentials from Replit and Lovable to prove your AI proficiency.

High-Severity IDOR Flaw Lets Admins Hijack TP-Link Omada Owner Accounts Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

High-Severity IDOR Flaw Lets Admins Hijack TP-Link Omada Owner Accounts

Do Son January 29, 2026 0

TP-Link fixes critical IDOR (CVE-2025-9520) in Omada Controller allowing admins to hijack Owner accounts. Update now to prevent total network takeover.

Safety Broken: PyTorch “Safe” Mode Bypassed by Critical RCE Flaw PyTorch vulnerability, CVE-2025-32434 CVE-2026-24747
  • Vulnerability Report

Safety Broken: PyTorch “Safe” Mode Bypassed by Critical RCE Flaw

Do Son January 29, 2026 0

PyTorch patches CVE-2026-24747 (CVSS 8.8). The "weights_only" safety flag failed, allowing RCE via malicious models. Update to v2.10.0 now.

CVE-2026-24765: PHPUnit Vulnerability Exposes CI/CD Pipelines to RCE PHPUnit RCE Poisoned Pipeline Execution PHPUnit Vulnerability CVE-2026-24765
  • Vulnerability Report

CVE-2026-24765: PHPUnit Vulnerability Exposes CI/CD Pipelines to RCE

Do Son January 29, 2026 0

Critical PHPUnit flaw CVE-2026-24765 (CVSS 7.8) allows RCE via unsafe deserialization in coverage files. Vulnerability hits CI/CD pipelines. Update now.

Spies in the Spreadsheet: “Sheet Attack” Uses Google Sheets & AI to Target India Iranian Hacktivists Operation Epic Fury Cyber New Generation Warfare Russian Hybrid Escalation Plex data breach Water Systems Cybersecurity - Threat Actor Naming Standard
  • Cyber Security
  • Malware

Spies in the Spreadsheet: “Sheet Attack” Uses Google Sheets & AI to Target India

Do Son January 29, 2026 0

Pakistan-linked spies target India with "Sheet Attack," using Google Sheets for C2 and GenAI to build malware. Learn about SHEETCREEP and FIREPOWER.

CVE-2026-24002: Critical Sandbox Escape Turns Grist Spreadsheets into RCE Weapons shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

CVE-2026-24002: Critical Sandbox Escape Turns Grist Spreadsheets into RCE Weapons

Do Son January 29, 2026 0

CVE-2026-24002 (CVSS 9.1) allows RCE in Grist via Pyodide sandbox escape. Update to v1.7.9 now and ensure Deno protection is active.

The “Zeroplayer” Arsenal: WinRAR Flaw CVE-2025-8088 Weaponized by Spies WinRAR Vulnerability CVE-2025-8088
  • Cybercriminals
  • Vulnerability Report

The “Zeroplayer” Arsenal: WinRAR Flaw CVE-2025-8088 Weaponized by Spies

Do Son January 29, 2026 0

Critical WinRAR flaw CVE-2025-8088 is exploited by spies & cybercriminals. "Zeroplayer" sells the exploit. Update to v7.13 to stop Startup folder attacks.
Fake AI Assistant: Malicious “ClawdBot” Extension Hides Trojan in VS Code ClawdBot Malware VS Code Trojan
  • Malware

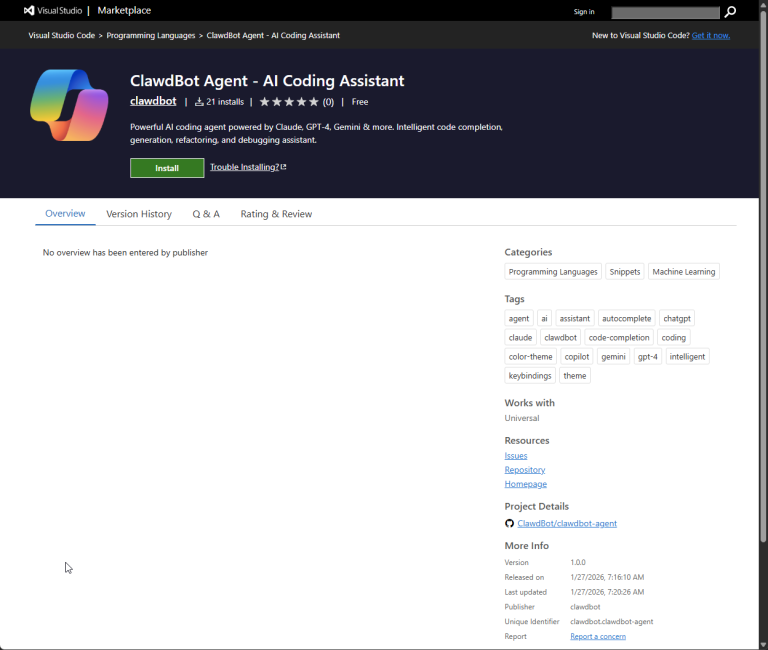
Fake AI Assistant: Malicious “ClawdBot” Extension Hides Trojan in VS Code

Do Son January 29, 2026 0

Malicious "ClawdBot Agent" VS Code extension exposed. Functioning as a real AI tool, it silently dropped malware. Microsoft removed it after 21 installs.

CVE-2026-23830: Critical SandboxJS Flaw (CVSS 10) Allows Total Sandbox Escape shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

CVE-2026-23830: Critical SandboxJS Flaw (CVSS 10) Allows Total Sandbox Escape

Do Son January 29, 2026 0

CVSS 10 flaw CVE-2026-23830 in SandboxJS allows RCE via unpatched Async functions. Attackers bypass all limits. Update to v0.8.26 immediately.

CVE-2025-14988: Critical 9.8 Vulnerability hits ibaPDA Industrial Software shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

CVE-2025-14988: Critical 9.8 Vulnerability hits ibaPDA Industrial Software

Do Son January 29, 2026 0

Critical ibaPDA flaw CVE-2025-14988 (CVSS 9.8) exposes industrial systems to file tampering. Update to v8.12.1 or harden settings now.

The “Fake CAPTCHA” Trap: Malware Hides in Google Calendar & Images CloudComputating - QSC framework
  • Malware

The “Fake CAPTCHA” Trap: Malware Hides in Google Calendar & Images

Do Son January 29, 2026 0

New Fake CAPTCHA campaign uses Google Calendar & steganography to drop Amatera Stealer. See how this attack exploits legitimate Windows tools to stay hidden.

Science at the Speed of AI: OpenAI Unveils Prism for LaTeX Research ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

Science at the Speed of AI: OpenAI Unveils Prism for LaTeX Research

Do Son January 29, 2026 0

OpenAI launches Prism in Jan 2026. Powered by GPT-5.2, this free LaTeX workspace automates citations, equations, and diagrams for scientists.

The Return of the Guide: Yahoo Scout Challenges Google with AI-Native Search Yahoo Scout AI answer engine, Anthropic Claude Yahoo search 2026
  • Technology

The Return of the Guide: Yahoo Scout Challenges Google with AI-Native Search

Do Son January 29, 2026 0

Yahoo debuts Scout in Jan 2026. This Anthropic Claude-powered answer engine blends AI summaries with prominent links to save the open web.

Excel’s New Brain: Agent Mode Brings GPT-5.2 and Claude 4.5 to Desktop Microsoft Excel Agent Mode 2026, Copilot model selector GPT-5.2 Claude 4.5
  • Technology

Excel’s New Brain: Agent Mode Brings GPT-5.2 and Claude 4.5 to Desktop

Do Son January 29, 2026 0

Microsoft Excel's Agent Mode is now on Windows and Mac! Switch between GPT-5.2 and Claude 4.5 to automate complex workbooks and live web data.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.