 Do Son
Most IoT security coverage is about devices being taken over: botnets, unsigned firmware, exposed admin ports. The...
Body-parser vulnerability CVE-2026-111181 (CVSS 7.5) enables Express denial of service with one request. Upgrade to body-parser 2.4.0 or 1.20.9.
 ddos-admin
New ADEX research shows how AI is making familiar scams cheaper and harder to detect, while fraudsters...
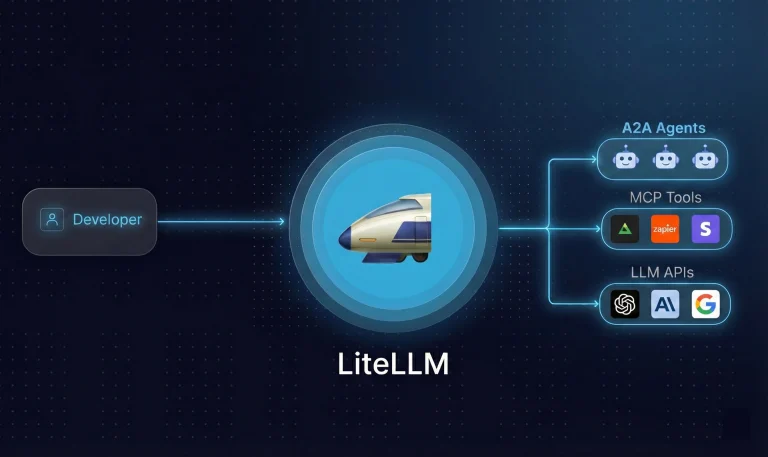
A critical LiteLLM vulnerability (CVSS 10.0) lets an unauthenticated file read leak the master key on Enterprise proxies. Update to 1.106.5 now.
Patch 9 critical Adobe vulnerabilities in Adobe Campaign Classic and Connect, including 9.9 CVSS RCE flaws CVE-2026-104351 and CVE-2026-48360.
Chrome security update 156.0.8078.73 fixes 52 flaws, including critical Chrome vulnerabilities like sandbox escape CVE-2026-118306. Update now.
Update to TeamViewer 15.83 to patch three high-severity TeamViewer vulnerabilities: CVE-2026-92372, CVE-2026-111585, and CVE-2026-92374.
Broadcom warns of a VMware SDDC Manager vulnerability, CVE-2026-111497 (CVSS 9.8), from the Node.js Brotli vulnerability. Patches pending.
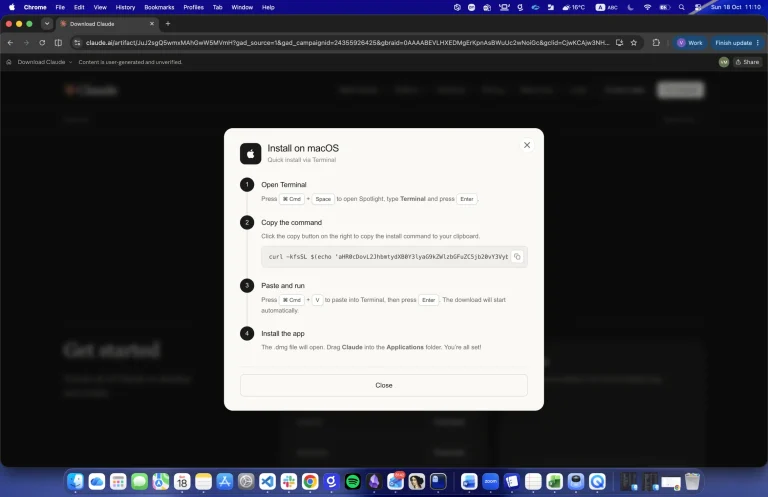
Gen Digital exposes a Claude malware campaign on claude.ai. This fake Download Claude malware campaign uses Google Ads and ClickFix to drop AMOS.
Microsoft explains why deleting Windows 11 Prefetch files degrades application startup performance while highlighting their crucial digital forensics role.
PoC and full details are public for the Linux nf_tables vulnerability CVE-2026-23111. The kernelCTF exploit gains root and escapes containers. Patch now.
Supermicro BMC vulnerabilities hit 392 boards. Critical IPMI flaw CVE-2026-18450 (CVSS 9.8) lets attackers run commands. Update BMC firmware now.
Moxa discloses three Moxa vulnerabilities in MRC Client and the end-of-life OnCell G3150A-LTE, including hard-coded keys and command injection.
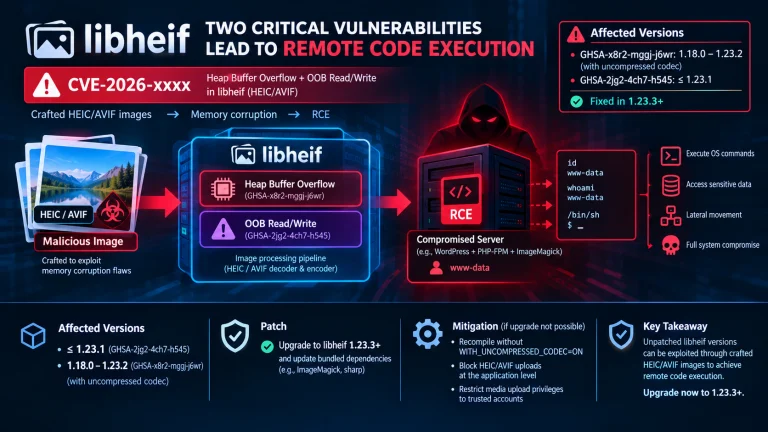
Details and PoC exploit code are out for critical libheif vulnerabilities GHSA-x8r2-mggj-j6wr and GHSA-2jg2-4ch7-h545. Upgrade to 1.23.3 now.
WatchGuard fixes 18 Fireware OS vulnerabilities on the Firebox firewall, including critical CVE-2026-103594 (CVSS 9.5). Upgrade to 2026.4 now.
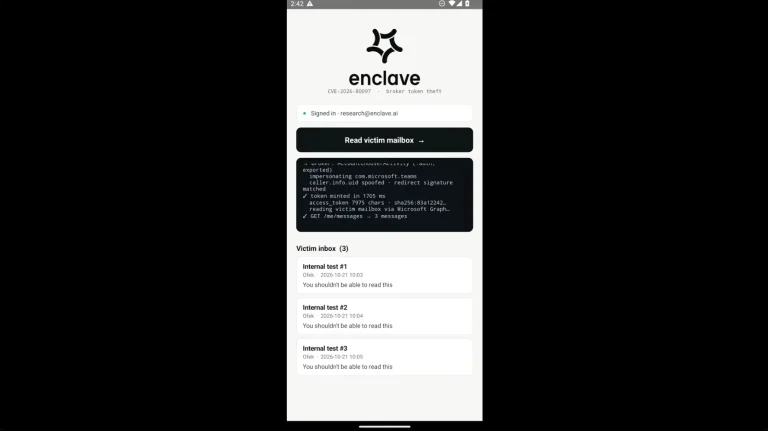
The Microsoft Authenticator AuthMask flaw allowed rogue Android apps to impersonate trusted software and hijack enterprise tokens and passkeys.
NVIDIA security update fixes NeMo Agent Toolkit vulnerability CVE-2026-65145 (CVSS 10.0) plus TensorRT-LLM and PhysX flaws. Update to 1.9.0 now.
CISA KEV catalog adds actively exploited Magento flaw CVE-2026-48356 and Brotli vulnerability CVE-2026-111497. Patch before November 10.
Patch 5 Veeam vulnerabilities in Veeam Backup & Replication and Veeam ONE, including critical flaw CVE-2026-108142 and MFA bypass CVE-2026-107671.
Quick verdict SelfyzAI is the AI creation platform I recommend when someone asks me for one account...
 cybernewswire
Hackers exploit YOOtheme Pro vulnerability CVE-2026-102785 (CVSS 10) for remote code execution, dropping webshells. Update to 5.0.53 now.