Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
TikTok’s Great Escape: Divestiture Closes as New USDS Entity Takes Control TikTok USDS Joint Venture LLC divestiture, Project Texas 2.0 ByteDance stake TikTokRefugee TikTok Ban, US Extension
  • Technology

TikTok’s Great Escape: Divestiture Closes as New USDS Entity Takes Control

Do Son January 26, 2026 0

TikTok avoids a U.S. ban in Jan 2026 by forming TikTok USDS Joint Venture LLC. ByteDance cedes 80.1% control to Oracle, Silver Lake, and MGX.

The DMA Standoff: Apple Slams EU “Delay Tactics” as Setapp Mobile Collapses iOS 27 Liquid Glass slider iPhone Flip rumors 2026 Setapp Mobile iOS shutdown, Apple DMA political delay tactics Apple AI pin wearable 2027, Siri Campos Gemini integration Apple AI strategy 2026, Liquid Glass interface Apple Intelligence Mac Pro Cancelled Mac Studio Future App Store antitrust, UK lawsuit iPhone Fold Hinge, Cost Optimization MacBook Pro, OLED display Apple supply chain, manufacturing automation Apple home security, smart camera Apple Earnings, AI Investment Apple EU Fine, DMA Appeal CVE-2023-23529
  • Technology

The DMA Standoff: Apple Slams EU “Delay Tactics” as Setapp Mobile Collapses

Do Son January 26, 2026 0

Apple accuses the EU of "political delay tactics" in Jan 2026 after Setapp Mobile shuts down. Discover why the Core Technology Fee is causing a crisis.

CVE-2025-27821: Apache Patches Out-of-Bounds Write Flaw in Hadoop HDFS Client CVE-2021-25642 Hadoop HDFS Vulnerability CVE-2025-27821
  • Vulnerability Report

CVE-2025-27821: Apache Patches Out-of-Bounds Write Flaw in Hadoop HDFS Client

Do Son January 25, 2026 0

Apache Hadoop HDFS native client flaw CVE-2025-27821 allows out-of-bounds writes. Update to v3.4.2 to prevent crashes and ensure data stability.
CISA Alert: Critical VMware vCenter RCE (CVSS 9.8) Now Exploited in the Wild CISA KEV Catalog DarkSword Exploit Draytek Routers VMware vCenter RCE CVE-2024-37079
  • Vulnerability Report

CISA Alert: Critical VMware vCenter RCE (CVSS 9.8) Now Exploited in the Wild

Do Son January 25, 2026 0

CISA adds VMware vCenter flaw CVE-2024-37079 (CVSS 9.8) to KEV catalog. Hackers are actively exploiting this RCE bug. Patch immediately.

How New Phishing Kits Are Turning Vishing into Real-Time Orchestration Vishing Kits MFA Bypass
  • Cybercriminals

How New Phishing Kits Are Turning Vishing into Real-Time Orchestration

Do Son January 25, 2026 0

Okta reveals new vishing kits that "drive" victim browsers. These real-time tools sync phone calls with phishing pages to bypass MFA number matching.

Bitwarden Evolution: New Monthly Billing and Proactive Phishing Defense for 2026 Bitwarden pricing update 2026, Bitwarden Premium monthly cost Windows 11 Passkey API Password Manager Integration
  • Technology

Bitwarden Evolution: New Monthly Billing and Proactive Phishing Defense for 2026

Do Son January 25, 2026 0

Bitwarden updates pricing in Jan 2026: Premium is now $1.65/mo. Discover the new Phishing Blocker, 5GB storage, and loyalty discounts for users.
End of an Era: Linux 7.0 Finally Retires the 1980s Supercomputing Legend Linux Kernel 7.1 release Linux Kernel update, AMD ZEN 6 support, Linux driver fixes Linux Kernel 7.1 i486 support Linux 7.0 HIPPI support removal, legacy networking protocol retirement Linus Torvalds AI slop Linux kernel, Lorenzo Stoakes AI tool debate Linux Kernel Rust CVE-2025-68260, Android Binder Rust Race Condition TSEM Security Module Controversy, Linus Torvalds LSM Dispute Kernel Panic, PoC released Linux Kernel 6.16, File System Fixes CVE-2023-42753 - Linux Kernel Developers
  • Linux

End of an Era: Linux 7.0 Finally Retires the 1980s Supercomputing Legend

Do Son January 25, 2026 0

Linux 7.0 officially drops HIPPI support in Jan 2026. Discover the history of this 800Mbps supercomputing giant and why the kernel is moving on.

Deep Kernel Fix: Linux Closes a 5-Year-Old Flaw in x86 Memory Handling Linux Kernel legacy driver removal Linux kernel x86 page fault, interrupt state asymmetry fix Linux ISO, false positive CVE-2023-6200 - Linux Kernel 6.12 LTS 6.14
  • Linux

Deep Kernel Fix: Linux Closes a 5-Year-Old Flaw in x86 Memory Handling

Do Son January 25, 2026 0

A 5-year-old flaw in Linux x86 page fault handling has finally been patched in Kernel 6.19. Discover how engineers fixed this "combinatorial nightmare."
CISA Adds 4 Critical Flaws to “Must-Patch” List as Exploits Surge CISA KEV Update Versa Concerto Vulnerability KEV Catalog Vulnerability Patch CVE-2025-30406
  • Vulnerability Report

CISA Adds 4 Critical Flaws to “Must-Patch” List as Exploits Surge

Do Son January 23, 2026 0

CISA adds 4 flaws to KEV, including critical Versa Concerto auth bypass (CVSS 9.2) & malicious "Prettier" package. Patch by Feb 12 to stop active attacks.

The Hacker’s Dream: NexPhone Debuts with Triple-OS Boot and 2036 Support NexPhone multi-OS smartphone, Windows 11 Linux Android phone
  • Technology

The Hacker’s Dream: NexPhone Debuts with Triple-OS Boot and 2036 Support

Do Son January 23, 2026 0

Discover the NexPhone: A 2026 breakthrough running Android, Linux, and Windows 11 on a single chip. Built for geeks with support until 2036.

“New” Path of Attack: Fully Upgraded Fortinet Devices Hit by SSO Exploits Fortinet patch bypass 2026, FortiGate SSO authentication exploit SharePoint Zero-Day, China APTs Exploited Vulnerabilities 2023
  • Vulnerability Report

“New” Path of Attack: Fully Upgraded Fortinet Devices Hit by SSO Exploits

Do Son January 23, 2026 0

Fortinet warns of a new Jan 2026 attack path bypassing December’s patches. Attackers use FortiCloud SSO to hijack firewalls. Learn the critical fix.

Wildcard Hijack: TrustAsia Revokes 143 Certificates After LiteSSL Vulnerability LiteSSL TrustAsia certificate revocation, ACME DNS-01 vulnerability
  • Vulnerability Report

Wildcard Hijack: TrustAsia Revokes 143 Certificates After LiteSSL Vulnerability

Do Son January 23, 2026 0

TrustAsia revoked 143 LiteSSL certificates in Jan 2026 after a critical ACME vulnerability allowed domain hijacking. See if your site is affected.

Outlook in Crisis: How to Fix the January 2026 Update Freezing Your Inbox Exfil Out&Look Microsoft 365 Logging Gap Outlook Classic KB5074109 freeze, January 2026 POP3 PST bug Outlook Classic POP3 freeze, KB5074109 Windows 11 bug Outlook, CPU Usage Outlook lag Outlook Lite discontinued
  • Windows

Outlook in Crisis: How to Fix the January 2026 Update Freezing Your Inbox

Do Son January 23, 2026 0

Microsoft's KB5074109 update is freezing Outlook Classic in Jan 2026. Learn how to fix POP3 and PST errors or rollback the update to save your mail.

YouTube’s 2026 Plan to Automate Shorts YouTube Shorts, digital well-being YouTube AI doppelgängers Shorts, Gemini 3 Playables games
  • Technology

YouTube’s 2026 Plan to Automate Shorts

Do Son January 23, 2026 0

YouTube CEO Neal Mohan reveals AI doppelgangers for Shorts and Gemini 3 games for 2026. Discover how the platform is fighting "AI slop" with tech.

Amazon’s Medical Move: New “Health AI” Assistant Turns Data into Doctor Visits Amazon One Medical Health AI, agentic health assistant 2026
  • Technology

Amazon’s Medical Move: New “Health AI” Assistant Turns Data into Doctor Visits

Do Son January 23, 2026 0

Amazon launches Health AI for One Medical in Jan 2026. This agentic assistant uses your medical history to book appointments and explain lab results.

Search Gets Personal: Google Integrates Gmail and Photos into AI Mode Google Search Personal Intelligence, Gemini 3 Search AI Mode Google Ad Redesign, Sponsored Results Visibility
  • Technology

Search Gets Personal: Google Integrates Gmail and Photos into AI Mode

Do Son January 23, 2026 0

Google launches Personal Intelligence in Jan 2026! Search AI Mode now uses your Gmail and Photos to provide hyper-tailored results.

Public Yet Private? Critical Appsmith Flaw Exposes Unpublished Actions (CVSS 9.4) CVE-2026-24042 Appsmith Vulnerability CVE-2026-22794
  • Vulnerability Report

Public Yet Private? Critical Appsmith Flaw Exposes Unpublished Actions (CVSS 9.4)

Do Son January 23, 2026 0

Critical Appsmith flaw CVE-2026-24042 (CVSS 9.4) allows public users to execute private, unpublished actions. Update to v1.95 now to secure your apps.
Public PoC Exploit Released for Critical Android Flaw Grants Apps Permissions Without You Knowing Android CVE-2024-23700 Zero-Interaction Exploit Candiru spyware Android vulnerability, security update
  • Vulnerability

Public PoC Exploit Released for Critical Android Flaw Grants Apps Permissions Without You Knowing

Do Son January 23, 2026 0

Public PoC exploit for Android CVE-2024-23700 allows critical privilege escalation without user interaction. WearOS & Custom ROMs are at risk.

Sabotage & Exploited in the Wild: Critical Backdoor Found in LA-Studio Element Kit CVE-2022-45359 LA-Studio Element Kit Backdoor CVE-2026-0920
  • Vulnerability Report

Sabotage & Exploited in the Wild: Critical Backdoor Found in LA-Studio Element Kit

Do Son January 23, 2026 0

Critical backdoor CVE-2026-0920 in LA-Studio Element Kit is being exploited in the wild. Former employee planted the code. Update to v1.6.0 immediately.
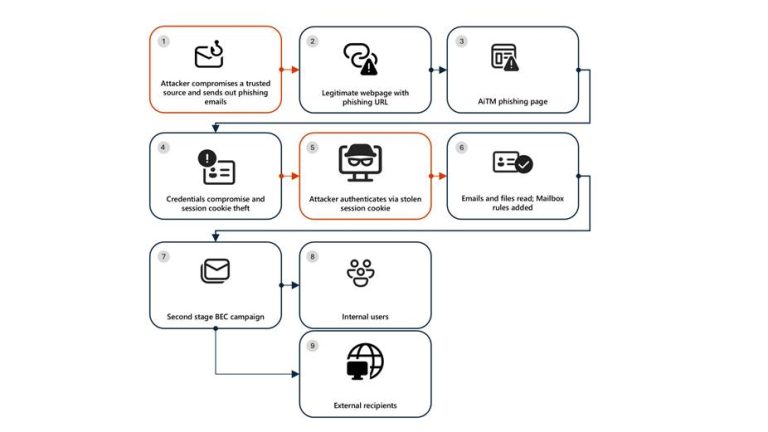
Energy Sector Under Siege: AiTM Phishing Turns Insiders Into Threats AiTM Phishing Energy Sector Business Email Compromise
  • Cybercriminals

Energy Sector Under Siege: AiTM Phishing Turns Insiders Into Threats

Do Son January 23, 2026 0

Microsoft warns of an AiTM phishing campaign targeting the energy sector. Hackers steal session cookies and abuse SharePoint to launch internal attacks.

CVE-2026-23594: High-Severity Flaw in HPE Alletra & Nimble Grants Admin Access HPE AutoPass Vulnerability, CVE-2026-23600 CVE-2024-22442 - HPE vulnerability HPE Storage Vulnerability CVE-2026-23594
  • Vulnerability Report

CVE-2026-23594: High-Severity Flaw in HPE Alletra & Nimble Grants Admin Access

Do Son January 23, 2026 0

HPE warns of critical flaw CVE-2026-23594 in Alletra & Nimble Storage. CVSS 8.8 bug allows remote admin access. Update to v6.1.2.800 now to secure data.

“SymPy” Imposter: Typosquatting Attack Turns Math Library into Crypto Miner sympy-dev Malware PyPI Supply Chain Attack
  • Malware

“SymPy” Imposter: Typosquatting Attack Turns Math Library into Crypto Miner

Do Son January 23, 2026 0

Malicious PyPI package "sympy-dev" impersonates SymPy to install XMRig miners via fileless execution. Check your dependencies immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.