Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
White House Orders Grok’s Reinstatement for Federal Use AI coding, grok-code-fast-1 xAI Grok 3 Grok 4, AI Model Baby Grok, xAI for Kids
  • Technology

White House Orders Grok’s Reinstatement for Federal Use

Do Son August 31, 2025 0

Despite recent controversies, the White House has reportedly ordered the reinstatement of xAI’s Grok for federal government use, cementing its place in the AI race.

Windows 11 25H2 Update Is Here: What’s New? Windows 11 update, version 25H2
  • Windows

Windows 11 25H2 Update Is Here: What’s New?

Do Son August 31, 2025 0

Windows 11's 25H2 update is now in the Release Preview channel. Learn about the new features, removed components, and how to get it early.

Why the U.S. Government Is Buying a Stake in Intel Intel Eric Demers GPU Chief Architect Intel, CHIPS Act Trump Intel, semiconductor investment Intel CHIPS Act
  • Technology

Why the U.S. Government Is Buying a Stake in Intel

Do Son August 31, 2025 0

The U.S. government has acquired an equity stake in Intel, freeing the company from CHIPS Act restrictions and cementing Washington's control over the chip industry.

Meta’s New AI NPCs Will Make Horizon Worlds Come to Life Metaverse, AI NPCs Horizon Worlds VR reversal
  • Technology

Meta’s New AI NPCs Will Make Horizon Worlds Come to Life

Do Son August 31, 2025 0

Meta is adding generative AI NPCs to Horizon Worlds. These characters will engage in real-time conversations, creating a more dynamic and immersive experience.

Microsoft Challenges OpenAI with First In-House AI Models Microsoft AI, MAI-1-preview
  • Technology

Microsoft Challenges OpenAI with First In-House AI Models

Do Son August 31, 2025 0

Microsoft launches its first in-house trained AI models, MAI-Voice-1 and MAI-1-preview, signaling a move toward independence from OpenAI's technology.

Nuclear Fusion Race Heats Up: A $863M Boost for CFS Nuclear Fusion, CFS Funding
  • Technology

Nuclear Fusion Race Heats Up: A $863M Boost for CFS

Do Son August 31, 2025 0

Nuclear fusion startup CFS just raised $863M from investors like NVIDIA and Google. This massive funding accelerates their quest for limitless, clean energy.

Can Llama 4.X Save Meta’s AI Ambitions? Meta Horizon Worlds Quest shutdown Meta AI, Child Safety Meta Robotics, Android of Robotics Meta AI, Llama 4.X Meta, AI regulation Meta AI, Data Center Impact Meta AI, Superintelligence Meta Copyrighted Data AI chatbot
  • Technology

Can Llama 4.X Save Meta’s AI Ambitions?

Do Son August 31, 2025 0

After a lukewarm reception to Llama 4, Meta is racing to release a new, more powerful model. Can Llama 4.X restore their place in the AI race?

Xbox’s New ‘Play History Sync’ Feature is a Game-Changer Xbox Cloud Gaming, Play History Sync
  • Technology

Xbox’s New ‘Play History Sync’ Feature is a Game-Changer

Do Son August 31, 2025 0

Xbox's new "Play History Sync" feature lets you seamlessly continue games across devices. Never lose momentum when switching from PC to console.

IBM watsonx Orchestrate Vulnerability (CVE-2025-0165) Exposes Systems to SQL Injection Attacks IBM CCA Vulnerability CVE-2025-13375 IBM Anthropic Partnership, AI Software Development watsonx Orchestrate, SQL injection CVE-2024-49803 - CVE-2024-41787 IBM Completes Acquisition HashiCorp
  • Vulnerability Report

IBM watsonx Orchestrate Vulnerability (CVE-2025-0165) Exposes Systems to SQL Injection Attacks

Do Son August 31, 2025 0

IBM has issued a security advisory for a SQL injection flaw (CVE-2025-0165) in watsonx Orchestrate. The high-severity bug could allow attackers to manipulate backend databases.

A Single URL Can Crash Your Website: Critical DoS Flaw (CVE-2025-58047) Found in Volto CMS Volto, vulnerability
  • Vulnerability Report

A Single URL Can Crash Your Website: Critical DoS Flaw (CVE-2025-58047) Found in Volto CMS

Do Son August 31, 2025 0

A high-severity DoS flaw (CVE-2025-58047) in Volto, the frontend for Plone CMS, allows an unauthenticated user to crash the server with a single crafted URL.
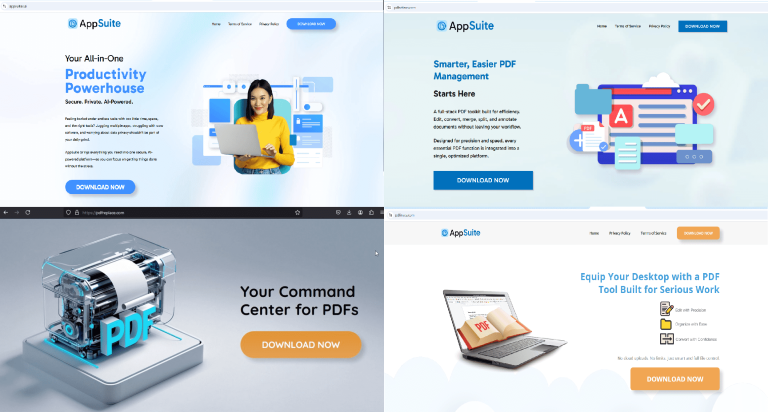
Trojan Horse: A Fake PDF Editor Is Actually a Malware-Laden Backdoor PDF Editor, malware
  • Malware

Trojan Horse: A Fake PDF Editor Is Actually a Malware-Laden Backdoor

Do Son August 31, 2025 0

A new report reveals that the AppSuite PDF Editor is a Trojan horse that functions as a backdoor. Its developers even submitted it to AV vendors to get it whitelisted.

From Zero to Conversations: How ChatGPT It Became Language Teacher ChatGPT-ad
  • Technique

From Zero to Conversations: How ChatGPT It Became Language Teacher

Do Son August 30, 2025 0
Why ChatGPT Turned Into an AI Tutor Students Actually Use ChatGPT has moved far beyond being a...
Read More Read more about From Zero to Conversations: How ChatGPT It Became Language Teacher
A Deceptive Ad on Facebook Is Spreading Advanced Android Malware malvertising, Android malware
  • Malware

A Deceptive Ad on Facebook Is Spreading Advanced Android Malware

Do Son August 30, 2025 0

A new report reveals a global malvertising campaign on Facebook spreading an evolved version of Brokewell malware to steal crypto and bypass 2FA.

BadSuccessor (CVE-2025-53779) Technique Persists Despite Microsoft Patch BadSuccessor, Active Directory
  • Vulnerability Report

BadSuccessor (CVE-2025-53779) Technique Persists Despite Microsoft Patch

Do Son August 30, 2025 0

A new Active Directory flaw, BadSuccessor, allows low-privileged users to become Domain Admins. Akamai researchers warn that the technique remains a threat even after patching.

MystRodX: A Stealthy New Backdoor Found Hiding in Networks for Over 20 Months MystRodX, stealthy backdoor
  • Malware

MystRodX: A Stealthy New Backdoor Found Hiding in Networks for Over 20 Months

Do Son August 30, 2025 0

A new report reveals MystRodX, a stealthy backdoor that uses passive wake-up triggers and multi-layer encryption to operate undetected in networks for months.

QNAP Patches Critical Flaw (CVE-2025-52856) with CVSS 9.3 QNAP Vulnerabilities CVE-2025-52856
  • Vulnerability Report

QNAP Patches Critical Flaw (CVE-2025-52856) with CVSS 9.3

Do Son August 29, 2025 0

QNAP has patched a critical improper authentication flaw (CVE-2025-52856) in its QVR firmware with a CVSS score of 9.3, allowing remote attackers to bypass security.

A Critical Zero-Click WhatsApp Flaw, CVE-2025-55177, Was Exploited in Zero-Day Attacks WhatsApp antitrust API probe India SIM-Binding Mandate Messaging App KYC WhatsApp DMA Interoperability BirdyChat Haiket Denmark Social Media Ban CVE-2025-55177 WhatsApp vulnerability, zero-click flaw npm Malware, System Wipe WhatsApp Windows App, WebView2 Downgrade WhatsApp Ban, US House NSO WhatsApp, Pegasus Spyware WhatsApp iPad iPadOS app
  • Vulnerability Report

A Critical Zero-Click WhatsApp Flaw, CVE-2025-55177, Was Exploited in Zero-Day Attacks

Do Son August 29, 2025 0

A critical zero-click flaw in WhatsApp (CVE-2025-55177), paired with an Apple zero-day, was used in sophisticated attacks. All users must update now.
Multi Flaws Found in HikCentral, Including a Bypass for Admin Access (CVE-2025-39247) Hikvision Vulnerability CVE-2026-0709 Hikvision Vulnerability CVE-2025-66176 Hikvision, vulnerability Canada Hikvision Ban, National Security Hikvision firmware updates
  • Vulnerability Report

Multi Flaws Found in HikCentral, Including a Bypass for Admin Access (CVE-2025-39247)

Do Son August 29, 2025 0

Hikvision has issued an advisory for three flaws in its HikCentral products. The most severe, with a CVSS of 8.6, allows an unauthenticated user to get admin access.

PoC Published: A Format String Bug in ImageMagick Could Allow Remote Code Execution ImageMagick, remote code execution
  • Vulnerability

PoC Published: A Format String Bug in ImageMagick Could Allow Remote Code Execution

Do Son August 29, 2025 0

ImageMagick has a format string bug (CVE-2025-55298) that can lead to RCE. A PoC is public, and an urgent patch is available for versions 7.1.2-2 and 6.9.13-28.

Interlock Ransomware Strikes: A New Strain Is Wrecking Havoc in North America and Europe Interlock ransomware, double extortion
  • Malware

Interlock Ransomware Strikes: A New Strain Is Wrecking Havoc in North America and Europe

Do Son August 29, 2025 0

A new report from AhnLab reveals the Interlock ransomware group is actively attacking businesses and critical infrastructure in North America and Europe with a sophisticated encryption model.

Beyond Scambaiting: YouTubers Help DOJ Bust a $65 Million Fraud Ring DOJ, fraud scheme
  • Cybercriminals

Beyond Scambaiting: YouTubers Help DOJ Bust a $65 Million Fraud Ring

Do Son August 29, 2025 0

The DOJ has indicted 28 members of a Chinese fraud ring for a $65M scheme targeting seniors. Evidence from YouTubers 'Scammer Payback' helped in the takedown.

Google’s $9 Billion Bet: The New Investment Fueling AI in Virginia Google Self-Preferencing Fine Idealo Antitrust Damages Anthropic, Google TPUs Google DMA Compliance, Search Self-Preferencing Google Play Store Ruling, Epic Games Victory Google fine, ad tech Google lawsuit, privacy violation Gmail security, false alarm Google Play EU regulation Google Security, Phone Number Leak Google 2025 - Google China’s Anti-Monopoly Law Google monopoly, ad tech Pixel 7a battery, battery swelling
  • Technology

Google’s $9 Billion Bet: The New Investment Fueling AI in Virginia

Do Son August 29, 2025 0

Google is investing $9 billion in Virginia by 2026 to expand its cloud and AI infrastructure. The plan includes a new data center and free AI access for college students.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.