Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
NVIDIA Refuses to Pay 15% China Revenue Share Without a Law NVIDIA GPU Security CUDA-Q Vulnerability NVIDIA Apex Vulnerability AI Infrastructure Security NVIDIA Cumulus Linux CVE-2025-33179 NVIDIA Arm divestment NVIDIA DGX Spark, CVE-2025-33187 NVIDIA Isaac-GROOT, Code Injection Megatron-LM Vulnerability, AI Code Injection NVIDIA China NVIDIA GPUs, Hardware Kill Switches NVIDIA Megatron-LM, LLM Vulnerabilities NVIDIA Base Command Manager - CVE-2024-0138
  • Technology

NVIDIA Refuses to Pay 15% China Revenue Share Without a Law

Do Son August 29, 2025 0

NVIDIA's CFO has stated the company will not pay the U.S. government a 15% revenue share on China sales unless the agreement is formally codified into law.

Cloud Gaming for Everyone: Xbox Opens Its Streaming Service to Game Pass Core and Standard Free Xbox Cloud Gaming, Ad-Supported Tier Xbox Cloud Gaming Game Pass
  • Technology

Cloud Gaming for Everyone: Xbox Opens Its Streaming Service to Game Pass Core and Standard

Do Son August 29, 2025 0

Xbox Cloud Gaming is now being tested for Game Pass Core and Standard subscribers. The expansion brings the feature to a wider audience beyond the premium Ultimate tier.

A New Race for Silicon: Apple Secures Half of TSMC’s 2nm Chip Production Apple silicon, in-house chips Apple Event, iPhone 17 Air TSMC, 2nm chips
  • Technology

A New Race for Silicon: Apple Secures Half of TSMC’s 2nm Chip Production

Do Son August 29, 2025 0

Apple has reportedly secured nearly half of TSMC's 2nm chip production for the iPhone 18's A20 processor, a move that highlights the fierce competition for cutting-edge silicon.

PoC Published: Critical Unauthenticated Command Injection Flaw in D-Link Routers (CVSS 9.8), No Patch! D-Link, command injection
  • Vulnerability

PoC Published: Critical Unauthenticated Command Injection Flaw in D-Link Routers (CVSS 9.8), No Patch!

Do Son August 29, 2025 0

D-Link warns of a critical command injection flaw (CVSS 9.8) in its EOL DIR-series routers. A PoC is public, and since no patch is available, devices must be replaced.

CRITICAL Zero-Day CVE-2025-57819 in FreePBX Is Under Active Attack (CVSS 10.0) Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Vulnerability Report

CRITICAL Zero-Day CVE-2025-57819 in FreePBX Is Under Active Attack (CVSS 10.0)

Do Son August 29, 2025 0

A critical zero-day (CVE-2025-57819) in FreePBX with a CVSS 10.0 score is being actively exploited. The flaw allows unauthenticated RCE, and admins must patch immediately.

CVE-2025-50979: SQL Injection Flaw in NodeBB Forum Software, PoC Available NodeBB, SQL injection
  • Vulnerability Report

CVE-2025-50979: SQL Injection Flaw in NodeBB Forum Software, PoC Available

Do Son August 29, 2025 0

A critical SQL injection flaw (CVE-2025-50979) in NodeBB allows remote attackers to access sensitive data. Admins are urged to patch immediately.
Is This a Rebrand? New Sinobi Ransomware Group Shows Code Overlap with Lynx Sinobi Group, ransomware
  • Malware

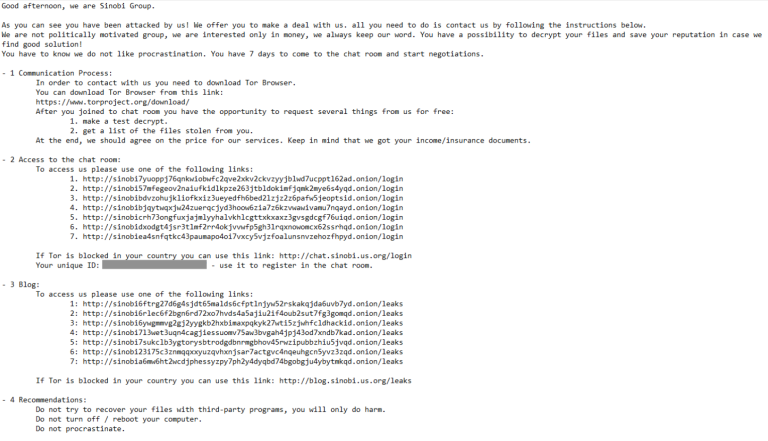
Is This a Rebrand? New Sinobi Ransomware Group Shows Code Overlap with Lynx

Do Son August 29, 2025 0

A new report links Sinobi Group ransomware to Lynx, a potential rebrand. The group is using strong encryption and targeting compromised SonicWall VPN credentials to gain access.
Anthropic Report: Criminals Are Weaponizing AI to Automate Cyberattacks at Scale Anthropic, AI misuse
  • Cybercriminals

Anthropic Report: Criminals Are Weaponizing AI to Automate Cyberattacks at Scale

Do Son August 29, 2025 0

A new Anthropic report reveals how criminals are weaponizing AI systems to automate attacks, create AI-generated ransomware, and secure fraudulent employment.

Malware-less Ransomware: How Storm-0501 is Pivoting to Cloud-Native Attacks Storm-0501, cloud ransomware
  • Cybercriminals

Malware-less Ransomware: How Storm-0501 is Pivoting to Cloud-Native Attacks

Do Son August 29, 2025 0

A new Microsoft report reveals that the Storm-0501 threat actor is pivoting to cloud-native ransomware, using cloud tools to exfiltrate and destroy data without malware.

A Deceptive AI Lure Is Hiding ScreenConnect & XWorm RAT to Hijack Your PC ScreenConnect, XWorm RAT
  • Malware

A Deceptive AI Lure Is Hiding ScreenConnect & XWorm RAT to Hijack Your PC

Do Son August 29, 2025 0

A new campaign is using fake AI-themed content to trick users into downloading a malicious ScreenConnect installer that secretly delivers the XWorm Remote Access Trojan.
Beyond Email: Why Your Microsoft Teams Chat Is Now a Phishing Danger Zone Teams phishing, Teams security
  • Cybercriminals

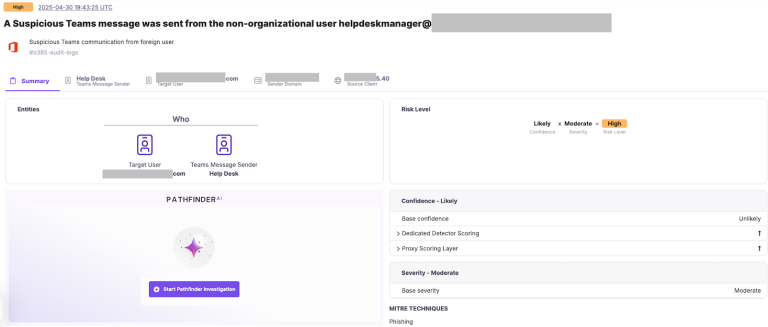
Beyond Email: Why Your Microsoft Teams Chat Is Now a Phishing Danger Zone

Do Son August 29, 2025 0

A new report reveals that attackers are abusing Microsoft Teams' collaboration features to launch phishing, vishing, and malware attacks, bypassing security warnings.

Kaspersky Report: Vulnerabilities Are Exploding, and Attackers Are Adapting shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Kaspersky Report: Vulnerabilities Are Exploding, and Attackers Are Adapting

Do Son August 29, 2025 0

Kaspersky's Q2 2025 report reveals a surge in vulnerabilities, with attackers exploiting classic flaws in Windows and WinRAR while adapting to AI and low-code platforms.

ShadowSilk Unmasked: The Hybrid Espionage Group Targeting Central Asian Governments Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cybercriminals

ShadowSilk Unmasked: The Hybrid Espionage Group Targeting Central Asian Governments

Do Son August 29, 2025 0

A new Group-IB report reveals ShadowSilk, a hybrid Chinese and Russian-speaking threat cluster that uses Telegram bots for cyber espionage against Central Asian governments.

After 21 Years, the Typepad Blogging Platform Is Shutting Down Typepad, blog platform
  • Technology

After 21 Years, the Typepad Blogging Platform Is Shutting Down

Do Son August 29, 2025 0

Typepad, a popular blogging platform, has announced it will shut down on September 30, 2025. Users are urged to export all of their content before that date.

Copilot Is Coming to Your Living Room with New Samsung Smart TV Partnership Microsoft Copilot, Samsung TVs
  • Technology

Copilot Is Coming to Your Living Room with New Samsung Smart TV Partnership

Do Son August 29, 2025 0

Microsoft is partnering with Samsung to bring Copilot AI to its 2025 TVs and smart displays, transforming the living room experience with a new conversational assistant.

Breaking the Passkey Promise: SquareX Discloses Major Passkey Vulnerability at DEF CON 33 20250820_Passkeys_Pwned_Cybernews_1200x720px_01_1_1756286223peVroPMVkD
  • Press Release

Breaking the Passkey Promise: SquareX Discloses Major Passkey Vulnerability at DEF CON 33

cybernewswire August 28, 2025 0
Palo Alto, California, 28th August 2025, CyberNewsWire
Read More Read more about Breaking the Passkey Promise: SquareX Discloses Major Passkey Vulnerability at DEF CON 33
URGENT: Sangoma FreePBX Warns of Exploit, Urges Immediate Administrator Lockdown FreePBX, security advisory
  • Vulnerability Report

URGENT: Sangoma FreePBX Warns of Exploit, Urges Immediate Administrator Lockdown

Do Son August 28, 2025 0

Sangoma has issued an urgent security advisory for a FreePBX exploit. Admins with publicly exposed control panels are urged to lock down access immediately.
Cisco Warns of High-Severity DoS Flaw (CVE-2025-20241) in Nexus Switches Cisco Secure FMC CVE-2026-20079 Cisco RCE, Firewall Vulnerability Cisco Nexus, vulnerability CVE-2024-20412 - Cisco data breach
  • Vulnerability Report

Cisco Warns of High-Severity DoS Flaw (CVE-2025-20241) in Nexus Switches

Do Son August 28, 2025 0

Cisco has issued a security advisory for a high-severity DoS vulnerability (CVE-2025-20241) in its Nexus switches that could allow an unauthenticated attacker to crash a device.

OpenAI Is Now Scanning Conversations and Reporting Harmful Content to Police GPT-OSS-SafeGuard, AI safety ChatGPT Memory Management, Paid Feature ChatGPT Teens ChatGPT, mental health
  • Technology

OpenAI Is Now Scanning Conversations and Reporting Harmful Content to Police

Do Son August 28, 2025 0

OpenAI has announced it is now scanning ChatGPT conversations for harmful content and reporting threats of physical harm to police in an effort to improve safety.

A CVSS 9.6 Remote Flaw Allows Unauthenticated Attackers to Bypass Dell ThinOS Dell ThinOS, remote access
  • Vulnerability

A CVSS 9.6 Remote Flaw Allows Unauthenticated Attackers to Bypass Dell ThinOS

Do Son August 28, 2025 0

Dell has released a critical security advisory for ThinOS 10, with a CVSS 9.6 flaw that allows unauthenticated remote attackers to bypass protection mechanisms.

PromptLock: A New AI-Powered Ransomware Strain Creates Unique, Elusive Scripts AI ransomware, PromptLock Against Ransomware - RECOPE Ransomware Attack
  • Malware

PromptLock: A New AI-Powered Ransomware Strain Creates Unique, Elusive Scripts

Do Son August 28, 2025 0

A new report from ESET reveals PromptLock, a ransomware strain that uses AI to dynamically generate malicious scripts, making it uniquely difficult for security software to detect.
Tencent Cloud’s Misconfiguration Exposed Internal Source Code and Credentials Booking.com Data Breach Claude Code Leak Anthropic Source Code YggTorrent data breach PS5 BootROM key leak 2026, PlayStation 5 unpatchable jailbreak Great Firewall data leak Dating App Breach, Tea App Leak 23andMe Data Leak
  • Data Leak

Tencent Cloud’s Misconfiguration Exposed Internal Source Code and Credentials

Do Son August 28, 2025 1

A severe misconfiguration in Tencent Cloud exposed sensitive internal credentials and source code to the public internet for months, risking a major breach.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.