Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Urgent Xerox FreeFlow Core Patch: Critical Flaws (CVSS 9.8) Allow RCE and SSRF Xerox RCE, FreeFlow Core Vulnerabilities
  • Vulnerability Report

Urgent Xerox FreeFlow Core Patch: Critical Flaws (CVSS 9.8) Allow RCE and SSRF

Do Son August 11, 2025 0

Xerox has patched two critical vulnerabilities (CVE-2025-8355, CVE-2025-8356) in FreeFlow Core 8.0.4, allowing attackers to exploit XML and path traversal flaws to achieve RCE and SSRF.

CVE-2025-5095 (CVSS 9.8): Critical Flaw in ARC Solo Broadcasting Devices Allows Unauthenticated Takeover ARC Solo, CISA Alert
  • Vulnerability Report

CVE-2025-5095 (CVSS 9.8): Critical Flaw in ARC Solo Broadcasting Devices Allows Unauthenticated Takeover

Do Son August 11, 2025 0

CISA warns of a critical authentication bypass flaw (CVE-2025-5095, CVSS 9.8) in ARC Solo devices, allowing attackers to change passwords and take full remote control without authentication.

Efimer Trojan: New Crypto-Stealer Hijacks Wallets via Fake Legal Threats & Malicious Torrents Efimer Trojan, Crypto Hijacking
  • Malware

Efimer Trojan: New Crypto-Stealer Hijacks Wallets via Fake Legal Threats & Malicious Torrents

Do Son August 11, 2025 0

Kaspersky exposes Efimer, a new crypto-stealer using fake legal threats and malicious torrents from compromised WordPress sites to hijack wallets and brute-force other sites.

CastleBot: The New MaaS Framework Fueling Info-Stealer & Ransomware Attacks CastleBot, Malware-as-a-Service
  • Malware

CastleBot: The New MaaS Framework Fueling Info-Stealer & Ransomware Attacks

Do Son August 11, 2025 0

IBM X-Force exposes CastleBot, a new MaaS framework that deploys infostealers and backdoors like NetSupport and WarmCookie via trojanized installers and phishing.

Linux Kernel Flaw (CVE-2025-38236): Privilege Escalation Risk, PoC Code Available Linux Kernel Exploit, Privilege Escalation
  • Vulnerability Report

Linux Kernel Flaw (CVE-2025-38236): Privilege Escalation Risk, PoC Code Available

Do Son August 11, 2025 0

A critical UAF flaw in the Linux kernel (CVE-2025-38236) allows for privilege escalation. A PoC exploit is now public, demonstrating how to escape the Chrome sandbox and gain kernel control.

GreedyBear Unmasked: How Stealthy Firefox Extensions and Fake Sites Stole $1M in Crypto GreedyBear, Cryptocurrency Theft
  • Cybercriminals

GreedyBear Unmasked: How Stealthy Firefox Extensions and Fake Sites Stole $1M in Crypto

Do Son August 11, 2025 0

A coordinated campaign by GreedyBear used 150+ malicious Firefox extensions and fake sites to steal over $1M in crypto. They are now using a new technique called Extension Hollowing to evade detection.

ScarCruft APT Deploys VCD Ransomware, Uses PubNub & New Malware in Espionage Campaign North Korea APT, PubNub Abuse
  • Cybercriminals

ScarCruft APT Deploys VCD Ransomware, Uses PubNub & New Malware in Espionage Campaign

Do Son August 11, 2025 0

S2W TALON exposes ScarCruft (APT37), a North Korean APT using a new campaign disguised as a postal notice, deploying NubSpy and VCD ransomware via PubNub C2.

WinRAR Update: Zero-Day Path Traversal Flaw (CVE-2025-8088) Actively Exploited to Deliver Malware WinRAR Zero-Day, Path Traversal CVE-2025-8088
  • Vulnerability Report

WinRAR Update: Zero-Day Path Traversal Flaw (CVE-2025-8088) Actively Exploited to Deliver Malware

Do Son August 11, 2025 0

ESET warns of an actively exploited WinRAR zero-day (CVE-2025-8088). The path traversal flaw allows attackers to execute code by crafting malicious archives.

Exclusive Threat Intelligence Transforming SOC Operations Goes Free exclusive_intel_cover
  • Technique

Exclusive Threat Intelligence Transforming SOC Operations Goes Free

Do Son August 11, 2025 0

Unlock the power of Threat Intelligence with free access to real-world attack data from ANY.RUN's innovative platform.
DarkCloud Rises: New Fileless Stealer Uses PowerShell & Process Hollowing to Evade Detection DarkCloud Stealer, Fileless Malware
  • Malware

DarkCloud Rises: New Fileless Stealer Uses PowerShell & Process Hollowing to Evade Detection

Do Son August 11, 2025 0

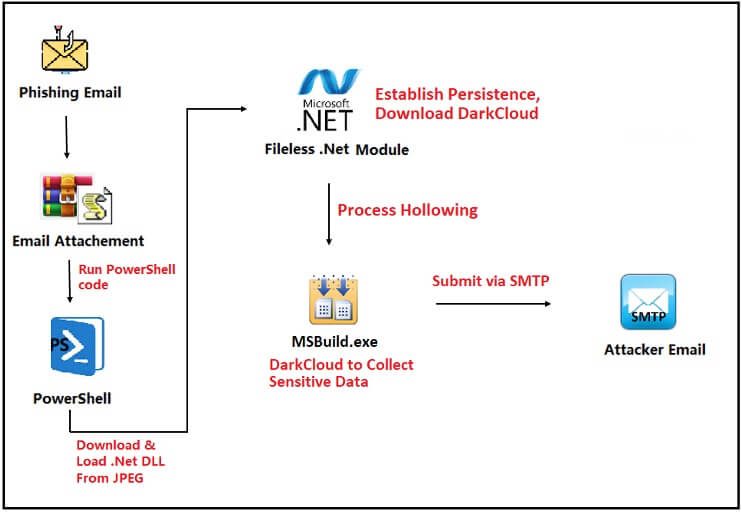
Fortinet uncovers a new DarkCloud stealer variant using a fileless, multi-stage attack chain with obfuscated PowerShell and process hollowing to evade detection and exfiltrate data.

Google Is Ending Steam Support for Chromebooks, But Gaming Isn’t Over Steam Store Redesign, Valve Update macOS Steam Game malware Chromebooks Steam
  • Technology

Google Is Ending Steam Support for Chromebooks, But Gaming Isn’t Over

Do Son August 9, 2025 0

Google is ending support for Steam on Chromebooks. The beta program will conclude on January 1, 2026, though cloud and Android gaming options remain.

Tesla Scraps Dojo Supercomputer Project, Shifts AI Strategy Tesla Dojo
  • Technology

Tesla Scraps Dojo Supercomputer Project, Shifts AI Strategy

Do Son August 9, 2025 0

Tesla is dissolving its Dojo supercomputer team, ending its in-house chip project. The company will now focus on external partnerships to power its AI ambitions.

Coding with GPT-5: Microsoft Integrates New AI Powerhouse into Visual Studio Code Visual Studio Code, GPT-5
  • Technology

Coding with GPT-5: Microsoft Integrates New AI Powerhouse into Visual Studio Code

Do Son August 9, 2025 0

Microsoft is rolling out GPT-5 support for Visual Studio Code via GitHub Copilot. The new model promises smarter and faster coding for paid subscribers.

How to Get Windows 10 Extended Security Updates for Free (or Cheap) Windows 10, Bing Integration
  • Windows

How to Get Windows 10 Extended Security Updates for Free (or Cheap)

Do Son August 9, 2025 0

Microsoft's Windows 10 ESU program offers one more year of security updates for $30, but you can get it for free by using Windows Backup or Bing Rewards.

Codex CLI Gets a Game-Changing Update: Log In with Your ChatGPT Account Codex CLI, OpenAI
  • Technology

Codex CLI Gets a Game-Changing Update: Log In with Your ChatGPT Account

Do Son August 9, 2025 0

OpenAI’s Codex CLI now allows direct login with a ChatGPT account, letting developers use their subscription quotas without paying extra API fees.

Raksha Bandhan Scams Surge in India: Phishing, Fake Stores, and Virtual Sibling Cons Target Festival Shoppers Raksha Bandhan Scams, Phishing Campaigns
  • Cybercriminals

Raksha Bandhan Scams Surge in India: Phishing, Fake Stores, and Virtual Sibling Cons Target Festival Shoppers

Do Son August 9, 2025 0

CloudSEK warns of a surge in Raksha Bandhan-themed phishing, fake websites, and UPI scams in India. Attackers use courier lures, fake e-stores, and social engineering to steal money.

PyPI Rejects Malicious ZIP Archives to Block “Parser Confusion” Attacks PyPI Security, ZIP Confusion
  • Vulnerability Report

PyPI Rejects Malicious ZIP Archives to Block “Parser Confusion” Attacks

Do Son August 9, 2025 0

PyPI is implementing new restrictions to reject problematic ZIP archives and protect against "parser confusion" attacks, which could bypass security checks and smuggle malicious files.

CISA Alert: Critical Flaws Expose EG4 Electronics Inverters to Remote Takeover EG4 Electronics, CISA Alert
  • Vulnerability Report

CISA Alert: Critical Flaws Expose EG4 Electronics Inverters to Remote Takeover

Do Son August 9, 2025 0

CISA warns of critical flaws in EG4 Electronics inverters (CVSS up to 9.2), allowing attackers to install malicious firmware, hijack control, and disrupt power generation.

Android Studio Narwhal Arrives: AI Agent Mode, XR Tools, and K2 Kotlin Now in Stable Release Android Studio, AI Agent Mode
  • Android

Android Studio Narwhal Arrives: AI Agent Mode, XR Tools, and K2 Kotlin Now in Stable Release

Do Son August 8, 2025 0

Android Studio Narwhal is now stable, introducing AI Agent Mode for complex tasks, new XR development tools, the K2 Kotlin compiler by default, and compatibility checks for 16KB pages.

RubyGems Under Attack: 60 Malicious Packages Found Stealing Credentials from Grey-Hat Marketers Cemu emulator Linux malware Blitz Brigantine AOBackdoor GitHub Malware Campaign StealC Infostealer TamperedChef Malware, SEO Poisoning Carbanak malware RubyGems Supply Chain, Infostealer
  • Malware

RubyGems Under Attack: 60 Malicious Packages Found Stealing Credentials from Grey-Hat Marketers

Do Son August 8, 2025 0

Socket uncovers a long-running supply chain attack on RubyGems. A threat actor published 60 malicious gems stealing credentials from grey-hat marketers.

GitLab Exposes a Clever Crypto Scam: Malicious PyPI Packages Hijack Bittensor Staking Bittensor Typosquatting, Crypto Scam
  • Cybercriminals

GitLab Exposes a Clever Crypto Scam: Malicious PyPI Packages Hijack Bittensor Staking

Do Son August 8, 2025 0

GitLab researchers uncovered a crypto scam on PyPI. Typosquatted Bittensor packages hijacked staking functions to silently drain users' crypto wallets.

DarkCloud Stealer: New Evasive Tactics Use Obfuscated Scripts & VB6 Payloads to Evade Detection darkcloud
  • Malware

DarkCloud Stealer: New Evasive Tactics Use Obfuscated Scripts & VB6 Payloads to Evade Detection

Do Son August 8, 2025 0

Unit 42 uncovers DarkCloud Stealer's new evasion tactics, including heavily obfuscated JavaScript/WSF loaders and a final VB6 payload that injects into RegAsm.exe to bypass detection.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.