Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Halo Security Achieves SOC 2 Type 1 Compliance, Validating Security Controls for Its Attack Surface Management Platform halo-security-soc2-type-1-pr_1747861523NMPbWxqoaj
  • Press Release

Halo Security Achieves SOC 2 Type 1 Compliance, Validating Security Controls for Its Attack Surface Management Platform

cybernewswire May 22, 2025 0
Miami, Florida, 22nd May 2025, CyberNewsWire
Read More Read more about Halo Security Achieves SOC 2 Type 1 Compliance, Validating Security Controls for Its Attack Surface Management Platform
Your AI Summary Will Have Ads: Google Integrates Sponsored Content into Search AI overview ads, Google search ads
  • Technology

Your AI Summary Will Have Ads: Google Integrates Sponsored Content into Search

Do Son May 22, 2025 0

Google is placing sponsored ads seamlessly within its AI-generated search summaries, appearing at the bottom of the AI overview on desktop and mobile.

Critical 0-Day: Cityworks Flaw Actively Exploited by Chinese APT UAT-6382 UTA
  • Cyber Security

Critical 0-Day: Cityworks Flaw Actively Exploited by Chinese APT UAT-6382

Do Son May 22, 2025 0

A China-linked APT, UAT-6382, is actively exploiting a zero-day (CVE-2025-0994) in Cityworks to gain RCE and persistent access to government and utility systems.

Europol & Microsoft Lead Global Takedown of Lumma Stealer, World’s Largest Infostealer Lumma Stealer takedown Cybercrime disruption
  • Cybercriminals

Europol & Microsoft Lead Global Takedown of Lumma Stealer, World’s Largest Infostealer

Do Son May 22, 2025 0

Global operation neutralizes Lumma Stealer, infecting hundreds of thousands of PCs. Europol & Microsoft seized over 1,300 malicious domains.

INE Security Partners with Abadnet Institute for Cybersecurity Training Programs in Saudi Arabia Cyberwire_Logo_-_INE_Security_-_1200x720px_1747851790kp8Vx0TKi1
  • Press Release

INE Security Partners with Abadnet Institute for Cybersecurity Training Programs in Saudi Arabia

cybernewswire May 22, 2025 0
Cary, North Carolina, 22nd May 2025, CyberNewsWire
Read More Read more about INE Security Partners with Abadnet Institute for Cybersecurity Training Programs in Saudi Arabia
ThreatBook Named a Notable Vendor in Global Network Analysis and Visibility (NAV) Independent Report ThreatBook_Logo_1747885054D8rFflroB8
  • Press Release

ThreatBook Named a Notable Vendor in Global Network Analysis and Visibility (NAV) Independent Report

cybernewswire May 22, 2025 0
Beijing, China, 22nd May 2025, CyberNewsWire
Read More Read more about ThreatBook Named a Notable Vendor in Global Network Analysis and Visibility (NAV) Independent Report
Privilege Escalation Flaws in Cisco Unified Intelligence Center Threaten User Data Integrity Cisco ISE Root Escalation * Read-Only Admin Exploit Cisco Secure FMC Vulnerability CVE-2026-20131 Cisco Meeting Management Vulnerability CVE-2026-20098 Cisco vulnerability, RCE flaw CVE-2025-20265 Cisco Meraki, VPN Vulnerability Cisco Nexus Dashboard - CVE-2024-20424 CVE-2025-20115 Cisco Vulnerability CVE-2018-0171 Privilege Escalation Cisco Unified Intelligence Center
  • Vulnerability

Privilege Escalation Flaws in Cisco Unified Intelligence Center Threaten User Data Integrity

Do Son May 22, 2025 0

Cisco patches two privilege escalation flaws in Unified Intelligence Center that could expose sensitive data. Users urged to upgrade immediately.

Unauthenticated Attacker Can Read Sensitive Files in Mitel OpenScape Xpressions MiContact Center Business Vulnerabilities Mitel vulnerability, OpenScape Xpressions
  • Vulnerability

Unauthenticated Attacker Can Read Sensitive Files in Mitel OpenScape Xpressions

Do Son May 22, 2025 0

A high-severity flaw (CVE-2025-48026) in Mitel OpenScape Xpressions allows unauthenticated attackers to read sensitive local files, including voicemail.

Google Chrome Update: 8 Security Fixes Including High-Severity Flaw Chrome security update, browser vulnerabilities
  • Vulnerability

Google Chrome Update: 8 Security Fixes Including High-Severity Flaw

Do Son May 22, 2025 0

Google Chrome released an update with 8 security fixes, including a high-severity use-after-free vulnerability (CVE-2025-5063). Update your browser now!

Unpatched 0-Days (CVSS 10): Versa Concerto Flaws Threaten Enterprise Networks Versa Concerto exploit, SD-WAN security
  • Vulnerability

Unpatched 0-Days (CVSS 10): Versa Concerto Flaws Threaten Enterprise Networks

Do Son May 22, 2025 0

ProjectDiscovery revealed critical zero-days (CVSS 10) in Versa Concerto, enabling full RCE and host compromise via auth bypass and Docker escape.

RADIUS Risk: Unauthenticated Remote Attacker Can Crash Cisco ISE by Default CVE-2024-20419 - Cisco Webex Vulnerability Cisco ISE DoS, CVE-2025-20152
  • Vulnerability

RADIUS Risk: Unauthenticated Remote Attacker Can Crash Cisco ISE by Default

Do Son May 22, 2025 0

Unauthenticated remote attackers can crash Cisco ISE via RADIUS, enabled by default. CVE-2025-20152 fix released—patch now to prevent DoS.

Grafana Zero-Day? Emergency Patch Released ‘One Day Ahead of Schedule’ for XSS Flaw Grafana SCIM Flaw CVE-2025-41115 Grafana Vulnerabilities, XSS Flaw Grafana security alert, XSS patch
  • Vulnerability

Grafana Zero-Day? Emergency Patch Released ‘One Day Ahead of Schedule’ for XSS Flaw

Do Son May 22, 2025 0

Grafana rushed an emergency patch for CVE-2025-4123, a high-severity XSS flaw that was made public. Upgrade now to prevent unauthorized access.

GitLab Patches High-Severity Flaws: DoS and 2FA Bypass Fixed GitLab Security Update CVE-2026-0723 CVE-2023-7028 & CVE-2023-5356 GitLab vulnerability, DoS flaw
  • Vulnerability

GitLab Patches High-Severity Flaws: DoS and 2FA Bypass Fixed

Do Son May 22, 2025 0

GitLab released urgent updates (18.0.1+) fixing high-severity flaws, including a DoS vulnerability (CVE-2025-0993) and a 2FA bypass (CVE-2024-12093).
Docker Containers Under Attack: New Self-Replicating Dero Cryptominer Dero cryptominer, Docker container hack
  • Malware

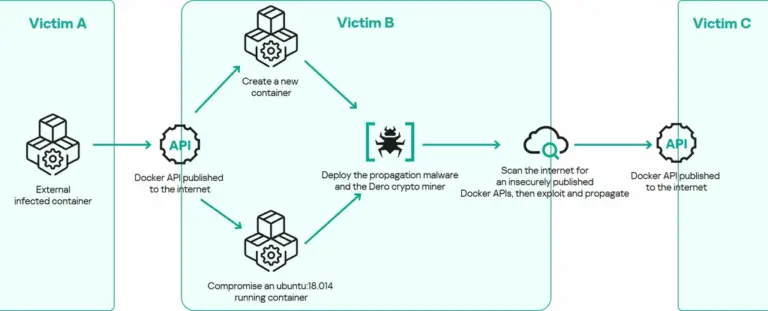
Docker Containers Under Attack: New Self-Replicating Dero Cryptominer

Do Son May 22, 2025 0

A new self-replicating Dero cryptominer is infecting exposed Docker containers, spreading as a worm without needing a C2 server.
NIST Proposes New Metric to Predict “Likely Exploited” Vulnerabilities NIST LEV, vulnerability prioritization Likely Exploited Vulnerability
  • Vulnerability

NIST Proposes New Metric to Predict “Likely Exploited” Vulnerabilities

Do Son May 22, 2025 0

NIST introduces the Likely Exploited Vulnerability (LEV) metric, a new way to estimate which CVEs have likely been exploited in the wild.

Langroid Flaws (CVSS 9.8) Expose LLM Apps to RCE Langroid vulnerability, LLM agent exploit
  • Vulnerability

Langroid Flaws (CVSS 9.8) Expose LLM Apps to RCE

Do Son May 22, 2025 0

Critical vulnerabilities (CVSS 9.8) in the Langroid Python framework allow remote code execution in LLM applications. Update to version 0.53.15 now!

Beyond Detection: PyBitmessage Protocol Used for Covert Monero Mining Campaign PyBitmessage malware, Monero coinminer
  • Malware

Beyond Detection: PyBitmessage Protocol Used for Covert Monero Mining Campaign

Do Son May 22, 2025 0

Threat actors are using the PyBitmessage protocol as a stealthy C2 channel to hide a Monero coinminer and backdoor, evading detection.

Critical Flaws in AI Browse Agents: Exposed to Credential Theft and Hijacking Prompt injection, agent hijacking
  • Vulnerability

Critical Flaws in AI Browse Agents: Exposed to Credential Theft and Hijacking

Do Son May 22, 2025 0

Learn about critical vulnerabilities in LLM-powered Browse agents like Browser Use, allowing domain bypass and prompt injection for data theft.

Industrial Alert: AutomationDirect MB-Gateway Flaw Rated CVSS 10, No Software Fix MB-Gateway vulnerability, OT security
  • Vulnerability

Industrial Alert: AutomationDirect MB-Gateway Flaw Rated CVSS 10, No Software Fix

Do Son May 22, 2025 0

AutomationDirect's MB-Gateway has a critical (CVSS 10) flaw allowing unauthenticated remote access and RCE. Hardware limits prevent a software fix; replacement is recommended.
Beyond Ads: Malvertising Campaign Leverages Google APIs to Redirect Shoppers to Fake Payments E-commerce fraud, JSONP vulnerability
  • Cybercriminals

Beyond Ads: Malvertising Campaign Leverages Google APIs to Redirect Shoppers to Fake Payments

Do Son May 22, 2025 0

Attackers exploit JSONP flaws in Google APIs to inject malicious scripts into e-commerce sites, silently redirecting users to fake payment pages.

Russian GRU’s APT28 Targets Global Logistics Supporting Ukraine Defense APT28 cyber-espionage, GRU cyberattack
  • Cyber Security
  • Malware

Russian GRU’s APT28 Targets Global Logistics Supporting Ukraine Defense

Do Son May 21, 2025 0

A joint advisory warns that Russia's APT28 (Fancy Bear) is actively targeting logistics and tech companies supporting Ukraine with espionage and data exfiltration.

setuptools Flaw Exposes Millions of Python Users to RCE setuptools vulnerability, Python RCE
  • Vulnerability

setuptools Flaw Exposes Millions of Python Users to RCE

Do Son May 21, 2025 0

A high-severity path traversal flaw in setuptools can allow RCE, exposing millions of Python users. Update to 78.1.1 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.