Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
BIND DNS Server Vulnerable to Remote Crash BIND 9 Vulnerability CVE-2025-13878 BIND Cache Poisoning, DNS RCE BIND Vulnerabilities, DNS Security BIND 9 vulnerabilities BIND vulnerability, DNS server crash
  • Vulnerability

BIND DNS Server Vulnerable to Remote Crash

Do Son May 21, 2025 0

A high-severity BIND DNS server vulnerability allows remote attackers to crash servers using malformed TSIG signatures. Urgent update advised.

Windows 11 Boosts Admin Security: Hello Required for Sensitive Tasks Windows 11 security, Admin protection
  • Windows

Windows 11 Boosts Admin Security: Hello Required for Sensitive Tasks

Do Son May 21, 2025 0

Windows 11 is enhancing admin protection by requiring Windows Hello for sensitive tasks and app access to camera, mic, and location.

Chrome’s Auto-Change: Boosting Password Security After Breaches Chrome password security, automatic password change
  • Technology

Chrome’s Auto-Change: Boosting Password Security After Breaches

Do Son May 21, 2025 0

Chrome can now automatically change compromised passwords for you, making your online accounts more secure after a data breach.
Attaxion Becomes the First EASM Platform to Integrate ENISA’s EU Vulnerability Database (EUVD) Attaxion_European_Vulnerability_Database_EUVD_Inte_1747776324MsHMNBAiCA
  • Press Release

Attaxion Becomes the First EASM Platform to Integrate ENISA’s EU Vulnerability Database (EUVD)

cybernewswire May 21, 2025 0
Dover, United States, 21st May 2025, CyberNewsWire
Read More Read more about Attaxion Becomes the First EASM Platform to Integrate ENISA’s EU Vulnerability Database (EUVD)
Three-Year Intrusion: SK Telecom Breach Exposes 27 Million User Records Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Data Leak

Three-Year Intrusion: SK Telecom Breach Exposes 27 Million User Records

Do Son May 21, 2025 0

A nearly three-year intrusion at SK Telecom compromised 27 million users, stealing IMSI, USIM keys, and texts, prompting SIM card replacements.

Palo Alto Networks Warns of XSS Flaw with PoC Exploit Code GlobalProtect XSS, PAN-OS security
  • Vulnerability

Palo Alto Networks Warns of XSS Flaw with PoC Exploit Code

Do Son May 21, 2025 0

A reflected XSS flaw in GlobalProtect (CVE-2025-0133) allows malicious JavaScript execution. PoC exploit code is available. Update your PAN-OS.
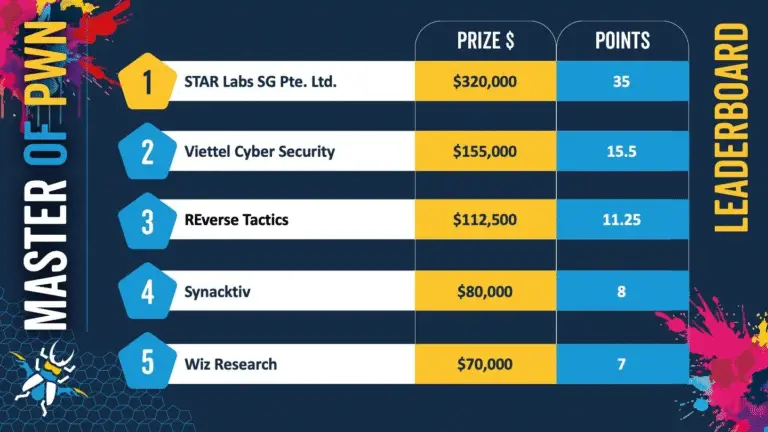
Pwn2Own Berlin Recap: VMware ESXi, Windows 11 Hacked with Zero-Days Pwn2Own winners, VMware ESXi hack
  • Vulnerability

Pwn2Own Berlin Recap: VMware ESXi, Windows 11 Hacked with Zero-Days

Do Son May 21, 2025 0

Pwn2Own Berlin saw VMware ESXi and Windows 11 compromised, along with Firefox. Researchers earned over $1M for 30+ zero-day exploits.

Microsoft Streamlines Nonprofit Offerings, Limits Free M365 & Office 365 E1 Licenses student discount Microsoft 365, Intelligent Services Microsoft 365 UWP, App Deprecation Microsoft 365, Startup Boost Windows 10 EOL, Microsoft 365 Support Protocol Deprecation Microsoft 365 Updates, IT Admin Alert Microsoft 365 VPN shut down Microsoft Authenticator, password manager Windows 10 Microsoft 365 Microsoft nonprofit policy, software donations
  • Technology

Microsoft Streamlines Nonprofit Offerings, Limits Free M365 & Office 365 E1 Licenses

Do Son May 21, 2025 0

Microsoft is changing its nonprofit licensing, discontinuing free M365 Business Premium & E1, offering basic licenses and significant discounts instead.

Google Beam: The Future of Hyper-Realistic 3D Video Conferencing is Here Google Beam, Project Starline
  • Technology

Google Beam: The Future of Hyper-Realistic 3D Video Conferencing is Here

Do Son May 21, 2025 0

Google Beam (formerly Project Starline) is launching with HP, bringing hyper-realistic 3D video conferencing to enterprises.
Google Unveils Flow, Veo 3, Imagen 4: New Era of AI Media Creation Apple Gemini AI AI Overviews, Google Search Google Gemini, Android Privacy Google Veo 3, AI Video Generation Google AI video, generative AI
  • Technology

Google Unveils Flow, Veo 3, Imagen 4: New Era of AI Media Creation

Do Son May 21, 2025 0

Google I/O 2025: Flow, Veo 3 (with audio), and Imagen 4 revealed for advanced AI-powered video and image creation.

Google Unveils $249.99/Month AI Ultra Subscription Google AI Ultra, AI subscription
  • Technology

Google Unveils $249.99/Month AI Ultra Subscription

Do Son May 21, 2025 0

Google AI Ultra is here at $249.99/month, offering advanced Gemini models, Flow, Veo 3, and 30TB Cloud storage.

Google Unveils FireSat: AI Satellite to Detect Wildfires in 20 Minutes Google FireSat, AI wildfire detection
  • Technology

Google Unveils FireSat: AI Satellite to Detect Wildfires in 20 Minutes

Do Son May 21, 2025 0

Google's new FireSat satellite uses AI to detect wildfires in just 20 minutes, a major leap for rapid emergency response and monitoring.

Critical Remote Code Execution Flaw Hits Lexmark Printers CVE-2025-1126 Lexmark, Remote Code Execution
  • Vulnerability

Critical Remote Code Execution Flaw Hits Lexmark Printers

Do Son May 21, 2025 0

Lexmark CVE-2025-1127 flaw allows remote code execution via embedded web server. Affects many printer models—patch firmware to version .240.206+ now.

Critical CVSS 9.8 RCE Flaw in vLLM Exposes AI Hosts to Remote Attacks vLLM Vulnerability CVE-2026-22778 vLLM Memory Corruption, AI Inference RCE CVE-2025-29783 CVE-2025-32444 vLLM vulnerability vLLM, Remote Code Execution
  • Vulnerability

Critical CVSS 9.8 RCE Flaw in vLLM Exposes AI Hosts to Remote Attacks

Do Son May 21, 2025 0

Critical CVSS 9.8 flaw in vLLM allows remote code execution via PyNcclPipe. Patch to 0.8.5 now to protect your AI infrastructure.

Critical containerd Vulnerability: Malicious Images Can Hijack Host Filesystem containerd vulnerability, container security
  • Vulnerability

Critical containerd Vulnerability: Malicious Images Can Hijack Host Filesystem

Do Son May 21, 2025 0

A critical containerd flaw (CVE-2025-47290) allows malicious container images to hijack the host filesystem. Update to version 2.1.1 now.
CISA Alerts: Vertiv Products Vulnerable to RCE, Auth Bypass (CVSS 9.8) Vertiv RCE, authentication bypass
  • Vulnerability

CISA Alerts: Vertiv Products Vulnerable to RCE, Auth Bypass (CVSS 9.8)

Do Son May 21, 2025 0

CISA warns of critical CVSS 9.8 flaws in Vertiv Liebert devices allowing RCE and auth bypass—patch now to protect OT environments.

Hazy Hawk: Stealthy Threat Actor Hijacks High-Profile Subdomains Hazy Hawk, CNAME hijacking
  • Cybercriminals

Hazy Hawk: Stealthy Threat Actor Hijacks High-Profile Subdomains

Do Son May 21, 2025 0

Hazy Hawk is exploiting DNS misconfigurations and CNAME hijacking to take over subdomains of high-profile organizations for scams and malware.

PoC Available: TP-Link Archer AX50 Flaw Allows Remote Root Access Archer AX50 exploit, router security
  • Vulnerability

PoC Available: TP-Link Archer AX50 Flaw Allows Remote Root Access

Do Son May 21, 2025 0

A critical vulnerability (CVE-2025-40634) in TP-Link Archer AX50 routers allows remote code execution as root. A public PoC increases the risk.

High-Severity Privilege Escalation Threat Hits Atlassian Jira Data Center CVE-2024-21678 Jira, Privilege Escalation
  • Vulnerability

High-Severity Privilege Escalation Threat Hits Atlassian Jira Data Center

Do Son May 21, 2025 0

CVE-2025-22157 is a CVSS 7.2 Jira vulnerability allowing privilege escalation. Update Jira Data Center now to prevent unauthorized access.

High Risk: PowerDNS DNSdist Flaw Allows Unauthenticated DoS Attacks PowerDNS Authoritative Server Vulnerabilities CVE-2026-42001 DoS CVE-2024-25581 DNSdist vulnerability, DNS DoS
  • Vulnerability

High Risk: PowerDNS DNSdist Flaw Allows Unauthenticated DoS Attacks

Do Son May 21, 2025 0

A critical DNSdist vulnerability allows unauthenticated attackers to launch DoS attacks, disrupting DNS operations. Update now to secure your system.

AI Scam Alert: Fake Kling AI Sites Deploy Infostealer, Hide Executables AI scam, filename masquerading
  • Cybercriminals
  • Malware

AI Scam Alert: Fake Kling AI Sites Deploy Infostealer, Hide Executables

Do Son May 21, 2025 0

Beware fake Kling AI sites! A new campaign uses deceptive filenames to trick users into downloading infostealers, stealing crypto and browser data.

Is Your Unix Automation Secure? Critical Broadcom Flaw Poses High Risk VMware Telco Cloud Platform 9 Tesco, Broadcom, VMware Walmart Broadcom Jericho4, Distributed AI Infrastructure Broadcom VMware, Perpetual Licenses AI Data Centers, Network Switch Unix automation security, Broadcom vulnerability
  • Vulnerability

Is Your Unix Automation Secure? Critical Broadcom Flaw Poses High Risk

Do Son May 21, 2025 0

A critical flaw in Broadcom's Automic Automation Agent for Unix exposes systems to privilege escalation. Check your version and update to stay secure.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.