
 Do Son
Swan Vector cyber-espionage campaign uses sophisticated malware to target institutions in Japan and Taiwan. Learn how they evade detection and steal data

Two CVEs in TheGem WordPress theme let subscriber-level users upload malicious files and take over sites. Patch to version 5.10.3.1 now.

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.

May 2025 Patch Tuesday fixes 83 Microsoft flaws, including 5 zero-days actively exploited. Critical updates address RCE and SYSTEM privilege bugs.

Ivanti fixes EPMM flaws CVE-2025-4427 and CVE-2025-4428, exploited in the wild for unauthenticated RCE. Update now or apply strict API access controls.

Fortinet warns CVE-2025-32756 is exploited in the wild. The critical RCE flaw affects FortiVoice, FortiMail, FortiNDR, and more. Patch immediately.

 Dan Agbo
Ten years ago, managing data privacy in an organization often meant manual checklists, policy binders, and reactive...

Europol-backed operation busts €3M investment fraud network deceiving 100+ victims via fake trading platform. Arrests made in Cyprus, Israel, Albania.

Google subtly refreshes its logo with gradient colors! Discover the quiet redesign of the 'G' and Gemini symbol ahead of Google I/O 2025

Dior notified customers in China of a data breach. Learn what customer information was accessed and what steps Dior is taking to address the incident
macOS 16 will introduce iOS-like clipboard permissions! Learn how this change will prevent apps from secretly accessing your copied data and protect against threats

Urgent: SAP's May 2025 Security Patch Day reveals critical vulnerabilities! Learn about the latest threats and how to protect your systems. Act now to secure your SAP landscape

PoC exploit for CVE-2025-31258 in macOS RemoteViewServices shows sandbox escape risk. Fixed in Sequoia 15.5. No active exploitation reported yet.

A security audit reveals critical flaws in GNU Screen, including a root exploit. The flaws impact both Screen 5.0.0 and 4.9.x, posing a major risk to Linux/UNIX systems.

CVE-2025-1087: Critical flaw in Kong Insomnia allows template injection and arbitrary code execution. Users urged to update to v11.0.2 immediately.

New report details APT37's "ToyBox Story" campaign, using spear phishing and cloud services to deploy RoKRAT malware. Fileless attacks and stealthy tactics revealed.

Attackers exploit fake AI video tools to deploy Noodlophile Stealer and XWorm, stealing credentials and data via Telegram bots.
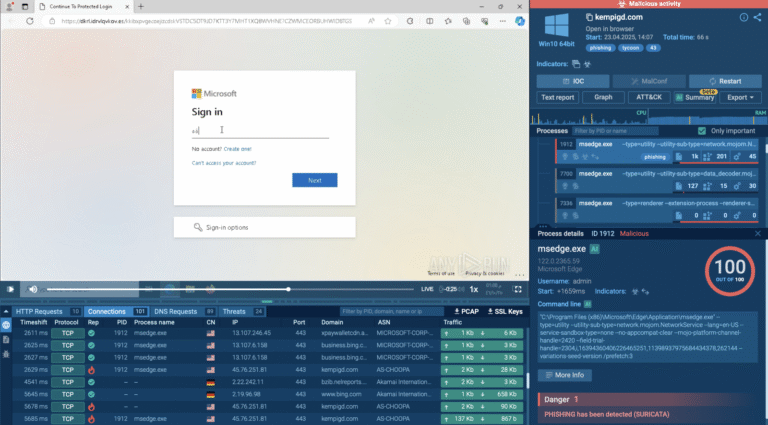
Explore the vulnerabilities in multi-factor authentication and effective strategies to prevent attackers from bypassing it.

PoC for CVE-2025-31644 shows how admin users can exploit F5 BIG-IP Appliance Mode to gain root access via command injection.

In-depth Ruko U11MINI 4K drone review. Explore its 8K photo, 96-min flight, <249g design & see if this budget 4K drone is for you!

New lightweight PupkinStealer malware silently steals browser data, messaging sessions, and desktop files, sending it all via Telegram.

Beware! Cybercriminals are using fake CAPTCHA pages to trick you into running commands that install the dangerous Lumma Stealer malware.