Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
DieNet Hacktivist Group Exploits DDoS-as-a-Service in Rapid Attacks DDoS-as-a-service DieNet
  • Cybercriminals

DieNet Hacktivist Group Exploits DDoS-as-a-Service in Rapid Attacks

Do Son May 9, 2025 0

DieNet, a new hacktivist group, is leveraging DDoS-as-a-service for rapid-fire attacks on critical infrastructure. NETSCOUT reports on their tactics and targets.

The Benefits Of Working With An Outsourcing Company Img_2025_05_08_06_41_32
  • Technique

The Benefits Of Working With An Outsourcing Company

Do Son May 8, 2025 0
There are many aspects that make up a business, from sales and production to even human relations...
Read More Read more about The Benefits Of Working With An Outsourcing Company
Microsoft Azure Supports Google’s A2A Protocol for Seamless AI Agent Communication AI interoperability, A2A protocol
  • Technology

Microsoft Azure Supports Google’s A2A Protocol for Seamless AI Agent Communication

Do Son May 8, 2025 0

Microsoft integrates Google's A2A protocol into Azure AI, enabling seamless communication between AI agents across different cloud platforms.

LinkedIn Enhances Job Search with New AI-Powered Features AI job search, LinkedIn AI
  • Technology

LinkedIn Enhances Job Search with New AI-Powered Features

Do Son May 8, 2025 0

LinkedIn introduces new AI-powered job search tools for a more intuitive experience. Discover roles that truly fit your skills and aspirations.

Critical CVE-2025-20188 (CVSS 10) Flaw in Cisco IOS XE WLCs Allows Remote Root Access CVE-2025-20188 IOS XE vulnerability Cisco
  • Vulnerability

Critical CVE-2025-20188 (CVSS 10) Flaw in Cisco IOS XE WLCs Allows Remote Root Access

Do Son May 8, 2025 0

Cisco patches CVE-2025-20188, a CVSS 10 flaw in IOS XE WLCs, enabling unauthenticated remote file uploads and root-level command execution.

Multi Vulnerabilities Found in SonicWall SMA 100 Series Prompt Urgent Security Update SonicWall Security Advisory SonicOS Patch 2026 CVE-2025-23006 SonicWall, SMA 100 Vulnerabilities
  • Vulnerability

Multi Vulnerabilities Found in SonicWall SMA 100 Series Prompt Urgent Security Update

Do Son May 8, 2025 0

SonicWall urges urgent updates to SMA 100 Series devices after critical post-auth vulnerabilities expose systems to file deletion and command injection.

CVE-2025-23123 (CVSS 10): Critical UniFi Protect Cameras Flaw Demands Immediate Updates UniFi Protect Cameras, Security Advisory
  • Vulnerability

CVE-2025-23123 (CVSS 10): Critical UniFi Protect Cameras Flaw Demands Immediate Updates

Do Son May 8, 2025 0

Ubiquiti warns of critical RCE flaw in UniFi Protect Cameras (CVE-2025-23123); update firmware and app to prevent potential network compromise.
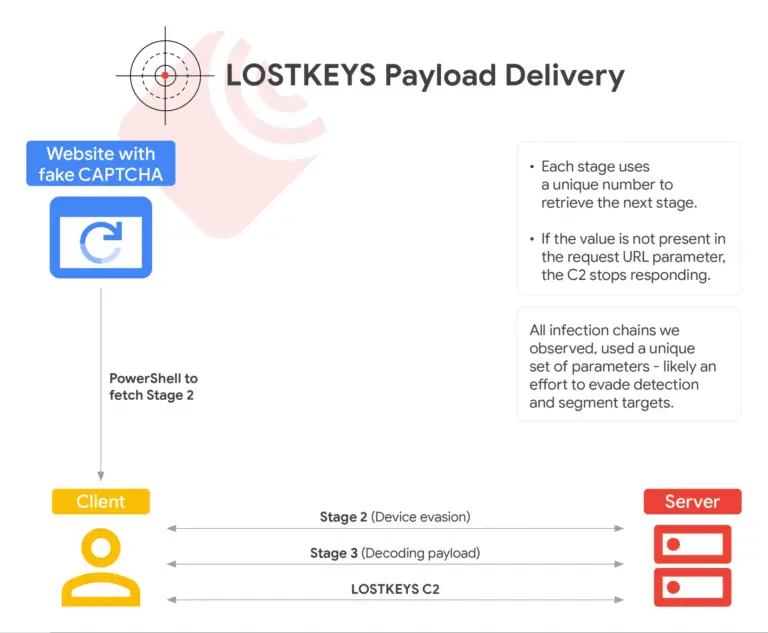
Google Uncovers LOSTKEYS Malware Used by Russian COLDRIVER for Cyber Espionage LOSTKEYS Malware, COLDRIVER
  • Cyber Security
  • Malware

Google Uncovers LOSTKEYS Malware Used by Russian COLDRIVER for Cyber Espionage

Do Son May 8, 2025 0

Google's GTIG reveals LOSTKEYS malware, a new tool by Russian actor COLDRIVER, targeting NATO advisors and Ukraine via fake CAPTCHAs.
Iranian Cyber Espionage Uses Fake Modeling Agency for Targeted Attacks Cyber Espionage, Iran
  • Cyber Security

Iranian Cyber Espionage Uses Fake Modeling Agency for Targeted Attacks

Do Son May 8, 2025 0

Unit 42 uncovers Iranian cyber espionage using a fake modeling agency website to selectively target victims with sophisticated techniques.

Inferno Drainer Steals Millions in Evolving Crypto Attacks axios Supply Chain Attack WAVESHAPER.V2 SnappyBee Malware Salt Typhoon Stately Taurus ScoringMathTea RAT, Lazarus Reflective DLL
  • Cybercriminals

Inferno Drainer Steals Millions in Evolving Crypto Attacks

Do Son May 8, 2025 0

Inferno Drainer returns stronger than ever, using Discord phishing and blockchain obfuscation to steal millions in crypto.

Agenda Ransomware Evolves with NETXLOADER and SmokeLoader in Global Campaigns Agenda ransomware, NETXLOADER
  • Malware

Agenda Ransomware Evolves with NETXLOADER and SmokeLoader in Global Campaigns

Do Son May 8, 2025 0

Agenda ransomware (Qilin) is back, now using the advanced NETXLOADER and SmokeLoader to enhance infiltration and evade detection. Targets global sectors.
APT36 Suspected in India Gov Spoofing Phishing with ClickFix Tactics APT36 phishing, ClickFix campaign
  • Cybercriminals
  • Malware

APT36 Suspected in India Gov Spoofing Phishing with ClickFix Tactics

Do Son May 8, 2025 0

A sophisticated phishing campaign, possibly by APT36, spoofs Indian government sites and uses ClickFix tactics to target Windows and Linux users.

CVE-2025-27533: Apache ActiveMQ Memory Allocation Bug Could Lead to Denial of Service ActiveMQ RCE Jolokia Exploit ActiveMQ CVE-2025-27533 ActiveMQ Deserialization RCE, CVE-2025-54539
  • Vulnerability

CVE-2025-27533: Apache ActiveMQ Memory Allocation Bug Could Lead to Denial of Service

Do Son May 8, 2025 0

A vulnerability in Apache ActiveMQ's buffer handling can cause memory exhaustion, leading to denial of service. Patch now to version 6.1.6+ or 5.19.0+.

Aikido Uncovers Malicious Code in Popular npm Package rand-user-agent RAT
  • Malware

Aikido Uncovers Malicious Code in Popular npm Package rand-user-agent

Do Son May 8, 2025 0

Aikido discovers a Remote Access Trojan (RAT) hidden in rand-user-agent, a popular npm package with 45,000 weekly downloads.

Lampion Malware Returns with ClickFix Tactics to Target Portuguese Sectors Lampion, ClickFix
  • Malware

Lampion Malware Returns with ClickFix Tactics to Target Portuguese Sectors

Do Son May 8, 2025 0

Unit 42 uncovers a sophisticated Lampion malware campaign using ClickFix social engineering tactics to target government and financial sectors in Portugal.

Critical Privilege Escalation Flaw in IGEL OS Exposes Systems to Root Access Risks IGEL OS, Privilege Escalation
  • Vulnerability

Critical Privilege Escalation Flaw in IGEL OS Exposes Systems to Root Access Risks

Do Son May 8, 2025 0

IGEL OS suffers from a critical privilege escalation vulnerability affecting OS 11 and OS 12. Users are urged to patch immediately.

Polish Police Bust DDoS-for-Hire Network in Europol Operation DDoS, Cyberattacks
  • Cybercriminals

Polish Police Bust DDoS-for-Hire Network in Europol Operation

Do Son May 7, 2025 0

Polish authorities arrested four individuals running a global DDoS-for-hire network, disrupting thousands of cyberattacks. Part of Europol's Operation PowerOFF.

Best Synthetic Data Generation Tools in 2025 CVE-2024-21508
  • Technique

Best Synthetic Data Generation Tools in 2025

Do Son May 7, 2025 0
Synthetic data may seem to be the stuff of science fiction, but these days in 2025, it’s...
Read More Read more about Best Synthetic Data Generation Tools in 2025
Zero-Day CLFS Vulnerability (CVE-2025-29824) Exploited in Ransomware Attacks Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Malware
  • Vulnerability

Zero-Day CLFS Vulnerability (CVE-2025-29824) Exploited in Ransomware Attacks

Do Son May 7, 2025 0

A zero-day privilege escalation vulnerability (CVE-2025-29824) in Microsoft CLFS was exploited by Balloonfly (Play ransomware) before the official patch.

Why Data Erasure Is the First Line of Defense Against Insider Threats? NTLM Relay Attacks
  • Technique

Why Data Erasure Is the First Line of Defense Against Insider Threats?

Do Son May 7, 2025 0
IBM’s Cost of a Data Breach 2024 report revealed that the highest data breach costs were generated...
Read More Read more about Why Data Erasure Is the First Line of Defense Against Insider Threats?
How to Scrape the Web at Scale with the Best Proxies in 2025 CVE-2023-49606
  • Technique

How to Scrape the Web at Scale with the Best Proxies in 2025

Do Son May 7, 2025 0

Learn how to scrape the web efficiently at scale using the best proxies in 2025. Avoid IP bans, boost speed, and collect data reliably and securely.
CISA Warns of Unsophisticated Cyber Actors Targeting U.S. Critical Infrastructure OT Systems CISA, ICS/SCADA
  • Cybercriminals

CISA Warns of Unsophisticated Cyber Actors Targeting U.S. Critical Infrastructure OT Systems

Do Son May 7, 2025 0

CISA warns that basic cyber attacks are targeting ICS/SCADA systems in the U.S. energy and transportation sectors due to poor cyber hygiene and exposed assets.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-115934CVSS 9.3
    An unauthenticated SQL injection can occur on the front end of any site that uses craft.search to perform a search,...
    📅 Updated: Nov 9, 2026
  • CVE-2026-119756CVSS 9.3
    Tasmota through 16.0.0, fixed in commit e97e1e4, contains a heap out-of-bounds write vulnerability in SendReceiveDeviceGroupMessage() that allows unauthenticated...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123488CVSS 9.3
    Craft CMS 4.0.0 before 4.18.9 and 5.0.0 before 5.11.2 contains an unauthenticated SQL injection vulnerability in the element...
    📅 Updated: Nov 9, 2026
  • CVE-2026-102530CVSS 9.4
    JupyterLab Desktop is the cross-platform desktop application for JupyterLab. Prior to 4.6.2-1, remote-server URLs were inserted into the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123960CVSS 9.4
    A weakness has been identified in TOTOLINK CA300-PoE 6.2c.884. This affects the function setWanConfig of the file /cgi-bin/cstecgi.cgi....
    📅 Updated: Nov 9, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 9, 2026
  • CVE-2026-100358CVSS 9.4
    SuiteCRM is an open-source, enterprise-ready Customer Relationship Management (CRM) software application. Prior to 7.15.2 and 8.10.2, the Studio...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.