Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CISA Warns of Critical Vulnerabilities in Planet Technology Products Planet Technology vulnerabilities, CISA advisory
  • Vulnerability

CISA Warns of Critical Vulnerabilities in Planet Technology Products

Do Son April 28, 2025 0

CISA warns of critical vulnerabilities in Planet Technology products, including command injection and hardcoded credentials, allowing attackers to manipulate devices.
Critical Flaw Exposes Linux Security Blind Spot: io_uring Bypasses Detection io_uring vulnerability, Linux runtime security
  • Linux
  • Malware
  • Vulnerability

Critical Flaw Exposes Linux Security Blind Spot: io_uring Bypasses Detection

Do Son April 28, 2025 0

ARMO researchers reveal how io_uring blinds Linux security tools like Falco, Tetragon, and Defender, exposing systems to undetected rootkit attacks.

React Router Vulnerabilities CVE-2025-43864 and CVE-2025-43865 Expose Web Applications to Attack React Router vulnerabilities patch React Router Vulnerabilities CVE-2025-61686
  • Vulnerability

React Router Vulnerabilities CVE-2025-43864 and CVE-2025-43865 Expose Web Applications to Attack

Do Son April 28, 2025 0

React Router flaws CVE-2025-43864 and CVE-2025-43865 allow cache poisoning and data spoofing attacks; users must upgrade to version 7.5.2 or later.
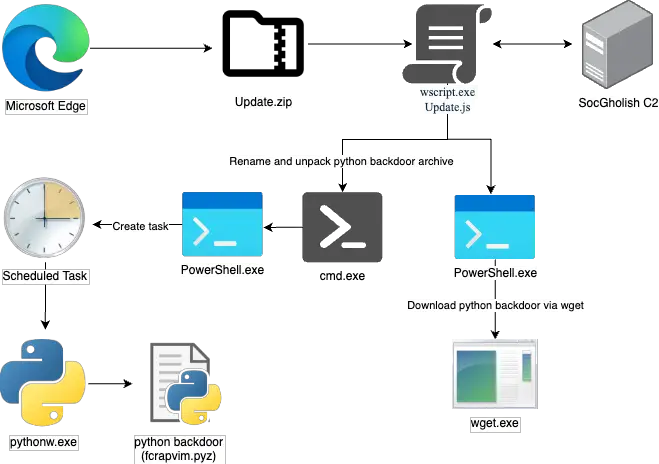
SocGholish and RansomHub: Sophisticated Attack Campaign Targeting Corporate Networks SocGholish, RansomHub
  • Cybercriminals
  • Malware

SocGholish and RansomHub: Sophisticated Attack Campaign Targeting Corporate Networks

Do Son April 28, 2025 0

eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.

DeviceCodePhishing: How a New Attack Bypasses FIDO and MFA Protections DeviceCodePhishing, OAuth phishing
  • Cybercriminals

DeviceCodePhishing: How a New Attack Bypasses FIDO and MFA Protections

Do Son April 28, 2025 0

DeviceCodePhishing exploits OAuth Device Code Flow to bypass MFA and FIDO protections, redirecting victims to real sites with no phishing signs.

CVE-2025-23016: Critical FastCGI Heap Overflow Threatens Embedded Devices, PoC Releases FastCGI vulnerability, CVE-2025-23016
  • Vulnerability

CVE-2025-23016: Critical FastCGI Heap Overflow Threatens Embedded Devices, PoC Releases

Do Son April 28, 2025 0

FastCGI CVE-2025-23016 vulnerability allows heap overflow and potential code execution on embedded devices. Users must upgrade to version 2.4.5 or later

North Korean APT ‘Contagious Interview’ Launches Fake Crypto Companies to Spread Malware Trio North Korea malware North Korea, OFAC sanctions DPRK AI hiring, Wagemole campaigns
  • Cybercriminals
  • Malware

North Korean APT ‘Contagious Interview’ Launches Fake Crypto Companies to Spread Malware Trio

Do Son April 28, 2025 0

Silent Push uncovers Lazarus Group's campaign using fake crypto job offers to spread malware (BeaverTail, InvisibleFerret, OtterCookie), targeting job seekers.

Multiple Vulnerabilities in NETSCOUT nGeniusONE Threaten Infrastructure Visibility Platforms nGeniusONE, Vulnerability
  • Vulnerability

Multiple Vulnerabilities in NETSCOUT nGeniusONE Threaten Infrastructure Visibility Platforms

Do Son April 28, 2025 0

NETSCOUT advisory reveals critical vulnerabilities in nGeniusONE, including hardcoded credentials & XSS. Update to version 6.4.0 b2350 or later immediately.

SessionShark: New Phishing Kit Bypasses Office 365 MFA MFA Bypass, SessionShark
  • Cybercriminals

SessionShark: New Phishing Kit Bypasses Office 365 MFA

Do Son April 28, 2025 0

Discover SessionShark, a sophisticated phishing toolkit designed to bypass Microsoft Office 365 multi-factor authentication by stealing session tokens.

The most popular PAIRMiner cloud mining investment in 2025, easily realize a daily income of $15,600 CVE-2024-55563 - transaction-relay jamming attack
  • Technique

The most popular PAIRMiner cloud mining investment in 2025, easily realize a daily income of $15,600

Do Son April 27, 2025 0
As the global cryptocurrency market continues to heat up, more and more investors are beginning to realize...
Read More Read more about The most popular PAIRMiner cloud mining investment in 2025, easily realize a daily income of $15,600
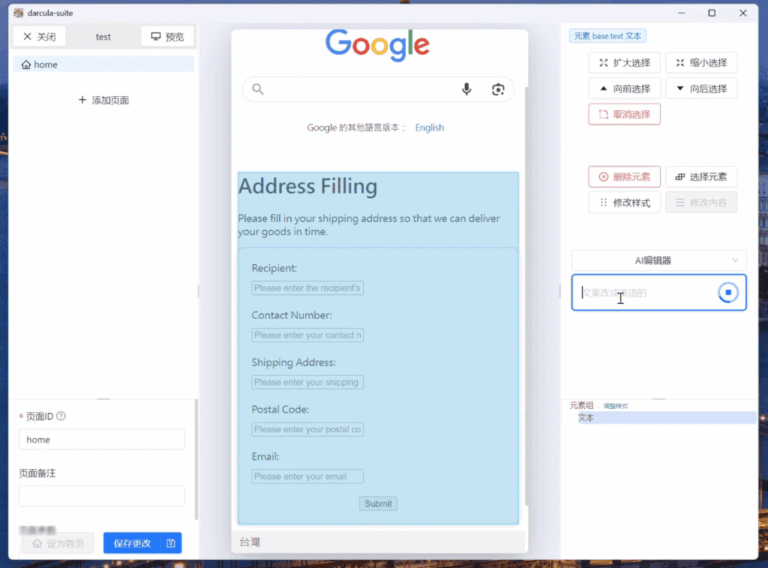
Darcula-Suite: AI Revolutionizes Phishing-as-a-Service Operations Darcula-Suite, Phishing-as-a-Service
  • Cybercriminals

Darcula-Suite: AI Revolutionizes Phishing-as-a-Service Operations

Do Son April 27, 2025 0

Darcula-Suite integrates AI to supercharge phishing-as-a-service operations, enabling faster, scalable, and more convincing phishing campaigns worldwide.

Lazarus Group’s “Operation SyncHole” Targets South Korean Industries Lazarus Group, Cyber Espionage Operation SyncHole
  • Cyber Security
  • Malware

Lazarus Group’s “Operation SyncHole” Targets South Korean Industries

Do Son April 27, 2025 0

Kaspersky uncovers "Operation SyncHole," a sophisticated cyber-espionage campaign by the Lazarus Group targeting critical South Korean sectors using advanced malware.

CVE-2025-43859: Request Smuggling Vulnerability in Python’s h11 HTTP Library Request Smuggling h11 vulnerability
  • Vulnerability

CVE-2025-43859: Request Smuggling Vulnerability in Python’s h11 HTTP Library

Do Son April 27, 2025 0

A CVE-2025-43859 vulnerability in Python’s h11 library may lead to request smuggling attacks when paired with buggy proxies. Patch to version 0.15.0 now.

ConnectWise Patches Critical ViewState RCE Vulnerability in ScreenConnect ScreenConnect vulnerability ViewState RCE
  • Vulnerability

ConnectWise Patches Critical ViewState RCE Vulnerability in ScreenConnect

Do Son April 26, 2025 0

ConnectWise addresses a critical ViewState code injection flaw in ScreenConnect. If machine keys are compromised, RCE is possible. Update immediately!

DslogdRAT Malware Targets Ivanti Connect Secure via CVE-2025-0282 Zero-Day Exploit Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Malware
  • Vulnerability

DslogdRAT Malware Targets Ivanti Connect Secure via CVE-2025-0282 Zero-Day Exploit

Do Son April 26, 2025 0

DslogdRAT malware exploited Ivanti Connect Secure via CVE-2025-0282, using web shells and C2 channels to evade detection and persist in networks.

NVIDIA Releases Security Update to Address GPU Driver Vulnerabilities NVIDIA GPU, Security Update
  • Vulnerability

NVIDIA Releases Security Update to Address GPU Driver Vulnerabilities

Do Son April 26, 2025 0

NVIDIA issues updates to patch GPU and vGPU flaws, including CVE-2025-23244, which allows privilege escalation and potential code execution.

CVE-2025-32432 (CVSS 10): Craft CMS Hit by Critical RCE Flaw Exploited in the Wild Craft CMS Vulnerability CVE-2026-32267 CVE-2023-41892 Craft CMS CVE-2025-32432
  • Vulnerability

CVE-2025-32432 (CVSS 10): Craft CMS Hit by Critical RCE Flaw Exploited in the Wild

Do Son April 25, 2025 0

Craft CMS patches critical CVE-2025-32432 flaw. Exploited in the wild—users must update to versions 3.9.15, 4.14.15, or 5.6.17.

AI Jailbreaks Expose Systemic Vulnerability in Generative AI Platforms AI Jailbreak Generative AI
  • Vulnerability

AI Jailbreaks Expose Systemic Vulnerability in Generative AI Platforms

Do Son April 25, 2025 0

CERT/CC reveals systemic jailbreak flaws in major AI models, including ChatGPT and Claude, enabling bypass of safety filters with identical prompt techniques.

North Korean Operatives Use GenAI to Infiltrate Global Tech Jobs, Okta Warns North Korea malware North Korea, OFAC sanctions DPRK AI hiring, Wagemole campaigns
  • Cybercriminals

North Korean Operatives Use GenAI to Infiltrate Global Tech Jobs, Okta Warns

Do Son April 25, 2025 0

Report details how North Korean operatives use AI to create fake personas and infiltrate tech companies, funneling funds to the DPRK regime.

Alphabet Q1 2025: Revenue Surges, Gemini 2.5 Launched Railway app Google Cloud suspension Google Cloud CDN Interconnect pricing 2026, GCP data transfer cost increase Google Cloud Disrupted ImageRunner Alphabet earnings, Google AI
  • Technology

Alphabet Q1 2025: Revenue Surges, Gemini 2.5 Launched

Do Son April 25, 2025 0

Alphabet reports strong Q1 2025 earnings with revenue up 12%. Google Cloud soars, Gemini 2.5 debuts, and AI Overviews gains traction.

Perplexity Plans AI-Powered Browser with Personalized Ads, Eyes Chrome Perplexity Comet, Chrome antitrust
  • Technology

Perplexity Plans AI-Powered Browser with Personalized Ads, Eyes Chrome

Do Son April 25, 2025 0

Perplexity.ai reveals "Comet" browser with AI integration and personalized ads. Exec expresses interest in Chrome amid Google antitrust case.

EU to Introduce Repairability Labels for Smartphones and Tablets AI Continent Action Plan European Commission EU repairability label, smartphone labeling
  • Technology

EU to Introduce Repairability Labels for Smartphones and Tablets

Do Son April 25, 2025 0

Starting June 20, the EU will require smartphones & tablets to display repairability, energy, & durability labels, aiding consumer decisions.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-125383CVSS 9.3
    INDOTALENT WHMS (Asp.Net-Core-Inventory-Order-Management-System) before 10.20261109 contains an authentication bypass vulnerability caused by a hard-coded JWT signing key, issuer...
    📅 Updated: Nov 9, 2026
  • CVE-2026-125384CVSS 9.3
    INDOTALENT WHMS before 10.20261109 contains a default credentials vulnerability that allows unauthenticated attackers to gain administrator access because...
    📅 Updated: Nov 9, 2026
  • CVE-2026-125370CVSS 9.3
    Kubero 3.0.0 through 3.1.1 contains an authentication bypass vulnerability that allows unauthenticated remote attackers to forge administrative JWTs...
    📅 Updated: Nov 9, 2026
  • CVE-2026-85295CVSS 9.8
    Chartbrew is an open-source web application that can connect directly to databases and APIs and use the data...
    📅 Updated: Nov 9, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 9, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 9, 2026
  • CVE-2026-125120CVSS 9.8
    Mongoose is a MongoDB object modeling tool designed to work in an asynchronous environment. Prior to 6.13.11, 7.8.12,...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115934CVSS 9.3
    An unauthenticated SQL injection can occur on the front end of any site that uses craft.search to perform a search,...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.