
 Do Son
Microsoft is gearing up for the Windows 11 25H2 update in October 2025. Early signs suggest it will be a minor release, focusing on stability and support.

Critical Craft CMS zero-day CVE-2025-32432 exploited with Yii flaw; Metasploit module published, urging urgent patching to prevent server breaches.

CISA warns of critical vulnerabilities in Planet Technology products, including command injection and hardcoded credentials, allowing attackers to manipulate devices.
ARMO researchers reveal how io_uring blinds Linux security tools like Falco, Tetragon, and Defender, exposing systems to undetected rootkit attacks.

React Router flaws CVE-2025-43864 and CVE-2025-43865 allow cache poisoning and data spoofing attacks; users must upgrade to version 7.5.2 or later.
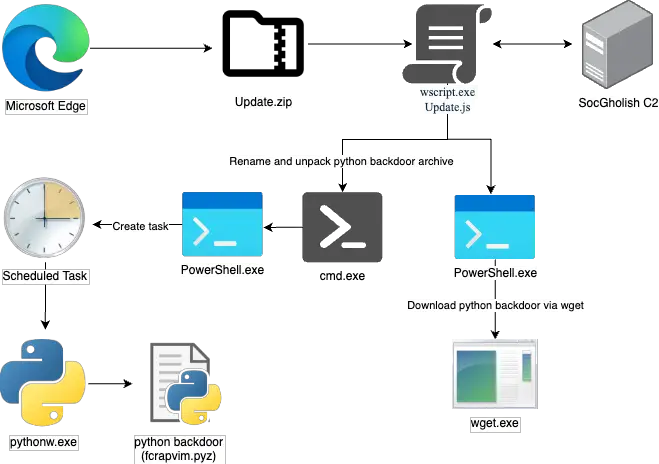
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.

DeviceCodePhishing exploits OAuth Device Code Flow to bypass MFA and FIDO protections, redirecting victims to real sites with no phishing signs.

FastCGI CVE-2025-23016 vulnerability allows heap overflow and potential code execution on embedded devices. Users must upgrade to version 2.4.5 or later

Silent Push uncovers Lazarus Group's campaign using fake crypto job offers to spread malware (BeaverTail, InvisibleFerret, OtterCookie), targeting job seekers.

NETSCOUT advisory reveals critical vulnerabilities in nGeniusONE, including hardcoded credentials & XSS. Update to version 6.4.0 b2350 or later immediately.

Discover SessionShark, a sophisticated phishing toolkit designed to bypass Microsoft Office 365 multi-factor authentication by stealing session tokens.
The most popular PAIRMiner cloud mining investment in 2025, easily realize a daily income of $15,600

The most popular PAIRMiner cloud mining investment in 2025, easily realize a daily income of $15,600
As the global cryptocurrency market continues to heat up, more and more investors are beginning to realize...
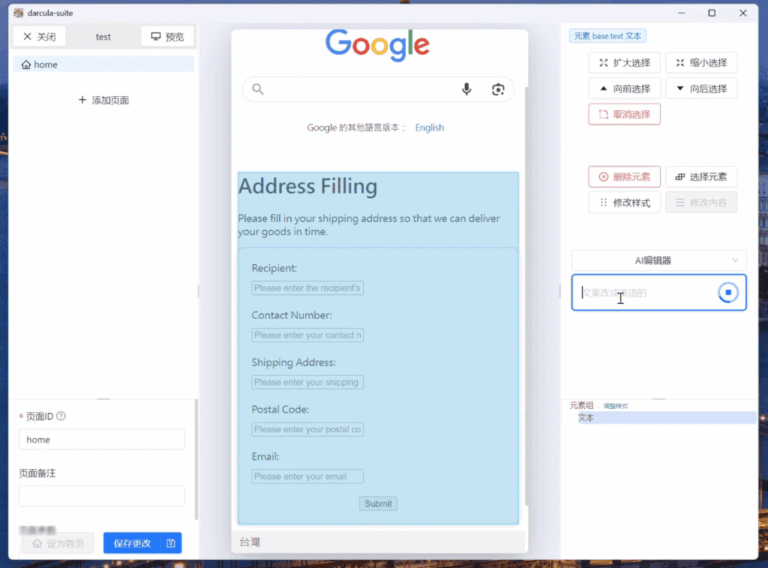
Darcula-Suite integrates AI to supercharge phishing-as-a-service operations, enabling faster, scalable, and more convincing phishing campaigns worldwide.

Kaspersky uncovers "Operation SyncHole," a sophisticated cyber-espionage campaign by the Lazarus Group targeting critical South Korean sectors using advanced malware.

A CVE-2025-43859 vulnerability in Python’s h11 library may lead to request smuggling attacks when paired with buggy proxies. Patch to version 0.15.0 now.

ConnectWise addresses a critical ViewState code injection flaw in ScreenConnect. If machine keys are compromised, RCE is possible. Update immediately!

DslogdRAT malware exploited Ivanti Connect Secure via CVE-2025-0282, using web shells and C2 channels to evade detection and persist in networks.

NVIDIA issues updates to patch GPU and vGPU flaws, including CVE-2025-23244, which allows privilege escalation and potential code execution.

Craft CMS patches critical CVE-2025-32432 flaw. Exploited in the wild—users must update to versions 3.9.15, 4.14.15, or 5.6.17.

CERT/CC reveals systemic jailbreak flaws in major AI models, including ChatGPT and Claude, enabling bypass of safety filters with identical prompt techniques.
Report details how North Korean operatives use AI to create fake personas and infiltrate tech companies, funneling funds to the DPRK regime.

Alphabet reports strong Q1 2025 earnings with revenue up 12%. Google Cloud soars, Gemini 2.5 debuts, and AI Overviews gains traction.